Category

Analyst Brief | Ransomware and Supply Chain
In mid July 2026, a previously unseen group calling itself D1R published three names on its dark web leak site. The first was Synopsys, an American firm that makes the design software used to build and test computer chips. The other two were customers of that first company: the British chip designer ARM, and the German engineering group Bosch. One supplier at the top, two of its customers underneath. On the face of it, a clean example of an attacker using one company as a doorway into others.
That story is a useful one for any manufacturer to sit with, because supply chain traversal is a real and growing problem. But the more interesting lesson here is not that the attack happened as described. It is that most of it probably did not, and that telling the difference is the whole job.
01 What D1R actually claimed
D1R’s leak site laid out a single narrative that ties all three victims together. The group said it found a flaw in a Synopsys registration form that let it pull an entire corporate customer database of roughly 40,000 entries, without needing any internal access. It posted a screenshot of a plain-text file as proof, showing a site identifier, a company name and a location on each row.
It then claimed that this list became a map. Using the customer names as a target list, D1R said it reached into ARM and into Bosch, framing both as downstream victims that were only exposed because the supplier at the top had leaked. Its own words on the Bosch page were blunt: thank Synopsys for showing us where the valuable data lives.
02 Holding the claims up to the light
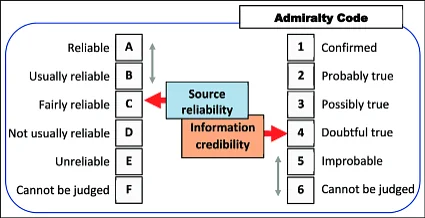
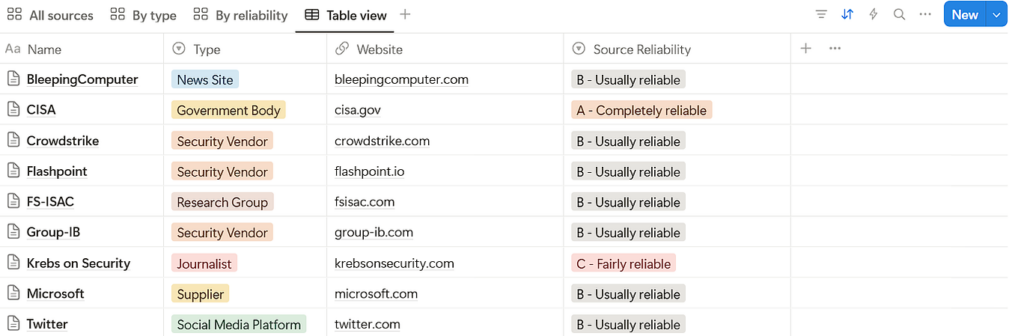
We reviewed the leak site content and set it against open source reporting and the vendors’ own material. The three claims do not hold together equally well.

Put together, the picture is of an emerging group building a dramatic supply chain story on top of thin proof. The tactic is not new. Exaggerating scope, recycling public documents and leaning on a big brand name are all cheap ways to manufacture pressure and buy credibility before a group has earned either.
03 Why a shaky claim still matters to you
It would be easy to read the above and move on. No confirmed breach, so no problem. That would be the wrong conclusion for a manufacturer, for two reasons.
First, the technique D1R is describing is entirely credible even when this particular execution is not. Attackers do compromise suppliers to reach their customers, and a leaked customer list genuinely is a targeting aid. The next group to try this may have real access rather than a public manual and a screenshot.
Second, and this is the part that bites, your name can appear on a leak site because of something that happened to a supplier, not to you. If a manufacturer using Synopsys tooling had first learned of this by seeing a customer’s name in that 40,000-line list, the damage would already be underway, in customer questions, in press enquiries, in board-level anxiety, regardless of whether a single file had truly been taken.

What good looks like
Monitoring your own perimeter is necessary but no longer sufficient. The D1R episode argues for extending that visibility outward, across the suppliers and partners whose problems can become yours.
- Know who is upstream of you. Keep a live view of the vendors, tooling and service providers your operation depends on, so that a name on a leak site immediately means something.
- Watch leak sites for your suppliers, not just yourself. Early sight of a supplier being named buys you time to ask the right questions before customers and journalists do.
- Be able to triage a claim fast. The value is not in the alert alone. It is in quickly separating an inflated extortion story from a genuine cascade, so you respond in proportion.
- Rehearse the third-party scenario. Decide in advance who owns the response when the incident is a supplier’s, not yours.
WORK WITH US
See it coming, from your suppliers as well as your own front door
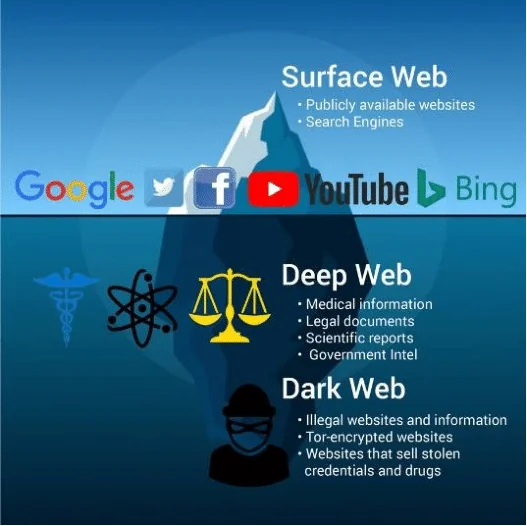
SOS Intelligence is a UK-based dark web threat intelligence platform. We continuously monitor the surface, deep and dark web, Telegram channels, criminal forums and breach databases, and surface what matters to your business, your clients and your supply chain, so you can act before attackers do. The D1R case is exactly the sort of thing our platform is built to catch early: a supplier gets named on a leak site, and you want to know about it straight away rather than hearing it from a customer or a journalist.
- Supply Chain Risk Monitoring. Track your vendors, partners and critical third parties, and know the moment a supplier is mentioned in a breach, a data sale or a dark web discussion, before it reaches your business.
- DARKMAP™ continuous monitoring. Automated, round-the-clock scanning across the dark web that surfaces credential leaks, data sales, ransomware mentions and brand impersonation in real time.
- Real-time Flash Alerts. Get notified the moment your monitored domains, credentials or keywords appear in threat feeds, hours ahead of conventional tooling, straight to your inbox or webhook.
- DARKSEARCH™ on demand. Search our indexed dark web database whenever you need to, to investigate a name, look up a domain or check out a claim like D1R’s for yourself.
Want to see what we are already picking up about your organisation and your supply chain? Book a free 30-minute demo, and we will scan your domain live on the call.







Recent Comments