Customer portal
Articles Tagged with

CVE intelligence

"SOS
CVE Top 10

The SOS Intelligence CVE Chatter Weekly Top Ten – 09 November 2026


This weekly blog post is from via our unique intelligence collection pipelines. We are your eyes and ears online, including the Dark Web.

There are thousands of vulnerability discussions each week. SOS Intelligence gathers a list of the most discussed Common Vulnerabilities and Exposures (CVE) online for the previous week.

We make every effort to ensure the accuracy of the data presented. As this is an automated process some errors may creep in.

If you are feeling generous please do make us aware of anything you spot, feel free to follow us on Twitter @sosintel and DM us. Thank you!


1.  CVE-2026-88073

Use after free in Windows Graphics Kernel allows an authorized attacker to elevate privileges locally.

https://nvd.nist.gov/vuln/detail/CVE-2026-88073


2.

https://nvd.nist.gov/vuln/detail/


3.

https://nvd.nist.gov/vuln/detail/


4.

https://nvd.nist.gov/vuln/detail/


5.

https://nvd.nist.gov/vuln/detail/


6.

https://nvd.nist.gov/vuln/detail/


7.

https://nvd.nist.gov/vuln/detail/


8.

https://nvd.nist.gov/vuln/detail/


9.

https://nvd.nist.gov/vuln/detail/


10.

https://nvd.nist.gov/vuln/detail/


"SOS
CVE Top 10

The SOS Intelligence CVE Chatter Weekly Top Ten – 02 November 2026


This weekly blog post is from via our unique intelligence collection pipelines. We are your eyes and ears online, including the Dark Web.

There are thousands of vulnerability discussions each week. SOS Intelligence gathers a list of the most discussed Common Vulnerabilities and Exposures (CVE) online for the previous week.

We make every effort to ensure the accuracy of the data presented. As this is an automated process some errors may creep in.

If you are feeling generous please do make us aware of anything you spot, feel free to follow us on Twitter @sosintel and DM us. Thank you!


1.  CVE-2026-10232

Insufficient validation of untrusted input in InterestGroups in Google Chrome prior to 149.0.7827.53 allowed a remote attacker who had compromised the renderer process to potentially perform a sandbox escape via a crafted HTML page. (Chromium security severity: High)

https://nvd.nist.gov/vuln/detail/CVE-2026-10232


2. CVE-2026-10233

Insufficient validation of untrusted input in InterestGroups in Google Chrome prior to 149.0.7827.53 allowed a remote attacker who had compromised the renderer process to potentially perform a sandbox escape via a crafted HTML page. (Chromium security severity: High)

https://nvd.nist.gov/vuln/detail/CVE-2026-10233


3. CVE-2026-10362

Insufficient validation of untrusted input in InterestGroups in Google Chrome prior to 149.0.7827.53 allowed a remote attacker who had compromised the renderer process to potentially perform a sandbox escape via a crafted HTML page. (Chromium security severity: High)

https://nvd.nist.gov/vuln/detail/CVE-2026-10362


4. CVE-2026-10601

Insufficient validation of untrusted input in InterestGroups in Google Chrome prior to 149.0.7827.53 allowed a remote attacker who had compromised the renderer process to potentially perform a sandbox escape via a crafted HTML page. (Chromium security severity: High)

https://nvd.nist.gov/vuln/detail/CVE-2026-10601


5. CVE-2026-10619

Insufficient validation of untrusted input in InterestGroups in Google Chrome prior to 149.0.7827.53 allowed a remote attacker who had compromised the renderer process to potentially perform a sandbox escape via a crafted HTML page. (Chromium security severity: High)

https://nvd.nist.gov/vuln/detail/CVE-2026-10619


6. CVE-2026-10634

Insufficient validation of untrusted input in InterestGroups in Google Chrome prior to 149.0.7827.53 allowed a remote attacker who had compromised the renderer process to potentially perform a sandbox escape via a crafted HTML page. (Chromium security severity: High)

https://nvd.nist.gov/vuln/detail/CVE-2026-10634


7. CVE-2026-10635

Insufficient validation of untrusted input in InterestGroups in Google Chrome prior to 149.0.7827.53 allowed a remote attacker who had compromised the renderer process to potentially perform a sandbox escape via a crafted HTML page. (Chromium security severity: High)

https://nvd.nist.gov/vuln/detail/CVE-2026-10635


8. CVE-2026-10638

Insufficient validation of untrusted input in InterestGroups in Google Chrome prior to 149.0.7827.53 allowed a remote attacker who had compromised the renderer process to potentially perform a sandbox escape via a crafted HTML page. (Chromium security severity: High)

https://nvd.nist.gov/vuln/detail/CVE-2026-10638


9. CVE-2026-10970

Insufficient validation of untrusted input in InterestGroups in Google Chrome prior to 149.0.7827.53 allowed a remote attacker who had compromised the renderer process to potentially perform a sandbox escape via a crafted HTML page. (Chromium security severity: High)

https://nvd.nist.gov/vuln/detail/CVE-2026-10970


10. CVE-2026-10971

Insufficient validation of untrusted input in InterestGroups in Google Chrome prior to 149.0.7827.53 allowed a remote attacker who had compromised the renderer process to potentially perform a sandbox escape via a crafted HTML page. (Chromium security severity: High)

https://nvd.nist.gov/vuln/detail/CVE-2026-10971


"SOS
CVE Top 10

The SOS Intelligence CVE Chatter Weekly Top Ten – 26 October 2026


This weekly blog post is from via our unique intelligence collection pipelines. We are your eyes and ears online, including the Dark Web.

There are thousands of vulnerability discussions each week. SOS Intelligence gathers a list of the most discussed Common Vulnerabilities and Exposures (CVE) online for the previous week.

We make every effort to ensure the accuracy of the data presented. As this is an automated process some errors may creep in.

If you are feeling generous please do make us aware of anything you spot, feel free to follow us on Twitter @sosintel and DM us. Thank you!


1.  CVE-2020-3259

A vulnerability in the web services interface of Cisco Adaptive Security Appliance (ASA) Software and Cisco Firepower Threat Defense (FTD) Software could allow an unauthenticated, remote attacker to retrieve memory contents on an affected device, which could lead to the disclosure of confidential information. The vulnerability is due to a buffer tracking issue when the software parses invalid URLs that are requested from the web services interface. An attacker could exploit this vulnerability by sending a crafted GET request to the web services interface. A successful exploit could allow the attacker to retrieve memory contents, which could lead to the disclosure of confidential information. Note: This vulnerability affects only specific AnyConnect and WebVPN configurations. For more information, see the Vulnerable Products section.

https://nvd.nist.gov/vuln/detail/CVE-2020-3259


2. CVE-2024-40766

A vulnerability in the web services interface of Cisco Adaptive Security Appliance (ASA) Software and Cisco Firepower Threat Defense (FTD) Software could allow an unauthenticated, remote attacker to retrieve memory contents on an affected device, which could lead to the disclosure of confidential information. The vulnerability is due to a buffer tracking issue when the software parses invalid URLs that are requested from the web services interface. An attacker could exploit this vulnerability by sending a crafted GET request to the web services interface. A successful exploit could allow the attacker to retrieve memory contents, which could lead to the disclosure of confidential information. Note: This vulnerability affects only specific AnyConnect and WebVPN configurations. For more information, see the Vulnerable Products section.

https://nvd.nist.gov/vuln/detail/CVE-2024-40766


3. CVE-2023-20269

A vulnerability in the web services interface of Cisco Adaptive Security Appliance (ASA) Software and Cisco Firepower Threat Defense (FTD) Software could allow an unauthenticated, remote attacker to retrieve memory contents on an affected device, which could lead to the disclosure of confidential information. The vulnerability is due to a buffer tracking issue when the software parses invalid URLs that are requested from the web services interface. An attacker could exploit this vulnerability by sending a crafted GET request to the web services interface. A successful exploit could allow the attacker to retrieve memory contents, which could lead to the disclosure of confidential information. Note: This vulnerability affects only specific AnyConnect and WebVPN configurations. For more information, see the Vulnerable Products section.

https://nvd.nist.gov/vuln/detail/CVE-2023-20269


4. CVE-2024-40711

A vulnerability in the web services interface of Cisco Adaptive Security Appliance (ASA) Software and Cisco Firepower Threat Defense (FTD) Software could allow an unauthenticated, remote attacker to retrieve memory contents on an affected device, which could lead to the disclosure of confidential information. The vulnerability is due to a buffer tracking issue when the software parses invalid URLs that are requested from the web services interface. An attacker could exploit this vulnerability by sending a crafted GET request to the web services interface. A successful exploit could allow the attacker to retrieve memory contents, which could lead to the disclosure of confidential information. Note: This vulnerability affects only specific AnyConnect and WebVPN configurations. For more information, see the Vulnerable Products section.

https://nvd.nist.gov/vuln/detail/CVE-2024-40711


5. CVE-2023-27532

A vulnerability in the web services interface of Cisco Adaptive Security Appliance (ASA) Software and Cisco Firepower Threat Defense (FTD) Software could allow an unauthenticated, remote attacker to retrieve memory contents on an affected device, which could lead to the disclosure of confidential information. The vulnerability is due to a buffer tracking issue when the software parses invalid URLs that are requested from the web services interface. An attacker could exploit this vulnerability by sending a crafted GET request to the web services interface. A successful exploit could allow the attacker to retrieve memory contents, which could lead to the disclosure of confidential information. Note: This vulnerability affects only specific AnyConnect and WebVPN configurations. For more information, see the Vulnerable Products section.

https://nvd.nist.gov/vuln/detail/CVE-2023-27532


6. CVE-2015-5477

Strapi through 4.5.5 allows attackers (with access to the admin panel) to discover sensitive user details by exploiting the query filter. The attacker can filter users by columns that contain sensitive information and infer a value from API responses. If the attacker has super admin access, then this can be exploited to discover the password hash and password reset token of all users. If the attacker has admin panel access to an account with permission to access the username and email of API users with a lower privileged role (e.g., Editor or Author), then this can be exploited to discover sensitive information for all API users but not other admin accounts.

https://nvd.nist.gov/vuln/detail/CVE-2015-5477


7. CVE-2026-96890

Strapi through 4.5.5 allows attackers (with access to the admin panel) to discover sensitive user details by exploiting the query filter. The attacker can filter users by columns that contain sensitive information and infer a value from API responses. If the attacker has super admin access, then this can be exploited to discover the password hash and password reset token of all users. If the attacker has admin panel access to an account with permission to access the username and email of API users with a lower privileged role (e.g., Editor or Author), then this can be exploited to discover sensitive information for all API users but not other admin accounts.

https://nvd.nist.gov/vuln/detail/CVE-2026-96890


8. CVE-2026-93675

Strapi through 4.5.5 allows attackers (with access to the admin panel) to discover sensitive user details by exploiting the query filter. The attacker can filter users by columns that contain sensitive information and infer a value from API responses. If the attacker has super admin access, then this can be exploited to discover the password hash and password reset token of all users. If the attacker has admin panel access to an account with permission to access the username and email of API users with a lower privileged role (e.g., Editor or Author), then this can be exploited to discover sensitive information for all API users but not other admin accounts.

https://nvd.nist.gov/vuln/detail/CVE-2026-93675


9. CVE-2026-88771

Strapi through 4.5.5 allows attackers (with access to the admin panel) to discover sensitive user details by exploiting the query filter. The attacker can filter users by columns that contain sensitive information and infer a value from API responses. If the attacker has super admin access, then this can be exploited to discover the password hash and password reset token of all users. If the attacker has admin panel access to an account with permission to access the username and email of API users with a lower privileged role (e.g., Editor or Author), then this can be exploited to discover sensitive information for all API users but not other admin accounts.

https://nvd.nist.gov/vuln/detail/CVE-2026-88771


10. CVE-2026-82531

Strapi through 4.5.5 allows attackers (with access to the admin panel) to discover sensitive user details by exploiting the query filter. The attacker can filter users by columns that contain sensitive information and infer a value from API responses. If the attacker has super admin access, then this can be exploited to discover the password hash and password reset token of all users. If the attacker has admin panel access to an account with permission to access the username and email of API users with a lower privileged role (e.g., Editor or Author), then this can be exploited to discover sensitive information for all API users but not other admin accounts.

https://nvd.nist.gov/vuln/detail/CVE-2026-82531


"SOS
CVE Top 10

The SOS Intelligence CVE Chatter Weekly Top Ten – 19 October 2026


This weekly blog post is from via our unique intelligence collection pipelines. We are your eyes and ears online, including the Dark Web.

There are thousands of vulnerability discussions each week. SOS Intelligence gathers a list of the most discussed Common Vulnerabilities and Exposures (CVE) online for the previous week.

We make every effort to ensure the accuracy of the data presented. As this is an automated process some errors may creep in.

If you are feeling generous please do make us aware of anything you spot, feel free to follow us on Twitter @sosintel and DM us. Thank you!


1.  CVE-2023-34960

A command injection vulnerability in the wsConvertPpt component of Chamilo v1.11.* up to v1.11.18 allows attackers to execute arbitrary commands via a SOAP API call with a crafted PowerPoint name.

https://nvd.nist.gov/vuln/detail/CVE-2023-34960


2. CVE-2021-1931

In the Linux kernel, the following vulnerability has been resolved:

rtmutex: Use waiter::task instead of current in remove_waiter()

remove_waiter() is used by the slowlock paths, but it is also used for
proxy-lock rollback in rt_mutex_start_proxy_lock() when invoked from
futex_requeue().

In the latter case waiter::task is not current, but remove_waiter()
operates on current for the dequeue operation. That results in several
problems:

1) the rbtree dequeue happens without waiter::task::pi_lock being held

2) the waiter task’s pi_blocked_on state is not cleared, which leaves a
dangling pointer primed for UAF around.

3) rt_mutex_adjust_prio_chain() operates on the wrong top priority waiter
task

Use waiter::task instead of current in all related operations in
remove_waiter() to cure those problems.

[ tglx: Fixup rt_mutex_adjust_prio_chain(), add a comment and amend the
changelog ]

https://nvd.nist.gov/vuln/detail/CVE-2021-1931


3. CVE-2023-4622

In the Linux kernel, the following vulnerability has been resolved:

rtmutex: Use waiter::task instead of current in remove_waiter()

remove_waiter() is used by the slowlock paths, but it is also used for
proxy-lock rollback in rt_mutex_start_proxy_lock() when invoked from
futex_requeue().

In the latter case waiter::task is not current, but remove_waiter()
operates on current for the dequeue operation. That results in several
problems:

1) the rbtree dequeue happens without waiter::task::pi_lock being held

2) the waiter task’s pi_blocked_on state is not cleared, which leaves a
dangling pointer primed for UAF around.

3) rt_mutex_adjust_prio_chain() operates on the wrong top priority waiter
task

Use waiter::task instead of current in all related operations in
remove_waiter() to cure those problems.

[ tglx: Fixup rt_mutex_adjust_prio_chain(), add a comment and amend the
changelog ]

https://nvd.nist.gov/vuln/detail/CVE-2023-4622


4. CVE-2024-31317

In the Linux kernel, the following vulnerability has been resolved:

rtmutex: Use waiter::task instead of current in remove_waiter()

remove_waiter() is used by the slowlock paths, but it is also used for
proxy-lock rollback in rt_mutex_start_proxy_lock() when invoked from
futex_requeue().

In the latter case waiter::task is not current, but remove_waiter()
operates on current for the dequeue operation. That results in several
problems:

1) the rbtree dequeue happens without waiter::task::pi_lock being held

2) the waiter task’s pi_blocked_on state is not cleared, which leaves a
dangling pointer primed for UAF around.

3) rt_mutex_adjust_prio_chain() operates on the wrong top priority waiter
task

Use waiter::task instead of current in all related operations in
remove_waiter() to cure those problems.

[ tglx: Fixup rt_mutex_adjust_prio_chain(), add a comment and amend the
changelog ]

https://nvd.nist.gov/vuln/detail/CVE-2024-31317


5. CVE-2024-50302

In the Linux kernel, the following vulnerability has been resolved:

rtmutex: Use waiter::task instead of current in remove_waiter()

remove_waiter() is used by the slowlock paths, but it is also used for
proxy-lock rollback in rt_mutex_start_proxy_lock() when invoked from
futex_requeue().

In the latter case waiter::task is not current, but remove_waiter()
operates on current for the dequeue operation. That results in several
problems:

1) the rbtree dequeue happens without waiter::task::pi_lock being held

2) the waiter task’s pi_blocked_on state is not cleared, which leaves a
dangling pointer primed for UAF around.

3) rt_mutex_adjust_prio_chain() operates on the wrong top priority waiter
task

Use waiter::task instead of current in all related operations in
remove_waiter() to cure those problems.

[ tglx: Fixup rt_mutex_adjust_prio_chain(), add a comment and amend the
changelog ]

https://nvd.nist.gov/vuln/detail/CVE-2024-50302


6. CVE-2024-53197

In the Linux kernel, the following vulnerability has been resolved:

rtmutex: Use waiter::task instead of current in remove_waiter()

remove_waiter() is used by the slowlock paths, but it is also used for
proxy-lock rollback in rt_mutex_start_proxy_lock() when invoked from
futex_requeue().

In the latter case waiter::task is not current, but remove_waiter()
operates on current for the dequeue operation. That results in several
problems:

1) the rbtree dequeue happens without waiter::task::pi_lock being held

2) the waiter task’s pi_blocked_on state is not cleared, which leaves a
dangling pointer primed for UAF around.

3) rt_mutex_adjust_prio_chain() operates on the wrong top priority waiter
task

Use waiter::task instead of current in all related operations in
remove_waiter() to cure those problems.

[ tglx: Fixup rt_mutex_adjust_prio_chain(), add a comment and amend the
changelog ]

https://nvd.nist.gov/vuln/detail/CVE-2024-53197


7. CVE-2025-21479

In the Linux kernel, the following vulnerability has been resolved:

rtmutex: Use waiter::task instead of current in remove_waiter()

remove_waiter() is used by the slowlock paths, but it is also used for
proxy-lock rollback in rt_mutex_start_proxy_lock() when invoked from
futex_requeue().

In the latter case waiter::task is not current, but remove_waiter()
operates on current for the dequeue operation. That results in several
problems:

1) the rbtree dequeue happens without waiter::task::pi_lock being held

2) the waiter task’s pi_blocked_on state is not cleared, which leaves a
dangling pointer primed for UAF around.

3) rt_mutex_adjust_prio_chain() operates on the wrong top priority waiter
task

Use waiter::task instead of current in all related operations in
remove_waiter() to cure those problems.

[ tglx: Fixup rt_mutex_adjust_prio_chain(), add a comment and amend the
changelog ]

https://nvd.nist.gov/vuln/detail/CVE-2025-21479


8. CVE-2026-10248

As part of Cisco’s ongoing commitment to proactive security and product quality, the engineering team for Cisco License On-Prem, formerly Cisco Smart Software Manager On-Prem (SSM On-Prem), has conducted a comprehensive internal security review. This review resulted in software hardening releases that address multiple internally discovered vulnerabilities.

The vulnerabilities tracked by CVE-2026-76482 are related to issues with improper input verification that are grouped under the Common Weakness Enumeration (CWE) Pillar CWE-347.

https://nvd.nist.gov/vuln/detail/CVE-2026-10248


9. CVE-2026-10249

As part of Cisco’s ongoing commitment to proactive security and product quality, the engineering team for Cisco License On-Prem, formerly Cisco Smart Software Manager On-Prem (SSM On-Prem), has conducted a comprehensive internal security review. This review resulted in software hardening releases that address multiple internally discovered vulnerabilities.

The vulnerabilities tracked by CVE-2026-76482 are related to issues with improper input verification that are grouped under the Common Weakness Enumeration (CWE) Pillar CWE-347.

https://nvd.nist.gov/vuln/detail/CVE-2026-10249


10. CVE-2026-10428

Vulnerability in NetScaler ADC and NetScaler Gateway.

This issue affects ADC: before 14.1-73.41, before 13.1-64.28, before 14.1-73.41 FIPS, and before 13.1-37.282; Gateway: before 14.1-73.41 and before 13.1-64.28.

https://nvd.nist.gov/vuln/detail/CVE-2026-10428


"SOS
CVE Top 10

The SOS Intelligence CVE Chatter Weekly Top Ten –


This weekly blog post is from via our unique intelligence collection pipelines. We are your eyes and ears online, including the Dark Web.

There are thousands of vulnerability discussions each week. SOS Intelligence gathers a list of the most discussed Common Vulnerabilities and Exposures (CVE) online for the previous week.

We make every effort to ensure the accuracy of the data presented. As this is an automated process some errors may creep in.

If you are feeling generous please do make us aware of anything you spot, feel free to follow us on Twitter @sosintel and DM us. Thank you!


1. 

https://nvd.nist.gov/vuln/detail/


2.

https://nvd.nist.gov/vuln/detail/


3.

https://nvd.nist.gov/vuln/detail/


4.

https://nvd.nist.gov/vuln/detail/


5.

https://nvd.nist.gov/vuln/detail/


6.

https://nvd.nist.gov/vuln/detail/


7.

https://nvd.nist.gov/vuln/detail/


8.

https://nvd.nist.gov/vuln/detail/


9.

https://nvd.nist.gov/vuln/detail/


10.

https://nvd.nist.gov/vuln/detail/


"Ransomware
Opinion, Ransomware

Ransomware Leak-Site Activity More Than Doubles Year on Year: What It Means for Manufacturing

SOS Intelligence data shows the manufacturing sector continues to be targeted significantly in observed ransomware leak-site activity, while the wider ecosystem is considerably busier and more fragmented than a year ago.

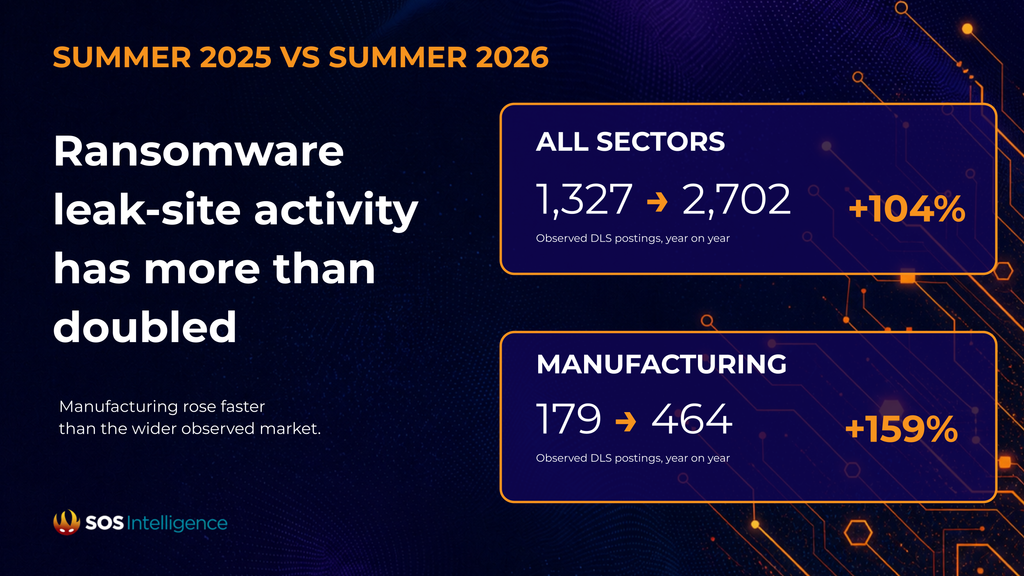
Between June and August 2026, SOS Intelligence recorded 2,702 organisations named on ransomware data-leak sites (DLSs), compared with 1,327 over the same period in 2025, an increase of approximately 104%. This matters not only because of direct organisational exposure, but because disruption can also have knock-on effects across connected supply chains.

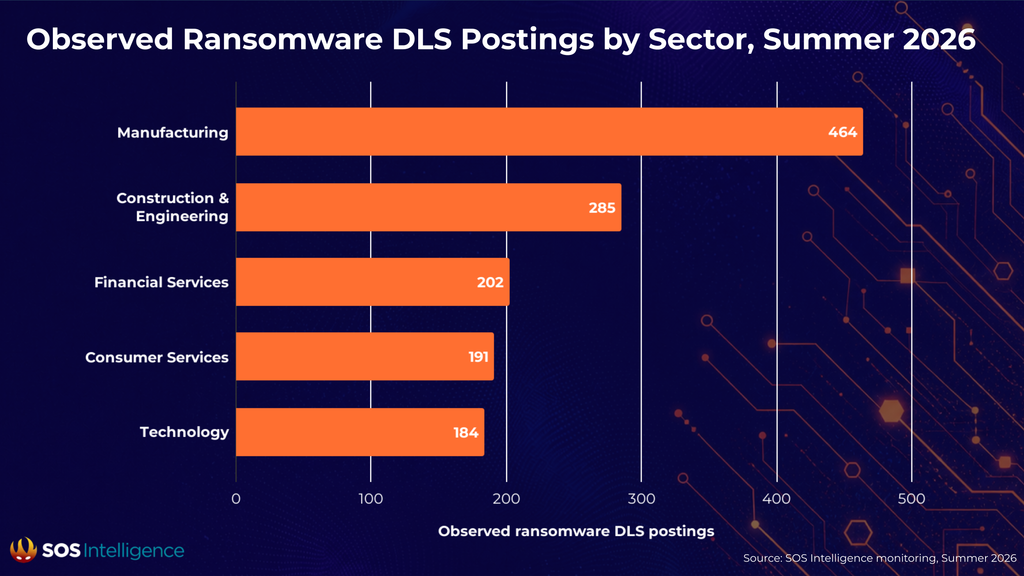
Manufacturing ransomware leak postings rose even faster year-on-year, from 179 to 464, taking the sector’s share of observed postings from around 13.5% to 17.2%.

Comparison of summer 2025 and 2026 ransomware leak-site activity, showing overall postings more than doubled and manufacturing posts rose even faster.

August set a new high: 1,081 organisations were named during the month, the highest figure in SOS Intelligence’s records. SOS also saw 80 different threat groups posting in August, another record.

Across the summer, SOS Intelligence observed 36 dark web ransomware threat groups that had not previously posted, responsible for 520 DLS postings, or 19.2% of the summer total. Some are likely to be rebrands rather than genuinely new groups, but even with that caveat, the ransomware ecosystem is clearly becoming more fragmented.

For manufacturing leaders, the important point is the sector’s sustained level of exposure. Manufacturing remains the sector with the highest number of observed ransomware DLS postings, and its year-on-year increase has outpaced the wider ransomware market.

horizontal bar chart showing observed ransomware DLS postings by sector for summer 2026. Manufacturing: 464 postings, Construction & engineering: 285 postings, Financial services: 202 postings, Consumer services: 191 postings, Technology: 184 postings.

That’s not the same as a sudden summer shift towards manufacturing. Postings rose 13.7% from spring to summer, only slightly ahead of the 12.3% increase across all observed postings. The important context is the sector’s starting position: manufacturing is already carrying a high level of observed exposure within a ransomware market that is expanding and changing quickly.

Higher ransomware activity is only part of the picture. Security teams also need to understand which groups are active, where activity is concentrating and how those patterns are shifting. Continuous threat monitoring and analyst-led intelligence can help teams keep that view current and prioritise the activity most relevant to their organisation.

SOS Intelligence will continue to track how this cyber threat environment is developing across ransomware groups, sectors and regions. Explore more SOS Intelligence analysis on ransomware, including what the latest activity means for manufacturing organisations.

Data note: Figures refer to organisations publicly named on ransomware data-leak sites and do not represent the full ransomware market.

"SOS
CVE Top 10

The SOS Intelligence CVE Chatter Weekly Top Ten – 31 August 2026


This weekly blog post is from via our unique intelligence collection pipelines. We are your eyes and ears online, including the Dark Web.

There are thousands of vulnerability discussions each week. SOS Intelligence gathers a list of the most discussed Common Vulnerabilities and Exposures (CVE) online for the previous week.

We make every effort to ensure the accuracy of the data presented. As this is an automated process some errors may creep in.

If you are feeling generous please do make us aware of anything you spot, feel free to follow us on Twitter @sosintel and DM us. Thank you!


1.  CVE-2026-1296

The Frontend Post Submission Manager Lite plugin for WordPress is vulnerable to Open Redirection in all versions up to, and including, 1.2.7 due to insufficient validation on the ‘requested_page’ POST parameter in the verify_username_password function. This makes it possible for unauthenticated attackers to redirect users to potentially malicious sites if they can successfully trick them into performing an action such as clicking on a link.

https://nvd.nist.gov/vuln/detail/CVE-2026-1296


2. CVE-2024-1234

XWiki Platform is a generic wiki platform offering runtime services for applications built on top of it. Any guest can perform arbitrary remote code execution through a request to `SolrSearch`. This impacts the confidentiality, integrity and availability of the whole XWiki installation. To reproduce on an instance, without being logged in, go to `/xwiki/bin/get/Main/SolrSearch?media=rss&text=%7D%7D%7D%7B%7Basync%20async%3Dfalse%7D%7D%7B%7Bgroovy%7D%7Dprintln%28″Hello%20from”%20%2B%20″%20search%20text%3A”%20%2B%20%2823%20%2B%2019%29%29%7B%7B%2Fgroovy%7D%7D%7B%7B%2Fasync%7D%7D%20`. If there is an output, and the title of the RSS feed contains `Hello from search text:42`, then the instance is vulnerable. This vulnerability has been patched in XWiki 15.10.11, 16.4.1 and 16.5.0RC1. Users are advised to upgrade. Users unable to upgrade may edit `Main.SolrSearchMacros` in `SolrSearchMacros.xml` on line 955 to match the `rawResponse` macro in `macros.vm#L2824` with a content type of `application/xml`, instead of simply outputting the content of the feed.

https://nvd.nist.gov/vuln/detail/CVE-2024-1234


3. CVE-2024-5678

XWiki Platform is a generic wiki platform offering runtime services for applications built on top of it. Any guest can perform arbitrary remote code execution through a request to `SolrSearch`. This impacts the confidentiality, integrity and availability of the whole XWiki installation. To reproduce on an instance, without being logged in, go to `/xwiki/bin/get/Main/SolrSearch?media=rss&text=%7D%7D%7D%7B%7Basync%20async%3Dfalse%7D%7D%7B%7Bgroovy%7D%7Dprintln%28″Hello%20from”%20%2B%20″%20search%20text%3A”%20%2B%20%2823%20%2B%2019%29%29%7B%7B%2Fgroovy%7D%7D%7B%7B%2Fasync%7D%7D%20`. If there is an output, and the title of the RSS feed contains `Hello from search text:42`, then the instance is vulnerable. This vulnerability has been patched in XWiki 15.10.11, 16.4.1 and 16.5.0RC1. Users are advised to upgrade. Users unable to upgrade may edit `Main.SolrSearchMacros` in `SolrSearchMacros.xml` on line 955 to match the `rawResponse` macro in `macros.vm#L2824` with a content type of `application/xml`, instead of simply outputting the content of the feed.

https://nvd.nist.gov/vuln/detail/CVE-2024-5678


4. CVE-2024-8856

XWiki Platform is a generic wiki platform offering runtime services for applications built on top of it. Any guest can perform arbitrary remote code execution through a request to `SolrSearch`. This impacts the confidentiality, integrity and availability of the whole XWiki installation. To reproduce on an instance, without being logged in, go to `/xwiki/bin/get/Main/SolrSearch?media=rss&text=%7D%7D%7D%7B%7Basync%20async%3Dfalse%7D%7D%7B%7Bgroovy%7D%7Dprintln%28″Hello%20from”%20%2B%20″%20search%20text%3A”%20%2B%20%2823%20%2B%2019%29%29%7B%7B%2Fgroovy%7D%7D%7B%7B%2Fasync%7D%7D%20`. If there is an output, and the title of the RSS feed contains `Hello from search text:42`, then the instance is vulnerable. This vulnerability has been patched in XWiki 15.10.11, 16.4.1 and 16.5.0RC1. Users are advised to upgrade. Users unable to upgrade may edit `Main.SolrSearchMacros` in `SolrSearchMacros.xml` on line 955 to match the `rawResponse` macro in `macros.vm#L2824` with a content type of `application/xml`, instead of simply outputting the content of the feed.

https://nvd.nist.gov/vuln/detail/CVE-2024-8856


5. CVE-2025-24813

XWiki Platform is a generic wiki platform offering runtime services for applications built on top of it. Any guest can perform arbitrary remote code execution through a request to `SolrSearch`. This impacts the confidentiality, integrity and availability of the whole XWiki installation. To reproduce on an instance, without being logged in, go to `/xwiki/bin/get/Main/SolrSearch?media=rss&text=%7D%7D%7D%7B%7Basync%20async%3Dfalse%7D%7D%7B%7Bgroovy%7D%7Dprintln%28″Hello%20from”%20%2B%20″%20search%20text%3A”%20%2B%20%2823%20%2B%2019%29%29%7B%7B%2Fgroovy%7D%7D%7B%7B%2Fasync%7D%7D%20`. If there is an output, and the title of the RSS feed contains `Hello from search text:42`, then the instance is vulnerable. This vulnerability has been patched in XWiki 15.10.11, 16.4.1 and 16.5.0RC1. Users are advised to upgrade. Users unable to upgrade may edit `Main.SolrSearchMacros` in `SolrSearchMacros.xml` on line 955 to match the `rawResponse` macro in `macros.vm#L2824` with a content type of `application/xml`, instead of simply outputting the content of the feed.

https://nvd.nist.gov/vuln/detail/CVE-2025-24813


6. CVE-2025-24893

XWiki Platform is a generic wiki platform offering runtime services for applications built on top of it. Any guest can perform arbitrary remote code execution through a request to `SolrSearch`. This impacts the confidentiality, integrity and availability of the whole XWiki installation. To reproduce on an instance, without being logged in, go to `/xwiki/bin/get/Main/SolrSearch?media=rss&text=%7D%7D%7D%7B%7Basync%20async%3Dfalse%7D%7D%7B%7Bgroovy%7D%7Dprintln%28″Hello%20from”%20%2B%20″%20search%20text%3A”%20%2B%20%2823%20%2B%2019%29%29%7B%7B%2Fgroovy%7D%7D%7B%7B%2Fasync%7D%7D%20`. If there is an output, and the title of the RSS feed contains `Hello from search text:42`, then the instance is vulnerable. This vulnerability has been patched in XWiki 15.10.11, 16.4.1 and 16.5.0RC1. Users are advised to upgrade. Users unable to upgrade may edit `Main.SolrSearchMacros` in `SolrSearchMacros.xml` on line 955 to match the `rawResponse` macro in `macros.vm#L2824` with a content type of `application/xml`, instead of simply outputting the content of the feed.

https://nvd.nist.gov/vuln/detail/CVE-2025-24893


7. CVE-2025-2563

XWiki Platform is a generic wiki platform offering runtime services for applications built on top of it. Any guest can perform arbitrary remote code execution through a request to `SolrSearch`. This impacts the confidentiality, integrity and availability of the whole XWiki installation. To reproduce on an instance, without being logged in, go to `/xwiki/bin/get/Main/SolrSearch?media=rss&text=%7D%7D%7D%7B%7Basync%20async%3Dfalse%7D%7D%7B%7Bgroovy%7D%7Dprintln%28″Hello%20from”%20%2B%20″%20search%20text%3A”%20%2B%20%2823%20%2B%2019%29%29%7B%7B%2Fgroovy%7D%7D%7B%7B%2Fasync%7D%7D%20`. If there is an output, and the title of the RSS feed contains `Hello from search text:42`, then the instance is vulnerable. This vulnerability has been patched in XWiki 15.10.11, 16.4.1 and 16.5.0RC1. Users are advised to upgrade. Users unable to upgrade may edit `Main.SolrSearchMacros` in `SolrSearchMacros.xml` on line 955 to match the `rawResponse` macro in `macros.vm#L2824` with a content type of `application/xml`, instead of simply outputting the content of the feed.

https://nvd.nist.gov/vuln/detail/CVE-2025-2563


8. CVE-2025-54253

XWiki Platform is a generic wiki platform offering runtime services for applications built on top of it. Any guest can perform arbitrary remote code execution through a request to `SolrSearch`. This impacts the confidentiality, integrity and availability of the whole XWiki installation. To reproduce on an instance, without being logged in, go to `/xwiki/bin/get/Main/SolrSearch?media=rss&text=%7D%7D%7D%7B%7Basync%20async%3Dfalse%7D%7D%7B%7Bgroovy%7D%7Dprintln%28″Hello%20from”%20%2B%20″%20search%20text%3A”%20%2B%20%2823%20%2B%2019%29%29%7B%7B%2Fgroovy%7D%7D%7B%7B%2Fasync%7D%7D%20`. If there is an output, and the title of the RSS feed contains `Hello from search text:42`, then the instance is vulnerable. This vulnerability has been patched in XWiki 15.10.11, 16.4.1 and 16.5.0RC1. Users are advised to upgrade. Users unable to upgrade may edit `Main.SolrSearchMacros` in `SolrSearchMacros.xml` on line 955 to match the `rawResponse` macro in `macros.vm#L2824` with a content type of `application/xml`, instead of simply outputting the content of the feed.

https://nvd.nist.gov/vuln/detail/CVE-2025-54253


9. CVE-2026-0594

XWiki Platform is a generic wiki platform offering runtime services for applications built on top of it. Any guest can perform arbitrary remote code execution through a request to `SolrSearch`. This impacts the confidentiality, integrity and availability of the whole XWiki installation. To reproduce on an instance, without being logged in, go to `/xwiki/bin/get/Main/SolrSearch?media=rss&text=%7D%7D%7D%7B%7Basync%20async%3Dfalse%7D%7D%7B%7Bgroovy%7D%7Dprintln%28″Hello%20from”%20%2B%20″%20search%20text%3A”%20%2B%20%2823%20%2B%2019%29%29%7B%7B%2Fgroovy%7D%7D%7B%7B%2Fasync%7D%7D%20`. If there is an output, and the title of the RSS feed contains `Hello from search text:42`, then the instance is vulnerable. This vulnerability has been patched in XWiki 15.10.11, 16.4.1 and 16.5.0RC1. Users are advised to upgrade. Users unable to upgrade may edit `Main.SolrSearchMacros` in `SolrSearchMacros.xml` on line 955 to match the `rawResponse` macro in `macros.vm#L2824` with a content type of `application/xml`, instead of simply outputting the content of the feed.

https://nvd.nist.gov/vuln/detail/CVE-2026-0594


10. CVE-2026-0770

XWiki Platform is a generic wiki platform offering runtime services for applications built on top of it. Any guest can perform arbitrary remote code execution through a request to `SolrSearch`. This impacts the confidentiality, integrity and availability of the whole XWiki installation. To reproduce on an instance, without being logged in, go to `/xwiki/bin/get/Main/SolrSearch?media=rss&text=%7D%7D%7D%7B%7Basync%20async%3Dfalse%7D%7D%7B%7Bgroovy%7D%7Dprintln%28″Hello%20from”%20%2B%20″%20search%20text%3A”%20%2B%20%2823%20%2B%2019%29%29%7B%7B%2Fgroovy%7D%7D%7B%7B%2Fasync%7D%7D%20`. If there is an output, and the title of the RSS feed contains `Hello from search text:42`, then the instance is vulnerable. This vulnerability has been patched in XWiki 15.10.11, 16.4.1 and 16.5.0RC1. Users are advised to upgrade. Users unable to upgrade may edit `Main.SolrSearchMacros` in `SolrSearchMacros.xml` on line 955 to match the `rawResponse` macro in `macros.vm#L2824` with a content type of `application/xml`, instead of simply outputting the content of the feed.

https://nvd.nist.gov/vuln/detail/CVE-2026-0770


"SOS
CVE Top 10

The SOS Intelligence CVE Chatter Weekly Top Ten – 24 August 2026


This weekly blog post is from via our unique intelligence collection pipelines. We are your eyes and ears online, including the Dark Web.

There are thousands of vulnerability discussions each week. SOS Intelligence gathers a list of the most discussed Common Vulnerabilities and Exposures (CVE) online for the previous week.

We make every effort to ensure the accuracy of the data presented. As this is an automated process some errors may creep in.

If you are feeling generous please do make us aware of anything you spot, feel free to follow us on Twitter @sosintel and DM us. Thank you!


1.  CVE-2026-59310

A vulnerability in the zip archive parser of ClamAV could allow an unauthenticated, remote attacker to cause a DoS condition on an affected device.

This vulnerability is due to improper memory handling when processing content in zip files during scanning. An attacker could exploit this vulnerability by submitting a crafted zip file for scanning. A successful exploit could allow the attacker to cause the ClamAV scanning process to terminate as a result of a memory double-free, resulting in a DoS condition on the affected software.

https://nvd.nist.gov/vuln/detail/CVE-2026-59310


2. CVE-2026-65400

A vulnerability in the zip archive parser of ClamAV could allow an unauthenticated, remote attacker to cause a DoS condition on an affected device.

This vulnerability is due to improper memory handling when processing content in zip files during scanning. An attacker could exploit this vulnerability by submitting a crafted zip file for scanning. A successful exploit could allow the attacker to cause the ClamAV scanning process to terminate as a result of a memory double-free, resulting in a DoS condition on the affected software.

https://nvd.nist.gov/vuln/detail/CVE-2026-65400


3. CVE-2026-14863

A vulnerability in the zip archive parser of ClamAV could allow an unauthenticated, remote attacker to cause a DoS condition on an affected device.

This vulnerability is due to improper memory handling when processing content in zip files during scanning. An attacker could exploit this vulnerability by submitting a crafted zip file for scanning. A successful exploit could allow the attacker to cause the ClamAV scanning process to terminate as a result of a memory double-free, resulting in a DoS condition on the affected software.

https://nvd.nist.gov/vuln/detail/CVE-2026-14863


4. CVE-2026-18412

A vulnerability in the zip archive parser of ClamAV could allow an unauthenticated, remote attacker to cause a DoS condition on an affected device.

This vulnerability is due to improper memory handling when processing content in zip files during scanning. An attacker could exploit this vulnerability by submitting a crafted zip file for scanning. A successful exploit could allow the attacker to cause the ClamAV scanning process to terminate as a result of a memory double-free, resulting in a DoS condition on the affected software.

https://nvd.nist.gov/vuln/detail/CVE-2026-18412


5. CVE-2026-20337

A vulnerability in the zip archive parser of ClamAV could allow an unauthenticated, remote attacker to cause a DoS condition on an affected device.

This vulnerability is due to improper memory handling when processing content in zip files during scanning. An attacker could exploit this vulnerability by submitting a crafted zip file for scanning. A successful exploit could allow the attacker to cause the ClamAV scanning process to terminate as a result of a memory double-free, resulting in a DoS condition on the affected software.

https://nvd.nist.gov/vuln/detail/CVE-2026-20337


6. CVE-2026-20338

A vulnerability in the zip archive parser of ClamAV could allow an unauthenticated, remote attacker to cause a DoS condition on an affected device.

This vulnerability is due to improper memory handling when processing content in zip files during scanning. An attacker could exploit this vulnerability by submitting a crafted zip file for scanning. A successful exploit could allow the attacker to cause the ClamAV scanning process to terminate as a result of a memory double-free, resulting in a DoS condition on the affected software.

https://nvd.nist.gov/vuln/detail/CVE-2026-20338


7. CVE-2026-20339

A vulnerability in the zip archive parser of ClamAV could allow an unauthenticated, remote attacker to cause a DoS condition on an affected device.

This vulnerability is due to improper memory handling when processing content in zip files during scanning. An attacker could exploit this vulnerability by submitting a crafted zip file for scanning. A successful exploit could allow the attacker to cause the ClamAV scanning process to terminate as a result of a memory double-free, resulting in a DoS condition on the affected software.

https://nvd.nist.gov/vuln/detail/CVE-2026-20339


8. CVE-2026-20345

A vulnerability in the zip archive parser of ClamAV could allow an unauthenticated, remote attacker to cause a DoS condition on an affected device.

This vulnerability is due to improper memory handling when processing content in zip files during scanning. An attacker could exploit this vulnerability by submitting a crafted zip file for scanning. A successful exploit could allow the attacker to cause the ClamAV scanning process to terminate as a result of a memory double-free, resulting in a DoS condition on the affected software.

https://nvd.nist.gov/vuln/detail/CVE-2026-20345


9. CVE-2026-20346

A vulnerability in the zip archive parser of ClamAV could allow an unauthenticated, remote attacker to cause a DoS condition on an affected device.

This vulnerability is due to improper memory handling when processing content in zip files during scanning. An attacker could exploit this vulnerability by submitting a crafted zip file for scanning. A successful exploit could allow the attacker to cause the ClamAV scanning process to terminate as a result of a memory double-free, resulting in a DoS condition on the affected software.

https://nvd.nist.gov/vuln/detail/CVE-2026-20346


10. CVE-2026-20347

A vulnerability in the zip archive parser of ClamAV could allow an unauthenticated, remote attacker to cause a DoS condition on an affected device.

This vulnerability is due to improper memory handling when processing content in zip files during scanning. An attacker could exploit this vulnerability by submitting a crafted zip file for scanning. A successful exploit could allow the attacker to cause the ClamAV scanning process to terminate as a result of a memory double-free, resulting in a DoS condition on the affected software.

https://nvd.nist.gov/vuln/detail/CVE-2026-20347


"SOS
CVE Top 10

The SOS Intelligence CVE Chatter Weekly Top Ten – 17 August 2026


This weekly blog post is from via our unique intelligence collection pipelines. We are your eyes and ears online, including the Dark Web.

There are thousands of vulnerability discussions each week. SOS Intelligence gathers a list of the most discussed Common Vulnerabilities and Exposures (CVE) online for the previous week.

We make every effort to ensure the accuracy of the data presented. As this is an automated process some errors may creep in.

If you are feeling generous please do make us aware of anything you spot, feel free to follow us on Twitter @sosintel and DM us. Thank you!


1.  CVE-2024-51479

Axios is a promise based HTTP client for the browser and Node.js. Prior to 1.15.0 and 0.31.0, Axios does not correctly handle hostname normalization when checking NO_PROXY rules. Requests to loopback addresses like localhost. (with a trailing dot) or [::1] (IPv6 literal) skip NO_PROXY matching and go through the configured proxy. This goes against what developers expect and lets attackers force requests through a proxy, even if NO_PROXY is set up to protect loopback or internal services. This issue leads to the possibility of proxy bypass and SSRF vulnerabilities allowing attackers to reach sensitive loopback or internal services despite the configured protections. This vulnerability is fixed in 1.15.0 and 0.31.0.

https://nvd.nist.gov/vuln/detail/CVE-2024-51479


2. CVE-2025-62718

Axios is a promise based HTTP client for the browser and Node.js. Prior to 1.15.0 and 0.31.0, Axios does not correctly handle hostname normalization when checking NO_PROXY rules. Requests to loopback addresses like localhost. (with a trailing dot) or [::1] (IPv6 literal) skip NO_PROXY matching and go through the configured proxy. This goes against what developers expect and lets attackers force requests through a proxy, even if NO_PROXY is set up to protect loopback or internal services. This issue leads to the possibility of proxy bypass and SSRF vulnerabilities allowing attackers to reach sensitive loopback or internal services despite the configured protections. This vulnerability is fixed in 1.15.0 and 0.31.0.

https://nvd.nist.gov/vuln/detail/CVE-2025-62718


3. CVE-2026-32315

motionEye (mEye) is an online interface for motion software, a video surveillance program with motion detection. Versions prior to 0.44.0 create the configuration file /etc/motioneye/motion.conf with 644 permissions (-rw-r–r–), making it readable by any local user on the system. This file contains sensitive data including the admin password hash, which can be leveraged by other vulnerabilities to escalate privileges. Additionally, per-camera configuration files (camera-*.conf) are also created with the same 644 permissions, potentially exposing camera-specific credentials and settings. The exposed SHA1 admin password hash can be cracked offline to recover the plaintext password, used directly to forge authenticated admin API requests via the signature authentication weakness (GHSA-45h7-499j-7ww3), and chained with the OS command injection flaw (CVE-2025-60787) to escalate a local unprivileged user to the Motion daemon user (often root), enabling full system compromise. This issue has been fixed in version 0.44.0.

https://nvd.nist.gov/vuln/detail/CVE-2026-32315


4. CVE-2019-20790

OpenDMARC through 1.3.2 and 1.4.x allows attacks that inject authentication results to provide false information about the domain that originated an e-mail message. This is caused by incorrect parsing and interpretation of SPF/DKIM authentication results, as demonstrated by the example.net(.example.com substring.

https://nvd.nist.gov/vuln/detail/CVE-2019-20790


5. CVE-2020-12272

OpenDMARC through 1.3.2 and 1.4.x allows attacks that inject authentication results to provide false information about the domain that originated an e-mail message. This is caused by incorrect parsing and interpretation of SPF/DKIM authentication results, as demonstrated by the example.net(.example.com substring.

https://nvd.nist.gov/vuln/detail/CVE-2020-12272


6. CVE-2026-60137

WordPress 6.8.x before 6.8.6, 6.9.x before 6.9.5, and 7.0.x before 7.0.2 does not properly sanitise the author__not_in parameter of WP_Query, which could allow SQL Injection when a plugin or theme passes untrusted input to the parameter.

https://nvd.nist.gov/vuln/detail/CVE-2026-60137


7. CVE-2026-63030

WordPress 6.8.x before 6.8.6, 6.9.x before 6.9.5, and 7.0.x before 7.0.2 does not properly sanitise the author__not_in parameter of WP_Query, which could allow SQL Injection when a plugin or theme passes untrusted input to the parameter.

https://nvd.nist.gov/vuln/detail/CVE-2026-63030


8. CVE-2019-11090

STMicroelectronics ST33TPHF2ESPI TPM devices before 2019-09-12 allow attackers to extract the ECDSA private key via a side-channel timing attack because ECDSA scalar multiplication is mishandled, aka TPM-FAIL.

https://nvd.nist.gov/vuln/detail/CVE-2019-11090


9. CVE-2019-16863

STMicroelectronics ST33TPHF2ESPI TPM devices before 2019-09-12 allow attackers to extract the ECDSA private key via a side-channel timing attack because ECDSA scalar multiplication is mishandled, aka TPM-FAIL.

https://nvd.nist.gov/vuln/detail/CVE-2019-16863


10. CVE-2023-1017

STMicroelectronics ST33TPHF2ESPI TPM devices before 2019-09-12 allow attackers to extract the ECDSA private key via a side-channel timing attack because ECDSA scalar multiplication is mishandled, aka TPM-FAIL.

https://nvd.nist.gov/vuln/detail/CVE-2023-1017


"SOS
CVE Top 10

The SOS Intelligence CVE Chatter Weekly Top Ten – 13 July 2026


This weekly blog post is from via our unique intelligence collection pipelines. We are your eyes and ears online, including the Dark Web.

There are thousands of vulnerability discussions each week. SOS Intelligence gathers a list of the most discussed Common Vulnerabilities and Exposures (CVE) online for the previous week.

We make every effort to ensure the accuracy of the data presented. As this is an automated process some errors may creep in.

If you are feeling generous please do make us aware of anything you spot, feel free to follow us on Twitter @sosintel and DM us. Thank you!


1.  CVE-2020-1938

A path traversal vulnerability affecting the Windows version of WinRAR allows the attackers to execute arbitrary code by crafting malicious archive files. This vulnerability was exploited in the wild and was discovered by Anton Cherepanov, Peter Košinár, and Peter Strýček
from ESET.

https://nvd.nist.gov/vuln/detail/CVE-2020-1938


2. CVE-2022-21227

A path traversal vulnerability affecting the Windows version of WinRAR allows the attackers to execute arbitrary code by crafting malicious archive files. This vulnerability was exploited in the wild and was discovered by Anton Cherepanov, Peter Košinár, and Peter Strýček
from ESET.

https://nvd.nist.gov/vuln/detail/CVE-2022-21227


3. CVE-2024-38063

A path traversal vulnerability affecting the Windows version of WinRAR allows the attackers to execute arbitrary code by crafting malicious archive files. This vulnerability was exploited in the wild and was discovered by Anton Cherepanov, Peter Košinár, and Peter Strýček
from ESET.

https://nvd.nist.gov/vuln/detail/CVE-2024-38063


4. CVE-2024-49113

A path traversal vulnerability affecting the Windows version of WinRAR allows the attackers to execute arbitrary code by crafting malicious archive files. This vulnerability was exploited in the wild and was discovered by Anton Cherepanov, Peter Košinár, and Peter Strýček
from ESET.

https://nvd.nist.gov/vuln/detail/CVE-2024-49113


5. CVE-2025-0368

A path traversal vulnerability affecting the Windows version of WinRAR allows the attackers to execute arbitrary code by crafting malicious archive files. This vulnerability was exploited in the wild and was discovered by Anton Cherepanov, Peter Košinár, and Peter Strýček
from ESET.

https://nvd.nist.gov/vuln/detail/CVE-2025-0368


6. CVE-2025-14847

A path traversal vulnerability affecting the Windows version of WinRAR allows the attackers to execute arbitrary code by crafting malicious archive files. This vulnerability was exploited in the wild and was discovered by Anton Cherepanov, Peter Košinár, and Peter Strýček
from ESET.

https://nvd.nist.gov/vuln/detail/CVE-2025-14847


7. CVE-2025-24118

A path traversal vulnerability affecting the Windows version of WinRAR allows the attackers to execute arbitrary code by crafting malicious archive files. This vulnerability was exploited in the wild and was discovered by Anton Cherepanov, Peter Košinár, and Peter Strýček
from ESET.

https://nvd.nist.gov/vuln/detail/CVE-2025-24118


8. CVE-2025-50708

A path traversal vulnerability affecting the Windows version of WinRAR allows the attackers to execute arbitrary code by crafting malicious archive files. This vulnerability was exploited in the wild and was discovered by Anton Cherepanov, Peter Košinár, and Peter Strýček
from ESET.

https://nvd.nist.gov/vuln/detail/CVE-2025-50708


9. CVE-2025-54100

A path traversal vulnerability affecting the Windows version of WinRAR allows the attackers to execute arbitrary code by crafting malicious archive files. This vulnerability was exploited in the wild and was discovered by Anton Cherepanov, Peter Košinár, and Peter Strýček
from ESET.

https://nvd.nist.gov/vuln/detail/CVE-2025-54100


10. CVE-2025-58434

A path traversal vulnerability affecting the Windows version of WinRAR allows the attackers to execute arbitrary code by crafting malicious archive files. This vulnerability was exploited in the wild and was discovered by Anton Cherepanov, Peter Košinár, and Peter Strýček
from ESET.

https://nvd.nist.gov/vuln/detail/CVE-2025-58434


1 2 3 … 21 22
New: Attack Surface Management · Dark web intelligence. Now with the bigger picture. | Explore SOS Intelligence ASM →
Privacy Settings
We use cookies to enhance your experience while using our website. If you are using our Services via a browser you can restrict, block or remove cookies through your web browser settings. We also use content and scripts from third parties that may use tracking technologies. You can selectively provide your consent below to allow such third party embeds. For complete information about the cookies we use, data we collect and how we process them, please check our Privacy Policy
Youtube
Consent to display content from - Youtube
Vimeo
Consent to display content from - Vimeo
Google Maps
Consent to display content from - Google
Spotify
Consent to display content from - Spotify
Sound Cloud
Consent to display content from - Sound