Customer portal
Articles Tagged with

SOS Intelligence

"SOS
CVE Top 10

The SOS Intelligence CVE Chatter Weekly Top Ten –


This weekly blog post is from via our unique intelligence collection pipelines. We are your eyes and ears online, including the Dark Web.

There are thousands of vulnerability discussions each week. SOS Intelligence gathers a list of the most discussed Common Vulnerabilities and Exposures (CVE) online for the previous week.

We make every effort to ensure the accuracy of the data presented. As this is an automated process some errors may creep in.

If you are feeling generous please do make us aware of anything you spot, feel free to follow us on Twitter @sosintel and DM us. Thank you!


1. 

https://nvd.nist.gov/vuln/detail/


2.

https://nvd.nist.gov/vuln/detail/


3.

https://nvd.nist.gov/vuln/detail/


4.

https://nvd.nist.gov/vuln/detail/


5.

https://nvd.nist.gov/vuln/detail/


6.

https://nvd.nist.gov/vuln/detail/


7.

https://nvd.nist.gov/vuln/detail/


8.

https://nvd.nist.gov/vuln/detail/


9.

https://nvd.nist.gov/vuln/detail/


10.

https://nvd.nist.gov/vuln/detail/


"Ransomware
Opinion, Ransomware

Ransomware Leak-Site Activity More Than Doubles Year on Year: What It Means for Manufacturing

SOS Intelligence data shows the manufacturing sector continues to be targeted significantly in observed ransomware leak-site activity, while the wider ecosystem is considerably busier and more fragmented than a year ago.

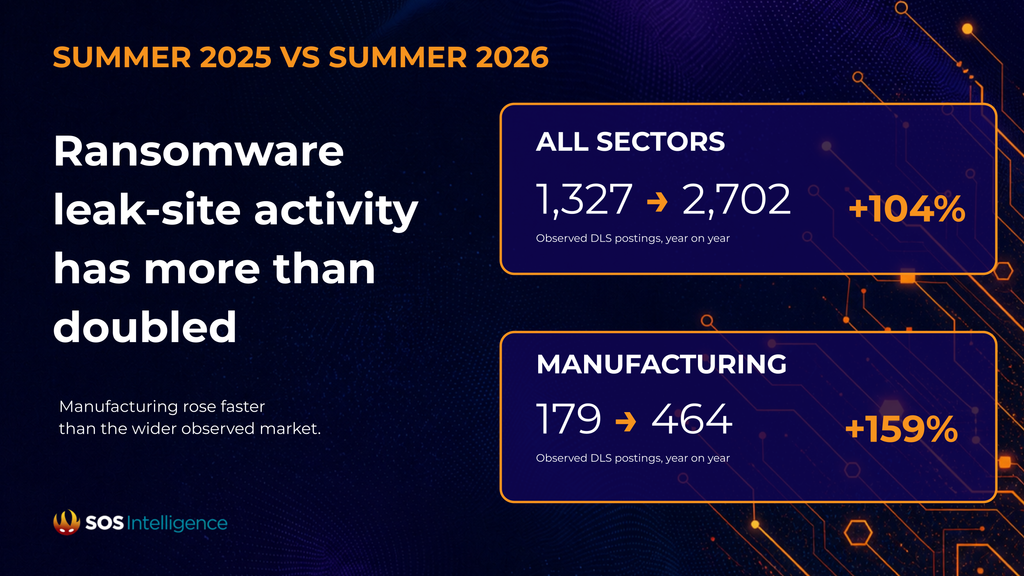
Between June and August 2026, SOS Intelligence recorded 2,702 organisations named on ransomware data-leak sites (DLSs), compared with 1,327 over the same period in 2025, an increase of approximately 104%. This matters not only because of direct organisational exposure, but because disruption can also have knock-on effects across connected supply chains.

Manufacturing ransomware leak postings rose even faster year-on-year, from 179 to 464, taking the sector’s share of observed postings from around 13.5% to 17.2%.

Comparison of summer 2025 and 2026 ransomware leak-site activity, showing overall postings more than doubled and manufacturing posts rose even faster.

August set a new high: 1,081 organisations were named during the month, the highest figure in SOS Intelligence’s records. SOS also saw 80 different threat groups posting in August, another record.

Across the summer, SOS Intelligence observed 36 dark web ransomware threat groups that had not previously posted, responsible for 520 DLS postings, or 19.2% of the summer total. Some are likely to be rebrands rather than genuinely new groups, but even with that caveat, the ransomware ecosystem is clearly becoming more fragmented.

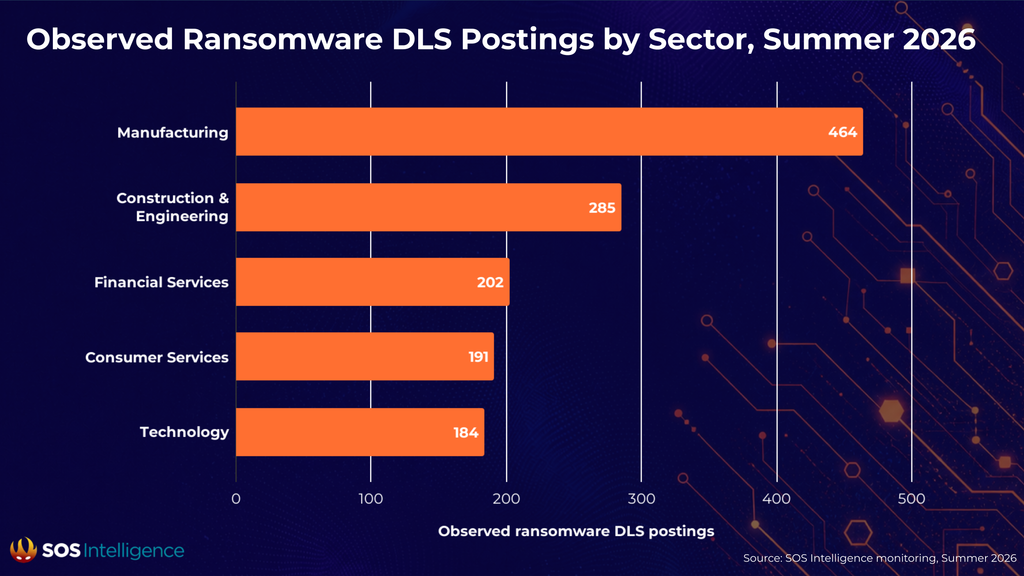
For manufacturing leaders, the important point is the sector’s sustained level of exposure. Manufacturing remains the sector with the highest number of observed ransomware DLS postings, and its year-on-year increase has outpaced the wider ransomware market.

horizontal bar chart showing observed ransomware DLS postings by sector for summer 2026. Manufacturing: 464 postings, Construction & engineering: 285 postings, Financial services: 202 postings, Consumer services: 191 postings, Technology: 184 postings.

That’s not the same as a sudden summer shift towards manufacturing. Postings rose 13.7% from spring to summer, only slightly ahead of the 12.3% increase across all observed postings. The important context is the sector’s starting position: manufacturing is already carrying a high level of observed exposure within a ransomware market that is expanding and changing quickly.

Higher ransomware activity is only part of the picture. Security teams also need to understand which groups are active, where activity is concentrating and how those patterns are shifting. Continuous threat monitoring and analyst-led intelligence can help teams keep that view current and prioritise the activity most relevant to their organisation.

SOS Intelligence will continue to track how this cyber threat environment is developing across ransomware groups, sectors and regions. Explore more SOS Intelligence analysis on ransomware, including what the latest activity means for manufacturing organisations.

Data note: Figures refer to organisations publicly named on ransomware data-leak sites and do not represent the full ransomware market.

"SOS
CVE Top 10

The SOS Intelligence CVE Chatter Weekly Top Ten – 31 August 2026


This weekly blog post is from via our unique intelligence collection pipelines. We are your eyes and ears online, including the Dark Web.

There are thousands of vulnerability discussions each week. SOS Intelligence gathers a list of the most discussed Common Vulnerabilities and Exposures (CVE) online for the previous week.

We make every effort to ensure the accuracy of the data presented. As this is an automated process some errors may creep in.

If you are feeling generous please do make us aware of anything you spot, feel free to follow us on Twitter @sosintel and DM us. Thank you!


1.  CVE-2026-1296

The Frontend Post Submission Manager Lite plugin for WordPress is vulnerable to Open Redirection in all versions up to, and including, 1.2.7 due to insufficient validation on the ‘requested_page’ POST parameter in the verify_username_password function. This makes it possible for unauthenticated attackers to redirect users to potentially malicious sites if they can successfully trick them into performing an action such as clicking on a link.

https://nvd.nist.gov/vuln/detail/CVE-2026-1296


2. CVE-2024-1234

XWiki Platform is a generic wiki platform offering runtime services for applications built on top of it. Any guest can perform arbitrary remote code execution through a request to `SolrSearch`. This impacts the confidentiality, integrity and availability of the whole XWiki installation. To reproduce on an instance, without being logged in, go to `/xwiki/bin/get/Main/SolrSearch?media=rss&text=%7D%7D%7D%7B%7Basync%20async%3Dfalse%7D%7D%7B%7Bgroovy%7D%7Dprintln%28″Hello%20from”%20%2B%20″%20search%20text%3A”%20%2B%20%2823%20%2B%2019%29%29%7B%7B%2Fgroovy%7D%7D%7B%7B%2Fasync%7D%7D%20`. If there is an output, and the title of the RSS feed contains `Hello from search text:42`, then the instance is vulnerable. This vulnerability has been patched in XWiki 15.10.11, 16.4.1 and 16.5.0RC1. Users are advised to upgrade. Users unable to upgrade may edit `Main.SolrSearchMacros` in `SolrSearchMacros.xml` on line 955 to match the `rawResponse` macro in `macros.vm#L2824` with a content type of `application/xml`, instead of simply outputting the content of the feed.

https://nvd.nist.gov/vuln/detail/CVE-2024-1234


3. CVE-2024-5678

XWiki Platform is a generic wiki platform offering runtime services for applications built on top of it. Any guest can perform arbitrary remote code execution through a request to `SolrSearch`. This impacts the confidentiality, integrity and availability of the whole XWiki installation. To reproduce on an instance, without being logged in, go to `/xwiki/bin/get/Main/SolrSearch?media=rss&text=%7D%7D%7D%7B%7Basync%20async%3Dfalse%7D%7D%7B%7Bgroovy%7D%7Dprintln%28″Hello%20from”%20%2B%20″%20search%20text%3A”%20%2B%20%2823%20%2B%2019%29%29%7B%7B%2Fgroovy%7D%7D%7B%7B%2Fasync%7D%7D%20`. If there is an output, and the title of the RSS feed contains `Hello from search text:42`, then the instance is vulnerable. This vulnerability has been patched in XWiki 15.10.11, 16.4.1 and 16.5.0RC1. Users are advised to upgrade. Users unable to upgrade may edit `Main.SolrSearchMacros` in `SolrSearchMacros.xml` on line 955 to match the `rawResponse` macro in `macros.vm#L2824` with a content type of `application/xml`, instead of simply outputting the content of the feed.

https://nvd.nist.gov/vuln/detail/CVE-2024-5678


4. CVE-2024-8856

XWiki Platform is a generic wiki platform offering runtime services for applications built on top of it. Any guest can perform arbitrary remote code execution through a request to `SolrSearch`. This impacts the confidentiality, integrity and availability of the whole XWiki installation. To reproduce on an instance, without being logged in, go to `/xwiki/bin/get/Main/SolrSearch?media=rss&text=%7D%7D%7D%7B%7Basync%20async%3Dfalse%7D%7D%7B%7Bgroovy%7D%7Dprintln%28″Hello%20from”%20%2B%20″%20search%20text%3A”%20%2B%20%2823%20%2B%2019%29%29%7B%7B%2Fgroovy%7D%7D%7B%7B%2Fasync%7D%7D%20`. If there is an output, and the title of the RSS feed contains `Hello from search text:42`, then the instance is vulnerable. This vulnerability has been patched in XWiki 15.10.11, 16.4.1 and 16.5.0RC1. Users are advised to upgrade. Users unable to upgrade may edit `Main.SolrSearchMacros` in `SolrSearchMacros.xml` on line 955 to match the `rawResponse` macro in `macros.vm#L2824` with a content type of `application/xml`, instead of simply outputting the content of the feed.

https://nvd.nist.gov/vuln/detail/CVE-2024-8856


5. CVE-2025-24813

XWiki Platform is a generic wiki platform offering runtime services for applications built on top of it. Any guest can perform arbitrary remote code execution through a request to `SolrSearch`. This impacts the confidentiality, integrity and availability of the whole XWiki installation. To reproduce on an instance, without being logged in, go to `/xwiki/bin/get/Main/SolrSearch?media=rss&text=%7D%7D%7D%7B%7Basync%20async%3Dfalse%7D%7D%7B%7Bgroovy%7D%7Dprintln%28″Hello%20from”%20%2B%20″%20search%20text%3A”%20%2B%20%2823%20%2B%2019%29%29%7B%7B%2Fgroovy%7D%7D%7B%7B%2Fasync%7D%7D%20`. If there is an output, and the title of the RSS feed contains `Hello from search text:42`, then the instance is vulnerable. This vulnerability has been patched in XWiki 15.10.11, 16.4.1 and 16.5.0RC1. Users are advised to upgrade. Users unable to upgrade may edit `Main.SolrSearchMacros` in `SolrSearchMacros.xml` on line 955 to match the `rawResponse` macro in `macros.vm#L2824` with a content type of `application/xml`, instead of simply outputting the content of the feed.

https://nvd.nist.gov/vuln/detail/CVE-2025-24813


6. CVE-2025-24893

XWiki Platform is a generic wiki platform offering runtime services for applications built on top of it. Any guest can perform arbitrary remote code execution through a request to `SolrSearch`. This impacts the confidentiality, integrity and availability of the whole XWiki installation. To reproduce on an instance, without being logged in, go to `/xwiki/bin/get/Main/SolrSearch?media=rss&text=%7D%7D%7D%7B%7Basync%20async%3Dfalse%7D%7D%7B%7Bgroovy%7D%7Dprintln%28″Hello%20from”%20%2B%20″%20search%20text%3A”%20%2B%20%2823%20%2B%2019%29%29%7B%7B%2Fgroovy%7D%7D%7B%7B%2Fasync%7D%7D%20`. If there is an output, and the title of the RSS feed contains `Hello from search text:42`, then the instance is vulnerable. This vulnerability has been patched in XWiki 15.10.11, 16.4.1 and 16.5.0RC1. Users are advised to upgrade. Users unable to upgrade may edit `Main.SolrSearchMacros` in `SolrSearchMacros.xml` on line 955 to match the `rawResponse` macro in `macros.vm#L2824` with a content type of `application/xml`, instead of simply outputting the content of the feed.

https://nvd.nist.gov/vuln/detail/CVE-2025-24893


7. CVE-2025-2563

XWiki Platform is a generic wiki platform offering runtime services for applications built on top of it. Any guest can perform arbitrary remote code execution through a request to `SolrSearch`. This impacts the confidentiality, integrity and availability of the whole XWiki installation. To reproduce on an instance, without being logged in, go to `/xwiki/bin/get/Main/SolrSearch?media=rss&text=%7D%7D%7D%7B%7Basync%20async%3Dfalse%7D%7D%7B%7Bgroovy%7D%7Dprintln%28″Hello%20from”%20%2B%20″%20search%20text%3A”%20%2B%20%2823%20%2B%2019%29%29%7B%7B%2Fgroovy%7D%7D%7B%7B%2Fasync%7D%7D%20`. If there is an output, and the title of the RSS feed contains `Hello from search text:42`, then the instance is vulnerable. This vulnerability has been patched in XWiki 15.10.11, 16.4.1 and 16.5.0RC1. Users are advised to upgrade. Users unable to upgrade may edit `Main.SolrSearchMacros` in `SolrSearchMacros.xml` on line 955 to match the `rawResponse` macro in `macros.vm#L2824` with a content type of `application/xml`, instead of simply outputting the content of the feed.

https://nvd.nist.gov/vuln/detail/CVE-2025-2563


8. CVE-2025-54253

XWiki Platform is a generic wiki platform offering runtime services for applications built on top of it. Any guest can perform arbitrary remote code execution through a request to `SolrSearch`. This impacts the confidentiality, integrity and availability of the whole XWiki installation. To reproduce on an instance, without being logged in, go to `/xwiki/bin/get/Main/SolrSearch?media=rss&text=%7D%7D%7D%7B%7Basync%20async%3Dfalse%7D%7D%7B%7Bgroovy%7D%7Dprintln%28″Hello%20from”%20%2B%20″%20search%20text%3A”%20%2B%20%2823%20%2B%2019%29%29%7B%7B%2Fgroovy%7D%7D%7B%7B%2Fasync%7D%7D%20`. If there is an output, and the title of the RSS feed contains `Hello from search text:42`, then the instance is vulnerable. This vulnerability has been patched in XWiki 15.10.11, 16.4.1 and 16.5.0RC1. Users are advised to upgrade. Users unable to upgrade may edit `Main.SolrSearchMacros` in `SolrSearchMacros.xml` on line 955 to match the `rawResponse` macro in `macros.vm#L2824` with a content type of `application/xml`, instead of simply outputting the content of the feed.

https://nvd.nist.gov/vuln/detail/CVE-2025-54253


9. CVE-2026-0594

XWiki Platform is a generic wiki platform offering runtime services for applications built on top of it. Any guest can perform arbitrary remote code execution through a request to `SolrSearch`. This impacts the confidentiality, integrity and availability of the whole XWiki installation. To reproduce on an instance, without being logged in, go to `/xwiki/bin/get/Main/SolrSearch?media=rss&text=%7D%7D%7D%7B%7Basync%20async%3Dfalse%7D%7D%7B%7Bgroovy%7D%7Dprintln%28″Hello%20from”%20%2B%20″%20search%20text%3A”%20%2B%20%2823%20%2B%2019%29%29%7B%7B%2Fgroovy%7D%7D%7B%7B%2Fasync%7D%7D%20`. If there is an output, and the title of the RSS feed contains `Hello from search text:42`, then the instance is vulnerable. This vulnerability has been patched in XWiki 15.10.11, 16.4.1 and 16.5.0RC1. Users are advised to upgrade. Users unable to upgrade may edit `Main.SolrSearchMacros` in `SolrSearchMacros.xml` on line 955 to match the `rawResponse` macro in `macros.vm#L2824` with a content type of `application/xml`, instead of simply outputting the content of the feed.

https://nvd.nist.gov/vuln/detail/CVE-2026-0594


10. CVE-2026-0770

XWiki Platform is a generic wiki platform offering runtime services for applications built on top of it. Any guest can perform arbitrary remote code execution through a request to `SolrSearch`. This impacts the confidentiality, integrity and availability of the whole XWiki installation. To reproduce on an instance, without being logged in, go to `/xwiki/bin/get/Main/SolrSearch?media=rss&text=%7D%7D%7D%7B%7Basync%20async%3Dfalse%7D%7D%7B%7Bgroovy%7D%7Dprintln%28″Hello%20from”%20%2B%20″%20search%20text%3A”%20%2B%20%2823%20%2B%2019%29%29%7B%7B%2Fgroovy%7D%7D%7B%7B%2Fasync%7D%7D%20`. If there is an output, and the title of the RSS feed contains `Hello from search text:42`, then the instance is vulnerable. This vulnerability has been patched in XWiki 15.10.11, 16.4.1 and 16.5.0RC1. Users are advised to upgrade. Users unable to upgrade may edit `Main.SolrSearchMacros` in `SolrSearchMacros.xml` on line 955 to match the `rawResponse` macro in `macros.vm#L2824` with a content type of `application/xml`, instead of simply outputting the content of the feed.

https://nvd.nist.gov/vuln/detail/CVE-2026-0770


"Ransomware
Opinion

Ransomware in Manufacturing: A Growing Business Risk

For a manufacturer, few things matter more than keeping production moving. When operations are interrupted, the consequences spread quickly across the business: missed orders, delayed deliveries, unhappy customers and lost revenue.

Yet manufacturing is facing a growing threat to that continuity. SOS Intelligence’s data shows that manufacturing has by far the largest number of ransomware victim listings of any industry we monitor – and that number is increasing.

Ransomware is a criminal attack that can simultaneously lock a company out of important systems and steal sensitive information, usually to extort large amounts of money from the business. For manufacturers, that can quickly turn a security incident into a much wider business problem.

Over a 30-month period, SOS Intelligence identified more than 2,100 manufacturing organisations listed on ransomware group leak sites. Our more recent UK data shows that upward trend continuing: manufacturing victim listings increased by 81% in the first half of 2026 compared to the previous six months.

The consequences can reach far beyond the systems initially affected. Disrupted production can mean lost output and revenue, delayed deliveries and missed customer commitments. Suppliers and other parts of the business may also be affected, while recovery costs and prolonged disruption can put further pressure on cash flow and profitability.

Even when production resumes, the impact may continue. Manufacturers hold valuable commercial information, from product designs and engineering specifications to supplier data and proprietary processes. If that information is stolen, it can create longer-term risks for customer relationships, competitive position and reputation.

Businesses cannot act on threats or weaknesses they cannot see, making visibility and awareness a vital part of reducing ransomware risk. Effective monitoring can provide earlier visibility of external risks and warning signs, giving organisations the opportunity to investigate and address potential problems before they develop into more serious incidents.

SOS Intelligence combines continuous external monitoring with analyst expertise, helping organisations understand their exposure, identify relevant threats, and prioritise action. For manufacturers facing a large and growing ransomware problem, that visibility can significantly reduce risk, giving organisations the opportunity to identify and address potential problems before they are exploited.

For leadership, the question is straightforward: do we have enough visibility of the risks facing our business to act before they become a serious problem?

Header photo by Ant Rozetsky on Unsplash

"SOS
CVE Top 10

The SOS Intelligence CVE Chatter Weekly Top Ten – 24 August 2026


This weekly blog post is from via our unique intelligence collection pipelines. We are your eyes and ears online, including the Dark Web.

There are thousands of vulnerability discussions each week. SOS Intelligence gathers a list of the most discussed Common Vulnerabilities and Exposures (CVE) online for the previous week.

We make every effort to ensure the accuracy of the data presented. As this is an automated process some errors may creep in.

If you are feeling generous please do make us aware of anything you spot, feel free to follow us on Twitter @sosintel and DM us. Thank you!


1.  CVE-2026-59310

A vulnerability in the zip archive parser of ClamAV could allow an unauthenticated, remote attacker to cause a DoS condition on an affected device.

This vulnerability is due to improper memory handling when processing content in zip files during scanning. An attacker could exploit this vulnerability by submitting a crafted zip file for scanning. A successful exploit could allow the attacker to cause the ClamAV scanning process to terminate as a result of a memory double-free, resulting in a DoS condition on the affected software.

https://nvd.nist.gov/vuln/detail/CVE-2026-59310


2. CVE-2026-65400

A vulnerability in the zip archive parser of ClamAV could allow an unauthenticated, remote attacker to cause a DoS condition on an affected device.

This vulnerability is due to improper memory handling when processing content in zip files during scanning. An attacker could exploit this vulnerability by submitting a crafted zip file for scanning. A successful exploit could allow the attacker to cause the ClamAV scanning process to terminate as a result of a memory double-free, resulting in a DoS condition on the affected software.

https://nvd.nist.gov/vuln/detail/CVE-2026-65400


3. CVE-2026-14863

A vulnerability in the zip archive parser of ClamAV could allow an unauthenticated, remote attacker to cause a DoS condition on an affected device.

This vulnerability is due to improper memory handling when processing content in zip files during scanning. An attacker could exploit this vulnerability by submitting a crafted zip file for scanning. A successful exploit could allow the attacker to cause the ClamAV scanning process to terminate as a result of a memory double-free, resulting in a DoS condition on the affected software.

https://nvd.nist.gov/vuln/detail/CVE-2026-14863


4. CVE-2026-18412

A vulnerability in the zip archive parser of ClamAV could allow an unauthenticated, remote attacker to cause a DoS condition on an affected device.

This vulnerability is due to improper memory handling when processing content in zip files during scanning. An attacker could exploit this vulnerability by submitting a crafted zip file for scanning. A successful exploit could allow the attacker to cause the ClamAV scanning process to terminate as a result of a memory double-free, resulting in a DoS condition on the affected software.

https://nvd.nist.gov/vuln/detail/CVE-2026-18412


5. CVE-2026-20337

A vulnerability in the zip archive parser of ClamAV could allow an unauthenticated, remote attacker to cause a DoS condition on an affected device.

This vulnerability is due to improper memory handling when processing content in zip files during scanning. An attacker could exploit this vulnerability by submitting a crafted zip file for scanning. A successful exploit could allow the attacker to cause the ClamAV scanning process to terminate as a result of a memory double-free, resulting in a DoS condition on the affected software.

https://nvd.nist.gov/vuln/detail/CVE-2026-20337


6. CVE-2026-20338

A vulnerability in the zip archive parser of ClamAV could allow an unauthenticated, remote attacker to cause a DoS condition on an affected device.

This vulnerability is due to improper memory handling when processing content in zip files during scanning. An attacker could exploit this vulnerability by submitting a crafted zip file for scanning. A successful exploit could allow the attacker to cause the ClamAV scanning process to terminate as a result of a memory double-free, resulting in a DoS condition on the affected software.

https://nvd.nist.gov/vuln/detail/CVE-2026-20338


7. CVE-2026-20339

A vulnerability in the zip archive parser of ClamAV could allow an unauthenticated, remote attacker to cause a DoS condition on an affected device.

This vulnerability is due to improper memory handling when processing content in zip files during scanning. An attacker could exploit this vulnerability by submitting a crafted zip file for scanning. A successful exploit could allow the attacker to cause the ClamAV scanning process to terminate as a result of a memory double-free, resulting in a DoS condition on the affected software.

https://nvd.nist.gov/vuln/detail/CVE-2026-20339


8. CVE-2026-20345

A vulnerability in the zip archive parser of ClamAV could allow an unauthenticated, remote attacker to cause a DoS condition on an affected device.

This vulnerability is due to improper memory handling when processing content in zip files during scanning. An attacker could exploit this vulnerability by submitting a crafted zip file for scanning. A successful exploit could allow the attacker to cause the ClamAV scanning process to terminate as a result of a memory double-free, resulting in a DoS condition on the affected software.

https://nvd.nist.gov/vuln/detail/CVE-2026-20345


9. CVE-2026-20346

A vulnerability in the zip archive parser of ClamAV could allow an unauthenticated, remote attacker to cause a DoS condition on an affected device.

This vulnerability is due to improper memory handling when processing content in zip files during scanning. An attacker could exploit this vulnerability by submitting a crafted zip file for scanning. A successful exploit could allow the attacker to cause the ClamAV scanning process to terminate as a result of a memory double-free, resulting in a DoS condition on the affected software.

https://nvd.nist.gov/vuln/detail/CVE-2026-20346


10. CVE-2026-20347

A vulnerability in the zip archive parser of ClamAV could allow an unauthenticated, remote attacker to cause a DoS condition on an affected device.

This vulnerability is due to improper memory handling when processing content in zip files during scanning. An attacker could exploit this vulnerability by submitting a crafted zip file for scanning. A successful exploit could allow the attacker to cause the ClamAV scanning process to terminate as a result of a memory double-free, resulting in a DoS condition on the affected software.

https://nvd.nist.gov/vuln/detail/CVE-2026-20347


"One
Tips

One supplier, three victims: what D1R tells us about supply chain risk

Analyst Brief   |   Ransomware and Supply Chain

In mid July 2026, a previously unseen group calling itself D1R published three names on its dark web leak site. The first was Synopsys, an American firm that makes the design software used to build and test computer chips. The other two were customers of that first company: the British chip designer ARM, and the German engineering group Bosch. One supplier at the top, two of its customers underneath. On the face of it, a clean example of an attacker using one company as a doorway into others.

That story is a useful one for any manufacturer to sit with, because supply chain traversal is a real and growing problem. But the more interesting lesson here is not that the attack happened as described. It is that most of it probably did not, and that telling the difference is the whole job.

01   What D1R actually claimed

D1R’s leak site laid out a single narrative that ties all three victims together. The group said it found a flaw in a Synopsys registration form that let it pull an entire corporate customer database of roughly 40,000 entries, without needing any internal access. It posted a screenshot of a plain-text file as proof, showing a site identifier, a company name and a location on each row.

It then claimed that this list became a map. Using the customer names as a target list, D1R said it reached into ARM and into Bosch, framing both as downstream victims that were only exposed because the supplier at the top had leaked. Its own words on the Bosch page were blunt: thank Synopsys for showing us where the valuable data lives.

02   Holding the claims up to the light

We reviewed the leak site content and set it against open source reporting and the vendors’ own material. The three claims do not hold together equally well.

Put together, the picture is of an emerging group building a dramatic supply chain story on top of thin proof. The tactic is not new. Exaggerating scope, recycling public documents and leaning on a big brand name are all cheap ways to manufacture pressure and buy credibility before a group has earned either.

03   Why a shaky claim still matters to you

It would be easy to read the above and move on. No confirmed breach, so no problem. That would be the wrong conclusion for a manufacturer, for two reasons.

First, the technique D1R is describing is entirely credible even when this particular execution is not. Attackers do compromise suppliers to reach their customers, and a leaked customer list genuinely is a targeting aid. The next group to try this may have real access rather than a public manual and a screenshot.

Second, and this is the part that bites, your name can appear on a leak site because of something that happened to a supplier, not to you. If a manufacturer using Synopsys tooling had first learned of this by seeing a customer’s name in that 40,000-line list, the damage would already be underway, in customer questions, in press enquiries, in board-level anxiety, regardless of whether a single file had truly been taken.

What good looks like

Monitoring your own perimeter is necessary but no longer sufficient. The D1R episode argues for extending that visibility outward, across the suppliers and partners whose problems can become yours.

  • Know who is upstream of you. Keep a live view of the vendors, tooling and service providers your operation depends on, so that a name on a leak site immediately means something.
  • Watch leak sites for your suppliers, not just yourself. Early sight of a supplier being named buys you time to ask the right questions before customers and journalists do.
  • Be able to triage a claim fast. The value is not in the alert alone. It is in quickly separating an inflated extortion story from a genuine cascade, so you respond in proportion.
  • Rehearse the third-party scenario. Decide in advance who owns the response when the incident is a supplier’s, not yours.

WORK WITH US

See it coming, from your suppliers as well as your own front door

SOS Intelligence is a UK-based dark web threat intelligence platform. We continuously monitor the surface, deep and dark web, Telegram channels, criminal forums and breach databases, and surface what matters to your business, your clients and your supply chain, so you can act before attackers do. The D1R case is exactly the sort of thing our platform is built to catch early: a supplier gets named on a leak site, and you want to know about it straight away rather than hearing it from a customer or a journalist.

  • Supply Chain Risk Monitoring. Track your vendors, partners and critical third parties, and know the moment a supplier is mentioned in a breach, a data sale or a dark web discussion, before it reaches your business.
  • DARKMAP™ continuous monitoring. Automated, round-the-clock scanning across the dark web that surfaces credential leaks, data sales, ransomware mentions and brand impersonation in real time.
  • Real-time Flash Alerts. Get notified the moment your monitored domains, credentials or keywords appear in threat feeds, hours ahead of conventional tooling, straight to your inbox or webhook.
  • DARKSEARCH™ on demand. Search our indexed dark web database whenever you need to, to investigate a name, look up a domain or check out a claim like D1R’s for yourself.

Want to see what we are already picking up about your organisation and your supply chain? Book a free 30-minute demo, and we will scan your domain live on the call.

Chain photo by JJ Ying on Unsplash

"SOS
CVE Top 10

The SOS Intelligence CVE Chatter Weekly Top Ten – 17 August 2026


This weekly blog post is from via our unique intelligence collection pipelines. We are your eyes and ears online, including the Dark Web.

There are thousands of vulnerability discussions each week. SOS Intelligence gathers a list of the most discussed Common Vulnerabilities and Exposures (CVE) online for the previous week.

We make every effort to ensure the accuracy of the data presented. As this is an automated process some errors may creep in.

If you are feeling generous please do make us aware of anything you spot, feel free to follow us on Twitter @sosintel and DM us. Thank you!


1.  CVE-2024-51479

Axios is a promise based HTTP client for the browser and Node.js. Prior to 1.15.0 and 0.31.0, Axios does not correctly handle hostname normalization when checking NO_PROXY rules. Requests to loopback addresses like localhost. (with a trailing dot) or [::1] (IPv6 literal) skip NO_PROXY matching and go through the configured proxy. This goes against what developers expect and lets attackers force requests through a proxy, even if NO_PROXY is set up to protect loopback or internal services. This issue leads to the possibility of proxy bypass and SSRF vulnerabilities allowing attackers to reach sensitive loopback or internal services despite the configured protections. This vulnerability is fixed in 1.15.0 and 0.31.0.

https://nvd.nist.gov/vuln/detail/CVE-2024-51479


2. CVE-2025-62718

Axios is a promise based HTTP client for the browser and Node.js. Prior to 1.15.0 and 0.31.0, Axios does not correctly handle hostname normalization when checking NO_PROXY rules. Requests to loopback addresses like localhost. (with a trailing dot) or [::1] (IPv6 literal) skip NO_PROXY matching and go through the configured proxy. This goes against what developers expect and lets attackers force requests through a proxy, even if NO_PROXY is set up to protect loopback or internal services. This issue leads to the possibility of proxy bypass and SSRF vulnerabilities allowing attackers to reach sensitive loopback or internal services despite the configured protections. This vulnerability is fixed in 1.15.0 and 0.31.0.

https://nvd.nist.gov/vuln/detail/CVE-2025-62718


3. CVE-2026-32315

motionEye (mEye) is an online interface for motion software, a video surveillance program with motion detection. Versions prior to 0.44.0 create the configuration file /etc/motioneye/motion.conf with 644 permissions (-rw-r–r–), making it readable by any local user on the system. This file contains sensitive data including the admin password hash, which can be leveraged by other vulnerabilities to escalate privileges. Additionally, per-camera configuration files (camera-*.conf) are also created with the same 644 permissions, potentially exposing camera-specific credentials and settings. The exposed SHA1 admin password hash can be cracked offline to recover the plaintext password, used directly to forge authenticated admin API requests via the signature authentication weakness (GHSA-45h7-499j-7ww3), and chained with the OS command injection flaw (CVE-2025-60787) to escalate a local unprivileged user to the Motion daemon user (often root), enabling full system compromise. This issue has been fixed in version 0.44.0.

https://nvd.nist.gov/vuln/detail/CVE-2026-32315


4. CVE-2019-20790

OpenDMARC through 1.3.2 and 1.4.x allows attacks that inject authentication results to provide false information about the domain that originated an e-mail message. This is caused by incorrect parsing and interpretation of SPF/DKIM authentication results, as demonstrated by the example.net(.example.com substring.

https://nvd.nist.gov/vuln/detail/CVE-2019-20790


5. CVE-2020-12272

OpenDMARC through 1.3.2 and 1.4.x allows attacks that inject authentication results to provide false information about the domain that originated an e-mail message. This is caused by incorrect parsing and interpretation of SPF/DKIM authentication results, as demonstrated by the example.net(.example.com substring.

https://nvd.nist.gov/vuln/detail/CVE-2020-12272


6. CVE-2026-60137

WordPress 6.8.x before 6.8.6, 6.9.x before 6.9.5, and 7.0.x before 7.0.2 does not properly sanitise the author__not_in parameter of WP_Query, which could allow SQL Injection when a plugin or theme passes untrusted input to the parameter.

https://nvd.nist.gov/vuln/detail/CVE-2026-60137


7. CVE-2026-63030

WordPress 6.8.x before 6.8.6, 6.9.x before 6.9.5, and 7.0.x before 7.0.2 does not properly sanitise the author__not_in parameter of WP_Query, which could allow SQL Injection when a plugin or theme passes untrusted input to the parameter.

https://nvd.nist.gov/vuln/detail/CVE-2026-63030


8. CVE-2019-11090

STMicroelectronics ST33TPHF2ESPI TPM devices before 2019-09-12 allow attackers to extract the ECDSA private key via a side-channel timing attack because ECDSA scalar multiplication is mishandled, aka TPM-FAIL.

https://nvd.nist.gov/vuln/detail/CVE-2019-11090


9. CVE-2019-16863

STMicroelectronics ST33TPHF2ESPI TPM devices before 2019-09-12 allow attackers to extract the ECDSA private key via a side-channel timing attack because ECDSA scalar multiplication is mishandled, aka TPM-FAIL.

https://nvd.nist.gov/vuln/detail/CVE-2019-16863


10. CVE-2023-1017

STMicroelectronics ST33TPHF2ESPI TPM devices before 2019-09-12 allow attackers to extract the ECDSA private key via a side-channel timing attack because ECDSA scalar multiplication is mishandled, aka TPM-FAIL.

https://nvd.nist.gov/vuln/detail/CVE-2023-1017


"Stealer
Investigation, The Dark Web

Stealer Logs: Understanding the Underground’s Most Dangerous Data Source

Introduction

Stealer logs represent the most dangerous commoditised threat to corporate security today. Unlike traditional data breaches that target specific organisations, infostealers cast a wide net across millions of users and machines, capturing everything from browser credentials to session tokens to cryptocurrency wallets in a single automated sweep.

So why are stealer logs such a critical concern right now? Because they are the common precursor to account takeover, ransomware deployment, and initial access brokerage. If your users’ credentials are in a stealer log marketplace, you do not have an identity problem; you have a breach waiting to happen.

This report examines what stealer logs are, how they are distributed and monetised, what data they contain, and how organisations can detect and defend against them. The scale is staggering: in the first half of 2025 alone, over 180,000 stealer logs were offered for sale on underground marketplaces. RedLine accounts for 44% of all logs collected. Vidar stole 65 million passwords in just six months.

If your domain appears in a stealer log, you are no longer operating under the assumption of credential compromise; you are operating under the certainty of it. The only question is whether the threat actor has already acted on that access.

How Infostealers Work

The Malware Itself

An infostealer is malware designed with a single purpose: to extract sensitive data from an infected machine and exfiltrate it to an attacker-controlled server. It runs silently, often with minimal resource consumption, which is why users and security teams can miss it for weeks or months.

So what data do they target? Browser autofill data, stored passwords, session cookies, saved payment card details, cryptocurrency wallet seed phrases and private keys, email account credentials, browser extensions, browsing history, installed software inventory, system information, and USB device history. The malware is indiscriminate; it grabs everything that might have value.

The sophistication varies. Basic infostealers are crude tools designed to grab whatever they can reach. Advanced infostealers include anti-analysis features, anti-virtualisation checks, geofencing to avoid high-risk jurisdictions, and code obfuscation to bypass signature-based detection.

Major Infostealer Families

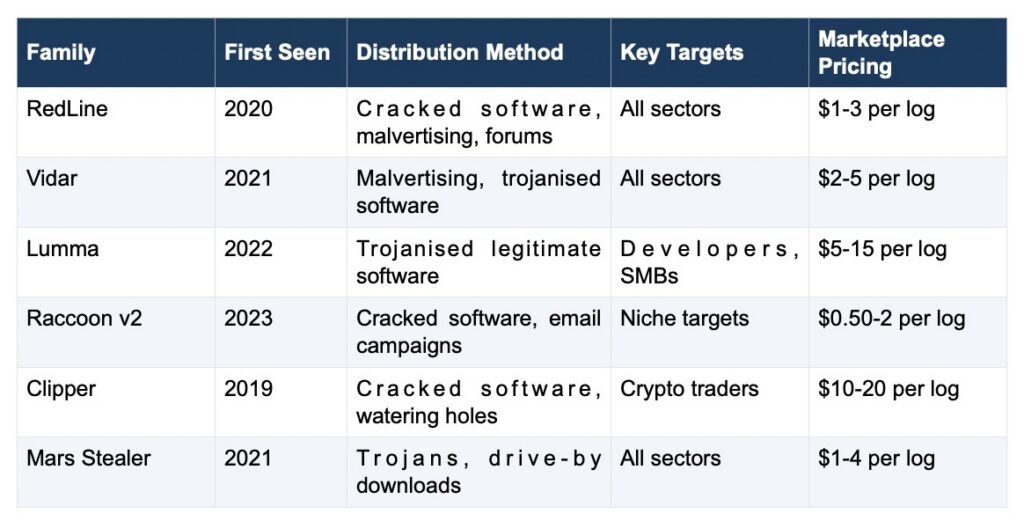
RedLine is the dominant family by volume. First observed in 2020, RedLine has evolved into a modular stealer with customisable features, support for multiple languages and operating systems, and active development. It accounts for 44% of all stealer logs captured by intelligence vendors. RedLine spreads primarily through cracked software, malicious advertising networks, and watering hole attacks targeting development forums.

Raccoon was one of the earliest widespread infostealers and became infamous for its ease of use and low barrier to entry. Variant developers could build custom builds for under $100. Although law enforcement operations disrupted Raccoon’s primary infrastructure in 2023 (following the October 2022 arrest of developer Mark Sokolovsky), variants continue to circulate. Raccoon logs are heavily discounted on marketplaces because the payloads are dated and signatures are well-known.

Vidar is one of the most aggressive and feature-rich infostealers in circulation. It records keystrokes, captures screenshots, exfiltrates browser data, and includes anti-reverse-engineering protections. Vidar was responsible for stealing 65 million passwords in a documented six-month period from 2024 to 2025. It spreads through malvertising, cracked software, and compromised download mirrors.

Lumma emerged in 2022 and gained traction rapidly because of its effective distribution mechanism and low detection rates. Lumma’s primary distribution vector is Trojanised legitimate software (video converters, games, file managers) distributed through third-party sites. Lumma logs are actively traded on underground markets at premium prices because they tend to contain fresh, high-value data.

The Malware-as-a-Service Model

Most modern infostealers operate as a service, not a discrete product. Operators host the command and control infrastructure, provide a web panel for customers to manage infections and download logs, and take a percentage of the revenue when logs are resold.

The client (a threat actor, distributor, or criminal organisation) uses the service to build custom malware variants, deploy them through their chosen vectors, and collect the resulting logs. The service operator handles the backend; the client handles distribution and monetisation.

This model democratises malware development. You do not need to be a skilled reverse engineer or malware author; you just need access to a distribution channel and a payment method. Prices for malware-as-a-service access range from $40 per month for basic builds to $500 per month for fully customised, high-stealth variants with obfuscation and anti-analysis features.

The Stealer Log Supply Chain: From Infection to Marketplace

Step One: Distribution

The first stage of the supply chain is getting the malware onto the target machine. Distribution methods include cracked software (the single largest vector), malicious advertisements and browser redirects, compromised legitimate software mirrors, phishing emails with trojanised attachments, and watering hole attacks targeting developers and specific industries.

Cracked software remains the dominant distribution method because the economics are simple: users want free versions of expensive software, threat actors provide infected versions, and the malware runs with the privileges of the software installation. Commonly trojanised products include AutoCAD, Microsoft Office, Photoshop, Ableton Live, JetBrains IDEs, and antivirus software itself. Underground marketplaces such as zqi3evypxq7ok3gqnimwnlesf6v76ksrpgtgb6j7hh6ye752apzmceyd[.]onion advertise cracking tools and hacking guides alongside stealer logs.

Step Two: Execution and Exfiltration

Once executed, the infostealer begins its automated collection routine. It enumerates installed browsers, reads credential storage databases, decrypts stored passwords using the operating system’s credential storage APIs, extracts browser cookies (which often contain active session tokens for web services), and collects any data it has permissions to access.

So what happens to this data once collected? The malware packages it into an archive (typically JSON or CSV format), compresses it, and sends it back to the attacker’s command and control server. This happens in seconds to minutes, often without any user-visible activity. Encryption in transit is variable; some stealers use HTTPS, others use simple obfuscation.

Step Three: Log Curation and Testing

The logs arrive at the attacker’s server in raw form. Experienced threat actors filter and verify logs before offering them for sale. They test login credentials against target services to confirm validity, check whether emails are associated with high-value targets (executives, technical staff, security personnel), and flag logs that contain cryptocurrency wallet data or payment card information for premium pricing.

A high-quality stealer log contains verified working credentials, a mix of personal and corporate accounts, cryptocurrency wallet information, and identifiable metadata such as system username and company name extracted from the system registry. Low-quality logs are unverified, old (more than a week old), or contain duplicates.

Step Four: Marketplace and Distribution

Verified logs are uploaded to underground marketplaces. The three most significant distribution channels are the Russian Market (a Telegram-native marketplace with automated purchasing and delivery), Genesis Market (a long-standing marketplace specialising in session cookies and browser profile data, subject to FBI takedown in April 2023 as part of Operation Cookie Monster), and ad hoc Telegram channels run by individual threat actors or resellers.

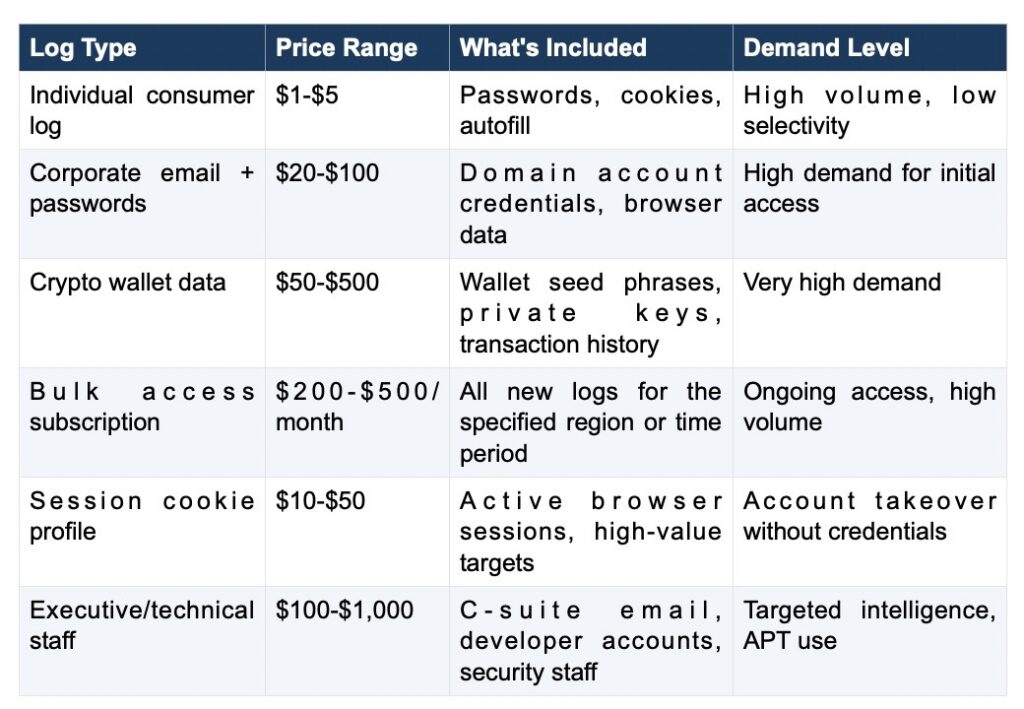
Pricing follows a predictable pattern: individual consumer logs $1 to $5, logs containing cryptocurrency or payment card data $10 to $50, corporate or email logs $20 to $100, and bulk access to large log repositories $1,000 to $5,000, depending on scope and recency. Some marketplaces offer subscription models where buyers pay $200 to $500 per month for unlimited access to new logs.

Step Five: Exploitation

Once purchased, the logs are used for account takeover (directly accessing email, SaaS applications, or banking portals), credential stuffing attacks against non-customers, password spray attacks across corporate networks, identification of high-value targets for targeted phishing or social engineering, and sales to other threat actors, ransomware gangs, or initial access brokers.

The timeline from infection to exploitation can be remarkably short. Logs may be available for purchase within 24 to 72 hours of infection. Active threat actors monitor marketplaces continuously, purchasing logs for targets relevant to their operations immediately after they appear for sale.

What’s Inside a Stealer Log

A typical stealer log is a structured data archive containing the following categories of information.

Browser Credentials

Passwords are stored in Chrome, Firefox, Edge, Opera, and other Chromium-based browsers. These are extracted using the browser’s own decryption APIs and are usually in plaintext in the log. If your users are reusing passwords across multiple services (which most do), a single compromised password gives access to email, SaaS applications, banking portals, and corporate networks.

Session Cookies and Browser Data

Session cookies are particularly valuable because they often grant access to authenticated services without requiring the user to log in again. A stolen cookie for a user’s email account, for example, allows an attacker to reset the password for every service that user has signed up for. Logs also contain browser autofill data, saved addresses, phone numbers, and credit card information.

Cryptocurrency Wallet Data

If the infected machine has a cryptocurrency wallet installed (MetaMask, Trust Wallet, Ledger, Trezor drivers), the infostealer attempts to extract wallet seed phrases, private keys, and transaction history. A stolen seed phrase gives the attacker full control of any cryptocurrency stored in that wallet. Logs containing wallet data command a significant price premium, with cryptocurrency-focused marketplaces like tamazoncmlw2ohkbsmqxnotudejdd4befrasxuigzzjumqu3zba535yd[.]onion advertising cloned cards and financial fraud tools alongside wallet data.

System and User Information

The log includes the machine’s hostname, registered Windows username, installed software inventory, list of network interfaces and IP addresses, list of USB devices ever connected, system serial number, and BIOS information. This metadata helps threat actors profile the target (e.g. is this a developer machine, does it have security software installed) and tailor exploitation.

Email and Application Data

If Outlook, Thunderbird, or other email clients are installed, logs may contain saved email credentials and cached email headers. Application-specific data is also captured, including saved credentials in password managers (if they are not properly locked), FTP clients, SSH keys, browser extensions, and stored API credentials in development tools.

Indicator Format

Logs are typically structured as JSON or CSV files within a ZIP archive. A single log might be 5 to 200 megabytes, depending on the system’s history and installed software. Large batch log collections can reach gigabytes and are broken into smaller chunks for distribution.

Key Statistics: The Scale of the Threat

RedLine accounts for 44% of all stealer logs analysed by intelligence platforms. This concentration means that if you are looking for signs of compromise via stealer logs, you are primarily tracking RedLine activity. However, that also means a significant proportion of logs come from other families like Vidar, Lumma, and Raccoon variants.

Vidar stole 65 million unique passwords in a documented six-month period from October 2024 to March 2025. This single family, operating from a single set of infrastructure, compromised a staggering volume of user accounts across consumer and corporate domains.

Over 180,000 stealer logs were offered for sale on identified underground marketplaces in the first half of 2025. This is an average of 30,000 logs per month, or roughly 1,000 logs per day.

More than 50% of ransomware victims had their domains listed in stealer logs before the ransomware deployment. This indicates that initial compromise via stealer log access is a primary precursor to ransomware attacks. Threat actors purchase logs to establish initial access, conduct reconnaissance, and stage the ransomware payload.

Major Infostealer Families

Stealer Log Pricing by Type

Impact Statistics

The Marketplace Ecosystem

Russian Market (Telegram Native)

Russian Market operates exclusively within Telegram and is the largest active stealer log marketplace as of 2025. The platform uses automated bots that handle purchasing, payment, and log delivery. Buyers simply send a payment in cryptocurrency and receive a direct link to download the log within minutes.

Russian Market does not charge a commission on individual sales; revenue comes from premium marketplace memberships, advertising, and selective enforcement of seller verification. The platform lists 50,000 to 100,000 logs at any given time, with new inventory added continuously.

Genesis Market

Genesis Market is a longer-established marketplace that specialises in session cookies, browser profiles, and authenticated user sessions rather than raw passwords. It operates a traditional web interface (accessed via Tor) and enforces strict verification of sellers. Genesis Market was subject to a major FBI takedown operation in April 2023.

Genesis Market takes a 10 to 15% commission on each sale. Logs on Genesis command higher prices than equivalent logs on the Russian Market because the payload (authenticated sessions) is more directly useful for account takeover without password changes. The marketplace has hosted millions of stolen sessions.

Telegram Channels and Resellers

Smaller threat actors and resellers operate ad hoc Telegram channels, often promoting newly harvested logs from specific geographic regions or specific malware families. These channels operate with less formal infrastructure and offer discounts for bulk purchases. Forums like bfdxjkv5e2z3ilrifzbnvxxvhbzsj67akjpj3zc6smzr4vv6oz565gyd[.]onion host escrow services and enable peer-to-peer trading of stolen logs.

Prices on Telegram are often lower than those on centralised marketplaces because resellers are trying to move inventory quickly and avoid law enforcement attention. However, logs are also less verified and may contain duplicates or stale data.

Regional Variations

Pricing and availability vary significantly by geography. Logs from developed economies (USA, UK, Germany, Japan) command premium prices. Logs from developing economies are discounted. Logs are also segmented by corporate association; logs from email addresses on Fortune 500 domain whitelists are marked as such and priced accordingly.

Corporate Risk: How Stealer Logs Enable Attacks

Account Takeover

The most direct exploitation path is account takeover. An attacker purchases a log containing the email address and password of a corporate employee. They attempt to log into the employee’s email account. If multi-factor authentication is not enabled (and many users do not enable it outside of work contexts), login succeeds.

From the email, the attacker resets passwords for every service the employee has linked to that email account. This includes SaaS applications, cloud storage, password managers, and often the employee’s corporate VPN or SSO portal if they have reused the same password across services.

Initial Access Brokerage

Ransomware gangs and APT operators do not have time to run large-scale malware campaigns. Instead, they purchase access from initial access brokers. An initial access broker uses stealer logs to identify high-value targets (corporate email addresses, domain admin accounts, people working for specific industries), purchases logs for those individuals, and then sells the access to ransomware operators or nation states.

A single log containing credentials for a domain admin or security operations centre staff member can sell for $5,000 to $50,000 to a ransomware operator, because that access drastically shortcuts the reconnaissance and lateral movement phases of a ransomware campaign.

Reconnaissance and Lateral Movement

Even if the initial compromised account is a low-privilege user, logs contain system information, installed software, network configuration, and connected USB devices. This metadata gives threat actors a profile of the corporate environment before they even gain access. They know which security software is in use, which development frameworks are deployed, and which network devices are present.

Once inside, the attacker uses the compromised account to access email (containing sensitive business information, network topology diagrams, and access credentials in forwarded messages), network drives, and internal tools. This leads to lateral movement to higher-privileged accounts and eventually to domain admin compromise.

Credential Stuffing and Password Spray

An attacker with a database of 1,000 stolen passwords can conduct password spray attacks against your corporate email system or Active Directory, trying the same password across all known email addresses in your organisation. The attack succeeds if employees have reused credentials or used predictable variations.

This is a silent attack that happens outside of your firewall and VPN, so your network monitoring tools do not detect it. The first sign may be unexpected password reset emails or successful logins from impossible locations.

Supply Chain Compromise

If your organisation relies on third-party software vendors or contractors, and those vendors’ employees are in the stealer logs, an attacker can compromise the vendor and use their access to gain indirect access to your systems. This is a far easier attack vector than breaching you directly.

How SOS Intelligence Monitors Stealer Logs

Our breach alert system continuously monitors underground marketplaces, forums, Telegram channels, and data dump collections for stealer logs and other sources of compromised data. We extract indicators of compromise from each log and match them against your organisational domains.

So how does detection work? We parse log contents for email addresses, domain names, usernames, system names, and other identifying information. We match these against your organisation’s known domain list. When we find a hit, we generate an alert with details: which user was compromised, which malware family was responsible (if known), what data was exposed, when the log appeared for sale, and what price it commanded on the marketplace.

We also track trends. We monitor which malware families are producing the most volume, which geographic regions are being targeted, and which industries are disproportionately represented in current stealer logs. This gives you visibility into both specific risks to your organisation and the broader threat landscape.

Our enrichment process adds context. We cross-reference the compromised email addresses with LinkedIn, WHOIS records, and internal threat intelligence to identify whether the compromised user holds a sensitive position (executive, developer, security staff). We flag logs that contain multiple compromised employees from the same organisation as indicators of targeted activity rather than random harvesting.

Defensive Recommendations

Detection and Monitoring

First: subscribe to breach alert services that monitor stealer log marketplaces and dark web collections. The earlier you know that your users are in stealer logs, the faster you can reset compromised credentials and audit for account access.

Second: implement continuous exposure monitoring. Track your organisational domains on dark web forums, marketplaces, pastebins, and leaked database collections. Many of these sources post publicly (just on obscure infrastructure); you do not need access to Telegram to find them.

Incident Response

If you discover that your domain is present in a stealer log, treat it as a credential compromise incident. Reset the password for the compromised user immediately. Force re-authentication on all active sessions (log them out everywhere). Enable multi-factor authentication if not already in use. Audit email forwarding rules, application integrations, and connected devices for signs of access.

Check whether the compromised user holds a sensitive role. If they do, expand your investigation: query your identity provider and email system for impossible logins, password changes, or unusual activity; check cloud storage for data exfiltration; and interview the user about recent phishing attempts or unusual system behaviour.

Credential Hygiene

Enforce strong, unique passwords for all systems, especially email and identity providers. Implement passwordless authentication where possible (FIDO2 hardware keys, Windows Hello). Where passwords are necessary, use a password manager with strong master passwords.

Multi-factor authentication is not optional; it is mandatory. If an attacker has your password (because it is in a stealer log), multi-factor authentication is the only thing that stops account takeover. Prioritise MFA for email and administrative accounts. Do not rely on SMS; use TOTP or hardware keys.

Threat Actor Knowledge

Understand which threat actors are currently targeting your industry. If you operate in critical infrastructure or financial services, you are targeted by state-sponsored actors and organised crime groups, not opportunistic cybercriminals. If you operate in technology or biotech, intellectual property theft is a primary motivation.

Review the malware families affecting your sector. If your users are appearing in Vidar or Lumma logs more frequently than average, your distribution channels may be compromised. If you see your domain in logs associated with a specific ransomware gang, you have a higher probability of imminent encryption activity.

Third-Party Risk

Audit your third-party vendors and contractors for Stealer log exposure. If a critical vendor has employees in breach, consider the implications for your access. Do they reuse passwords, or are their systems segmented? Do they have elevated privileges in your environment?

Implement zero-trust principles for vendor access. Do not assume that a contractor’s machine is clean; segment their access, require multi-factor authentication, and monitor their activity as you would a hostile external party.

Appendix: DARKSEARCH Observed Indicators

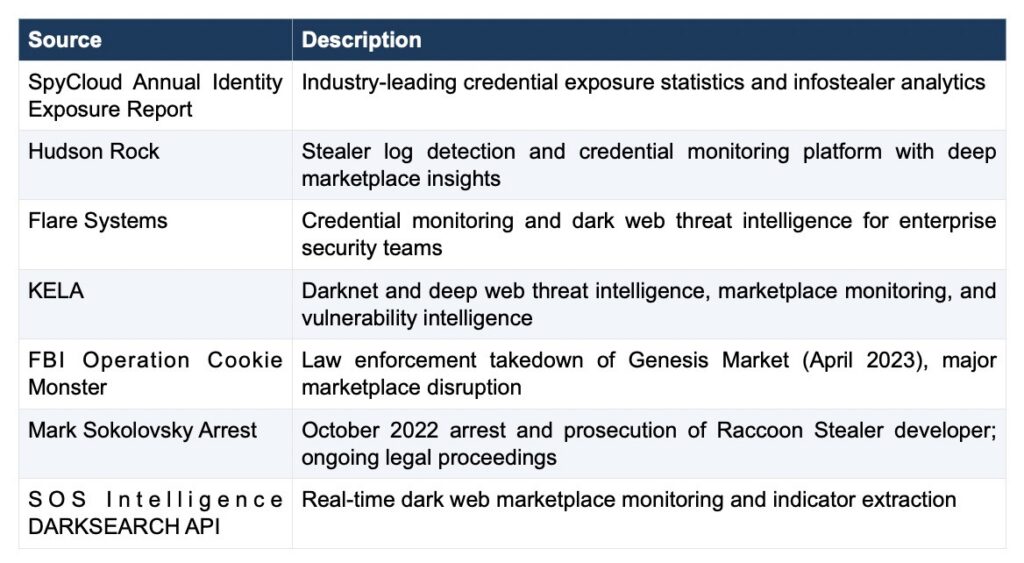
The following table documents confirmed indicators from dark web marketplaces and forums monitored via SOS Intelligence’s DARKSEARCH API. All onion addresses are defanged for security and compliance purposes. These indicators are provided for threat intelligence and detection purposes only.

External References

The analysis in this report draws on publicly available threat intelligence, academic research, and law enforcement activity reports. Key sources include:

Conclusion

Stealer logs are not a future threat; they are a present reality. The scale of harvesting, the sophistication of the malware, and the availability of stolen data on open marketplaces mean that credential compromise is no longer exceptional. It is expected.

Your organisation’s security posture must start with the assumption that your users’ credentials are compromised. That means: strong, unique passwords, multi-factor authentication, continuous monitoring of dark web sources, rapid response to breach alerts, and zero-trust policies for sensitive access.

The defenders who will prevail are those who detect compromise early and respond immediately. Every hour between when a stealer log appears on a marketplace and when you reset the compromised credentials is an hour the attacker can exploit that access.

If you do not have visibility into dark web stealer log marketplaces today, you do not have a complete picture of your organisation’s actual risk. Close that gap now.

Danger photo by Edwin Hooper on Unsplash

Malware photo by Ed Hardie on Unsplash

Browser photo by BoliviaInteligente on Unsplash

No trespassing photo by Joseph Corl on Unsplash

"SOS
CVE Top 10

The SOS Intelligence CVE Chatter Weekly Top Ten – 13 July 2026


This weekly blog post is from via our unique intelligence collection pipelines. We are your eyes and ears online, including the Dark Web.

There are thousands of vulnerability discussions each week. SOS Intelligence gathers a list of the most discussed Common Vulnerabilities and Exposures (CVE) online for the previous week.

We make every effort to ensure the accuracy of the data presented. As this is an automated process some errors may creep in.

If you are feeling generous please do make us aware of anything you spot, feel free to follow us on Twitter @sosintel and DM us. Thank you!


1.  CVE-2020-1938

A path traversal vulnerability affecting the Windows version of WinRAR allows the attackers to execute arbitrary code by crafting malicious archive files. This vulnerability was exploited in the wild and was discovered by Anton Cherepanov, Peter Košinár, and Peter Strýček
from ESET.

https://nvd.nist.gov/vuln/detail/CVE-2020-1938


2. CVE-2022-21227

A path traversal vulnerability affecting the Windows version of WinRAR allows the attackers to execute arbitrary code by crafting malicious archive files. This vulnerability was exploited in the wild and was discovered by Anton Cherepanov, Peter Košinár, and Peter Strýček
from ESET.

https://nvd.nist.gov/vuln/detail/CVE-2022-21227


3. CVE-2024-38063

A path traversal vulnerability affecting the Windows version of WinRAR allows the attackers to execute arbitrary code by crafting malicious archive files. This vulnerability was exploited in the wild and was discovered by Anton Cherepanov, Peter Košinár, and Peter Strýček
from ESET.

https://nvd.nist.gov/vuln/detail/CVE-2024-38063


4. CVE-2024-49113

A path traversal vulnerability affecting the Windows version of WinRAR allows the attackers to execute arbitrary code by crafting malicious archive files. This vulnerability was exploited in the wild and was discovered by Anton Cherepanov, Peter Košinár, and Peter Strýček
from ESET.

https://nvd.nist.gov/vuln/detail/CVE-2024-49113


5. CVE-2025-0368

A path traversal vulnerability affecting the Windows version of WinRAR allows the attackers to execute arbitrary code by crafting malicious archive files. This vulnerability was exploited in the wild and was discovered by Anton Cherepanov, Peter Košinár, and Peter Strýček
from ESET.

https://nvd.nist.gov/vuln/detail/CVE-2025-0368


6. CVE-2025-14847

A path traversal vulnerability affecting the Windows version of WinRAR allows the attackers to execute arbitrary code by crafting malicious archive files. This vulnerability was exploited in the wild and was discovered by Anton Cherepanov, Peter Košinár, and Peter Strýček
from ESET.

https://nvd.nist.gov/vuln/detail/CVE-2025-14847


7. CVE-2025-24118

A path traversal vulnerability affecting the Windows version of WinRAR allows the attackers to execute arbitrary code by crafting malicious archive files. This vulnerability was exploited in the wild and was discovered by Anton Cherepanov, Peter Košinár, and Peter Strýček
from ESET.

https://nvd.nist.gov/vuln/detail/CVE-2025-24118


8. CVE-2025-50708

A path traversal vulnerability affecting the Windows version of WinRAR allows the attackers to execute arbitrary code by crafting malicious archive files. This vulnerability was exploited in the wild and was discovered by Anton Cherepanov, Peter Košinár, and Peter Strýček
from ESET.

https://nvd.nist.gov/vuln/detail/CVE-2025-50708


9. CVE-2025-54100

A path traversal vulnerability affecting the Windows version of WinRAR allows the attackers to execute arbitrary code by crafting malicious archive files. This vulnerability was exploited in the wild and was discovered by Anton Cherepanov, Peter Košinár, and Peter Strýček
from ESET.

https://nvd.nist.gov/vuln/detail/CVE-2025-54100


10. CVE-2025-58434

A path traversal vulnerability affecting the Windows version of WinRAR allows the attackers to execute arbitrary code by crafting malicious archive files. This vulnerability was exploited in the wild and was discovered by Anton Cherepanov, Peter Košinár, and Peter Strýček
from ESET.

https://nvd.nist.gov/vuln/detail/CVE-2025-58434


"SOS
CVE Top 10

The SOS Intelligence CVE Chatter Weekly Top Ten – 06 July 2026


This weekly blog post is from via our unique intelligence collection pipelines. We are your eyes and ears online, including the Dark Web.

There are thousands of vulnerability discussions each week. SOS Intelligence gathers a list of the most discussed Common Vulnerabilities and Exposures (CVE) online for the previous week.

We make every effort to ensure the accuracy of the data presented. As this is an automated process some errors may creep in.

If you are feeling generous please do make us aware of anything you spot, feel free to follow us on Twitter @sosintel and DM us. Thank you!


1.  CVE-2025-54100

telnetd in GNU inetutils through 2.7 allows an out-of-bounds write in the LINEMODE SLC (Set Local Characters) suboption handler because add_slc does not check whether the buffer is full.

https://nvd.nist.gov/vuln/detail/CVE-2025-54100


2. CVE-2020-1938

telnetd in GNU inetutils through 2.7 allows an out-of-bounds write in the LINEMODE SLC (Set Local Characters) suboption handler because add_slc does not check whether the buffer is full.

https://nvd.nist.gov/vuln/detail/CVE-2020-1938


3. CVE-2025-50708

telnetd in GNU inetutils through 2.7 allows an out-of-bounds write in the LINEMODE SLC (Set Local Characters) suboption handler because add_slc does not check whether the buffer is full.

https://nvd.nist.gov/vuln/detail/CVE-2025-50708


4. CVE-2022-21227

telnetd in GNU inetutils through 2.7 allows an out-of-bounds write in the LINEMODE SLC (Set Local Characters) suboption handler because add_slc does not check whether the buffer is full.

https://nvd.nist.gov/vuln/detail/CVE-2022-21227


5. CVE-2024-38063

telnetd in GNU inetutils through 2.7 allows an out-of-bounds write in the LINEMODE SLC (Set Local Characters) suboption handler because add_slc does not check whether the buffer is full.

https://nvd.nist.gov/vuln/detail/CVE-2024-38063


6. CVE-2024-49113

telnetd in GNU inetutils through 2.7 allows an out-of-bounds write in the LINEMODE SLC (Set Local Characters) suboption handler because add_slc does not check whether the buffer is full.

https://nvd.nist.gov/vuln/detail/CVE-2024-49113


7. CVE-2025-0368

telnetd in GNU inetutils through 2.7 allows an out-of-bounds write in the LINEMODE SLC (Set Local Characters) suboption handler because add_slc does not check whether the buffer is full.

https://nvd.nist.gov/vuln/detail/CVE-2025-0368


8. CVE-2025-14847

telnetd in GNU inetutils through 2.7 allows an out-of-bounds write in the LINEMODE SLC (Set Local Characters) suboption handler because add_slc does not check whether the buffer is full.

https://nvd.nist.gov/vuln/detail/CVE-2025-14847


9. CVE-2025-24118

telnetd in GNU inetutils through 2.7 allows an out-of-bounds write in the LINEMODE SLC (Set Local Characters) suboption handler because add_slc does not check whether the buffer is full.

https://nvd.nist.gov/vuln/detail/CVE-2025-24118


10. CVE-2025-58434

telnetd in GNU inetutils through 2.7 allows an out-of-bounds write in the LINEMODE SLC (Set Local Characters) suboption handler because add_slc does not check whether the buffer is full.

https://nvd.nist.gov/vuln/detail/CVE-2025-58434


1 2 3 … 33 34
New: Attack Surface Management · Dark web intelligence. Now with the bigger picture. | Explore SOS Intelligence ASM →
Privacy Settings
We use cookies to enhance your experience while using our website. If you are using our Services via a browser you can restrict, block or remove cookies through your web browser settings. We also use content and scripts from third parties that may use tracking technologies. You can selectively provide your consent below to allow such third party embeds. For complete information about the cookies we use, data we collect and how we process them, please check our Privacy Policy
Youtube
Consent to display content from - Youtube
Vimeo
Consent to display content from - Vimeo
Google Maps
Consent to display content from - Google
Spotify
Consent to display content from - Spotify
Sound Cloud
Consent to display content from - Sound