Customer portal
Articles Tagged with

SOS Intelligence

"SOS
CVE Top 10

The SOS Intelligence CVE Chatter Weekly Top Ten – 18 August 2025


This weekly blog post is from via our unique intelligence collection pipelines. We are your eyes and ears online, including the Dark Web.

There are thousands of vulnerability discussions each week. SOS Intelligence gathers a list of the most discussed Common Vulnerabilities and Exposures (CVE) online for the previous week.

We make every effort to ensure the accuracy of the data presented. As this is an automated process some errors may creep in.

If you are feeling generous please do make us aware of anything you spot, feel free to follow us on Twitter @sosintel and DM us. Thank you!


1.  CVE-2025-8088

A path traversal vulnerability affecting the Windows version of WinRAR allows the attackers to execute arbitrary code by crafting malicious archive files. This vulnerability was exploited in the wild and was discovered by Anton Cherepanov, Peter Košinár, and Peter Strýček
from ESET.

https://nvd.nist.gov/vuln/detail/CVE-2025-8088


2. CVE-2024-38476

Vulnerability in core of Apache HTTP Server 2.4.59 and earlier are vulnerably to information disclosure, SSRF or local script execution via backend applications whose response headers are malicious or exploitable.

Users are recommended to upgrade to version 2.4.60, which fixes this issue.

https://nvd.nist.gov/vuln/detail/CVE-2024-38476


3. CVE-2025-21204

Improper link resolution before file access (‘link following’) in Windows Update Stack allows an authorized attacker to elevate privileges locally.

https://nvd.nist.gov/vuln/detail/CVE-2025-21204


4. CVE-2024-21762

A out-of-bounds write in Fortinet FortiOS versions 7.4.0 through 7.4.2, 7.2.0 through 7.2.6, 7.0.0 through 7.0.13, 6.4.0 through 6.4.14, 6.2.0 through 6.2.15, 6.0.0 through 6.0.17, FortiProxy versions 7.4.0 through 7.4.2, 7.2.0 through 7.2.8, 7.0.0 through 7.0.14, 2.0.0 through 2.0.13, 1.2.0 through 1.2.13, 1.1.0 through 1.1.6, 1.0.0 through 1.0.7 allows attacker to execute unauthorized code or commands via specifically crafted requests

https://nvd.nist.gov/vuln/detail/CVE-2024-21762


5. CVE-2024-21060

Vulnerability in the MySQL Server product of Oracle MySQL (component: Server: Data Dictionary). Supported versions that are affected are 8.0.36 and prior and 8.3.0 and prior. Easily exploitable vulnerability allows high privileged attacker with network access via multiple protocols to compromise MySQL Server. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of MySQL Server. CVSS 3.1 Base Score 4.9 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:N/I:N/A:H).

https://nvd.nist.gov/vuln/detail/CVE-2024-21060


6. CVE-2021-40539

Zoho ManageEngine ADSelfService Plus version 6113 and prior is vulnerable to REST API authentication bypass with resultant remote code execution.

https://nvd.nist.gov/vuln/detail/CVE-2021-40539


7. CVE-2024-10687

The Photos, Files, YouTube, Twitter, Instagram, TikTok, Ecommerce Contest Gallery – Upload, Vote, Sell via PayPal, Social Share Buttons plugin for WordPress is vulnerable to time-based SQL Injection via the $collectedIds parameter in all versions up to, and including, 24.0.3 due to insufficient escaping on the user supplied parameter and lack of sufficient preparation on the existing SQL query. This makes it possible for unauthenticated attackers to append additional SQL queries into already existing queries that can be used to extract sensitive information from the database.

https://nvd.nist.gov/vuln/detail/CVE-2024-10687


8. CVE-2017-8759

Microsoft .NET Framework 2.0, 3.5, 3.5.1, 4.5.2, 4.6, 4.6.1, 4.6.2 and 4.7 allow an attacker to execute code remotely via a malicious document or application, aka “.NET Framework Remote Code Execution Vulnerability.”

https://nvd.nist.gov/vuln/detail/CVE-2017-8759


9. CVE-2016-10033

The mailSend function in the isMail transport in PHPMailer before 5.2.18 might allow remote attackers to pass extra parameters to the mail command and consequently execute arbitrary code via a ” (backslash double quote) in a crafted Sender property.

https://nvd.nist.gov/vuln/detail/CVE-2016-10033


10. CVE-2025-32433

Erlang/OTP is a set of libraries for the Erlang programming language. Prior to versions OTP-27.3.3, OTP-26.2.5.11, and OTP-25.3.2.20, a SSH server may allow an attacker to perform unauthenticated remote code execution (RCE). By exploiting a flaw in SSH protocol message handling, a malicious actor could gain unauthorized access to affected systems and execute arbitrary commands without valid credentials. This issue is patched in versions OTP-27.3.3, OTP-26.2.5.11, and OTP-25.3.2.20. A temporary workaround involves disabling the SSH server or to prevent access via firewall rules.

https://nvd.nist.gov/vuln/detail/CVE-2025-32433


"SOS
CVE Top 10

The SOS Intelligence CVE Chatter Weekly Top Ten – 11 August 2025


This weekly blog post is from via our unique intelligence collection pipelines. We are your eyes and ears online, including the Dark Web.

There are thousands of vulnerability discussions each week. SOS Intelligence gathers a list of the most discussed Common Vulnerabilities and Exposures (CVE) online for the previous week.

We make every effort to ensure the accuracy of the data presented. As this is an automated process some errors may creep in.

If you are feeling generous please do make us aware of anything you spot, feel free to follow us on Twitter @sosintel and DM us. Thank you!


1.  CVE-2025-21204

Improper link resolution before file access (‘link following’) in Windows Update Stack allows an authorized attacker to elevate privileges locally.

https://nvd.nist.gov/vuln/detail/CVE-2025-21204


2. CVE-2024-38476

Vulnerability in core of Apache HTTP Server 2.4.59 and earlier are vulnerably to information disclosure, SSRF or local script execution via backend applications whose response headers are malicious or exploitable.

Users are recommended to upgrade to version 2.4.60, which fixes this issue.

https://nvd.nist.gov/vuln/detail/CVE-2024-38476


3. CVE-2024-21762

A out-of-bounds write in Fortinet FortiOS versions 7.4.0 through 7.4.2, 7.2.0 through 7.2.6, 7.0.0 through 7.0.13, 6.4.0 through 6.4.14, 6.2.0 through 6.2.15, 6.0.0 through 6.0.17, FortiProxy versions 7.4.0 through 7.4.2, 7.2.0 through 7.2.8, 7.0.0 through 7.0.14, 2.0.0 through 2.0.13, 1.2.0 through 1.2.13, 1.1.0 through 1.1.6, 1.0.0 through 1.0.7 allows attacker to execute unauthorized code or commands via specifically crafted requests

https://nvd.nist.gov/vuln/detail/CVE-2024-21762


4. CVE-2017-8759

Microsoft .NET Framework 2.0, 3.5, 3.5.1, 4.5.2, 4.6, 4.6.1, 4.6.2 and 4.7 allow an attacker to execute code remotely via a malicious document or application, aka “.NET Framework Remote Code Execution Vulnerability.”

https://nvd.nist.gov/vuln/detail/CVE-2017-8759


5. CVE-2024-21060

Vulnerability in the MySQL Server product of Oracle MySQL (component: Server: Data Dictionary). Supported versions that are affected are 8.0.36 and prior and 8.3.0 and prior. Easily exploitable vulnerability allows high privileged attacker with network access via multiple protocols to compromise MySQL Server. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of MySQL Server. CVSS 3.1 Base Score 4.9 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:N/I:N/A:H).

https://nvd.nist.gov/vuln/detail/CVE-2024-21060


6. CVE-2021-40539

Zoho ManageEngine ADSelfService Plus version 6113 and prior is vulnerable to REST API authentication bypass with resultant remote code execution.

https://nvd.nist.gov/vuln/detail/CVE-2021-40539


7. CVE-2016-10033

The mailSend function in the isMail transport in PHPMailer before 5.2.18 might allow remote attackers to pass extra parameters to the mail command and consequently execute arbitrary code via a ” (backslash double quote) in a crafted Sender property.

https://nvd.nist.gov/vuln/detail/CVE-2016-10033


8. CVE-2024-10687

The Photos, Files, YouTube, Twitter, Instagram, TikTok, Ecommerce Contest Gallery – Upload, Vote, Sell via PayPal, Social Share Buttons plugin for WordPress is vulnerable to time-based SQL Injection via the $collectedIds parameter in all versions up to, and including, 24.0.3 due to insufficient escaping on the user supplied parameter and lack of sufficient preparation on the existing SQL query. This makes it possible for unauthenticated attackers to append additional SQL queries into already existing queries that can be used to extract sensitive information from the database.

https://nvd.nist.gov/vuln/detail/CVE-2024-10687


9. CVE-2025-21298

Windows OLE Remote Code Execution Vulnerability

https://nvd.nist.gov/vuln/detail/CVE-2025-21298


10. CVE-2024-6409

A race condition vulnerability was discovered in how signals are handled by OpenSSH’s server (sshd). If a remote attacker does not authenticate within a set time period, then sshd’s SIGALRM handler is called asynchronously. However, this signal handler calls various functions that are not async-signal-safe, for example, syslog(). As a consequence of a successful attack, in the worst case scenario, an attacker may be able to perform a remote code execution (RCE) as an unprivileged user running the sshd server.

https://nvd.nist.gov/vuln/detail/CVE-2024-6409


"Behind
Investigation, Opinion

Behind the Mask: Creating and Maintaining Sock Puppet Accounts for Online Research

When conducting online research or gathering open-source intelligence (OSINT), it is often necessary to observe or interact with digital spaces without revealing your true identity. This is where sock puppet accounts come into play. A sock puppet is a fictitious online identity created to access information, join closed groups, monitor activity, or engage with targets while protecting the researcher’s real identity and intent.

Used properly, sock puppets are an essential part of an investigator’s toolkit. However, their creation and use come with both ethical and legal responsibilities. Misuse can lead to legal consequences, reputational damage, or compromised investigations. Practitioners must always follow legal guidance and act within clearly defined ethical boundaries.

In this blog, we will explore how to plan, create, and maintain effective sock puppet accounts for OSINT purposes. We will discuss key operational security (OPSEC) measures, common pitfalls to avoid, and strategies for maintaining a convincing online persona over time. Whether you are new to this practice or looking to refine your approach, this guide will help you lay a solid foundation for safe and responsible online research.

What Is a Sock Puppet Account?

A sock puppet account is a false or alternate online identity used to conceal the true identity of the user behind it. In the context of online investigations and intelligence gathering, sock puppets allow researchers to access and monitor digital spaces without drawing attention to their real-world affiliations or investigative purpose.

These accounts are beneficial in OSINT investigations where anonymity is critical. They may be used to:

  • Access private or semi-restricted forums and groups
  • Observe conversations on social media without alerting subjects
  • Collect threat intelligence from Dark Web marketplaces or closed communities
  • Engage with individuals or groups in a way that does not compromise operational security

While sock puppets can be powerful tools, their use must always be underpinned by legal and ethical awareness. Investigators should never use false identities to entrap, manipulate, or harass individuals. The goal is passive information gathering, not interference or provocation. Moreover, laws governing online impersonation, data protection, and computer misuse vary between jurisdictions, and it is the investigator’s responsibility to ensure compliance.

Wherever possible, work within organisational policies, maintain internal approval processes for sensitive research, and document all actions for accountability. Ethical OSINT hinges not only on what can be done, but on what should be done.

Planning Your Sock Puppet Strategy

Before creating a sock puppet account, it is essential to define a clear objective. What do you need the account to do? Your goal might be to passively observe a forum, monitor a social media group, or engage with a specific individual or community. The purpose of the account will shape every decision that follows, from the choice of platform to the construction of your online persona.

Understanding your target environment is a crucial part of this planning stage. Different platforms have different norms, verification processes, and levels of scrutiny. A persona that appears credible on Reddit might not be believable on LinkedIn. Consider regional factors as well: language, time zone, and cultural references all contribute to the authenticity of an account. An inconsistency in these details can quickly arouse suspicion.

With your objective and environment defined, you can begin to craft a suitable cover story. This should include a basic biography, a plausible location, interests relevant to the communities you plan to interact with, and a consistent tone of voice. Keep the persona simple, but detailed enough to withstand casual scrutiny. Avoid unnecessary complexity, which can increase the risk of contradictions or mistakes.

A well-planned sock puppet starts long before the account is created. By aligning your objectives with your operational context and building a realistic backstory, you lay the groundwork for a credible and sustainable online identity.

Creating the Sock Puppet Account

Once your planning is complete, the next step is to create the sock puppet account itself. This process involves selecting the right platform, crafting a believable identity, and ensuring that your setup maintains strong operational security from the outset.

Choosing the Right Platform

Select your platform based on the objective of the investigation. If you need to observe professional activity or gather company intelligence, LinkedIn might be appropriate. For community discussions, Reddit or Discord may be more useful. For threat intelligence gathering, forums or encrypted messaging apps could be more suitable. Each platform has its own registration process, verification requirements, and user expectations, all of which must be considered.

Crafting a Believable Identity

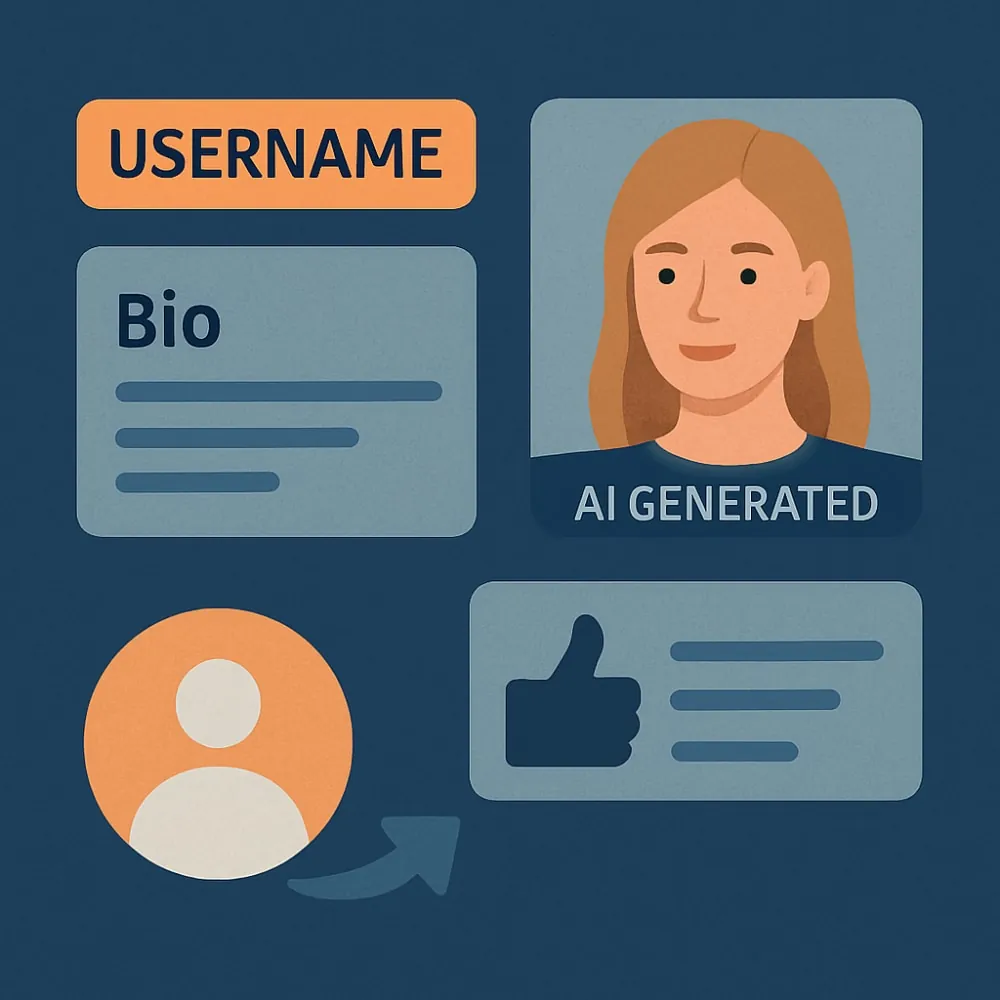
A convincing sock puppet needs to pass casual inspection. Start with a realistic username and a dedicated email address that fits your persona. Avoid using anything that resembles your real name or any identifiers linked to your organisation.

  • Profile photo: Use AI-generated images or copyright-free alternatives. Tools like ThisPersonDoesNotExist or Generated Photos can be helpful, but check for anomalies that might raise suspicion.
  • Biography and interests: Write a brief, plausible bio that fits the persona and platform. Add relevant interests or affiliations to make the account appear active and authentic.
  • Posting behaviour: Mirror the tone, grammar, and posting frequency typical for the platform and user type. If your persona is a 30-year-old from Manchester, for example, ensure the language and topics reflect that identity.
  • Language consistency: Stick to one language and dialect throughout. Switching between different styles or regions can be a clear indicator of inauthenticity.

Acquiring a Clean IP

To prevent your real identity or location from being linked to the sock puppet, use a clean and separate IP address. A reputable VPN or proxy service is essential, and in some cases, a dedicated virtual machine or separate device should be used. Avoid logging in to real accounts or using your usual browser within the same environment, as cross-contamination can compromise the entire operation.

Account creation is not just about filling in a form. Every detail, from your profile picture to your browser setup, contributes to the believability and security of the puppet. Take your time, document each step, and treat the identity as if it were real.

OPSEC Considerations

Operational Security (OPSEC) is critical to the effective use of sock puppet accounts. Without proper precautions, it is easy to leave digital traces that link back to your real identity or organisation. To maintain credibility and protect yourself, you must build strong habits around device use, network hygiene, and identity compartmentalisation.

Device and Network Isolation

Always use a dedicated environment for sock puppet activity. This might be a virtual machine (VM), a separate user profile, or an entirely distinct physical device. The key is to ensure that no personal data, saved credentials, or browsing habits from your real identity carry over into the puppet’s digital footprint. Similarly, connect via a trusted VPN or proxy with a location appropriate to the persona. Never use your home or work IP address when managing sock puppets.

Avoiding Contamination

Cross-contamination with real accounts is one of the most common OPSEC failures. Use a clean browser instance with no saved cookies, autofill data, or extensions that may reveal identifying information. Consider using privacy-focused browsers or containerised browsing sessions to isolate activity. Disable features like browser synchronisation or automatic logins, which could leak personal credentials.

Using Burner Phones and Anonymous Email

When platforms require phone numbers for verification, use a burner device or a secure, anonymised SMS service, provided it complies with legal and policy requirements. Similarly, choose privacy-conscious email providers such as ProtonMail or Tutanota. The email address should align with the puppet’s identity and not reference any real-world details.

Password and Account Recovery Separation

Treat sock puppets as standalone entities. Use unique, complex passwords for each account and manage them using a secure password manager. Keep recovery options consistent with the identity – never link your real email or phone number. If using recovery questions, invent answers that match the puppet’s backstory and document them securely.

Logging and Documentation

Maintain secure records of your sock puppets, including account details, access credentials, personas, activity logs, and creation dates. This helps track usage over time, identify potential compromises, and safely retire or rotate identities when needed. Store this information in an encrypted format or within a secure password management tool.

Sock puppet OPSEC is not about one-time precautions – it requires ongoing discipline. A single mistake can expose your identity or compromise the entire investigation. Take a cautious, methodical approach and revisit your OPSEC practices regularly.

Maintaining Sock Puppets Over Time

Creating a sock puppet is only the beginning. To remain credible and useful over time, the account must appear active, consistent, and authentic. Dormant or obviously artificial profiles are more likely to be flagged by platforms or ignored by the communities you are trying to observe. Maintaining a sock puppet means simulating the behaviour of a genuine user, without attracting unnecessary attention.

Simulating Real Behaviour

Regular interaction is key to building a believable presence. Depending on the platform, this might include:

  • Liking or sharing posts
  • Following relevant accounts or joining groups
  • Commenting or replying in a manner consistent with the persona

These interactions should be contextually appropriate and contribute to the puppet’s credibility. For example, a user who claims to be interested in cybersecurity might follow industry influencers, comment on relevant articles, or share news stories.

Scheduling Realistic Activity Patterns

Sock puppets should reflect normal online behaviour. Consider the timezone and daily schedule of the persona. If your puppet claims to be based in Berlin, it would be unusual for them to post at 3 a.m. local time. Avoid excessive or erratic posting, which can appear automated or suspicious. A light but consistent activity pattern over time is more convincing than bursts of high engagement.

Avoiding Automation Red Flags

Some platforms are aggressive in detecting and removing accounts that behave like bots. Avoid scripted or repeated actions, especially immediately after account creation. Do not mass-follow users or copy-paste identical comments across threads. Behave like a real person – slow, deliberate, and occasionally imperfect.

Regularly Updating Profile Content

Real users update their profiles from time to time. Refresh your puppet’s bio, add a new interest, or change a profile picture occasionally to reflect life events or shifting interests. These subtle changes reinforce the illusion of an active, evolving online identity.

Ultimately, a successful sock puppet account blends in. It should quietly accumulate a digital footprint that supports its cover story and gives you access to the information you need, without ever drawing attention to itself.

Risks, Red Flags, and Account Burnout

Even well-crafted sock puppets carry risk. Platforms continue to improve their ability to detect suspicious behaviour, and users themselves may flag accounts that appear inauthentic. Understanding common warning signs and knowing when to retire or rotate an identity is key to maintaining long-term operational capability.

Common Ways Sock Puppets Get Flagged or Banned

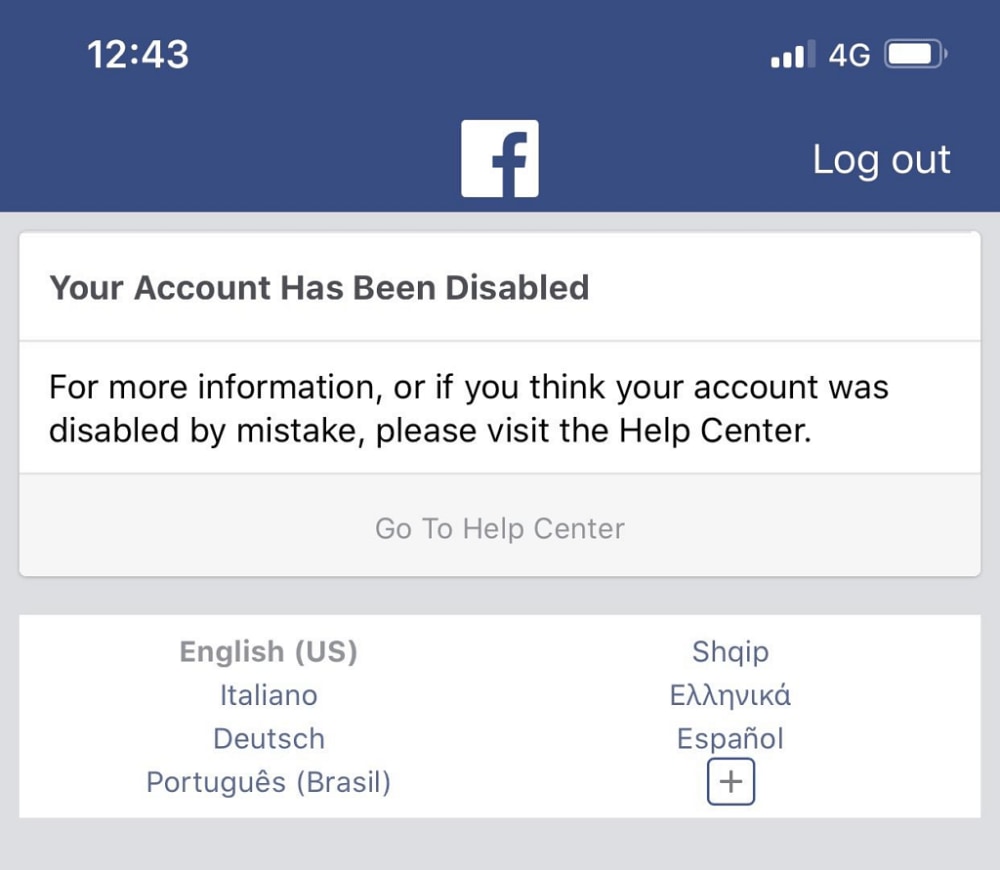
Sock puppets may be suspended or deleted for a range of reasons, including:

  • Logging in from multiple geographic locations in a short space of time
  • Sudden spikes in activity (e.g. mass liking, following, or posting)
  • Use of stock or AI-generated profile images that resemble known fake accounts
  • Repeated use of the same contact details, browser fingerprint, or device setup
  • Lack of meaningful interaction or organic growth over time

Even a single policy violation can draw scrutiny, particularly on mainstream social media platforms where automated systems are quick to act.

Avoiding Repetitive Patterns Across Accounts

If you operate multiple sock puppets, ensure that each has a unique and independent identity. Reusing the same backstory, writing style, or image sources across accounts can make them easier to detect and link together. Separate devices, email addresses, and behavioural traits help to isolate each puppet and reduce the risk of a cascading compromise.

When to Retire a Puppet and How to Replace It Safely

No sock puppet should be considered permanent. If an account is inactive, becomes untrustworthy, or begins attracting unwanted attention, it is often safer to retire it than to try and recover its credibility. Before deletion, remove any content that could be linked to other operations. Keep a log of why it was retired, and plan how a replacement will fill the same role with improved safeguards.

Having Backup Identities Ready

To ensure continuity, it is good practice to maintain a small number of standby identities.  This is sometimes referred to as a “puppet farm”. These can be developed gradually in the background, gaining basic credibility over time, so they are ready to use when needed. In some cases, it may also be appropriate to establish layered personas, where one puppet supports or interacts with another to enhance realism.

Maintaining sock puppets is an operational task that requires regular attention. The digital landscape shifts constantly, and even the most convincing puppet may eventually outlive its usefulness. Being prepared to adapt is vital.

7. Tools and Resources

Successful sock puppet operations depend not only on planning and technique, but also on using the right tools to support anonymity, security, and realism. The following categories highlight essential resources for anyone managing online personas, with emphasis on privacy-focused solutions.

VPNs and Secure Browsers

To prevent IP address leaks or location-based flags, always connect through a reliable virtual private network (VPN). Services such as Mullvad or Proton VPN offer privacy-focused features without logging user activity. In addition, using secure or privacy-hardened browsers, such as Firefox with privacy containers, Brave, or Tor Browser, can help prevent tracking and cross-contamination between real and sock puppet identities.

For advanced operations, consider launching sock puppets within secure environments such as Tails OS or a hardened virtual machine to reduce the digital footprint even further.

Image Generation Tools

Choosing a believable profile image is vital. AI-generated photo tools like ThisPersonDoesNotExist or Generated.Photos create unique images that are not traceable to real people, reducing the risk of impersonation claims. However, these images should be reviewed carefully for visual anomalies that might suggest they are artificial. Alternatively, use licence-free photo repositories where permitted.

Secure Email Services

Every puppet should have its own email address from a secure, privacy-conscious provider. Services such as ProtonMail, Tutanota, or Mailfence are widely used for this purpose. Avoid mainstream providers that require phone verification or link accounts to existing profiles. Where possible, create the email account using the same VPN and device you plan to use for the puppet itself.

Password and Identity Managers

Managing multiple identities requires strict separation and secure record-keeping. Tools like Bitwarden, KeePassXC, or 1Password can be used to store login details, backstory notes, recovery options, and activity logs in an encrypted format. Avoid reusing passwords or security questions across accounts, and clearly label each identity to avoid mistakes.

Burner Phone and SMS Services

Some platforms require phone number verification. Where legally permitted, use burner phones or temporary SMS services to meet this requirement. Options include physical SIMs with disposable devices or online services such as MySudo or Silent Link, though reliability and legality vary by region. Never use your personal or work number under any circumstances.

A well-prepared toolkit makes managing sock puppets more secure, efficient, and scalable. Review your tools regularly, keep backups where needed, and ensure you remain up to date with changes in platform behaviour or verification processes.

Final Thoughts and Best Practices

Sock puppet accounts are powerful tools for legitimate online research. When used responsibly, they enable investigators, analysts, and researchers to access vital information, monitor digital threats, and engage with online communities without exposing their true identity. However, with this capability comes a significant ethical and operational responsibility.

These accounts should never be used to deceive, manipulate, or harm individuals. Their purpose is to observe, gather intelligence, and support investigations that serve the public interest or protect organisations from threats. Operating within legal boundaries and upholding professional standards is essential.

The digital landscape is constantly changing. Platforms evolve, detection methods improve, and user behaviour shifts. This means sock puppet strategies must also be regularly reviewed and refined. What works today may not be effective tomorrow, so ongoing learning and adaptation are key to maintaining both access and security.

Finally, any organisation or individual engaging in this kind of work should develop their own standard operating procedures (SOPs). These should include clear guidelines for planning, creation, use, and retirement of sock puppet accounts. Testing identities in controlled environments before deploying them for real investigations can also help identify weaknesses before they become liabilities.

Used with care, discipline, and a strong ethical framework, sock puppets can provide valuable insight while keeping investigators safe and discreet.

Red flag photo by Paolo Bendandi and sock puppet photo by Natalie Kinnear.

"SOS
CVE Top 10

The SOS Intelligence CVE Chatter Weekly Top Ten – 04 August 2025


This weekly blog post is from via our unique intelligence collection pipelines. We are your eyes and ears online, including the Dark Web.

There are thousands of vulnerability discussions each week. SOS Intelligence gathers a list of the most discussed Common Vulnerabilities and Exposures (CVE) online for the previous week.

We make every effort to ensure the accuracy of the data presented. As this is an automated process some errors may creep in.

If you are feeling generous please do make us aware of anything you spot, feel free to follow us on Twitter @sosintel and DM us. Thank you!


1.  CVE-2025-21298

Windows OLE Remote Code Execution Vulnerability

https://nvd.nist.gov/vuln/detail/CVE-2025-21298


2. CVE-2025-53770

Deserialization of untrusted data in on-premises Microsoft SharePoint Server allows an unauthorized attacker to execute code over a network.
Microsoft is aware that an exploit for CVE-2025-53770 exists in the wild.
Microsoft is preparing and fully testing a comprehensive update to address this vulnerability. In the meantime, please make sure that the mitigation provided in this CVE documentation is in place so that you are protected from exploitation.

https://nvd.nist.gov/vuln/detail/CVE-2025-53770


3. CVE-2025-5287

The Likes and Dislikes Plugin plugin for WordPress is vulnerable to SQL Injection via the ‘post’ parameter in all versions up to, and including, 1.0.0 due to insufficient escaping on the user supplied parameter and lack of sufficient preparation on the existing SQL query. This makes it possible for unauthenticated attackers to append additional SQL queries into already existing queries that can be used to extract sensitive information from the database.

https://nvd.nist.gov/vuln/detail/CVE-2025-5287


4. CVE-2025-49704

Improper control of generation of code (‘code injection’) in Microsoft Office SharePoint allows an authorized attacker to execute code over a network.

https://nvd.nist.gov/vuln/detail/CVE-2025-49704


5. CVE-2024-23660

The Binance Trust Wallet app for iOS in commit 3cd6e8f647fbba8b5d8844fcd144365a086b629f, git tag 0.0.4 misuses the trezor-crypto library and consequently generates mnemonic words for which the device time is the only entropy source, leading to economic losses, as exploited in the wild in July 2023. An attacker can systematically generate mnemonics for each timestamp within an applicable timeframe, and link them to specific wallet addresses in order to steal funds from those wallets.

https://nvd.nist.gov/vuln/detail/CVE-2024-23660


6. CVE-2025-49706

Improper authentication in Microsoft Office SharePoint allows an unauthorized attacker to perform spoofing over a network.

https://nvd.nist.gov/vuln/detail/CVE-2025-49706


7. CVE-2025-53771

Improper authentication in Microsoft Office SharePoint allows an unauthorized attacker to perform spoofing over a network.

https://nvd.nist.gov/vuln/detail/CVE-2025-53771


8. CVE-2024-38476

Vulnerability in core of Apache HTTP Server 2.4.59 and earlier are vulnerably to information disclosure, SSRF or local script execution via backend applications whose response headers are malicious or exploitable.

Users are recommended to upgrade to version 2.4.60, which fixes this issue.

https://nvd.nist.gov/vuln/detail/CVE-2024-38476


9. CVE-2025-20337

A vulnerability in a specific API of Cisco ISE and Cisco ISE-PIC could allow an unauthenticated, remote attacker to execute arbitrary code on the underlying operating system as root. The attacker does not require any valid credentials to exploit this vulnerability.

This vulnerability is due to insufficient validation of user-supplied input. An attacker could exploit this vulnerability by submitting a crafted API request. A successful exploit could allow the attacker to obtain root privileges on an affected device.

https://nvd.nist.gov/vuln/detail/CVE-2025-20337


10. CVE-2025-6554

Type confusion in V8 in Google Chrome prior to 138.0.7204.96 allowed a remote attacker to perform arbitrary read/write via a crafted HTML page. (Chromium security severity: High)

https://nvd.nist.gov/vuln/detail/CVE-2025-6554


"SOS
CVE Top 10

The SOS Intelligence CVE Chatter Weekly Top Ten – 28 July 2025


This weekly blog post is from via our unique intelligence collection pipelines. We are your eyes and ears online, including the Dark Web.

There are thousands of vulnerability discussions each week. SOS Intelligence gathers a list of the most discussed Common Vulnerabilities and Exposures (CVE) online for the previous week.

We make every effort to ensure the accuracy of the data presented. As this is an automated process some errors may creep in.

If you are feeling generous please do make us aware of anything you spot, feel free to follow us on Twitter @sosintel and DM us. Thank you!


1.  CVE-2017-5689

An unprivileged network attacker could gain system privileges to provisioned Intel manageability SKUs: Intel Active Management Technology (AMT) and Intel Standard Manageability (ISM). An unprivileged local attacker could provision manageability features gaining unprivileged network or local system privileges on Intel manageability SKUs: Intel Active Management Technology (AMT), Intel Standard Manageability (ISM), and Intel Small Business Technology (SBT).

https://nvd.nist.gov/vuln/detail/CVE-2017-5689


2. CVE-2025-53770

Deserialization of untrusted data in on-premises Microsoft SharePoint Server allows an unauthorized attacker to execute code over a network.
Microsoft is aware that an exploit for CVE-2025-53770 exists in the wild.
Microsoft is preparing and fully testing a comprehensive update to address this vulnerability. In the meantime, please make sure that the mitigation provided in this CVE documentation is in place so that you are protected from exploitation.

https://nvd.nist.gov/vuln/detail/CVE-2025-53770


3. CVE-2025-49706

Improper authentication in Microsoft Office SharePoint allows an unauthorized attacker to perform spoofing over a network.

https://nvd.nist.gov/vuln/detail/CVE-2025-49706


4. CVE-2025-49704

Improper control of generation of code (‘code injection’) in Microsoft Office SharePoint allows an authorized attacker to execute code over a network.

https://nvd.nist.gov/vuln/detail/CVE-2025-49704


5. CVE-2025-47165

Use after free in Microsoft Office Excel allows an unauthorized attacker to execute code locally.

https://nvd.nist.gov/vuln/detail/CVE-2025-47165


6. CVE-2025-27817

A possible arbitrary file read and SSRF vulnerability has been identified in Apache Kafka Client. Apache Kafka Clients accept configuration data for setting the SASL/OAUTHBEARER connection with the brokers, including “sasl.oauthbearer.token.endpoint.url” and “sasl.oauthbearer.jwks.endpoint.url”. Apache Kafka allows clients to read an arbitrary file and return the content in the error log, or sending requests to an unintended location. In applications where Apache Kafka Clients configurations can be specified by an untrusted party, attackers may use the “sasl.oauthbearer.token.endpoint.url” and “sasl.oauthbearer.jwks.endpoint.url” configuratin to read arbitrary contents of the disk and environment variables or make requests to an unintended location. In particular, this flaw may be used in Apache Kafka Connect to escalate from REST API access to filesystem/environment/URL access, which may be undesirable in certain environments, including SaaS products.

Since Apache Kafka 3.9.1/4.0.0, we have added a system property (“-Dorg.apache.kafka.sasl.oauthbearer.allowed.urls”) to set the allowed urls in SASL JAAS configuration. In 3.9.1, it accepts all urls by default for backward compatibility. However in 4.0.0 and newer, the default value is empty list and users have to set the allowed urls explicitly.

https://nvd.nist.gov/vuln/detail/CVE-2025-27817


7. CVE-2025-6554

Type confusion in V8 in Google Chrome prior to 138.0.7204.96 allowed a remote attacker to perform arbitrary read/write via a crafted HTML page. (Chromium security severity: High)

https://nvd.nist.gov/vuln/detail/CVE-2025-6554


8. CVE-2025-48799

Improper link resolution before file access (‘link following’) in Windows Update Service allows an authorized attacker to elevate privileges locally.

https://nvd.nist.gov/vuln/detail/CVE-2025-48799


9. CVE-2025-53771

Improper limitation of a pathname to a restricted directory (‘path traversal’) in Microsoft Office SharePoint allows an unauthorized attacker to perform spoofing over a network.

https://nvd.nist.gov/vuln/detail/CVE-2025-53771


10. CVE-2024-6409

A race condition vulnerability was discovered in how signals are handled by OpenSSH’s server (sshd). If a remote attacker does not authenticate within a set time period, then sshd’s SIGALRM handler is called asynchronously. However, this signal handler calls various functions that are not async-signal-safe, for example, syslog(). As a consequence of a successful attack, in the worst case scenario, an attacker may be able to perform a remote code execution (RCE) as an unprivileged user running the sshd server.

https://nvd.nist.gov/vuln/detail/CVE-2024-6409


"SOS
CVE Top 10

The SOS Intelligence CVE Chatter Weekly Top Ten – 21 July 2025


This weekly blog post is from via our unique intelligence collection pipelines. We are your eyes and ears online, including the Dark Web.

There are thousands of vulnerability discussions each week. SOS Intelligence gathers a list of the most discussed Common Vulnerabilities and Exposures (CVE) online for the previous week.

We make every effort to ensure the accuracy of the data presented. As this is an automated process some errors may creep in.

If you are feeling generous please do make us aware of anything you spot, feel free to follow us on Twitter @sosintel and DM us. Thank you!


1.  CVE-2021-40539

Zoho ManageEngine ADSelfService Plus version 6113 and prior is vulnerable to REST API authentication bypass with resultant remote code execution.

https://nvd.nist.gov/vuln/detail/CVE-2021-40539


2. CVE-2025-6554

Type confusion in V8 in Google Chrome prior to 138.0.7204.96 allowed a remote attacker to perform arbitrary read/write via a crafted HTML page. (Chromium security severity: High)

https://nvd.nist.gov/vuln/detail/CVE-2025-6554


3. CVE-2021-44228

Apache Log4j2 2.0-beta9 through 2.15.0 (excluding security releases 2.12.2, 2.12.3, and 2.3.1) JNDI features used in configuration, log messages, and parameters do not protect against attacker controlled LDAP and other JNDI related endpoints. An attacker who can control log messages or log message parameters can execute arbitrary code loaded from LDAP servers when message lookup substitution is enabled. From log4j 2.15.0, this behavior has been disabled by default. From version 2.16.0 (along with 2.12.2, 2.12.3, and 2.3.1), this functionality has been completely removed. Note that this vulnerability is specific to log4j-core and does not affect log4net, log4cxx, or other Apache Logging Services projects.

https://nvd.nist.gov/vuln/detail/CVE-2021-44228


4. CVE-2025-5287

The Likes and Dislikes Plugin plugin for WordPress is vulnerable to SQL Injection via the ‘post’ parameter in all versions up to, and including, 1.0.0 due to insufficient escaping on the user supplied parameter and lack of sufficient preparation on the existing SQL query. This makes it possible for unauthenticated attackers to append additional SQL queries into already existing queries that can be used to extract sensitive information from the database.

https://nvd.nist.gov/vuln/detail/CVE-2025-5287


5. CVE-2024-21762

A out-of-bounds write in Fortinet FortiOS versions 7.4.0 through 7.4.2, 7.2.0 through 7.2.6, 7.0.0 through 7.0.13, 6.4.0 through 6.4.14, 6.2.0 through 6.2.15, 6.0.0 through 6.0.17, FortiProxy versions 7.4.0 through 7.4.2, 7.2.0 through 7.2.8, 7.0.0 through 7.0.14, 2.0.0 through 2.0.13, 1.2.0 through 1.2.13, 1.1.0 through 1.1.6, 1.0.0 through 1.0.7 allows attacker to execute unauthorized code or commands via specifically crafted requests

https://nvd.nist.gov/vuln/detail/CVE-2024-21762


6. CVE-2024-21060

Vulnerability in the MySQL Server product of Oracle MySQL (component: Server: Data Dictionary). Supported versions that are affected are 8.0.36 and prior and 8.3.0 and prior. Easily exploitable vulnerability allows high privileged attacker with network access via multiple protocols to compromise MySQL Server. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of MySQL Server. CVSS 3.1 Base Score 4.9 (Availability impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:H/UI:N/S:U/C:N/I:N/A:H).

https://nvd.nist.gov/vuln/detail/CVE-2024-21060


7. CVE-2017-8759

Microsoft .NET Framework 2.0, 3.5, 3.5.1, 4.5.2, 4.6, 4.6.1, 4.6.2 and 4.7 allow an attacker to execute code remotely via a malicious document or application, aka “.NET Framework Remote Code Execution Vulnerability.”

https://nvd.nist.gov/vuln/detail/CVE-2017-8759


8. CVE-2016-10033

The mailSend function in the isMail transport in PHPMailer before 5.2.18 might allow remote attackers to pass extra parameters to the mail command and consequently execute arbitrary code via a ” (backslash double quote) in a crafted Sender property.

https://nvd.nist.gov/vuln/detail/CVE-2016-10033


9. CVE-2024-10687

The Photos, Files, YouTube, Twitter, Instagram, TikTok, Ecommerce Contest Gallery – Upload, Vote, Sell via PayPal, Social Share Buttons plugin for WordPress is vulnerable to time-based SQL Injection via the $collectedIds parameter in all versions up to, and including, 24.0.3 due to insufficient escaping on the user supplied parameter and lack of sufficient preparation on the existing SQL query. This makes it possible for unauthenticated attackers to append additional SQL queries into already existing queries that can be used to extract sensitive information from the database.

https://nvd.nist.gov/vuln/detail/CVE-2024-10687


10. CVE-2016-1252

The apt package in Debian jessie before 1.0.9.8.4, in Debian unstable before 1.4~beta2, in Ubuntu 14.04 LTS before 1.0.1ubuntu2.17, in Ubuntu 16.04 LTS before 1.2.15ubuntu0.2, and in Ubuntu 16.10 before 1.3.2ubuntu0.1 allows man-in-the-middle attackers to bypass a repository-signing protection mechanism by leveraging improper error handling when validating InRelease file signatures.

https://nvd.nist.gov/vuln/detail/CVE-2016-1252


"SOS
CVE Top 10

The SOS Intelligence CVE Chatter Weekly Top Ten – 14 July 2025


This weekly blog post is from via our unique intelligence collection pipelines. We are your eyes and ears online, including the Dark Web.

There are thousands of vulnerability discussions each week. SOS Intelligence gathers a list of the most discussed Common Vulnerabilities and Exposures (CVE) online for the previous week.

We make every effort to ensure the accuracy of the data presented. As this is an automated process some errors may creep in.

If you are feeling generous please do make us aware of anything you spot, feel free to follow us on Twitter @sosintel and DM us. Thank you!


1.  CVE-2025-5287

The Likes and Dislikes Plugin plugin for WordPress is vulnerable to SQL Injection via the ‘post’ parameter in all versions up to, and including, 1.0.0 due to insufficient escaping on the user supplied parameter and lack of sufficient preparation on the existing SQL query. This makes it possible for unauthenticated attackers to append additional SQL queries into already existing queries that can be used to extract sensitive information from the database.

https://nvd.nist.gov/vuln/detail/CVE-2025-5287


2. CVE-2025-24813

Path Equivalence: ‘file.Name’ (Internal Dot) leading to Remote Code Execution and/or Information disclosure and/or malicious content added to uploaded files via write enabled Default Servlet in Apache Tomcat.

This issue affects Apache Tomcat: from 11.0.0-M1 through 11.0.2, from 10.1.0-M1 through 10.1.34, from 9.0.0.M1 through 9.0.98.

If all of the following were true, a malicious user was able to view security sensitive files and/or inject content into those files:
– writes enabled for the default servlet (disabled by default)
– support for partial PUT (enabled by default)
– a target URL for security sensitive uploads that was a sub-directory of a target URL for public uploads
– attacker knowledge of the names of security sensitive files being uploaded
– the security sensitive files also being uploaded via partial PUT

If all of the following were true, a malicious user was able to perform remote code execution:
– writes enabled for the default servlet (disabled by default)
– support for partial PUT (enabled by default)
– application was using Tomcat’s file based session persistence with the default storage location
– application included a library that may be leveraged in a deserialization attack

Users are recommended to upgrade to version 11.0.3, 10.1.35 or 9.0.99, which fixes the issue.

https://nvd.nist.gov/vuln/detail/CVE-2025-24813


3. CVE-2021-40539

Zoho ManageEngine ADSelfService Plus version 6113 and prior is vulnerable to REST API authentication bypass with resultant remote code execution.

https://nvd.nist.gov/vuln/detail/CVE-2021-40539


4. CVE-2022-3602

A buffer overrun can be triggered in X.509 certificate verification, specifically in name constraint checking. Note that this occurs after certificate chain signature verification and requires either a CA to have signed the malicious certificate or for the application to continue certificate verification despite failure to construct a path to a trusted issuer. An attacker can craft a malicious email address to overflow four attacker-controlled bytes on the stack. This buffer overflow could result in a crash (causing a denial of service) or potentially remote code execution. Many platforms implement stack overflow protections which would mitigate against the risk of remote code execution. The risk may be further mitigated based on stack layout for any given platform/compiler. Pre-announcements of CVE-2022-3602 described this issue as CRITICAL. Further analysis based on some of the mitigating factors described above have led this to be downgraded to HIGH. Users are still encouraged to upgrade to a new version as soon as possible. In a TLS client, this can be triggered by connecting to a malicious server. In a TLS server, this can be triggered if the server requests client authentication and a malicious client connects. Fixed in OpenSSL 3.0.7 (Affected 3.0.0,3.0.1,3.0.2,3.0.3,3.0.4,3.0.5,3.0.6).

https://nvd.nist.gov/vuln/detail/CVE-2022-3602


5. CVE-2024-24919

Potentially allowing an attacker to read certain information on Check Point Security Gateways once connected to the internet and enabled with remote Access VPN or Mobile Access Software Blades. A Security fix that mitigates this vulnerability is available.

https://nvd.nist.gov/vuln/detail/CVE-2024-24919


6. CVE-2025-5777

Insufficient input validation leading to memory overread when the NetScaler is configured as a Gateway (VPN virtual server, ICA Proxy, CVPN, RDP Proxy) OR AAA virtual server

https://nvd.nist.gov/vuln/detail/CVE-2025-5777


7. CVE-2022-3786

A buffer overrun can be triggered in X.509 certificate verification, specifically in name constraint checking. Note that this occurs after certificate chain signature verification and requires either a CA to have signed a malicious certificate or for an application to continue certificate verification despite failure to construct a path to a trusted issuer. An attacker can craft a malicious email address in a certificate to overflow an arbitrary number of bytes containing the `.’ character (decimal 46) on the stack. This buffer overflow could result in a crash (causing a denial of service). In a TLS client, this can be triggered by connecting to a malicious server. In a TLS server, this can be triggered if the server requests client authentication and a malicious client connects.

https://nvd.nist.gov/vuln/detail/CVE-2022-3786


8. CVE-2025-6554

Type confusion in V8 in Google Chrome prior to 138.0.7204.96 allowed a remote attacker to perform arbitrary read/write via a crafted HTML page. (Chromium security severity: High)

https://nvd.nist.gov/vuln/detail/CVE-2025-6554


9. CVE-2025-33073

Improper access control in Windows SMB allows an authorized attacker to elevate privileges over a network.

https://nvd.nist.gov/vuln/detail/CVE-2025-33073


10. CVE-2025-6430

When a file download is specified via the `Content-Disposition` header, that directive would be ignored if the file was included via a `<embed>` or `<object>` tag, potentially making a website vulnerable to a cross-site scripting attack. This vulnerability affects Firefox < 140 and Firefox ESR < 128.12.

https://nvd.nist.gov/vuln/detail/CVE-2025-6430


"Why
Investigation, Opinion

Why Hackers Hack: Exploring What Motivates Cybercriminal Activity

Cybercrime continues to rise in scale, complexity and impact, affecting individuals, businesses and governments alike. While much attention is given to how attacks happen, it’s just as important to ask why they occur in the first place. Understanding what motivates attackers is a crucial part of building an effective defence.

So, why do hackers hack?

Some are driven by financial gain, while others act on behalf of a nation-state or in support of a political cause. There are those motivated by revenge or personal challenge, and others who simply exploit opportunities because they can.

In this post, we explore the key motivations behind cybercriminal activity, helping you better understand the intent behind the threat and its implications for your organisation’s security posture.

Financial Gain

For many cybercriminals, money is the primary motivator. The vast majority of cybercrime is financially driven, with threat actors seeking to extract value from individuals, businesses or governments through theft, fraud or extortion.

Ransomware is perhaps the most well-known example. Attackers encrypt a victim’s data and demand payment, usually in cryptocurrency, in exchange for the decryption key. The rise of Ransomware-as-a-Service (RaaS) has made these attacks more accessible, allowing less technically skilled criminals to launch sophisticated campaigns using tools developed by others.

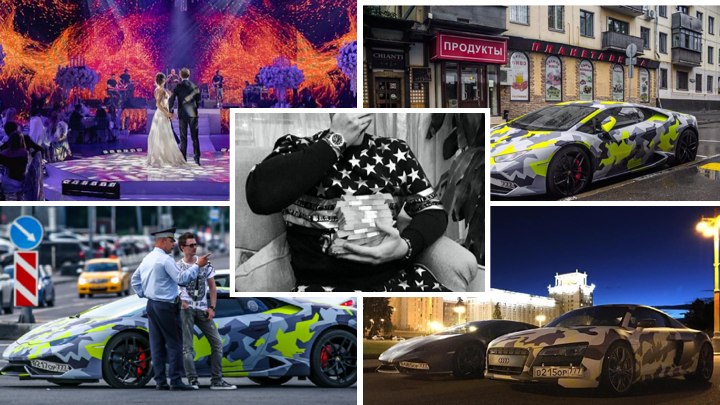
One of the most notorious examples of financially motivated cybercrime is Evil Corp, a Russia-based cybercrime group responsible for developing and distributing the Dridex banking Trojan and BitPaymer ransomware. The group, led by Maksim Yakubets, has been linked to attacks that have caused hundreds of millions of pounds in damages globally. According to the U.S. Department of the Treasury, Yakubets was allegedly tasked by Russian intelligence to conduct espionage operations alongside his cybercriminal activities. He is known not just for the scale of his crimes, but also for flaunting his wealth – reportedly driving a Lamborghini with a personalised number plate that reads “THIEF”.

Phishing and business email compromise (BEC) are also common financially motivated attacks. These techniques are designed to trick victims into handing over login credentials, payment details or other sensitive information that can be monetised directly or resold on dark web marketplaces. The FBI has reported billions of dollars in losses from BEC schemes, which often involve attackers impersonating executives or suppliers to redirect large financial transactions.

What’s particularly concerning is how mature and professionalised the cybercriminal ecosystem has become. Online forums and marketplaces, often hosted on the dark web, serve as thriving hubs where criminals buy and sell tools, data and services. This includes malware, exploit kits, stolen credentials and even technical support for other attackers. Some actors specialise in initial access, others in data theft or extortion, and many operate purely as brokers or facilitators.

As a result, modern cyberattacks are rarely the work of a lone hacker. Instead, they often involve multiple actors working together across a decentralised and anonymous marketplace. For a relatively low cost, almost anyone can purchase the tools and expertise needed to carry out a breach.

With high rewards and limited risk in many jurisdictions, financially motivated cybercrime remains one of the most significant threats facing organisations today.

Ideological or Political Motivation (Hacktivism)

Not all cybercriminals are driven by profit. Some are motivated by political beliefs, social causes or ideologies. These individuals or groups, often referred to as hacktivists, use hacking as a form of protest, aiming to disrupt, expose or embarrass organisations and governments they oppose.

One of the most recognisable hacktivist collectives is Anonymous, a loosely organised group known for its cyber campaigns against governments, corporations and extremist groups. Their activities have ranged from distributed denial of service (DDoS) attacks on financial institutions, to leaking sensitive documents from law enforcement agencies and political bodies.

Hacktivism has also played a prominent role in modern conflicts. In the early days of the Russia–Ukraine war, groups on both sides of the conflict engaged in cyber operations. Ukrainian-aligned actors, including the so-called IT Army of Ukraine, targeted Russian government websites and media outlets with defacements and DDoS attacks. Meanwhile, pro-Russian hacktivist groups like Killnet have launched attacks against European infrastructure in retaliation for political support of Ukraine.

These operations are not always highly technical, but they can be disruptive and attention-grabbing. For example, in 2022, Killnet claimed responsibility for attacks on several websites belonging to airports, healthcare providers and public institutions across Europe, using basic but effective DDoS techniques.

Hacktivism can blur the line between political protest and criminal activity. While some view it as a legitimate form of dissent in the digital age, it often involves illegal access, data leaks or service disruption, and can escalate geopolitical tensions or cause collateral damage to innocent third parties.

For defenders, politically motivated attacks pose a unique challenge. They may not follow the typical patterns of financially driven crime, and their targets can shift quickly based on current events, perceived injustices or ideological trends.

State-Sponsored Espionage

Some of the most advanced and persistent cyber threats come not from criminals seeking profit, but from nation-states pursuing strategic objectives. These attacks are often aimed at gathering intelligence, disrupting rivals, or gaining long-term access to critical systems. Unlike financially motivated actors, state-sponsored groups tend to operate with significant resources, patience and stealth.

These threat actors – often referred to as Advanced Persistent Threats (APTs) – typically target government departments, defence contractors, critical national infrastructure, and major corporations. Their goal may be to steal sensitive data, conduct surveillance, interfere with democratic processes, or enable future sabotage.

A prominent example is APT29, also known as Cozy Bear, a group linked to Russia’s Foreign Intelligence Service (SVR). They have been implicated in numerous high-profile intrusions, including the 2020 SolarWinds supply chain attack, which compromised several US federal agencies and global private sector organisations. The operation was notable for its sophistication and subtlety, remaining undetected for months.

Similarly, APT10, associated with China’s Ministry of State Security, was involved in an extensive global cyber espionage campaign targeting managed service providers (MSPs). By compromising these third-party IT providers, APT10 was able to access a wide range of downstream client networks, including government and corporate systems in the UK, US and beyond.

Unlike typical cybercriminals, these groups are often protected by their host governments and operate with impunity. They may also work in parallel with criminal organisations, blurring the lines between state and non-state activity. For example, some ransomware attacks have been linked to actors with suspected ties to nation-states, suggesting a dual-purpose intent: generating revenue while causing strategic disruption.

The motivations behind state-sponsored cyber operations are diverse, ranging from political influence and military advantage to intellectual property theft and economic gain. These campaigns are rarely random; they are calculated, well-resourced and long-term in nature.

For organisations, this means traditional defences may not be enough. Combating espionage-level threats requires a heightened focus on detection, incident response and threat intelligence, particularly for those in sensitive sectors.

Corporate or Industrial Espionage

Businesses, particularly those with valuable intellectual property and trade secrets, are prime targets for corporate or industrial espionage. Cybercriminals and competing organisations alike seek to gain an unfair advantage by stealing sensitive data related to research and development (R&D), product designs, strategic plans or proprietary technologies.

This type of espionage often overlaps with state-sponsored cyber operations, where nation-states target foreign companies to bolster their own industries or military capabilities. A notable example is the Operation Aurora campaign, uncovered in 2010, where threat actors believed to be linked to China targeted Google and dozens of other major companies. The attackers aimed to steal intellectual property and gain access to corporate networks.

Similarly, in 2021, the US Department of Justice indicted members of a Chinese hacking group known as APT41 for conducting widespread cyber intrusions into video game companies and technology firms, stealing source code and proprietary information to benefit commercial interests.

R&D-heavy sectors such as biotechnology, aerospace, automotive and software development face particularly high risks. The theft of trade secrets not only undermines a company’s competitive edge but can also result in substantial financial losses and damage to reputation.

Unlike typical financially motivated attacks, corporate espionage campaigns are usually stealthy and meticulously planned. Attackers may maintain prolonged access to compromised networks, gathering intelligence over months or even years to extract maximum value.

Organisations must therefore prioritise safeguarding their intellectual property through robust cybersecurity measures, employee awareness, and stringent access controls. Collaboration with industry partners and government agencies can also help in detecting and mitigating these sophisticated threats.

Personal Challenge or Prestige

For some hackers, the motivation is less about money or politics and more about curiosity, thrill-seeking, or the desire for recognition within their communities. These individuals often see hacking as a puzzle to be solved or a challenge to be conquered, gaining personal satisfaction and prestige among peers.

This motivation is particularly common among younger or amateur hackers, sometimes referred to as “script kiddies”, who may lack advanced skills but are eager to prove themselves by exploiting vulnerabilities or defacing websites. The hacking community online – including forums, social media groups and dark web marketplaces – can foster this behaviour, offering a platform for sharing exploits, bragging rights and reputation-building.

A notable example is the hacktivist group LulzSec, which gained international attention in 2011 through a series of high-profile attacks targeting organisations like Sony, the CIA, and PBS. Their actions were largely driven by the desire to embarrass their victims and entertain themselves, rather than for financial gain or political objectives.

Similarly, the case of Jonathan James, a teenage hacker from the United States, illustrates this motivation. At just 15 years old, James infiltrated several government systems, including NASA, stealing source code and causing significant disruption. His actions seemed motivated by the challenge and thrill of hacking rather than monetary rewards.

While these hackers might not always intend serious harm, their actions can have unintended consequences: disrupting services, compromising data, or exposing vulnerabilities that other malicious actors might exploit.

Revenge or Personal Grievances

Not all cyber threats originate externally – sometimes the greatest risks come from insiders motivated by personal grudges or feelings of revenge. Disgruntled employees, former staff or contractors with authorised access can deliberately cause harm to an organisation by leaking sensitive information, sabotaging systems or stealing data.

One of the most infamous cases involved Edward Snowden, a former NSA contractor who leaked vast amounts of classified information, motivated by a personal belief that the public had the right to know about government surveillance programmes. Though his actions sparked worldwide debate on privacy, they also caused significant damage to intelligence operations.

In the corporate sphere, a UK-based case saw a former IT administrator take revenge after being dismissed by deleting critical files and disabling user accounts, resulting in days of downtime and financial loss.

Such incidents highlight the critical importance of internal controls, thorough monitoring and robust offboarding procedures. Regularly reviewing access rights, implementing the principle of least privilege, and monitoring unusual activity can help detect and prevent insider threats before they escalate.

Organisations must balance trust with vigilance, fostering a positive workplace culture while ensuring employees understand the consequences of malicious actions.

Opportunistic or Accidental Hacking

Not all cyberattacks are the result of carefully planned operations. Many stem from opportunistic or accidental hacking, where attackers use automated tools to scan large numbers of systems for common vulnerabilities. These attacks require minimal effort but can still cause significant damage, especially to organisations or individuals with poor basic cyber hygiene.

Automated bots and scripts regularly probe the internet for unpatched software, weak passwords, misconfigured devices, or open ports. Once a vulnerability is found, the attacker may exploit it to gain access, often without a specific target in mind. This “spray and pray” approach relies on volume rather than precision.

For example, the WannaCry ransomware outbreak in 2017 rapidly spread across the globe by exploiting a known Windows vulnerability. Many affected organisations had failed to apply critical patches, making them vulnerable to this widespread, indiscriminate attack.

These types of attacks highlight the importance of fundamental cybersecurity practices: regularly updating software, using strong, unique passwords, enabling multi-factor authentication, and maintaining good network hygiene. Even basic measures can significantly reduce the risk posed by opportunistic attackers.

While opportunistic hacking might lack the sophistication or motive of targeted attacks, its impact can be equally devastating if proper precautions are not taken.

Mixed Motivations

In reality, cybercriminal motivations are often complex and overlapping rather than clear-cut. Many attacks are driven by a combination of factors – financial, political, ideological, or personal – which can make attribution and defence especially challenging.

A common scenario involves financially motivated cybercriminal groups being hired or tolerated by state actors to carry out attacks that serve national interests. These groups operate with relative impunity in exchange for providing offensive cyber capabilities or disruptive services.

For example, the notorious ransomware group REvil (also known as Sodinokibi) has been linked to criminal operations that sometimes intersect with geopolitical objectives. While primarily motivated by profit through ransomware extortion, there are indications that some affiliates have conducted operations aligning with certain state interests or received indirect protection from their home governments.

Such hybrid motivations complicate the threat landscape, blurring the lines between organised crime and state-sponsored espionage or sabotage. For defenders, understanding these intertwined incentives is crucial for developing effective cyber defence strategies and threat intelligence.

Conclusion

Cybercriminals are motivated by a wide and varied range of factors – from financial gain and political agendas to personal grudges and the pursuit of prestige. Understanding these diverse motivations is essential for organisations seeking to build effective defences in an increasingly complex cyber threat landscape.

By recognising what drives threat actors, businesses and individuals can better anticipate potential attack vectors, prioritise security investments, and tailor their incident response strategies accordingly. A threat-informed defence approach goes beyond technical measures, incorporating intelligence, awareness and proactive risk management.

As cyber threats continue to evolve, adopting a comprehensive, informed security posture is no longer optional – it is vital. Organisations should take active steps to understand their adversaries, strengthen their defences, and cultivate a culture of vigilance to stay ahead in the ongoing battle against cybercrime.

Header Photo by Furkan Elveren on Unsplash

"SOS
CVE Top 10

The SOS Intelligence CVE Chatter Weekly Top Ten – 07 July 2025


This weekly blog post is from via our unique intelligence collection pipelines. We are your eyes and ears online, including the Dark Web.

There are thousands of vulnerability discussions each week. SOS Intelligence gathers a list of the most discussed Common Vulnerabilities and Exposures (CVE) online for the previous week.

We make every effort to ensure the accuracy of the data presented. As this is an automated process some errors may creep in.

If you are feeling generous please do make us aware of anything you spot, feel free to follow us on Twitter @sosintel and DM us. Thank you!


1.  CVE-2025-5839

A vulnerability, which was classified as critical, has been found in Tenda AC9 15.03.02.13. Affected by this issue is the function fromadvsetlanip of the file /goform/AdvSetLanip of the component POST Request Handler. The manipulation of the argument lanMask leads to buffer overflow. The attack may be launched remotely. The exploit has been disclosed to the public and may be used.

https://nvd.nist.gov/vuln/detail/CVE-2025-5839


2. CVE-2025-6554

Type confusion in V8 in Google Chrome prior to 138.0.7204.96 allowed a remote attacker to perform arbitrary read/write via a crafted HTML page. (Chromium security severity: High)

https://nvd.nist.gov/vuln/detail/CVE-2025-6554


3. CVE-2025-32463

Sudo before 1.9.17p1 allows local users to obtain root access because /etc/nsswitch.conf from a user-controlled directory is used with the –chroot option.

https://nvd.nist.gov/vuln/detail/CVE-2025-32463


4. CVE-2025-32462

Sudo before 1.9.17p1, when used with a sudoers file that specifies a host that is neither the current host nor ALL, allows listed users to execute commands on unintended machines.

https://nvd.nist.gov/vuln/detail/CVE-2025-32462


5. CVE-2023-26075

An issue was discovered in Samsung Mobile Chipset and Baseband Modem Chipset for Exynos 850, Exynos 980, Exynos 1080, Exynos 1280, Exynos 2200, Exynos Modem 5123, Exynos Modem 5300, and Exynos Auto T5123. An intra-object overflow in the 5G MM message codec can occur due to insufficient parameter validation when decoding the Service Area List.

https://nvd.nist.gov/vuln/detail/CVE-2023-26075


6. CVE-2017-5638

The Jakarta Multipart parser in Apache Struts 2 2.3.x before 2.3.32 and 2.5.x before 2.5.10.1 has incorrect exception handling and error-message generation during file-upload attempts, which allows remote attackers to execute arbitrary commands via a crafted Content-Type, Content-Disposition, or Content-Length HTTP header, as exploited in the wild in March 2017 with a Content-Type header containing a #cmd= string.

https://nvd.nist.gov/vuln/detail/CVE-2017-5638


7. CVE-2025-43200

This issue was addressed with improved checks. This issue is fixed in watchOS 11.3.1, macOS Ventura 13.7.4, iOS 15.8.4 and iPadOS 15.8.4, iOS 16.7.11 and iPadOS 16.7.11, iPadOS 17.7.5, visionOS 2.3.1, macOS Sequoia 15.3.1, iOS 18.3.1 and iPadOS 18.3.1, macOS Sonoma 14.7.4. A logic issue existed when processing a maliciously crafted photo or video shared via an iCloud Link. Apple is aware of a report that this issue may have been exploited in an extremely sophisticated attack against specific targeted individuals.

https://nvd.nist.gov/vuln/detail/CVE-2025-43200


8. CVE-2024-38063

Windows TCP/IP Remote Code Execution Vulnerability

https://nvd.nist.gov/vuln/detail/CVE-2024-38063


9. CVE-2023-26074

An issue was discovered in Samsung Mobile Chipset and Baseband Modem Chipset for Exynos 850, Exynos 980, Exynos 1080, Exynos 1280, Exynos 2200, Exynos Modem 5123, Exynos Modem 5300, and Exynos Auto T5123.. A heap-based buffer overflow in the 5G MM message codec can occur due to insufficient parameter validation when decoding operator-defined access category definitions.

https://nvd.nist.gov/vuln/detail/CVE-2023-26074


10. CVE-2024-4990

In yiisoft/yii2 version 2.0.48, the base Component class contains a vulnerability where the `__set()` magic method does not validate that the value passed is a valid Behavior class name or configuration. This allows an attacker to instantiate arbitrary classes, passing parameters to their constructors and invoking setter methods. Depending on the installed dependencies, various types of attacks are possible, including the execution of arbitrary code, retrieval of sensitive information, and unauthorized access.

https://nvd.nist.gov/vuln/detail/CVE-2024-4990


"SOS
CVE Top 10

The SOS Intelligence CVE Chatter Weekly Top Ten – 30 June 2025


This weekly blog post is from via our unique intelligence collection pipelines. We are your eyes and ears online, including the Dark Web.

There are thousands of vulnerability discussions each week. SOS Intelligence gathers a list of the most discussed Common Vulnerabilities and Exposures (CVE) online for the previous week.

We make every effort to ensure the accuracy of the data presented. As this is an automated process some errors may creep in.

If you are feeling generous please do make us aware of anything you spot, feel free to follow us on Twitter @sosintel and DM us. Thank you!


1.  CVE-2024-4990

In yiisoft/yii2 version 2.0.48, the base Component class contains a vulnerability where the `__set()` magic method does not validate that the value passed is a valid Behavior class name or configuration. This allows an attacker to instantiate arbitrary classes, passing parameters to their constructors and invoking setter methods. Depending on the installed dependencies, various types of attacks are possible, including the execution of arbitrary code, retrieval of sensitive information, and unauthorized access.

https://nvd.nist.gov/vuln/detail/CVE-2024-4990


2. CVE-2024-58136

Yii 2 before 2.0.52 mishandles the attaching of behavior that is defined by an __class array key, a CVE-2024-4990 regression, as exploited in the wild in February through April 2025.

https://nvd.nist.gov/vuln/detail/CVE-2024-58136


3. CVE-2025-5839

A vulnerability, which was classified as critical, has been found in Tenda AC9 15.03.02.13. Affected by this issue is the function fromadvsetlanip of the file /goform/AdvSetLanip of the component POST Request Handler. The manipulation of the argument lanMask leads to buffer overflow. The attack may be launched remotely. The exploit has been disclosed to the public and may be used.

https://nvd.nist.gov/vuln/detail/CVE-2025-5839


4. CVE-2018-6981

VMware ESXi 6.7 without ESXi670-201811401-BG and VMware ESXi 6.5 without ESXi650-201811301-BG, VMware ESXi 6.0 without ESXi600-201811401-BG, VMware Workstation 15, VMware Workstation 14.1.3 or below, VMware Fusion 11, VMware Fusion 10.1.3 or below contain uninitialized stack memory usage in the vmxnet3 virtual network adapter which may allow a guest to execute code on the host.

https://nvd.nist.gov/vuln/detail/CVE-2018-6981


5. CVE-2025-32432

Craft is a flexible, user-friendly CMS for creating custom digital experiences on the web and beyond. Starting from version 3.0.0-RC1 to before 3.9.15, 4.0.0-RC1 to before 4.14.15, and 5.0.0-RC1 to before 5.6.17, Craft is vulnerable to remote code execution. This is a high-impact, low-complexity attack vector. This issue has been patched in versions 3.9.15, 4.14.15, and 5.6.17, and is an additional fix for CVE-2023-41892.

https://nvd.nist.gov/vuln/detail/CVE-2025-32432


6. CVE-2025-33053

External control of file name or path in Internet Shortcut Files allows an unauthorized attacker to execute code over a network.

https://nvd.nist.gov/vuln/detail/CVE-2025-33053


7. CVE-2024-21762

A out-of-bounds write in Fortinet FortiOS versions 7.4.0 through 7.4.2, 7.2.0 through 7.2.6, 7.0.0 through 7.0.13, 6.4.0 through 6.4.14, 6.2.0 through 6.2.15, 6.0.0 through 6.0.17, FortiProxy versions 7.4.0 through 7.4.2, 7.2.0 through 7.2.8, 7.0.0 through 7.0.14, 2.0.0 through 2.0.13, 1.2.0 through 1.2.13, 1.1.0 through 1.1.6, 1.0.0 through 1.0.7 allows attacker to execute unauthorized code or commands via specifically crafted requests

https://nvd.nist.gov/vuln/detail/CVE-2024-21762


8. CVE-2025-49144

Notepad++ is a free and open-source source code editor. In versions 8.8.1 and prior, a privilege escalation vulnerability exists in the Notepad++ v8.8.1 installer that allows unprivileged users to gain SYSTEM-level privileges through insecure executable search paths. An attacker could use social engineering or clickjacking to trick users into downloading both the legitimate installer and a malicious executable to the same directory (typically Downloads folder – which is known as Vulnerable directory). Upon running the installer, the attack executes automatically with SYSTEM privileges. This issue has been fixed and will be released in version 8.8.2.

https://nvd.nist.gov/vuln/detail/CVE-2025-49144


9. CVE-2024-20720

Adobe Commerce versions 2.4.6-p3, 2.4.5-p5, 2.4.4-p6 and earlier are affected by an Improper Neutralization of Special Elements used in an OS Command (‘OS Command Injection’) vulnerability that could lead in arbitrary code execution by an attacker. Exploitation of this issue does not require user interaction.

https://nvd.nist.gov/vuln/detail/CVE-2024-20720


10. CVE-2024-38476

Vulnerability in core of Apache HTTP Server 2.4.59 and earlier are vulnerably to information disclosure, SSRF or local script execution via backend applications whose response headers are malicious or exploitable.

Users are recommended to upgrade to version 2.4.60, which fixes this issue.

https://nvd.nist.gov/vuln/detail/CVE-2024-38476


1 2 … 5 6 7 8 9 … 33 34
New: Attack Surface Management · Dark web intelligence. Now with the bigger picture. | Explore SOS Intelligence ASM →
Privacy Settings
We use cookies to enhance your experience while using our website. If you are using our Services via a browser you can restrict, block or remove cookies through your web browser settings. We also use content and scripts from third parties that may use tracking technologies. You can selectively provide your consent below to allow such third party embeds. For complete information about the cookies we use, data we collect and how we process them, please check our Privacy Policy
Youtube
Consent to display content from - Youtube
Vimeo
Consent to display content from - Vimeo
Google Maps
Consent to display content from - Google
Spotify
Consent to display content from - Spotify
Sound Cloud
Consent to display content from - Sound