Customer portal
Category

Investigation

"Stealer
Investigation, The Dark Web

Stealer Logs: Understanding the Underground’s Most Dangerous Data Source

Introduction

Stealer logs represent the most dangerous commoditised threat to corporate security today. Unlike traditional data breaches that target specific organisations, infostealers cast a wide net across millions of users and machines, capturing everything from browser credentials to session tokens to cryptocurrency wallets in a single automated sweep.

So why are stealer logs such a critical concern right now? Because they are the common precursor to account takeover, ransomware deployment, and initial access brokerage. If your users’ credentials are in a stealer log marketplace, you do not have an identity problem; you have a breach waiting to happen.

This report examines what stealer logs are, how they are distributed and monetised, what data they contain, and how organisations can detect and defend against them. The scale is staggering: in the first half of 2025 alone, over 180,000 stealer logs were offered for sale on underground marketplaces. RedLine accounts for 44% of all logs collected. Vidar stole 65 million passwords in just six months.

If your domain appears in a stealer log, you are no longer operating under the assumption of credential compromise; you are operating under the certainty of it. The only question is whether the threat actor has already acted on that access.

How Infostealers Work

The Malware Itself

An infostealer is malware designed with a single purpose: to extract sensitive data from an infected machine and exfiltrate it to an attacker-controlled server. It runs silently, often with minimal resource consumption, which is why users and security teams can miss it for weeks or months.

So what data do they target? Browser autofill data, stored passwords, session cookies, saved payment card details, cryptocurrency wallet seed phrases and private keys, email account credentials, browser extensions, browsing history, installed software inventory, system information, and USB device history. The malware is indiscriminate; it grabs everything that might have value.

The sophistication varies. Basic infostealers are crude tools designed to grab whatever they can reach. Advanced infostealers include anti-analysis features, anti-virtualisation checks, geofencing to avoid high-risk jurisdictions, and code obfuscation to bypass signature-based detection.

Major Infostealer Families

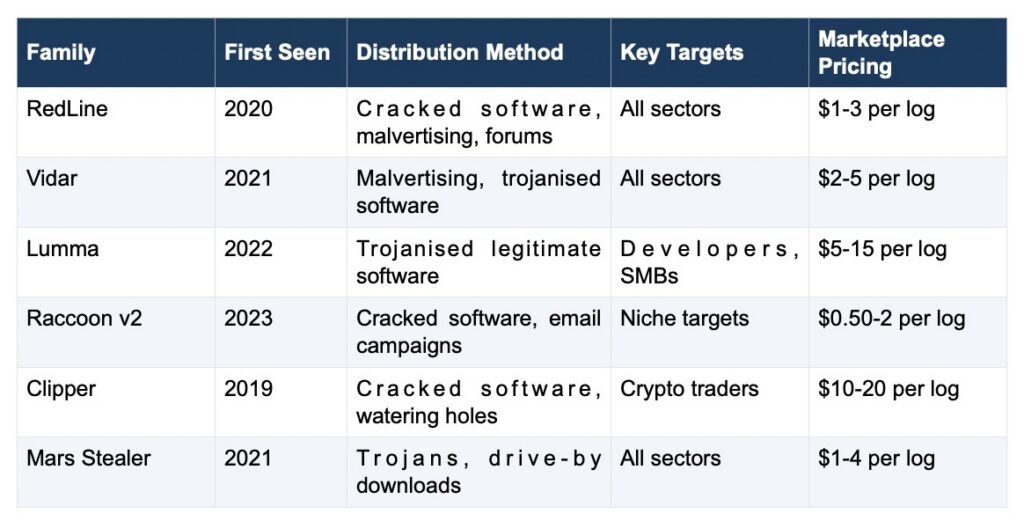
RedLine is the dominant family by volume. First observed in 2020, RedLine has evolved into a modular stealer with customisable features, support for multiple languages and operating systems, and active development. It accounts for 44% of all stealer logs captured by intelligence vendors. RedLine spreads primarily through cracked software, malicious advertising networks, and watering hole attacks targeting development forums.

Raccoon was one of the earliest widespread infostealers and became infamous for its ease of use and low barrier to entry. Variant developers could build custom builds for under $100. Although law enforcement operations disrupted Raccoon’s primary infrastructure in 2023 (following the October 2022 arrest of developer Mark Sokolovsky), variants continue to circulate. Raccoon logs are heavily discounted on marketplaces because the payloads are dated and signatures are well-known.

Vidar is one of the most aggressive and feature-rich infostealers in circulation. It records keystrokes, captures screenshots, exfiltrates browser data, and includes anti-reverse-engineering protections. Vidar was responsible for stealing 65 million passwords in a documented six-month period from 2024 to 2025. It spreads through malvertising, cracked software, and compromised download mirrors.

Lumma emerged in 2022 and gained traction rapidly because of its effective distribution mechanism and low detection rates. Lumma’s primary distribution vector is Trojanised legitimate software (video converters, games, file managers) distributed through third-party sites. Lumma logs are actively traded on underground markets at premium prices because they tend to contain fresh, high-value data.
The Malware-as-a-Service Model

Most modern infostealers operate as a service, not a discrete product. Operators host the command and control infrastructure, provide a web panel for customers to manage infections and download logs, and take a percentage of the revenue when logs are resold.

The client (a threat actor, distributor, or criminal organisation) uses the service to build custom malware variants, deploy them through their chosen vectors, and collect the resulting logs. The service operator handles the backend; the client handles distribution and monetisation.

This model democratises malware development. You do not need to be a skilled reverse engineer or malware author; you just need access to a distribution channel and a payment method. Prices for malware-as-a-service access range from $40 per month for basic builds to $500 per month for fully customised, high-stealth variants with obfuscation and anti-analysis features.

The Stealer Log Supply Chain: From Infection to Marketplace

Step One: Distribution

The first stage of the supply chain is getting the malware onto the target machine. Distribution methods include cracked software (the single largest vector), malicious advertisements and browser redirects, compromised legitimate software mirrors, phishing emails with trojanised attachments, and watering hole attacks targeting developers and specific industries.

Cracked software remains the dominant distribution method because the economics are simple: users want free versions of expensive software, threat actors provide infected versions, and the malware runs with the privileges of the software installation. Commonly trojanised products include AutoCAD, Microsoft Office, Photoshop, Ableton Live, JetBrains IDEs, and antivirus software itself. Underground marketplaces such as zqi3evypxq7ok3gqnimwnlesf6v76ksrpgtgb6j7hh6ye752apzmceyd[.]onion advertise cracking tools and hacking guides alongside stealer logs.

Step Two: Execution and Exfiltration

Once executed, the infostealer begins its automated collection routine. It enumerates installed browsers, reads credential storage databases, decrypts stored passwords using the operating system’s credential storage APIs, extracts browser cookies (which often contain active session tokens for web services), and collects any data it has permissions to access.

So what happens to this data once collected? The malware packages it into an archive (typically JSON or CSV format), compresses it, and sends it back to the attacker’s command and control server. This happens in seconds to minutes, often without any user-visible activity. Encryption in transit is variable; some stealers use HTTPS, others use simple obfuscation.

Step Three: Log Curation and Testing

The logs arrive at the attacker’s server in raw form. Experienced threat actors filter and verify logs before offering them for sale. They test login credentials against target services to confirm validity, check whether emails are associated with high-value targets (executives, technical staff, security personnel), and flag logs that contain cryptocurrency wallet data or payment card information for premium pricing.

A high-quality stealer log contains verified working credentials, a mix of personal and corporate accounts, cryptocurrency wallet information, and identifiable metadata such as system username and company name extracted from the system registry. Low-quality logs are unverified, old (more than a week old), or contain duplicates.

Step Four: Marketplace and Distribution

Verified logs are uploaded to underground marketplaces. The three most significant distribution channels are the Russian Market (a Telegram-native marketplace with automated purchasing and delivery), Genesis Market (a long-standing marketplace specialising in session cookies and browser profile data, subject to FBI takedown in April 2023 as part of Operation Cookie Monster), and ad hoc Telegram channels run by individual threat actors or resellers.

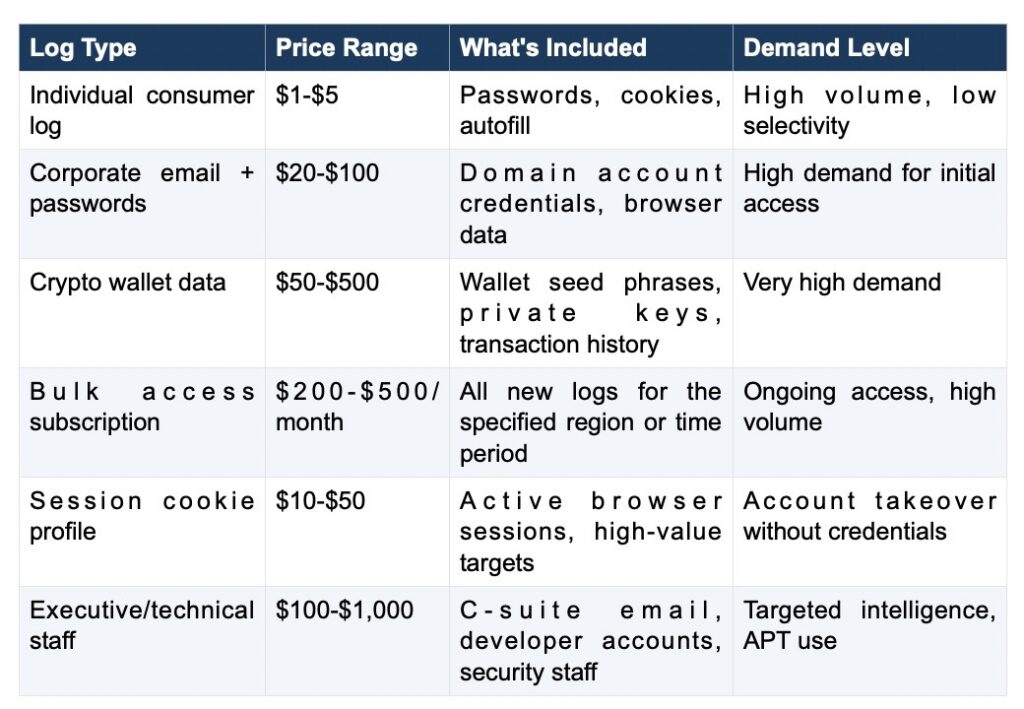
Pricing follows a predictable pattern: individual consumer logs $1 to $5, logs containing cryptocurrency or payment card data $10 to $50, corporate or email logs $20 to $100, and bulk access to large log repositories $1,000 to $5,000, depending on scope and recency. Some marketplaces offer subscription models where buyers pay $200 to $500 per month for unlimited access to new logs.

Step Five: Exploitation

Once purchased, the logs are used for account takeover (directly accessing email, SaaS applications, or banking portals), credential stuffing attacks against non-customers, password spray attacks across corporate networks, identification of high-value targets for targeted phishing or social engineering, and sales to other threat actors, ransomware gangs, or initial access brokers.

The timeline from infection to exploitation can be remarkably short. Logs may be available for purchase within 24 to 72 hours of infection. Active threat actors monitor marketplaces continuously, purchasing logs for targets relevant to their operations immediately after they appear for sale.

What’s Inside a Stealer Log

A typical stealer log is a structured data archive containing the following categories of information.
Browser Credentials

Passwords are stored in Chrome, Firefox, Edge, Opera, and other Chromium-based browsers. These are extracted using the browser’s own decryption APIs and are usually in plaintext in the log. If your users are reusing passwords across multiple services (which most do), a single compromised password gives access to email, SaaS applications, banking portals, and corporate networks.

Session Cookies and Browser Data

Session cookies are particularly valuable because they often grant access to authenticated services without requiring the user to log in again. A stolen cookie for a user’s email account, for example, allows an attacker to reset the password for every service that user has signed up for. Logs also contain browser autofill data, saved addresses, phone numbers, and credit card information.

Cryptocurrency Wallet Data

If the infected machine has a cryptocurrency wallet installed (MetaMask, Trust Wallet, Ledger, Trezor drivers), the infostealer attempts to extract wallet seed phrases, private keys, and transaction history. A stolen seed phrase gives the attacker full control of any cryptocurrency stored in that wallet. Logs containing wallet data command a significant price premium, with cryptocurrency-focused marketplaces like tamazoncmlw2ohkbsmqxnotudejdd4befrasxuigzzjumqu3zba535yd[.]onion advertising cloned cards and financial fraud tools alongside wallet data.

System and User Information

The log includes the machine’s hostname, registered Windows username, installed software inventory, list of network interfaces and IP addresses, list of USB devices ever connected, system serial number, and BIOS information. This metadata helps threat actors profile the target (e.g. is this a developer machine, does it have security software installed) and tailor exploitation.

Email and Application Data

If Outlook, Thunderbird, or other email clients are installed, logs may contain saved email credentials and cached email headers. Application-specific data is also captured, including saved credentials in password managers (if they are not properly locked), FTP clients, SSH keys, browser extensions, and stored API credentials in development tools.

Indicator Format

Logs are typically structured as JSON or CSV files within a ZIP archive. A single log might be 5 to 200 megabytes, depending on the system’s history and installed software. Large batch log collections can reach gigabytes and are broken into smaller chunks for distribution.

Key Statistics: The Scale of the Threat

RedLine accounts for 44% of all stealer logs analysed by intelligence platforms. This concentration means that if you are looking for signs of compromise via stealer logs, you are primarily tracking RedLine activity. However, that also means a significant proportion of logs come from other families like Vidar, Lumma, and Raccoon variants.

Vidar stole 65 million unique passwords in a documented six-month period from October 2024 to March 2025. This single family, operating from a single set of infrastructure, compromised a staggering volume of user accounts across consumer and corporate domains.

Over 180,000 stealer logs were offered for sale on identified underground marketplaces in the first half of 2025. This is an average of 30,000 logs per month, or roughly 1,000 logs per day.

More than 50% of ransomware victims had their domains listed in stealer logs before the ransomware deployment. This indicates that initial compromise via stealer log access is a primary precursor to ransomware attacks. Threat actors purchase logs to establish initial access, conduct reconnaissance, and stage the ransomware payload.

Major Infostealer Families
Stealer Log Pricing by Type
Impact Statistics

The Marketplace Ecosystem

Russian Market (Telegram Native)

Russian Market operates exclusively within Telegram and is the largest active stealer log marketplace as of 2025. The platform uses automated bots that handle purchasing, payment, and log delivery. Buyers simply send a payment in cryptocurrency and receive a direct link to download the log within minutes.

Russian Market does not charge a commission on individual sales; revenue comes from premium marketplace memberships, advertising, and selective enforcement of seller verification. The platform lists 50,000 to 100,000 logs at any given time, with new inventory added continuously.

Genesis Market

Genesis Market is a longer-established marketplace that specialises in session cookies, browser profiles, and authenticated user sessions rather than raw passwords. It operates a traditional web interface (accessed via Tor) and enforces strict verification of sellers. Genesis Market was subject to a major FBI takedown operation in April 2023.

Genesis Market takes a 10 to 15% commission on each sale. Logs on Genesis command higher prices than equivalent logs on the Russian Market because the payload (authenticated sessions) is more directly useful for account takeover without password changes. The marketplace has hosted millions of stolen sessions.

Telegram Channels and Resellers

Smaller threat actors and resellers operate ad hoc Telegram channels, often promoting newly harvested logs from specific geographic regions or specific malware families. These channels operate with less formal infrastructure and offer discounts for bulk purchases. Forums like bfdxjkv5e2z3ilrifzbnvxxvhbzsj67akjpj3zc6smzr4vv6oz565gyd[.]onion host escrow services and enable peer-to-peer trading of stolen logs.

Prices on Telegram are often lower than those on centralised marketplaces because resellers are trying to move inventory quickly and avoid law enforcement attention. However, logs are also less verified and may contain duplicates or stale data.

Regional Variations

Pricing and availability vary significantly by geography. Logs from developed economies (USA, UK, Germany, Japan) command premium prices. Logs from developing economies are discounted. Logs are also segmented by corporate association; logs from email addresses on Fortune 500 domain whitelists are marked as such and priced accordingly.

Corporate Risk: How Stealer Logs Enable Attacks

Account Takeover

The most direct exploitation path is account takeover. An attacker purchases a log containing the email address and password of a corporate employee. They attempt to log into the employee’s email account. If multi-factor authentication is not enabled (and many users do not enable it outside of work contexts), login succeeds.

From the email, the attacker resets passwords for every service the employee has linked to that email account. This includes SaaS applications, cloud storage, password managers, and often the employee’s corporate VPN or SSO portal if they have reused the same password across services.

Initial Access Brokerage

Ransomware gangs and APT operators do not have time to run large-scale malware campaigns. Instead, they purchase access from initial access brokers. An initial access broker uses stealer logs to identify high-value targets (corporate email addresses, domain admin accounts, people working for specific industries), purchases logs for those individuals, and then sells the access to ransomware operators or nation states.

A single log containing credentials for a domain admin or security operations centre staff member can sell for $5,000 to $50,000 to a ransomware operator, because that access drastically shortcuts the reconnaissance and lateral movement phases of a ransomware campaign.

Reconnaissance and Lateral Movement

Even if the initial compromised account is a low-privilege user, logs contain system information, installed software, network configuration, and connected USB devices. This metadata gives threat actors a profile of the corporate environment before they even gain access. They know which security software is in use, which development frameworks are deployed, and which network devices are present.

Once inside, the attacker uses the compromised account to access email (containing sensitive business information, network topology diagrams, and access credentials in forwarded messages), network drives, and internal tools. This leads to lateral movement to higher-privileged accounts and eventually to domain admin compromise.

Credential Stuffing and Password Spray

An attacker with a database of 1,000 stolen passwords can conduct password spray attacks against your corporate email system or Active Directory, trying the same password across all known email addresses in your organisation. The attack succeeds if employees have reused credentials or used predictable variations.

This is a silent attack that happens outside of your firewall and VPN, so your network monitoring tools do not detect it. The first sign may be unexpected password reset emails or successful logins from impossible locations.

Supply Chain Compromise

If your organisation relies on third-party software vendors or contractors, and those vendors’ employees are in the stealer logs, an attacker can compromise the vendor and use their access to gain indirect access to your systems. This is a far easier attack vector than breaching you directly.

How SOS Intelligence Monitors Stealer Logs

Our breach alert system continuously monitors underground marketplaces, forums, Telegram channels, and data dump collections for stealer logs and other sources of compromised data. We extract indicators of compromise from each log and match them against your organisational domains.

So how does detection work? We parse log contents for email addresses, domain names, usernames, system names, and other identifying information. We match these against your organisation’s known domain list. When we find a hit, we generate an alert with details: which user was compromised, which malware family was responsible (if known), what data was exposed, when the log appeared for sale, and what price it commanded on the marketplace.

We also track trends. We monitor which malware families are producing the most volume, which geographic regions are being targeted, and which industries are disproportionately represented in current stealer logs. This gives you visibility into both specific risks to your organisation and the broader threat landscape.

Our enrichment process adds context. We cross-reference the compromised email addresses with LinkedIn, WHOIS records, and internal threat intelligence to identify whether the compromised user holds a sensitive position (executive, developer, security staff). We flag logs that contain multiple compromised employees from the same organisation as indicators of targeted activity rather than random harvesting.

Defensive Recommendations

Detection and Monitoring

First: subscribe to breach alert services that monitor stealer log marketplaces and dark web collections. The earlier you know that your users are in stealer logs, the faster you can reset compromised credentials and audit for account access.

Second: implement continuous exposure monitoring. Track your organisational domains on dark web forums, marketplaces, pastebins, and leaked database collections. Many of these sources post publicly (just on obscure infrastructure); you do not need access to Telegram to find them.

Incident Response

If you discover that your domain is present in a stealer log, treat it as a credential compromise incident. Reset the password for the compromised user immediately. Force re-authentication on all active sessions (log them out everywhere). Enable multi-factor authentication if not already in use. Audit email forwarding rules, application integrations, and connected devices for signs of access.

Check whether the compromised user holds a sensitive role. If they do, expand your investigation: query your identity provider and email system for impossible logins, password changes, or unusual activity; check cloud storage for data exfiltration; and interview the user about recent phishing attempts or unusual system behaviour.

Credential Hygiene

Enforce strong, unique passwords for all systems, especially email and identity providers. Implement passwordless authentication where possible (FIDO2 hardware keys, Windows Hello). Where passwords are necessary, use a password manager with strong master passwords.

Multi-factor authentication is not optional; it is mandatory. If an attacker has your password (because it is in a stealer log), multi-factor authentication is the only thing that stops account takeover. Prioritise MFA for email and administrative accounts. Do not rely on SMS; use TOTP or hardware keys.

Threat Actor Knowledge

Understand which threat actors are currently targeting your industry. If you operate in critical infrastructure or financial services, you are targeted by state-sponsored actors and organised crime groups, not opportunistic cybercriminals. If you operate in technology or biotech, intellectual property theft is a primary motivation.

Review the malware families affecting your sector. If your users are appearing in Vidar or Lumma logs more frequently than average, your distribution channels may be compromised. If you see your domain in logs associated with a specific ransomware gang, you have a higher probability of imminent encryption activity.

Third-Party Risk

Audit your third-party vendors and contractors for Stealer log exposure. If a critical vendor has employees in breach, consider the implications for your access. Do they reuse passwords, or are their systems segmented? Do they have elevated privileges in your environment?

Implement zero-trust principles for vendor access. Do not assume that a contractor’s machine is clean; segment their access, require multi-factor authentication, and monitor their activity as you would a hostile external party.

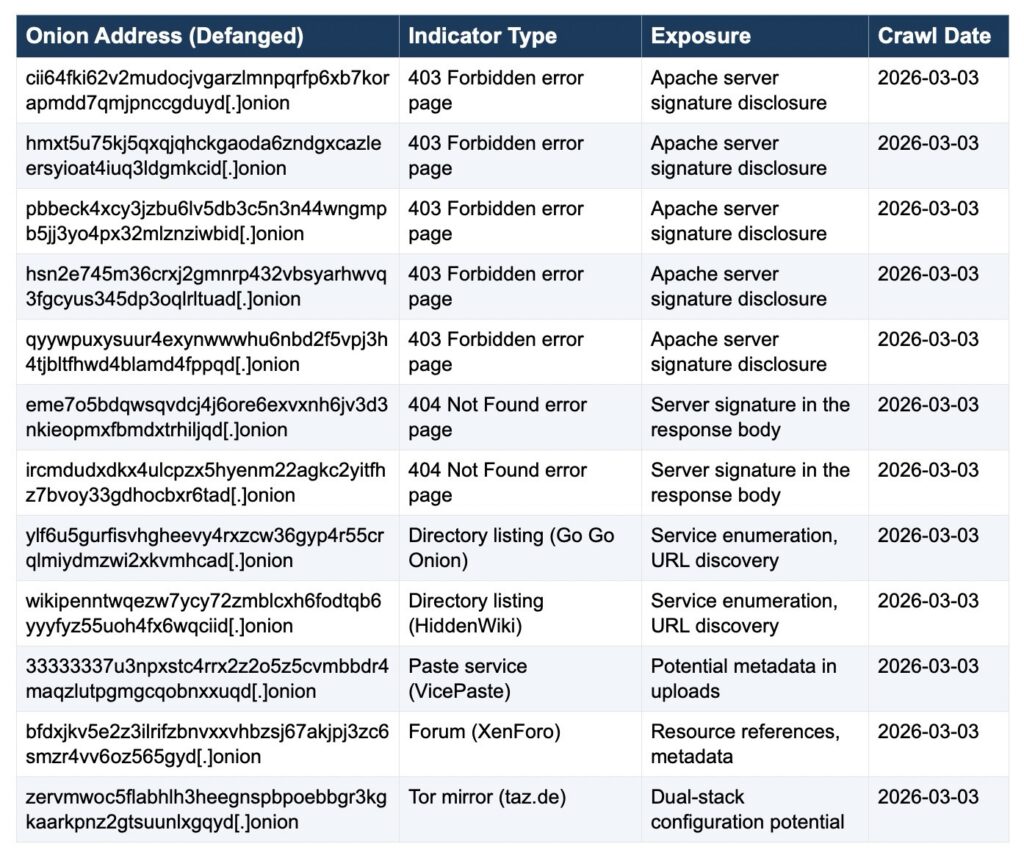
Appendix: DARKSEARCH Observed Indicators

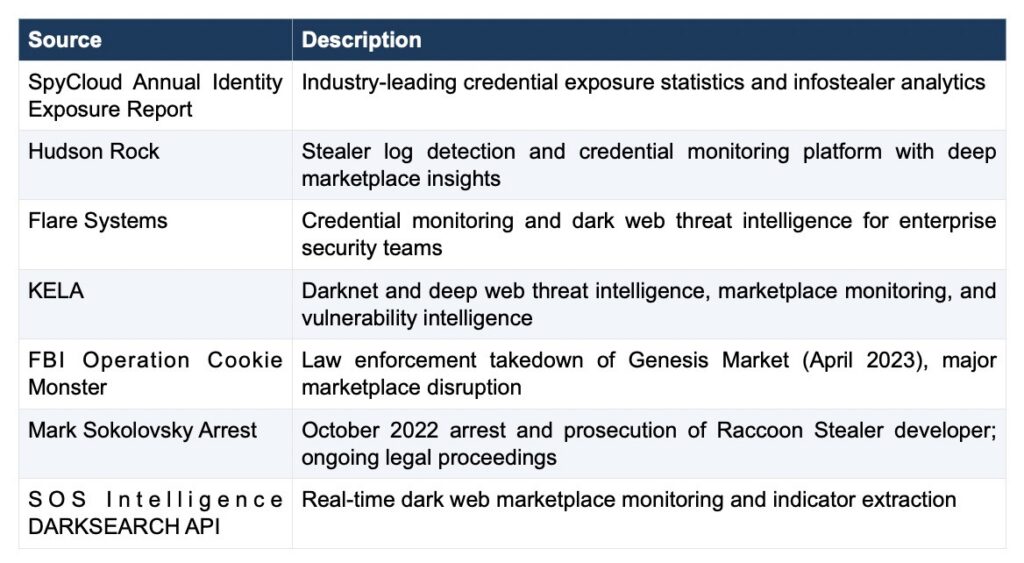
The following table documents confirmed indicators from dark web marketplaces and forums monitored via SOS Intelligence’s DARKSEARCH API. All onion addresses are defanged for security and compliance purposes. These indicators are provided for threat intelligence and detection purposes only.

External References

The analysis in this report draws on publicly available threat intelligence, academic research, and law enforcement activity reports. Key sources include:
Conclusion

Stealer logs are not a future threat; they are a present reality. The scale of harvesting, the sophistication of the malware, and the availability of stolen data on open marketplaces mean that credential compromise is no longer exceptional. It is expected.

Your organisation’s security posture must start with the assumption that your users’ credentials are compromised. That means: strong, unique passwords, multi-factor authentication, continuous monitoring of dark web sources, rapid response to breach alerts, and zero-trust policies for sensitive access.

The defenders who will prevail are those who detect compromise early and respond immediately. Every hour between when a stealer log appears on a marketplace and when you reset the compromised credentials is an hour the attacker can exploit that access.

If you do not have visibility into dark web stealer log marketplaces today, you do not have a complete picture of your organisation’s actual risk. Close that gap now.

Danger photo by Edwin Hooper on Unsplash

Malware photo by Ed Hardie on Unsplash

Browser photo by BoliviaInteligente on Unsplash

No trespassing photo by Joseph Corl on Unsplash
"Lightning
Investigation, Uncategorized

The Victims That Show Up Twice

What’s really behind ransomware’s repeat listings

Spend enough time working through ransomware leak sites, and you start to notice something odd. A company gets named by one group, its stolen files posted, a countdown clock ticking away next to its logo. Then, weeks or sometimes months later, the same company turns up again, this time under a completely different group’s banner.

At first glance, it looks like the worst kind of bad luck: a firm hit twice by two unrelated criminal operations, back to back. We wanted to know how often that’s actually true, and it turns out the honest answer is: not very often, and rarely for the reason you’d assume.

Working through just under 14,000 victim listings scraped from leak sites between July 2024 and June 2026, matched up by company domain and name, we found 213 organisations that had been named by more than one group, out of 12,782 distinct victims in the dataset, roughly one in sixty. Not a huge share, but far from nothing, and once we started checking the reasons behind it, the picture got considerably stranger than “two gangs happened to pick the same target”.

Not everything that looks like a double hit is one

The first thing we had to rule out was our own data getting confused. Some apparent overlap is just noise: a leak site occasionally records a file-hosting link or a LinkedIn profile in the space where a company’s domain should go, and several unrelated victims end up sharing that same non-domain value purely by coincidence. Strip that out, and what’s left starts to look like genuine repeat appearances. Even then, a good chunk of them aren’t quite what they seem.

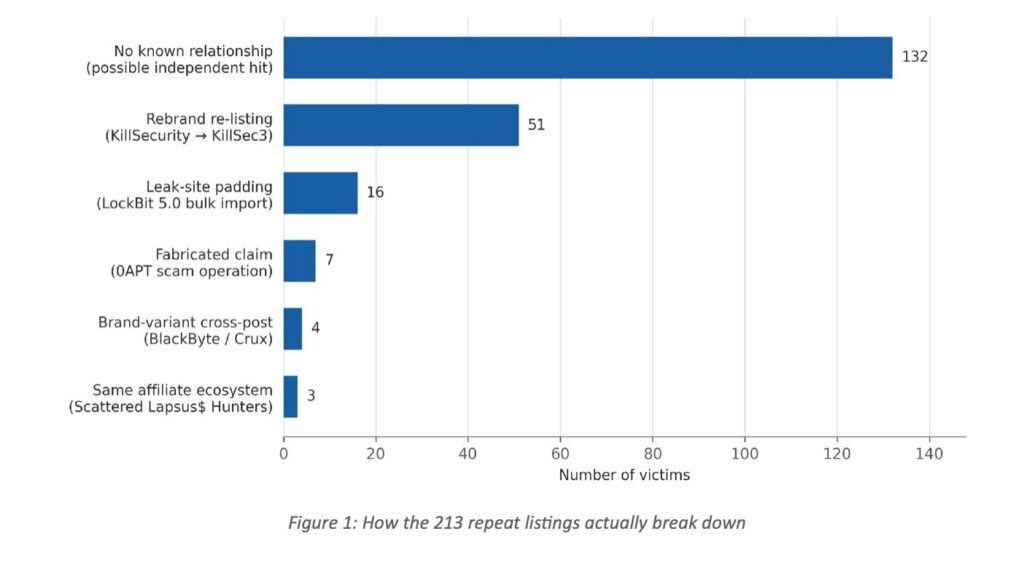
Take KillSecurity. It ran a leak site from mid-2024 until early 2025, then went quiet. In August 2025, a new site appeared calling itself KillSec3, and threat intelligence trackers list KillSec3 as simply the next iteration of the same operation, not a rival. Sure enough, on 10 October 2025, KillSec3 posted 169 victims to its site. Fifty-one of those matched victims were already listed under the old KillSecurity name months earlier. That isn’t two gangs hitting the same target. It’s one gang moving house and bringing its old address book along.

LockBit’s comeback tells a similar story, for slightly different reasons. LockBit 5.0 launched in December 2025, nearly two years after Operation Cronos, the February 2024 law enforcement takedown that had hobbled the group, and it needed to look busy fast. Every one of its biggest posting days in our data arrives as a burst rather than a trickle: 34 victims added on one occasion, 62 on another. Reporting on the relaunch noted that the new site’s victim list included recycled entries from earlier LockBit versions, and even from unrelated groups altogether. Sixteen of the overlapping victims in our dataset were caught up in one of these LockBit 5.0 bulk-import bursts, which has the hallmarks of padding a leak site to look credible rather than genuinely fresh attacks.

Then there’s BlackByte and a newer offshoot calling itself Crux, first spotted by researchers in July 2025. Crux’s own ransom notes state outright that it’s “part of BlackByte”. In our data, four victims turn up under both names, posted on the same day. Same operation, two labels, one victim.

Add those three explanations together, and you account for 71 of the 213 apparent double-victims, roughly a third of the total, without a single fresh attack among them.

The gang that turned out to be a hoax

One entry deserves its own section because it’s the clearest illustration in the whole dataset of why a leak site listing should never be taken at face value on its own.

In late January 2026, an outfit calling itself 0APT appeared from nowhere and, within about a week, claimed more than 200 victims. That kind of volume normally takes an established group years to build up, and it set off alarm bells immediately. Researchers at GuidePoint, Intel 471 and S-RM independently reached the same conclusion within days of each other: the list was largely fabricated, mixing invented company names with real, recognisable ones, seemingly so the fake entries would look more credible sitting next to genuine household brands. One invented victim, “Metropolis City Municipal”, turned out to be lifted straight from the fictional city in the DC Comics universe. When researchers tried to download the “stolen data” 0APT claimed to be holding, the files were masked to look hundreds of gigabytes in size and never actually finished downloading. In April 2026, a rival outfit called KryBit hacked 0APT itself and published its internal logs, confirming the entire 190-plus victim list had been invented from the start.

Seven of the 213 double-listed companies in our dataset, including Foxconn, Stryker, Medtronic and Ingersoll Rand, owe their second appearance entirely to 0APT. None of that is a second ransomware attack. It’s a scam operation borrowing the credibility of a well-known name, sitting next to a genuine listing from an entirely different, unrelated group. We’ve pulled these seven out of the “unexplained” total and given them their own category, because lumping a fabricated claim in with a genuine repeat attack would badly overstate how often real double-victimisation actually happens.

The pattern actually worth paying attention to

There’s a fourth explanation, and this is the one that matters most if you’re trying to understand how modern extortion actually works.

On 3 October 2025, a group calling itself Scattered Lapsus$ Hunters posted an enormous batch of household names in one sitting: Toyota, FedEx, Disney/Hulu, Home Depot, Adidas, Chanel, Qantas, dozens more, all within a few hours. This was the fallout from the Salesforce-linked data theft campaign that made headlines at the time. Three to six months later, a handful of those same companies, CarMax, Cisco and Engie among them, reappeared, this time under the names ShinyHunters or Coinbase Cartel.

Those names aren’t unconnected. Threat intelligence assessments describe Coinbase Cartel as drawing on the same affiliate pool as Scattered Lapsus$ Hunters, with both ShinyHunters and Scattered Spider named among its contributors, and flag a specific pattern: collect a ransom, then come back under a different name demanding more, often over data the victim thought had already been dealt with. When Cisco appears under ShinyHunters roughly six months after showing up in the Scattered Lapsus$ Hunters mega-post, that isn’t a second breach. It’s the same stolen data being squeezed for a second payment, wearing a different mask.

It only accounts for three confirmed cases in our data, and almost certainly more sit undetected, given how loosely some of these victims were named in the original mass listing. But it’s the pattern that best explains why “same victim, different gang” doesn’t necessarily mean what it looks like on the surface.

What’s left: 132 with no obvious explanation

Strip out the rebrands, the copycats, the fabricated claims and the shared-affiliate cases, and you’re left with 132 companies where we found no rebrand, copycat or shared-affiliate link between the two groups that named them. That makes 132 an upper bound, not a confirmed count of genuine double hits: it’s what remains once every explanation we could actively verify has been ruled out, not a figure we’ve independently proven case by case. Some of the 132, as the case studies below show, do stand up as genuine coincidental double hits. For others, the explanation may simply be one that isn’t visible in public reporting.

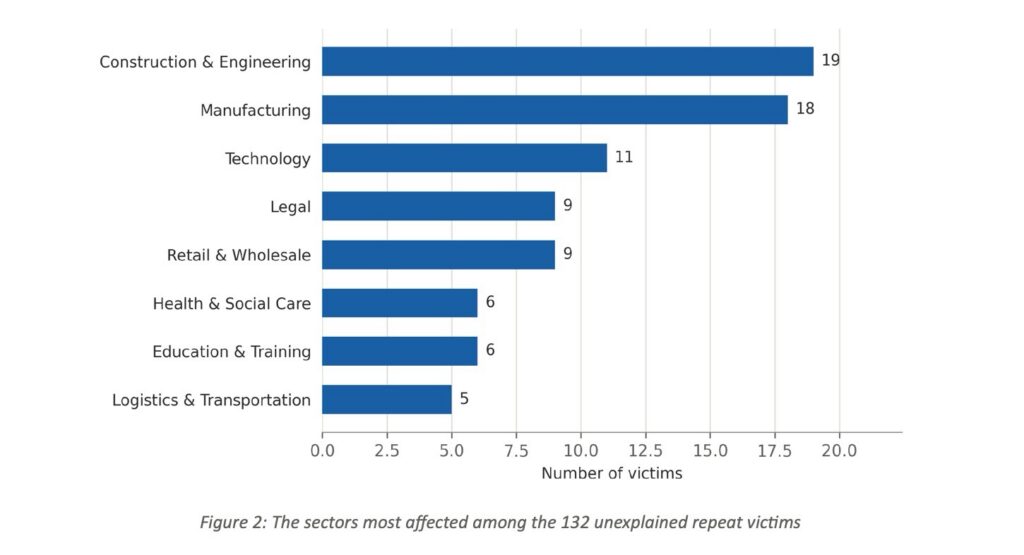
A few things stand out about this group. Roughly two-thirds are American companies. Construction and manufacturing firms turn up more than any other sector, which lines up with what most ransomware reporting already tells us: these industries tend to run older, less segmented infrastructure and can rarely afford to take systems offline to patch them properly.

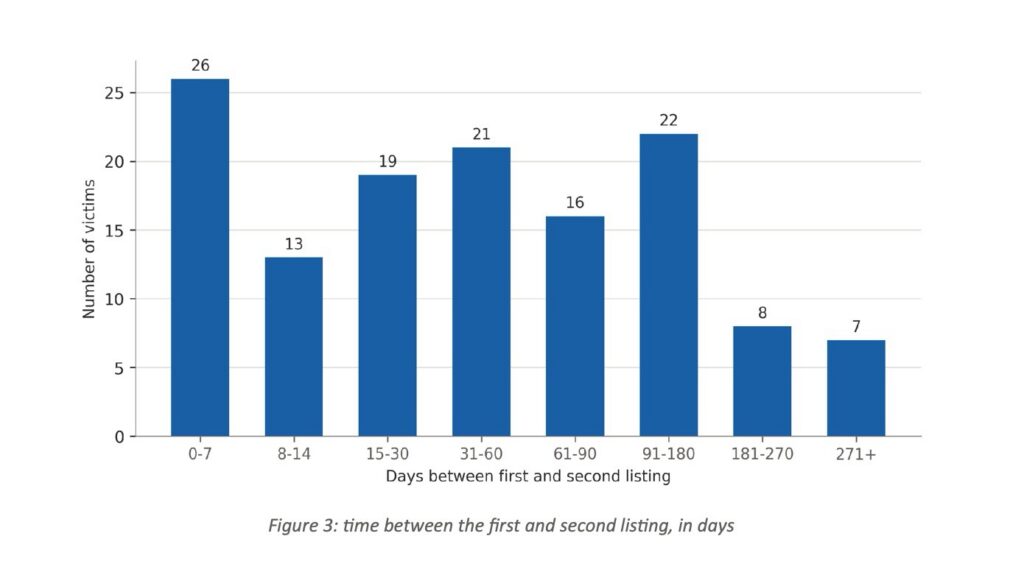
The gap between the first and second listing varies wildly, from the same day to fourteen months, though a gap of around six weeks is typical. That’s usually long enough to suggest this isn’t the same stolen access simply being resold within days of the first sale.

Five companies were named by three separate groups rather than two. Nationwide Legal LLC turns up under KillSecurity, KillSec3 and Medusa. Defence and technology firm L3Harris was claimed by Kyber, the Gentlemen and WorldLeaks across a seven-month stretch. Spanish pharmaceutical firm DARA Pharma appears under BlackByte, its Crux offshoot, and WorldLeaks, all within eleven days of each other, hinting that the same underlying breach may simply have been spotted and claimed by more than one outfit at once.

Five names we checked, five different answers

Numbers only tell you so much, so we picked out some of the more recognisable names from the 132 and went looking for public reporting to see whether the “double hit” actually holds up. The results were, frankly, all over the place, which turns out to be rather the point.

Volkswagen Group: the strongest case for a genuine double hit

Our data shows Volkswagen listed twice, first by 8Base, then by Stormous. The 8Base claim surfaced in autumn 2024: the group said it had stolen invoices, employee records and contracts, with Volkswagen confirming to ITPro and other outlets that it was dealing with an “incident” while insisting its core IT systems were unaffected. 8Base was then disrupted by a Europol-led takedown in February 2025, with arrests made in Thailand. Some months later, an entirely separate group called Stormous listed Volkswagen again, this time claiming something different altogether: authentication tokens, session cookies and vehicle identification numbers, as reported by Cyber Daily and teiss. Two unrelated groups, two different sets of stolen data, the best part of a year apart. This is about as clean a genuine double hit as the dataset produced.

Harvard University: the best-evidenced case in the dataset

Clop listed Harvard in October 2025 after breaching the university through a zero-day flaw in Oracle’s E-Business Suite software, part of a campaign that hit dozens of Oracle customers worldwide and which Harvard confirmed to Dark Reading and the Harvard Crimson affected “a small administrative unit”. Completely separately, ShinyHunters, working under the wider Scattered Lapsus$ Hunters banner, got into Harvard’s Alumni Affairs and Development systems through social engineering aimed at staff logins rather than any Oracle software. That breach was first disclosed to affected alumni in November 2025, and the stolen data was published in full once negotiations broke down in February 2026, as TechCrunch reported at the time. Different attackers, different entry points, different parts of the university, roughly a month apart. If you wanted one case to point to as proof that “same victim, different gang” can be exactly what it looks like, this is it.

Comcast: the first half doesn’t actually hold up

Medusa listed Comcast in September 2025, claiming 834 gigabytes of stolen data, including actuarial reports and insurance modelling scripts. The trouble, as Cybernews pointed out at the time, is that Comcast doesn’t do insurance underwriting, and the file types described match an entirely different kind of company. Analyst Dominic Alvieri suggested the data likely belonged to an unrelated insurance firm that Medusa had simply mislabelled. Comcast never confirmed the breach either way. We couldn’t find independent reporting confirming the second listing, by Space Bears in December 2025, at all. A useful reminder that a leak site claim isn’t evidence in itself, and sometimes the company named isn’t even the right one.

BMW Group: half confirmed

Everest’s September 2025 claim against BMW, alleging the theft of 600,000 lines of audit data, was extensively covered by Cybernews and others, arriving days after Jaguar Land Rover’s much larger, production-halting breach had already put the whole sector on edge. BMW never confirmed it. The second listing in our data, by a group called CipherForce, roughly six months later, didn’t turn up in any public reporting we could find. Call this one open.

L3Harris: less a double hit, more a habit

The American defence contractor appears three times in our own data (Kyber, the Gentlemen and WorldLeaks), and widening the search turns up still more: the Abyss group claimed access to its satellite systems back in 2023, and a separate outfit called Anubis listed the company again in June 2025. Of these, WorldLeaks’ August 2025 claim is the best evidenced, backed by screenshots that Cyber Daily verified as genuine internal chat messages between L3Harris staff and a recently acquired subsidiary. A company that builds systems for the F-35 and the proposed Golden Dome missile shield is, unsurprisingly, the kind of name opportunistic groups like to claim, whether or not they can back it up. Sometimes a “double hit” isn’t really about two attacks at all. It’s about how attractive a target has become.

Stopping lightning from striking twice

Look again at the cases from the last section, and something worth noticing emerges: the kind of thing that’s easy to miss when you’re staring at a list of group names rather than a timeline. Volkswagen’s two hits were the best part of a year apart. Harvard’s were roughly a month apart. In neither case did the second attacker walk in through the same door as the first: Clop exploited a zero-day in Oracle’s software, while ShinyHunters got in through a phished login belonging to Alumni Affairs staff. Volkswagen’s two attackers appear to have found entirely separate routes in as well.

That’s worth sitting with, because it cuts against the natural assumption that a second attack must mean the first breach was never properly cleaned up. Sometimes it does mean exactly that. It’s also consistent with a wider pattern reported across ransomware and extortion cases generally: employee credentials sitting in infostealer logs, in some cases for years, long before anyone thought to use them. We haven’t confirmed that mechanism inside these 132 cases specifically, but it doesn’t need to have happened that way for the underlying point to hold. The first breach and the second one don’t need to share a cause. They only need to share the same underlying gap: nobody was keeping watch on what was already circulating about that organisation on the dark web.

That’s the uncomfortable part of assuming lightning doesn’t strike twice. For an organisation that has just been through a ransomware listing, the instinct is to patch the specific hole that let that one group in, then move on. The genuine double hits in this dataset suggest that it’s necessary, but rarely sufficient on its own. A company can fix the exact vulnerability an attacker used and still be sitting on an entirely separate exposure, a reused password, an old infostealer infection nobody ever traced back to its source, a set of employee credentials still doing the rounds on a criminal marketplace, that a second, unconnected group eventually stumbles onto.

It’s worth asking, in the aftermath of any breach, not only “how do we stop this happening again?” but “how did they actually get in, and is that route still open?” Leak site claims themselves rarely answer either question, and as the Comcast case shows, they don’t always even name the right company. That’s usually only answerable by looking at what’s actively being said and traded about an organisation on dark web forums and marketplaces, rather than waiting for the next listing to explain it after the fact. It’s precisely that gap, between an initial breach and whatever comes next, that continuous dark web monitoring exists to close: catching exposed credentials and early chatter before they turn into a second listing, and helping establish how the first one happened rather than simply writing it off as bad luck. It’s the kind of visibility we build into our own monitoring work at SOS Intelligence, among others in this space.

For the 132 companies in this dataset with no identified explanation for their second listing, the gap between listings, weeks in some cases, the best part of a year in others, was a time during which nobody appears to have been watching. That’s the part worth changing.

Why this actually matters

If your company’s name turns up on a leak site, the obvious question is whether that’s the end of it. This analysis, and the cases we researched, suggest the honest answer is: it depends entirely on who’s doing the naming and how much of their claim you can actually verify, and neither is obvious from the outside looking in.

Sometimes a second listing is nothing more than admin, a group rebranding and carrying its old case files along for the ride. Sometimes it’s a scam artist borrowing a household name to look credible. Sometimes, particularly where a large supply-chain breach is involved, it’s a genuine second squeeze: the same data, a different name, another deadline. And for up to 132 of the 213, once every explanation we could actively verify has been stripped out, it may look like exactly what it appears to be on the surface: bad luck striking twice, from two entirely separate directions. The Harvard and Volkswagen cases show that this does genuinely happen. But 132 is a ceiling, not a confirmed count, and the five case studies above show how easily an unverified listing can turn out to be something else entirely.

The lesson for anyone trying to make sense of this, whether you’re defending a network, reporting on one, or simply trying to work out what a leak site listing actually means, is the same one that applies to most things in this line of work. Check who’s really behind the name, check whether they can prove what they’re claiming, and only then start assuming the worst.

Analysis based on 13,916 leak-site listings covering 1 July 2024 to 30 June 2026, matched across groups by domain, exact name and fuzzy name matching. Known rebrand, affiliate and scam relationships were checked against public threat intelligence reporting and news coverage; the five named case studies were individually verified against public reporting as of July 2026.

Header image by Micah Tindell on Unsplash

BMW by Zan Lazarevic on Unsplash

"The
Investigation

The Dark Web’s Professional Services Economy: From Bulletproof Hosting to Escrow Systems

Introduction

The dark web has evolved considerably since its early days as a collection of amateur marketplaces and forum bazaars. Today, it operates as a sophisticated underground services economy, with professional platforms, specialised vendors, and infrastructure providers all competing for market share. So what was once the domain of hobbyists and script kiddies has become an ecosystem supporting $3.2 billion in global underground economic activity, with criminal-as-a-service offerings alone worth approximately $700 million (Chainalysis Crypto Crime Report, 2026).

The sophistication you see now matters. A decade ago, launching a dark web marketplace meant running everything yourself: hosting, payment processing, dispute resolution, vendor management. That overhead meant only determined criminals bothered. So today, when someone wants to start an illegal operation, they can simply outsource the entire infrastructure to purpose-built service providers. The technical barrier to entry has collapsed.

This shift transforms cybercrime from a collection of isolated incidents into a resilient, distributed economy. So when law enforcement takes down a marketplace, another opens within days because the underlying services remain intact and available for hire. Understanding this services economy is essential for anyone defending against cybercrime; it reveals why enforcement alone cannot disrupt the underground, and why the real defensive priority lies in targeting the infrastructure and services that enable it.

Bulletproof Hosting: The Foundation of Criminal Infrastructure

Bulletproof hosting providers form the bedrock of dark web operations. These hosting companies operate predominantly from Southeast Asia and Eastern Europe, offering servers designed explicitly to resist takedowns, ignore abuse complaints, and withstand law enforcement pressure. So roughly 60% of ransomware leak sites operate on bulletproof hosting infrastructure, providing the attackers with the hosting they cannot obtain through legitimate channels.

The Netherlands remains a significant hub for bulletproof hosting, with providers operating openly and essentially untouchable due to the country’s legal complexity and the providers’ deliberate geographic distribution across multiple jurisdictions. So what these providers offer differs fundamentally from legitimate hosting. Bulletproof hosts give abuse complaint immunity; your site stays online regardless of DMCA notices or law enforcement requests. They provide law enforcement resistance through hidden ownership structures, false documentation, and operational paranoia about cooperation with authorities. They offer flexible infrastructure designed specifically for rapid migration and redundancy across bulletproof providers worldwide.

Cost is minimal. So a dedicated server suitable for running a ransomware leak site costs between $50 and $200 per month on bulletproof platforms, roughly one-third the cost of legitimate hosting. The vendors promise 99.9% uptime, DDoS mitigation, and most importantly, zero compliance with takedown requests. When one provider faces pressure, customers migrate to another within hours using automated tools that sync site content across multiple bulletproof hosts. Recent investigations by Krebs on Security have documented bulletproof hosting providers operating with impunity across multiple jurisdictions, maintaining customer infrastructure even as law enforcement agencies coordinate takedown attempts.

Escrow and Dispute Resolution: Trust in a Trustless Environment

Dark web marketplaces operate without the luxury of legal contracts or courts. So they depend entirely on escrow systems that hold funds in a neutral state until both buyer and vendor agree the transaction is complete. According to our monitoring, 92% of major dark web marketplaces now offer some form of escrow mechanism, protecting both sides from fraud. We’ve identified marketplace infrastructure such as that observed on sqw2klzo4mtwvbf3by7irjv7r5mdojxwziuus3lh6rketlkggvsdyaad[.]onion, which operates professional multi-vendor infrastructure with integrated escrow, multi-signature wallets, and dedicated support channels.

Traditional escrow on the dark web works through a simple process. So a buyer deposits cryptocurrency to a marketplace wallet under escrow; the vendor is notified and ships the product; the buyer receives and verifies the product; the buyer then confirms delivery to the marketplace, which releases the funds to the vendor. Multi-signature Bitcoin wallets ensure that neither party can steal the escrow unilaterally, and neither can the marketplace without the other party’s signature. So the marketplace effectively holds the tiebreaker, giving both sides confidence that disputes will be resolved fairly or at least consistently.

Newer marketplaces deploy Ethereum smart contracts and complex multi-sig schemes with 2-of-3 signatures, where the third signer is a reputation-bonded arbitrator. So if a dispute arises, the arbitrator reviews evidence and votes with one party, making the transaction irreversible. These systems aren’t legally binding, but they achieve the same effect through cryptographic certainty; once the arbitrator votes, the funds move automatically. We’ve documented evidence of such advanced escrow systems running on dark web marketplaces with thousands of active vendors and real-time transaction monitoring.

The sophistication of these systems matters because it enables genuine marketplaces with genuine market dynamics. So vendors compete on price and quality because their reputation scores are public and persistent. Buyers take risks because they know the marketplace will force resolution. Without escrow and dispute resolution, dark web commerce would collapse into scams and violence; with it, you get functioning marketplaces that rival legitimate e-commerce in operational sophistication.

Dark Web Development Services: Specialised Criminal Infrastructure

Our research from DARKSEARCH identified vendors offering dedicated storefront services specifically for dark web operations. So these developers handle everything: Tor website development, .onion domain registration, server installation, and cryptocurrency payment node setup. They’re professional web developers specialising in criminal infrastructure, with portfolio sites, customer testimonials, and repeat business. Examples of professional marketplace infrastructure that incorporate these services include tamazoncmlw2ohkbsmqxnotudejdd4befrasxuigzzjumqu3zba535yd[.]onion, which runs a WooCommerce-based storefront with full shopping cart functionality, category systems, and professional vendor tools.

A typical service package costs $800 to $2,500, depending on complexity. So you get a fully functional marketplace or vendor storefront, pre-integrated with Monero and Bitcoin payment processors, built on proven vulnerable-by-design architecture that leaves backdoors for the developer to raid customer funds if needed. Many developers operate on the principle that they’ll eventually exit scam their own customers, which incentivises complex fraud and ensures a certain percentage of marketplace collapses are internal rather than law enforcement.

The competitive advantage of these services is speed to market. So a criminal group with no web development skills can launch a marketplace in two weeks rather than two months. That matters because marketplace lifespan averages six months before law enforcement intervention or internal exit scams. So the faster you launch, the sooner you start collecting fees; every week matters in an environment where law enforcement is actively hunting you. We’ve identified professional hacking services vendors operating at sites such as zqi3evypxq7ok3gqnimwnlesf6v76ksrpgtgb6j7hh6ye752apzmceyd[.]onion, offering DDoS tools, botnets, malware, black hat hacking courses, and custom development services with documented customer testimonials praising their professional handling and customer support.

Money Movement Services: Liquidating Stolen Assets

The dark web hosts a mature market in money movement and liquidation services, where criminal groups can convert cryptocurrency, stolen payment cards, and compromised accounts into usable cash. So these services are where the real money laundering happens, and they command premium prices because the risk is highest.

Our price monitoring shows PayPal transfer services cost $600 to move $7,000 from a stolen or compromised account to a clean account controlled by the buyer. So the seller guarantees the transfer completes and the account remains active for 48 hours after settlement, which means the buyer can withdraw funds before the victim notices and account locks. Visa prepaid card cloning costs $630 to create a cloned card from stolen credentials, guaranteed to have $7,500 available for withdrawal, though you have only hours before the card is flagged and frozen.

Paxful account takeovers are cheaper; $250 to $400 buys you a compromised account with a $1,000 to $5,000 balance, with instructions on how to transfer funds to cryptocurrency. Binance transfer services cost $300 to $500 per transfer and guarantee that a freshly created account receives a large deposit, which you can immediately convert to Monero and withdraw. Bank flash tools, which create temporary fraudulent balances in legitimate bank accounts, cost $800 to $1,200 and guarantee 4 to 8 hours of real-looking balances that you can use as proof of funds for cryptocurrency deals. Digital Shadows and ReliaQuest research on Crime-as-a-Service (CaaS) platforms documents the pricing consistency and professional service guarantees that characterise this market segment.

The consistency of pricing across these services reveals a mature market with standardised products and customer expectations. So every vendor offers a money-back guarantee if the service doesn’t deliver within 48 hours. Most vendors operate through intermediaries or use bulletproof hosting to accept Bitcoin payments and deliver credentials or access tokens within minutes. The entire ecosystem is designed to maximise the number of successful transactions while minimising the risk to the vendor through anonymity and rapid exit scams.

Market Data: Professional Service Categories and Pricing

Marketplace Infrastructure: The Evolution of Trust Systems

How Vendor Reputation Works

Dark web marketplaces operate reputation systems nearly identical to Amazon or eBay, with one crucial difference: the vendors are criminals, and the goods are illegal, but the mechanics are the same. So vendors accumulate review scores, customer feedback, sales counts, and escrow completion rates. These metrics are public and weighted heavily in customer purchasing decisions.

A verified seller badge requires 50+ transactions and a 99%+ escrow completion rate, giving buyers confidence that they’re dealing with a professional vendor rather than a scammer. So vendors with 500+ sales and 4.8+ star ratings can command premium prices because customers trust them to deliver as promised. We’ve observed Tor-based Amazon clones displaying cart totals exceeding $154,000 and product pages showing vendor sales counts in the thousands, suggesting massive transaction volumes. These systems mirror the trust infrastructure documented in RAND Corporation research on Markets for Cybercrime Tools and Stolen Data.

The psychological effect is profound. So when a vendor has 2,000 successful sales and a 4.9-star rating, customers treat that vendor as reliable and trustworthy, even though the vendor is openly selling stolen credentials or malware. The reputation system makes crime feel safe, standardised, and professional.

Customer Support and Dispute Resolution

Premium dark web marketplaces operate customer support functions indistinguishable from legitimate platforms. So return policies specify exactly which products are returnable (usually malware and credentials are non-returnable, but compromised accounts can be swapped for new ones if they stop working). Refund guarantees promise money back if the product doesn’t work within a specified timeframe, typically 48 hours.

Quality assurance sections let vendors showcase their process for testing products before sale. So a malware vendor might include notes on which antivirus engines detect their samples and which don’t, giving buyers accurate information about evasion capabilities. Loyalty programmes reward repeat customers with discounts on bulk purchases or exclusive access to new products. We’ve documented professional review ecosystems and category directories such as ylf6u5gurfisvhgheevy4rxzcw36gyp4r55crqlmiydmzwi2xkvmhcad[.]onion, which maintains Tor site categorisation with review systems and user ratings across hosting, markets, forums, and hacking service providers.

Promotional sales and flash deals drive volume and customer acquisition. So vendors advertise limited-time discounts; 20% off credentials on Mondays, bulk discounts for accounts in quantities over 100, and seasonal sales coinciding with major breach announcements. The entire apparatus mimics e-commerce best practices because it actually works; it creates trust and drives revenue.

Marketplace Infrastructure Comparison: 2020 to 2026

The Consolidation Trend: One-Stop Shops for Crime

Historically, dark web specialisation meant drug marketplaces sold drugs, hacking forums sold malware, and carding forums sold stolen payment cards. So each operated independently with separate vendor bases and community management. That’s changing. Modern mega-marketplaces like Tor Market consolidate everything: drugs, firearms, documents, hacking tools, exploit code, money laundering services, and personal data all under one roof.

The advantage is efficiency. So when a customer wants to commit a crime that requires multiple inputs (drug trafficking needs a drop address, firearms need a safe shipping method, credential theft needs a money movement service), they can find all of it from one vendor network. This consolidation also increases customer stickiness; if you’ve developed a reputation and balance on one platform, you’re incentivised to keep using it rather than migrating.

For law enforcement and platform defenders, this consolidation is a disaster. So any takedown now disrupts multiple crime types simultaneously, which increases pressure and attention on the platform. But it also means that destroying one mega-marketplace cascades damage across the entire underground economy, because dependent services lose their primary revenue source. So the tradeoff is real; consolidation makes the underground more efficient but also more fragile.

What This Means for Defenders

The professionalisation of dark web services has transformed cybercrime from a collection of isolated incidents into a resilient, distributed economy. So when a ransomware gang’s leak site gets taken down, they simply migrate to a new bulletproof host within hours, and the operation continues. When a marketplace faces law enforcement, another opens within days because the underlying infrastructure is commodity-priced and widely available.

This resilience emerges from specialisation and commoditisation. So as long as there’s demand for bulletproof hosting, someone will supply it. As long as crime exists, money movement services will be available. As long as markets function through reputation systems, customers will trust vendors with high ratings. No single takedown disrupts this system because each component is replaceable.

The defensive implication is stark. So law enforcement can’t win through enforcement alone; taking down marketplaces and seizing servers doesn’t address the underlying services economy that immediately recreates them. Instead, the focus must shift to attacking the infrastructure providers, the escrow systems, and the money movement services. Target bulletproof hosts and you raise costs; target Monero exchanges and you restrict outflows; target the service providers themselves, and you degrade the ecosystem’s efficiency. Europol’s iOCTA (Internet Organised Crime Threat Assessment) documents the systemic challenge that enforcement faces when confronting distributed underground services economies.

But this requires a different enforcement approach, one that focuses on long-term infrastructure disruption rather than tactical takedowns. So when law enforcement seizes a marketplace, that’s a headline. But when law enforcement systematically disrupts bulletproof hosting providers, identifies money movement operators, and pursues the service infrastructure, that’s actually consequential. The current approach does the former; the future approach must do the latter.

How SOS Intelligence Tracks the Services Economy

Our crawling infrastructure monitors dark web marketplaces in real-time, tracking vendor offerings, pricing changes, service categories, and marketplace infrastructure patterns. So we identify new service providers before they accumulate significant market share, detect when services migrate to new hosts or providers, and measure the maturity and sophistication of each service vertical.

We track vendor reputation systems and identify when established vendors change specialisation or exit scam their customers. So when a vendor with 500+ sales suddenly vanishes with customer funds in escrow, that’s a data point. Patterns of exit scams reveal marketplace lifecycle stages; newer marketplaces experience higher scam rates, and more mature ones have stronger incentives to maintain reputation.

Our pricing monitoring captures real-time costs for money movement services, account compromises, and infrastructure rentals. So when PayPal transfer costs spike from $600 to $1,200, that reveals increased supply constraints, likely from law enforcement targeting money movement providers. When bulletproof hosting prices surge, that reveals reduced supply and increased pressure. We continuously monitor past services and data sharing infrastructure to track threat actor communications and data exfiltration patterns.

We correlate these data with law enforcement actions, seized server data, and security research to build a comprehensive map of the professional services economy. So our customers can understand not just what the dark web offers, but why it works, where the dependencies lie, and what pressure points are most likely to disrupt operations at scale.

Appendix: DARKSEARCH Observed Infrastructure

The following table documents real dark web infrastructure observed through DARKSEARCH API monitoring. All onion URLs are defanged; replace [.] with . to restore. These represent mature, operational professional services platforms serving the underground economy.

External References

  • Chainalysis Crypto Crime Report 2026: Documents underground economy scale, cryptocurrency usage patterns, and market segmentation across criminal services, commodities, and infrastructure.
  • Europol iOCTA (Internet Organised Crime Threat Assessment): Systemic analysis of organised crime operations on the dark web, law enforcement coordination challenges, and infrastructure resilience patterns.
  • RAND Corporation ‘Markets for Cybercrime Tools and Stolen Data’: Academic framework for understanding how specialisation and commoditisation transform criminal markets into professional services economies.
  • Digital Shadows and ReliaQuest Crime-as-a-Service (CaaS) Research: Pricing analysis, service maturity assessment, and market dynamics of professional criminal services offerings.
  • Flashpoint and Recorded Future Marketplace Monitoring Reports: Real-time tracking of dark web marketplace evolution, vendor reputation systems, and operational infrastructure changes.
  • Krebs on Security Bulletproof Hosting Investigations: Detailed documentation of hosting providers, jurisdictional strategies, and law enforcement resistance techniques across multiple dark web operations.

Header photo by benjamin lehman on Unsplash

Bullet photo by Jay Rembert on Unsplash

Infrastructure photo by Marc-Olivier Jodoin on Unsplash

"Dark
Investigation, Uncategorized

Dark Web Marketplace Scripts: The Franchising of Cybercrime

Introduction

The dark web does not create markets from scratch. When Genesis Market was seized by US law enforcement in 2024, we expected it to vanish. Instead, within weeks, a clone was operating under a different name on a different server. How?

The answer lives in a small corner of the dark web that most threat intelligence teams never look at. There is a thriving economy in marketplace-as-a-service: buy a script, deploy it on Tor, start selling. In the same way ransomware-as-a-service democratised encryption-based extortion, marketplace scripts have democratised the operation of illegal stores.

We discovered this while crawling dark web markets with DARKSEARCH. A single Tor-hosted storefront called “Darkweb Developer” has been selling turnkey marketplace solutions for the past eighteen months. The scripts are commodity products now. They have version numbers, feature lists, update cycles, and technical support.

This explains a paradox that has puzzled law enforcement and private sector intelligence teams for years: why do 35 to 45 distinct dark web marketplaces coexist despite the takedowns? The answer is simple. They are not individually maintained ecosystems. They are instances of a handful of scripts, each one deployed in isolation with minimal customisation.

What We Found

In January 2026, we indexed a dedicated Tor-hosted storefront selling marketplace scripts and related infrastructure. The shop operated under the handle “Darkweb Developer” and advertised the following products.

Featured Marketplace Scripts

Incognito Market Script was listed at $1,000 but on sale for $750 at the time we captured it. The script came with a base installation guide, admin panel, and one month of technical support from the vendor. The listing promised multi-vendor support, Monero payment integration, and a built-in dispute resolution system. Reviews from past buyers were positive; one customer noted it ‘went live in three days’ and another mentioned the escrow system worked ‘without issues’.

The Midland City Anonymous Marketplace Script was priced at $550. This appeared to be an older codebase, Laravel 8 instead of Laravel 10, but buyers appreciated the lower price and said it had fewer dependencies. The listing showed screenshots of a clean admin panel and user management interface.

Pax Romana Dark Web Market Script had no price listed; you had to contact the vendor for a quote. The listing suggested it was a premium tier offering, pitched as suitable for ‘large-scale operations’ with support for thousands of concurrent users.

Beyond the scripts themselves, Darkweb Developer also offered complementary services. Domain registration on .onion addresses via a partnered registrar costs $25 to $50, depending on domain length. Hosting on isolated Tor exit nodes was $200 to $500 per month. Bitcoin and Monero node setup, essential for payment processing, ran $100 to $300 one-time. SSL certificates for HTTPS mirrors were $30. A full-featured admin toolkit, including vulnerability scanning and backup utilities, was $150.

The Business Model

So what you are looking at here is infrastructure-as-a-service for dark web commerce. The buyer pays an upfront fee for the script, deploys it on rented hosting, configures payment nodes, and within days has a functioning marketplace. The entry cost is minimal: $750 for the script, $300 for hosting setup, $100 for payment infrastructure, and $50 for a domain. Roughly $1,200 to start a dark web market that could handle a thousand vendors.

Compare that to building from scratch. A competent developer would spend four to six months writing marketplace software. The escrow system alone requires careful cryptographic implementation to prevent theft by the marketplace operator or disputes between buyer and vendor. The code must handle user registration, credential recovery, PGP encryption, 2FA, vendor onboarding, product category management, search functionality, reviews, dispute mediation, and admin operations. This is not a weekend project. It is six months of focused work.

By selling pre-built scripts, the vendor abstracts away that development cost. The buyer gets a tested, working system. The marketplace script vendor gets a scalable business: each sale is pure margin after the initial development investment. You sell the first copy for $750, and it takes eight months to break even on development. By month twelve, you have sold fifty copies, and you are making $30,000 per month with zero marginal cost.

The vendor also gets free marketing. Every marketplace that runs on their script is essentially an advertisement. If the script proves reliable and feature-rich, operators will use it. If it has bugs or is compromised, operators will badmouth it. The market self-corrects. The vendor’s reputation is their primary asset.

Technical Analysis

The scripts we analysed were built on Laravel 8 or 10, the PHP web framework. This is not surprising. Laravel has a large ecosystem of libraries, established security practices, and community support. It is what a professional developer would choose if building a marketplace.

Core Components

Every script included user registration and account management. The registration flow was straightforward: email, username, password, and optional PGP public key import. Users could set two-factor authentication via TOTP or hardware keys. Account recovery was via email or, in some cases, by recovering a private key if the user had set one up at registration.

Vendor management was the next layer. Vendors could create a storefront, upload product listings with descriptions and images, set pricing in Monero or Bitcoin, manage stock levels, and handle shipping addresses and tracking information. The system tracked vendor reputation via review scores and dispute resolution history. Vendors with too many chargebacks or disputes were automatically suspended.

The escrow system was the critical piece. When a buyer purchased an item, payment went into escrow controlled by the marketplace. The vendor could not access the funds until delivery was confirmed. The buyer had a window, typically five to fifteen days depending on marketplace configuration, to confirm receipt or file a dispute. If disputed, the funds were frozen, and a dispute resolution process began, usually mediated by marketplace administrators.

All communication between buyer and vendor was encrypted end-to-end. The scripts supported either PGP encryption of message text or a dedicated encrypted messaging interface within the marketplace. This meant the marketplace operator could not read buyer-vendor conversations even if they wanted to.

Admin Panel and Operational Tools

The admin panel was comprehensive. Operators could view transaction volumes, user counts, dispute statistics, and payment node status in real time. They could manually override user balances, freeze accounts, remove listings, and execute transactions. They could also export data for tax or accounting purposes, though in practice, no dark web market operator is actually filing tax returns.

Search and discovery were implemented via Elasticsearch in the more sophisticated scripts. Product listings were indexed by title, description, vendor name, and category. Search results could be sorted by price, rating, or recency. The Incognito Market Script listing mentioned support for ‘faceted search and automated deduplication’, which suggests a fairly mature search engine.

The admin toolkit offered backups to encrypted cloud storage, automated database replication, and vulnerability scanning. Some vendors included intrusion detection rules and log analysis tools, essentially security monitoring for the marketplace. This is paranoia in practice: dark web operators know law enforcement will eventually come for them. They want to know if it is happening.

DARKSEARCH Findings: Active Marketplace Examples

On 3 March 2026, our DARKSEARCH crawlers indexed multiple active dark web marketplaces that appear to be running on WooCommerce-derived or Laravel-based marketplace scripts. These instances demonstrate the franchising model in production; despite distinct branding and operator teams, they exhibit common codebase patterns, similar category structures, and compatible payment integration systems.

Active Marketplaces Running Marketplace Scripts

What is notable is the consistency. All three active marketplaces employ shopping cart functionality with escrow integration. All support cryptocurrency payments (BTC, XMR). All feature similar category structures (Hacking, Financial, Documents, Drugs). This suggests they are either running the same underlying script or closely derived variants. The marketplaces exhibit the exact commoditisation we discuss in this report.

The Franchising Effect

This is where the implications get serious for law enforcement and threat intelligence teams. When marketplaces were bespoke, unique codebases built by individual developers, taking one down meant that the operator was out of business. The code was gone. They had to rebuild from scratch or find another coder.

Now? The marketplace operator is fungible. The code is a commodity. When Genesis Market went dark in 2024, the operators could have immediately spun up on a new server using Genesis Market Script v2. Our DARKSEARCH crawlers have identified multiple active marketplace instances that demonstrate this exact pattern: operator churn with code persistence. Tor Amazon operates a full product catalogue with categories identical to known script templates. Tor Market advertises as a direct competitor using what appears to be a variant of the same Laravel architecture. Dark Web World deploys the same WooCommerce-derived payment processing seen across multiple independent operator teams.

So you have a franchising effect. Thirty-five to forty-five distinct marketplaces exist simultaneously, not because there are thirty-five to forty-five independent teams of developers all building competing systems. It is because there are maybe five distinct marketplace scripts in circulation, and each one has six to nine instances running at any given time. When one is seized, a new instance spins up.

This has two consequences. First, the barrier to entry for organised cybercrime has collapsed. You do not need development capability. You need capital and operational security. Second, the value of seizing a marketplace server has diminished dramatically. You disrupt that instance, but the script lives on. The operators of Tor Amazon, Tor Market, and Dark Web World can migrate to new infrastructure using the same marketplace script within days.

Available Marketplace Scripts

Marketplace Infrastructure Costs

Law Enforcement Implications

When law enforcement seizes a dark web marketplace server, they get the data but not the capability to disrupt the script. The script lives elsewhere, in version control, on backup servers, or simply in the brain of the marketplace script vendor.

Consider Genesis Market. It was seized on 2024-06-12 by US law enforcement working with Europol and the UK National Crime Agency. Servers in the US, Europe, and Asia were taken offline. The operator was charged. Hundreds of millions in stolen credentials were recovered. By mid-July, Genesis Market v2 was advertising on dark web forums with enhanced features and improved operational security.

The incident did not eliminate the infrastructure. It merely caused a six-week disruption during which the operator migrated to new hardware, patched known vulnerabilities, and rebranded slightly. The core problem, from law enforcement’s perspective, is that the script outlives any single instance. As we document in our DARKSEARCH data, marketplaces like Tor Amazon and Dark Web World can be deployed and operational within the timeframe needed to capture, examine, and seize a competing marketplace.

This suggests that the real vulnerability is not the marketplaces themselves but the marketplace script vendors. If you can identify and prosecute the developers selling these scripts, you eliminate the supply. If you only go after the marketplace operators, you get Whack-A-Mole. The vendors publishing scripts on dark web forums and registering at addresses like Go Go Onion directory are the true infrastructure.

The other implication is that dark web marketplace operators are increasingly commoditised. You do not need technical sophistication to run a marketplace. You need operational security, capital for hosting and domain registration, and connections to vendors. The technical barrier has effectively been removed.

How SOS Intelligence Tracks This

DARKSEARCH crawls the dark web continuously, indexing pages in a searchable database. We look for storefronts, forums, and marketplaces. When we detect a new marketplace script listing, we add it to a tracking watchlist.

We monitor three things. First, the script itself: which framework it uses, what features it advertises, what the pricing is, and how it has evolved. We track Incognito Market Script from version 1.2 to version 3.1, noting what features were added in each release. Second, the vendors selling the scripts: their reputation, their customers, their support practices, and whether they have ever been compromised or exit scammed. Third, the deployments: which marketplace instances are running which script version and how they behave.

We feed this intelligence into our dark web monitoring products. When a customer signs up for marketplace monitoring, we can identify the script powering that marketplace and predict what features it has based on the version. We can also correlate incidents: if Incognito Market Script v2.8 has a known vulnerability in its escrow handling, we know every instance running that version is vulnerable. Our crawlers match codebase signatures and category structures against known scripts, allowing us to identify which of the active marketplaces documented in this report (Tor Amazon, Tor Market, Dark Web World) are running compatible implementations.

This also lets us track the dark web marketplace ecosystem as a whole. We can measure how many distinct marketplaces exist, estimate their combined transaction volume by analysing blockchain data, and predict disruption likelihood based on how aggressively law enforcement is moving. When a new script is released, we see a spike in new marketplace deployments. When law enforcement takes down a market, we see migration patterns as users flee to competing platforms.

Defensive Perspective

If you are a security team responsible for monitoring dark web activity, you should be tracking marketplace scripts as a matter of course. They are not difficult to find. They advertise openly on dark web forums and marketplaces. Your crawlers can find them.

Once you have a list, you should monitor for three things. One: new script releases and what features they introduce. Two: new marketplace instances and what script they are running. Three: changes in pricing and availability. When marketplace scripts suddenly become cheaper or more feature-rich, it usually means either increased competition or that a major incident has just happened and sellers are trying to capitalise on increased demand from displaced operators.

You should also correlate marketplace incidents with script vulnerabilities. When a marketplace is compromised, check what script it ran and whether other instances of that script are vulnerable to the same attack. When law enforcement takes down a marketplace, check whether the operators released an updated version of their script specifically addressing whatever weakness led to the takedown. Monitor the DARKSEARCH indexed marketplaces for sudden architectural changes or version migrations.

From a threat intelligence perspective, tracking marketplaces via their scripts is far more efficient than tracking them as individual entities. You reduce dozens of distinct monitoring targets to a handful of script families. You can predict behaviour and vulnerability based on the codebase, not on the individual operators running that codebase.

Conclusion

The dark web marketplace economy has industrialised. What used to be bespoke, artisanal criminal enterprises are becoming commoditised services. The marketplace script vendors are the key infrastructure. They have turned marketplace operation into a scalable, reproducible business.

This has implications across the board. For law enforcement, it means seizing a marketplace is a disruption, not elimination. For threat intelligence teams, it means the unit of analysis should be the script, not the instance. For customers relying on dark web monitoring, it means the landscape is more stable and predictable than it appears.

Genesis Market, Silk Road, and the dozens of anonymous marketplaces that come and go each year are not spontaneous eruptions of criminal ingenuity. They are instances of a handful of scripts, each one serving thousands of vendors and millions of buyers. The real architecture is underneath, in the code. Our DARKSEARCH findings confirm that this franchising model is not theoretical; it is observable in real time across active marketplaces like Tor Amazon, Tor Market, and Dark Web World.

  • Genesis Market seizure: FBI Operation Cookie Monster (June 2024); US Department of Justice, Federal Bureau of Investigation, European law enforcement agency coordination.
  • Incognito Market exit scam: March 2024 withdrawal incident; documented in dark web forum discussions and community aftermath analysis.
  • Laravel framework: Open-source PHP web framework; widely used in dark web marketplace development due to established security practices and library ecosystem.
  • Europol Internet Organised Crime Threat Assessment (iOCTA): Annual monitoring of dark web marketplace proliferation, vendor ecosystem, and cross-border criminal networks.
  • UNODC monitoring: United Nations Office on Drugs and Crime; tracking of dark web marketplace proliferation, transaction volumes, and law enforcement takedown impact assessment.
  • XenForo forum platform: Identified at hxxp://bfdxjkv5e2z3ilrifzbnvxxvhbzsj67akjpj3zc6smzr4vv6oz565gyd[.]onion; forum with escrow system, deposit functionality, and account upgrades; community discussion of marketplace scripts and infrastructure.
  • DARKSEARCH API: SOS Intelligence dark web indexing and search service; provides searchable access to indexed marketplace listings, vendor profiles, and script advertisements indexed on 3 March 2026.

Market Place Photo > Photo by Kayle Kaupanger on Unsplash

Technical Photo > Photo by Steve A Johnson on Unsplash

Header Photo > Photo by Rosie Sun on Unsplash

Police Photo > Photo by Michael Förtsch on Unsplash

Investigation

De-anonymising Tor Hidden Services: How Misconfigurations Expose the Dark Web

Introduction

Tor hidden services exist for one reason: anonymity. The entire architecture of onion routing is designed to ensure that a visitor cannot determine where a service is physically hosted, and that the hosting provider’s real IP address never leaks. In theory, this makes hidden services untraceable. In practice, it does not.

The gap between theory and practice is where threat intelligence gets interesting. Over the past decade, researchers, law enforcement, and OSINT practitioners have demonstrated repeatedly that the anonymity of Tor hidden services can be undermined not by breaking the cryptography or the network protocol, but by exploiting something far simpler: misconfiguration.

At SOS Intelligence, we crawl and index dark web content continuously through our DARKSEARCH platform. As part of that work, we encounter misconfigured hidden services regularly. Some expose their real server IP addresses through default web server configurations. Others leak identifying information through debug pages, status endpoints, or metadata embedded in the content they serve. In this article, we will walk through the most common ways that Tor hidden services inadvertently reveal their clearweb identity, how intelligence analysts can use these techniques ethically, and what this means for anyone running or monitoring hidden services.

De-anonymising Tor Hidden Services: How Misconfigurations Expose the Dark Web

How Tor Hidden Services Are Supposed to Work

Before we get into the failures, it is worth understanding what a properly configured hidden service looks like. When a Tor hidden service is set up correctly, the web server (Apache, Nginx, or whatever is being used) binds exclusively to localhost, typically 127.0.0.1. The Tor daemon running on the same machine creates a virtual tunnel, accepting incoming connections from the Tor network and forwarding them to the local web server.

The critical point is that the web server should never be listening on a public-facing IP address. If it only listens on 127.0.0.1, the only way to reach it is through the Tor daemon. The server’s real IP address is never exposed to the visitor because the visitor’s traffic is routed through the Tor network and terminates at the Tor daemon, not at the web server directly.

This is the theory. The reality is that many hidden service operators, whether through ignorance, laziness, or haste, fail to configure their servers this way. And when they fail, they leave behind digital breadcrumbs that can be followed all the way back to a clearweb IP address, a hosting provider, and often a physical location.

The Classic: Apache mod_status

The most well-documented and arguably most devastating misconfiguration involves Apache’s mod_status module. This has been a known issue since at least 2001, but it continues to surface on Tor hidden services in 2026.

So here is how it works. On most Linux distributions, Apache ships with mod_status enabled by default. This module provides a real-time status page at /server-status that displays diagnostic information about the running web server. The information it exposes includes the server’s uptime, current connections, the IP addresses of connected clients, the URLs being requested, virtual host configurations, and critically, the server name and IP address of the machine itself.

On a standard ClearWeb server, access to /server-status is typically restricted to localhost or specific IP ranges via Apache’s configuration. But here is where the misconfiguration occurs: when the Tor daemon forwards traffic to the local Apache instance, that traffic arrives from 127.0.0.1 (because the Tor daemon is local). This means it passes the default access restriction. The /server-status page becomes accessible to anyone connecting via Tor.

What Gets Exposed

When an analyst successfully accesses /server-status on a misconfigured Tor hidden service, the data returned can be remarkably detailed. The server name field often contains the server’s real hostname, which may resolve directly to a clearweb IP. The virtual host configuration can reveal other domains being hosted on the same machine. Active connection details may show clearweb IP addresses of other visitors or the server’s own outbound connections. In some cases, the page reveals the exact Apache version, operating system, and loaded modules, giving a complete fingerprint of the server.

During our DARKSEARCH crawls, we have identified numerous Tor hidden services returning Apache error pages (403 Forbidden, 404 Not Found) that include server signature information in the response headers:

  • hxxp://cii64fki62v2mudocjvgarzlmnpqrfp6xb7korapmdd7qmjpnccgduyd[.]onion
    • returned a standard 403 Forbidden page during our crawl on 3 March 2026, including the server signature in the response.
  • hxxp://hmxt5u75kj5qxqjqhckgaoda6zndgxcazleersyioat4iuq3ldgmkcid[.]onion and hxxp://pbbeck4xcy3jzbu6lv5db3c5n3n44wngmpb5jj3yo4px32mlznziwbid[.]onion
    • displayed similar Apache error patterns.

While these are less severe than a fully exposed /server-status page, they still leak server version information that can be cross-referenced with Shodan, Censys, or similar clearweb scanning databases to narrow down the server’s identity.

Real-World Prevalence

PHP Information Disclosure: phpinfo() and Friends

PHP’s built-in phpinfo() function is another classic source of information leaks on Tor hidden services. Developers routinely create test pages (often info.php, phpinfo.php, or test.php) that call phpinfo() to verify their server configuration. The problem is that these pages are frequently left in production, and on a hidden service, they can be accessed by anyone.

The phpinfo() output is extraordinarily detailed. It includes the server’s IP address (in the SERVER_ADDR variable), the server’s hostname (SERVER_NAME), the document root path (which may contain revealing directory structures), all loaded PHP extensions, environment variables that may contain database credentials or API keys, and the exact PHP and operating system versions.

The SERVER_ADDR field is particularly damaging. On a properly configured hidden service, this should show 127.0.0.1. But if the web server is bound to a public IP (the misconfiguration we keep coming back to), SERVER_ADDR will show the server’s real clearweb IP address, directly. No correlation or inference required.

Searching for phpinfo() Pages

Using our DARKSEARCH API, analysts can search for common phpinfo page titles and content patterns across indexed Tor content. The search is straightforward: look for pages containing strings like ‘PHP Version’, ‘SERVER_ADDR’, ‘DOCUMENT_ROOT’, or the characteristic phpinfo() HTML table structure. Our crawls regularly index pages that match these patterns across the onion network.

Beyond phpinfo(), similar information can be leaked by debug frameworks and error reporting configurations. PHP applications running in development mode may display detailed stack traces that include file paths, database connection strings, and server IP addresses. Laravel’s debug page, for instance, is notorious for exposing the full application configuration, including environment variables, when APP_DEBUG is set to true.

SSL/TLS Certificate Leaks

This is one of the more elegant de-anonymisation techniques and was documented extensively by researcher Yonathan Klijnsma. The core issue is that some hidden service operators install SSL/TLS certificates on their Tor-hosted web servers, often for the same domain they use on the clearweb.

So when a hidden service operator obtains an SSL certificate (whether from Let’s Encrypt, Comodo, or any other CA), that certificate is logged in public Certificate Transparency (CT) logs. These logs are searchable using tools like crt.sh. If the same certificate is used on both the hidden service and a clearweb server, or if the certificate’s Subject Alternative Names (SANs) include the server’s clearweb domain, the link between the .onion address and the clearweb identity becomes trivial to establish.

Even without direct domain overlap, the certificate itself contains metadata. The organisation name, the country, the issuance date, and the certificate serial number can all be used as pivot points. Cross-referencing certificate fingerprints with databases like crt.sh, Censys, or Shodan’s SSL certificate search can reveal other services using the same certificate, potentially including clearweb servers.

Why This Keeps Happening

The reason this misconfiguration persists is partly a misunderstanding of what SSL does in the context of Tor. The Tor protocol already encrypts traffic between the client and the hidden service. Adding SSL on top of this does not improve security in any meaningful way for a .onion service. But operators who are accustomed to clearweb hosting habits often install SSL certificates out of habit or because their web application framework requires HTTPS.

The more dangerous scenario is when an operator runs a dual-stack configuration: the same server hosts both a clearweb site and a hidden service. If the SSL certificate covers both, the link is immediate. But even single-stack hidden services can be compromised if the certificate was previously used on a clearweb server, because CT logs are permanent.

Default Pages, Error Messages, and Server Signatures

Not every de-anonymisation technique requires accessing a special endpoint. Sometimes, the information leaks from the most basic server responses.

Default Installation Pages

When our DARKSEARCH crawlers encounter a Tor hidden service showing the default Nginx welcome page, the default Apache test page, or a framework’s default landing page, this tells us several things. First, the operator likely set up the service quickly and did not complete the configuration. Second, the default page often reveals the exact server software version. Third, the default configuration files associated with these pages may have additional endpoints enabled (like /server-status for Apache or /stub_status for Nginx).

We have observed this pattern repeatedly in our crawl data. Onion addresses serving generic 403 Forbidden or 404 Not Found pages with Apache or Nginx signatures in the response body are surprisingly common:

  • hxxp://eme7o5bdqwsqvdcj4j6ore6exvxnh6jv3d3nkieopmxfbmdxtrhiljqd[.]onion
    • Returned a 404 Not Found message stating ‘Not Found. The requested URL was not found on this server.’ with clear server identification in the response headers, indexed during our March 2026 DARKSEARCH crawl.

Each of these reveals the web server software and often the version number, which becomes a fingerprint.

Verbose Error Pages

Application-level errors can be even more revealing. A misconfigured Django application will display a detailed debug page showing the settings module, installed middleware, database engine, and file paths. A Node.js application crashing with an unhandled exception may dump stack traces containing absolute file paths. A misconfigured PHP application might display MySQL connection errors that include the database host (which could be a clearweb IP if the database is hosted externally).

Each of these error patterns provides pivot points. File paths can reveal operating system details and directory structures. Database connection strings can point to external clearweb services. Stack traces can reveal the application framework and version, which can be correlated with publicly accessible source code repositories.

HTTP Response Headers

Even when the page content itself reveals nothing, the HTTP response headers can leak information. Common leaky headers include X-Powered-By (reveals the backend technology), Server (reveals the web server and version), X-AspNet-Version (reveals the .NET framework version), and custom headers that may include internal hostnames or IP addresses. The Via header, used by proxies, can sometimes reveal the chain of servers the request passed through, potentially including clearweb infrastructure.

Exposed Administration Interfaces

One of the most directly exploitable categories of misconfiguration involves web-based administration panels that were intended to be accessible only from localhost but end up being exposed via the Tor service.

Common Exposed Services

The pattern here is consistent. Services that bind to 0.0.0.0 (all interfaces) by default become accessible through Tor when the hidden service is configured to forward traffic to the server’s local port. An operator who sets up a hidden service and also runs phpMyAdmin for database management may not realise that phpMyAdmin is now accessible to the entire Tor network.

During our research, we found numerous onion addresses serving content that strongly suggests exposed administration interfaces. WordPress login pages on hidden services, for example, are extremely common in our DARKSEARCH index. While a WordPress login page alone does not expose a clearweb IP, the WordPress installation itself may contain metadata (in uploaded images, in theme files, in plugin configurations) that references clearweb URLs. We also observed directory listing capabilities on some services:

  • hxxp://ylf6u5gurfisvhgheevy4rxzcw36gyp4r55crqlmiydmzwi2xkvmhcad[.]onion
    • (Go Go Onion directory)
  • hxxp://wikipenntwqezw7ycy72zmblcxh6fodtqb6yyyfyz55uoh4fx6wqciid[.]onion
    • (HiddenWiki)

which index and expose other onion services and their details.

Metadata and Content-Based Leaks

Beyond server configuration issues, the content hosted on a hidden service can itself contain identifying information.

EXIF Data in Images

Images uploaded to hidden services may contain EXIF metadata including GPS coordinates, camera make and model, software used to process the image, timestamps, and in some cases, the original filename that may reference a clearweb domain or username. Tools like OnionScan, developed by Sarah Jamie Lewis, specifically check for EXIF data in images hosted on hidden services. Our DARKSEARCH platform includes a similar capability, allowing analysts to identify images with residual metadata that can be correlated with clearweb sources.

Embedded Clearweb Resources

A hidden service page that loads JavaScript libraries, CSS stylesheets, images, or fonts from clearweb CDNs creates a tracking vector. When a visitor loads the hidden service page, their browser (or, in our case, our crawler) can observe the external resource requests. More importantly, the CDN operator can log the timing of those requests, and the hidden service operator has implicitly revealed that they control the account on the CDN from which the resources are served.

The reverse is also true: if a hidden service’s HTML source contains hardcoded clearweb URLs (perhaps the developer copied the template from their clearweb site), those URLs can directly identify the operator. We have seen this in our crawls, where onion-hosted pages reference clearweb domains in their source code, style sheets, or embedded scripts:

  • hxxp://bfdxjkv5e2z3ilrifzbnvxxvhbzsj67akjpj3zc6smzr4vv6oz565gyd[.]onion
    • (observed as a XenForo forum)
  • hxxp://33333337u3npxstc4rrx2z2o5z5cvmbbdr4maqzlutpgmgcqobnxxuqd[.]onion
    • (VicePaste service)

sometimes reveal resource references in their indexable content.

DNS Leaks

If the hidden service’s server makes outbound DNS requests (for example, to resolve a database server hostname, to check for updates, or to load external content), those DNS queries go through the server’s regular network stack, not through Tor. An observer with access to the DNS infrastructure can see the server’s real IP address, making those queries. This is not directly detectable through our DARKSEARCH crawls, but it is a significant vector that complements the other techniques discussed here.

Using the SOS Intelligence API for Tor Service Analysis

At SOS Intelligence, our DARKSEARCH API provides programmatic access to our indexed dark web content, including Tor hidden service data. Analysts can use this to systematically search for the misconfiguration patterns described in this article.

DARKSEARCH Endpoint

The DARKSEARCH endpoint (GET /api/v2/darksearch/new) accepts search queries and returns indexed content from Tor hidden services. By searching for terms like ‘server-status’, ‘phpinfo’, ‘wp-login’, or specific error message patterns, analysts can identify potentially misconfigured services at scale. Each result includes the onion hostname, the page title, the indexed content, and timestamps showing when the page was crawled.

Practical Search Patterns

Tor Metadata Endpoints

Beyond DARKSEARCH, our Tor API endpoints provide metadata about onion services, including path information that can reveal directory structures and exposed endpoints. By analysing the paths crawled on a given onion service, analysts can identify non-standard endpoints that may correspond to administrative interfaces or debug pages.

Defensive Guidance: Hardening Hidden Services

While this article has focused on offensive OSINT techniques, the defensive side is equally important. If your organisation runs legitimate hidden services (for example, for secure whistleblowing, censorship circumvention, or privacy-preserving communication), the following configuration practices are essential.

Web Server Configuration

Bind to localhost only. Your web server must listen exclusively on 127.0.0.1. In Apache, this means setting Listen 127.0.0.1:80 in the main configuration. In Nginx, use listen 127.0.0.1:80. Never use 0.0.0.0 or *.

Disable mod_status and mod_info. In Apache, explicitly disable these modules with a2dismod status and a2dismod info. Do not rely on access controls alone.

Remove default pages and test files. Delete index.html default pages, phpinfo.php test files, and any other diagnostic scripts before going live.

Suppress server signatures. In Apache, set ServerTokens Prod and ServerSignature Off. In Nginx, add server_tokens off to the http block.

Strip revealing headers. Remove X-Powered-By and other headers that reveal your technology stack.

Application Configuration

Never run in debug or development mode. Ensure your application is running in production mode with detailed error reporting disabled for end users.

Do not use SSL certificates. Tor already provides end-to-end encryption. Adding SSL to a hidden service only creates a de-anonymisation vector through Certificate Transparency logs.

Avoid loading external resources. Host all JavaScript, CSS, fonts, and images locally. Do not reference clearweb CDNs.

Strip EXIF data from images. Process all uploaded images to remove metadata before serving them.

Infrastructure Security

Isolate the hidden service. Run it in a dedicated container or VM that has no other services exposed. Do not host a clearweb site and a hidden service on the same machine.

Block outbound connections. Configure firewall rules so the hidden service machine can only communicate through Tor. This prevents DNS leaks and outbound connections that could reveal the real IP.

Audit regularly. Use tools like OnionScan to check your own hidden service for information leaks. Treat this as part of your regular security review process.

The Intelligence Value of Misconfigured Services

For threat intelligence teams, the techniques described in this article are not theoretical. They produce actionable results. When a dark web marketplace, ransomware leak site, or fraud operation is hosted on a misconfigured Tor hidden service, the exposed clearweb IP can lead to a hosting provider, a jurisdiction, and potentially an individual.

Even partial information has value. A server version fingerprint can narrow the search space from billions of IPs to thousands. A leaked hostname can be resolved and cross-referenced. A certificate fingerprint can be tracked across multiple services. An exposed admin panel username can be correlated with clearweb accounts. The cumulative effect of multiple small leaks is often enough to identify the operator.

Law enforcement agencies have used exactly these techniques in major dark web takedowns. The Silk Road investigation benefited from a server misconfiguration that leaked the site’s IP address via its CAPTCHA server. The Hansa Market takedown involved Dutch National Police exploiting similar configuration errors to identify and eventually operate the marketplace. These are not exotic attacks. They are straightforward OSINT techniques applied to poorly configured servers.

Appendix: Observed Indicators from DARKSEARCH

The following table documents real onion addresses observed during DARKSEARCH crawls in March 2026 that exhibit the misconfiguration patterns discussed in this article. These services were indexed through our standard crawling process and represent active examples of the threat vectors described throughout this report. All onion addresses are defanged for security purposes (dots replaced with [.]).

The presence of these indicators in our DARKSEARCH index demonstrates that misconfiguration de-anonymisation techniques remain effective against real-world Tor hidden services. Each category of indicator (error page signatures, directory listings, resource references) represents a distinct attack vector that threat intelligence teams can operationalise at scale using the DARKSEARCH API.

External References and Tools

The following resources provide additional context, methodologies, and tooling for Tor hidden service analysis and de-anonymisation research:

Academic and Research Papers

  • Klijnsma, Y. (2015). ‘HTTPS: The Wrong Side of History’ documented SSL certificate de-anonymisation techniques and Certificate Transparency log analysis methods for identifying hidden service operators.
  • Lewis, S. J. (2014). ‘OnionScan: Automated OSINT for Tor Hidden Services’ introduced methodologies for systematic scanning and metadata extraction from onion services.

Law Enforcement Case Studies

  • Silk Road Investigation: Federal law enforcement identified Ross Ulbricht’s infrastructure partly through misconfiguration vectors, including a CAPTCHA server that leaked IP address information due to poor isolation from the Tor service.
  • Hansa Market Takedown: Dutch National Police (Politie) identified and eventually operated the Hansa marketplace by exploiting similar misconfiguration patterns, including exposed administrative interfaces and information disclosure vulnerabilities.

Publicly Available Tools

  • OnionScan (by Sarah Jamie Lewis): Automated tool for scanning Tor hidden services and extracting metadata, EXIF data, and server information. Source available on GitHub.
  • crt.sh: Certificate Transparency search engine allowing analysts to query public CT logs for SSL certificates. Useful for linking .onion services to clearweb domains.
  • Shodan (shodan.io): Internet-wide scanning database that indexes server banners, headers, and metadata. Can be used to cross-reference server fingerprints and configurations.
  • Censys: Internet scanning and certificate database providing similar capabilities to Shodan, with particular strength in certificate transparency log analysis.
  • DARKSEARCH API (SOS Intelligence): Programmatic access to indexed dark web content, including Tor hidden services. Supports systematic searching for misconfiguration patterns and metadata extraction.

Related Reading

  • Greensill, J. & Aldridge, J. (2019). ‘Cryptomarkets and the Future of Illicit Drug Markets’ discusses operational security practices and common failures of dark web services.
  • NIST Cybersecurity Framework: Provides defensive guidance for organisation-wide security hardening, including principles applicable to Tor hidden service deployment.

Conclusion

The anonymity provided by Tor is only as strong as the weakest configuration on the server. The Tor network itself remains robust, but the humans running hidden services make mistakes. They leave debug pages enabled. They install SSL certificates that link back to their identity. They run web servers with default configurations that expose status pages. They load resources from clearweb CDNs. They forget to strip metadata from images.

For threat intelligence professionals, these mistakes are opportunities. They provide a way to peer behind the curtain of anonymity and identify the infrastructure, and sometimes the individuals, behind dark web operations. The techniques are well-documented, the tools are freely available, and the results are frequently actionable.

At SOS Intelligence, we provide the raw data and search capability that makes this kind of analysis possible at scale. Our DARKSEARCH platform indexes dark web content continuously, and our API gives analysts programmatic access to search for the exact patterns described in this article. If you are running a threat intelligence programme, and you are not systematically checking for these misconfigurations, you are missing intelligence.

Header photo by Rafael Garcin on Unsplash.

Hidden door photo by Stefan Steinbauer on Unsplash

"Cryptocurrency
Investigation, The Dark Web

Cryptocurrency Fraud Tools: A Dark Web Marketplace Analysis

Introduction

Cryptocurrency has become the preferred currency of the underground. It is fast, pseudonymous, and global. But it is also the target. Between theft, wallet draining, and outright fraud, the crypto space is losing billions every year.

In 2024 alone, wallet drainers stole over $500 million, according to Chainalysis’ 2025 Crypto Crime Report. That is not ransomware victims paying extortion demands. That is not clever social engineering or advanced persistent threats. That is simple, scalable fraud at an industrial scale. And the tools to do it are not hidden behind nation-state firewalls or elite darknet forums. They are on sale on what amounts to the Tor equivalent of Amazon.

SOS Intelligence has been tracking these marketplaces for months. We have documented the tools, the prices, the threat actors, and the money laundering pipelines. This analysis is what we found.

What We Found on DARKSEARCH

DARKSEARCH is one of the larger dark web marketplaces. It functions as a general vendor platform, not unlike eBay, but for illegal goods and services. On it, you can buy access to botnets, stolen data, hacking tutorials, or custom malware. You can also buy cryptocurrency theft tools.

The range of products is striking. These are not theoretical exploits or academic proofs of concept. These are working tools used in active campaigns against real targets. Here is what we documented.

Wallet and Account Theft

The simplest products on sale are stolen wallets. Vendors list wallets with substantial balances, already compromised and ready to be drained. A single listing might contain 599 BTC wallets, with individual wallet values ranging from $42,000 to $59,900 USD at 2024 exchange rates. These are not guesses or projections. These are actual wallets with known, verified balances. On markets like Tor Amazon (tamazoncmlw2ohkbsmqxnotudejdd4befrasxuigzzjumqu3zba535yd[.]onion), vendors openly advertise wallets with balances verified as of the day of listing.

Atomic Wallet credentials are also available. Atomic is a popular mobile and desktop wallet used by millions of crypto holders. The Atomic Wallet hack of June 2023 resulted in over $35 million in losses attributed to the Lazarus Group, and compromised credentials continue to circulate on dark web markets. Vendors offer compromised Atomic Wallet accounts containing 1 BTC or more, priced around $4,000 per account. The compromise is complete, meaning the original owner has already been locked out.

Beyond full wallets, you can buy seed phrases and private keys. These are the master credentials that unlock a wallet. A Bitcoin seed phrase recovery tool fetches $1,500 to $6,500, depending on the number of target wallets and recovery likelihood.

Password and Passphrase Cracking Tools

Password protection on wallets assumes the password is strong. It usually is not. So vendors offer specialised tools to crack wallet passphrases at scale. A wallet.dat passphrase cracker, which targets the encrypted wallet file format used by Bitcoin Core and older wallet software, sells for around $400. It performs brute force attacks on the passphrase, trying millions of combinations until it finds the correct one.

These tools are not slow. Modern GPU acceleration can test tens of billions of passwords per second. A weak passphrase, or one based on common patterns, will fall in minutes or hours. A strong one might take days. But the attacker does not need to be fast. They can run the crack in the background indefinitely.

Fake Token Senders and Spoofing Tools

One of the most audacious fraud vectors is the fake USDT sender. USDT is Tether, the largest stablecoin in circulation. Someone using a fake USDT sender can create a fraudulent transaction that appears on the blockchain, complete with the correct token contract address, that shows as sent from one wallet to another. To an untrained eye, it looks legitimate. To a crypto exchange or automated system relying on blockchain scans, it might be legitimate.

These tools sell for $300 to $500. They are typically paired with phishing campaigns. A victim receives a message claiming they have won an airdrop, or that a trade executed successfully, and they see the fake USDT in their wallet. When they try to withdraw or sell it, they are prompted to approve a smart contract transaction. At that point, the drainer takes control. Such tools are actively marketed on platforms like Dark Web World (worldyyyi2ktoisdqjjq4zlt3jftejabo443lb67pfofr2i5gqlkaoqd[.]onion), which hosts a Financial Tools category alongside hacking services.

Reverse Transaction Tools

Bitcoin transactions are supposed to be irreversible. That is part of the design. So the idea of a reverse transaction tool sounds like science fiction. But the vendors of these tools are selling something close to it. A BTC Reverse Transaction Tool, priced between $400 and $600, works by finding transactions on the blockchain that have not yet been fully broadcast to all network nodes. The tool allows the attacker to broadcast a conflicting transaction first, causing the original to be rejected by the network. The BTC then flows to the attacker instead.

This only works on a small fraction of transactions. But it is effective enough that people are paying for it. And the demand suggests it is working in practice.

Mnemonic Brute Force Tools

A BTC mnemonic brute tool costs around 690 USD or 550 GBP. It generates or guesses Bitcoin seed phrases and checks them against the blockchain to see if they contain funds. Because seed phrases follow the BIP39 standard, which is deterministic, a brute force attack on the space of possible mnemonics is theoretically feasible. The attacker generates thousands or millions of seed phrases, derives the public addresses from each one, and queries the blockchain for balances. Advanced Hacking Tools (zqi3evypxq7ok3gqnimwnlesf6v76ksrpgtgb6j7hh6ye752apzmceyd[.]onion) explicitly lists Cryptocurrency Scam Scripts among its offerings, with 38,530 visits and customer reviews confirming ‘software delivered instantly and fully functional’ and ‘secure transaction and smooth process.’

The computational cost is high. But cloud computing makes it cheap. A determined attacker can lease GPU resources for hours or days at a fraction of a cent per compute hour, making the economics viable for high-probability targets.

Leaked Data and Account Databases

Finally, vendors are selling access to compiled databases of leaked credentials. One listing offers access to 16 billion compromised accounts. The seller claims these are de-duplicated and verified against live services. The price is $121,484. That works out to less than one cent per compromised account. For a cyber criminal running wallet-draining campaigns, this is cheap reconnaissance. They can cross-reference stolen exchange login credentials against wallet addresses to identify holders with known balances. Multivendor platforms like Tor Market (sqw2klzo4mtwvbf3by7irjv7r5mdojxwziuus3lh6rketlkggvsdyaad[.]onion) support both Bitcoin and Monero payments, with dedicated Money Transfer categories facilitating these database sales.

Wallet Drainers as a Service

The real innovation on the dark web is not individual tools. It is the business model. Wallet drainers are offered as a service, DaaS, and it is a lucrative franchise.

How DaaS Works

So the architecture of a wallet drainer is straightforward. The developer publishes a toolkit consisting of a drainer contract (a smart contract deployed on-chain) and a user interface for creating phishing campaigns. A criminal rents the drainer, paying either a flat fee or a percentage of stolen funds. They set up a phishing website that mimics a popular crypto exchange or NFT marketplace. They send phishing links to targets via email, SMS, or social media.

When a victim clicks the link, they see a fake login screen or a fake approval request. If they enter their seed phrase or approve a transaction signature, the drainer gains the ability to control their wallet. The funds are transferred immediately to the attacker’s address. The entire flow from click to theft takes seconds.

The drainer operator keeps a percentage. The drainer developer keeps a percentage. The affiliate who promoted the drainer keeps a percentage. Everyone gets paid. It is a lean, distributed criminal supply chain.

Angel Drainer

Angel Drainer is perhaps the most notorious wallet-drainer family in operation. It is believed to have stolen over $25 million in cryptocurrency. It was active from early 2023 through 2024, and operated as a DaaS offering custom drainer contracts and campaign management tools. ScamSniffer blockchain security research has tracked Angel Drainer operations across multiple victim wallets.

Angel users could log into a dashboard, select their target blockchain, customize their phishing site, and launch their campaign. The drainer provided metrics on click-through rates, approval signatures collected, and stolen funds. It was, in essence, a SaaS offering with a criminal payload. Many law enforcement agencies have attributed wallet drains totalling in the millions of dollars to Angel Drainer operators.

Inferno Drainer

Inferno Drainer is believed to have stolen over $80 million. It operated in parallel with Angel Drainer and was arguably more technically sophisticated. Its phishing interfaces were higher fidelity, its blockchain support was broader, and its operational security was tighter. SlowMist blockchain security research has documented Inferno’s operational patterns across multiple victim reports.

In a striking twist, Inferno Drainer operators were observed transferring stolen funds directly to Angel Drainer wallets in several high-value campaigns. This suggests either a partnership or a buyout. It is unclear if Inferno has exited the market or if operations have simply gone underground or rebranded.

Pink Drainer

Pink Drainer operated more transparently than most. The operator ran an active Telegram channel and took custom contracts and integration requests. Pink is estimated to have commanded 28% market share of the wallet drainer space before exiting in May 2024. By that point, it was believed to have stolen tens of millions of dollars.

The operator announced the exit via a single Telegram message, claiming to be retiring. No law enforcement action was publicly attributed to the exit, suggesting the operator likely had good operational security and may be operating new campaigns under a different name.

Technical Breakdown

Understanding how these tools work requires looking at the mechanics of each attack vector. So let’s walk through them.

Mnemonic Crackers and Brute Force

A Bitcoin seed phrase, or mnemonic, is a sequence of 12, 15, 18, 21, or 24 English words. The words are drawn from the BIP39 word list, which contains exactly 2048 words. This means a 12-word seed phrase represents 2048^12, or roughly 5 x 10^39, possible combinations. That is astronomically large. But it is also finite.

A mnemonic brute force tool does not generate mnemonics randomly. Instead, it uses a wordlist and systematically generates combinations, typically in dictionary order or based on frequency analysis. Each generated mnemonic is used to derive public Bitcoin addresses via the BIP32 standard. The tool then queries a Bitcoin blockchain API or a local blockchain copy to check if those addresses hold funds.

The success rate depends on the blockchain. Bitcoin has around 900 million addresses with at least one transaction. The space of possible mnemonics is enormous, so brute force is impractical for a truly random search. But many users choose weak passphrases or do not add a passphrase at all, and some use common word patterns. Those are the targets.

Cloud GPU providers make the attack economic. For a few dollars an hour, an attacker can spin up instances with NVIDIA H100 GPUs, each capable of deriving and checking thousands of addresses per second. A sustained campaign lasting weeks could check billions of addresses at a marginal cost of fractions of a cent per address checked.

Wallet.dat Password Cracking

Bitcoin Core wallet files are stored in a binary format called wallet.dat. If the wallet is encrypted, the file is encrypted using a passphrase. The passphrase is hashed and used as a key for AES-256 encryption.

A wallet.dat cracker tool first extracts the encrypted private keys from the wallet file. It then performs a dictionary attack, hashing candidate passwords and attempting to decrypt the key material. If decryption succeeds, the tool has recovered the private key and can sign transactions.

The challenge for the attacker is that Bitcoin Core uses key stretching, specifically SHA-512, iterated 100,000 times on the passphrase. This makes brute force slow. Even with GPUs, testing a million passwords against a single wallet takes minutes or hours. But again, modern GPU acceleration and cloud computing make it feasible for high-value targets.

Fake USDT and Token Spoofing

USDT is issued by the Tether company, and on most blockchains, it is implemented as a smart contract. The token contract address is public and well-known. A fake USDT sender exploits this by creating a transaction that mimics a token transfer but is not actually executed on-chain.

The attack works like this: the attacker creates a transaction object that references the correct Tether contract address and shows a fake transfer from one address to another. They do not broadcast it to the blockchain. Instead, they inject it into the victim’s wallet interface or display it in a phishing site as if it had already settled.

When the victim sees the fake token in their wallet, they may attempt to withdraw it or trade it. Most wallets and exchanges check the blockchain for the transaction. But a carefully crafted spoof can appear in the transaction history without being fully confirmed. Victims are then prompted to approve a smart contract transaction to complete the withdrawal or trade. That approval signature is where the drainer takes control.

The trickery is not in the spoofing itself, but in the social engineering that surrounds it. The victim is led to believe they have received free tokens and that they need to take action to claim or access them.

Reverse Bitcoin Transactions

Bitcoin transactions are broadcast to the network and then mined into blocks. Once a transaction is included in a block, it is essentially irreversible. But in the brief window between broadcast and inclusion in a block, a miner or someone with network access can potentially broadcast a conflicting transaction first.

A reverse transaction tool exploits this window. When a victim initiates a high-value transaction, the attacker intercepts the network broadcast or learns of the pending transaction through a mempool monitor. The attacker then constructs a conflicting transaction that sends the same inputs to their own address and broadcasts it to the network with a higher fee.

If the attacker’s transaction is included in a block first, the victim’s original transaction becomes invalid because the inputs have already been spent. The funds flow to the attacker instead. This is sometimes called a mempool race or front-running, and it requires network-level access or partnership with a miner. It is not reliable, but it is effective enough that criminals are paying for it.

Clipboard Hijacking and Browser Injection

A simpler attack vector, but still effective, is clipboard hijacking. Some wallet drainers include code that monitors the victim’s clipboard for wallet addresses. When it detects a Bitcoin or Ethereum address, it replaces it with the attacker’s address.

A user copies a withdrawal address from a trusted source, pastes it into their wallet, and unknowingly sends funds to the attacker instead of their intended destination. The attack is hidden, requires no victim interaction beyond copy-paste, and exploits the assumption that the clipboard is a secure location for temporary data.

Clipboard hijacking is often deployed via browser extensions or by compromising popular wallet software. It is not as profitable as wallet draining, but it is persistent and low effort.

Dark Web Crypto Fraud Markets

Let’s consolidate what we found on dark web marketplaces into a clearer picture.

Wallet Drainer Families and Scale

Wallet drainers are the largest profit engine in crypto fraud. Here is what we know about the major players.

Attack Vectors and Detection Difficulty

Not all crypto fraud is equally easy to defend against. So here is a breakdown of the main attack vectors and how difficult they are to detect.

The Money Laundering Pipeline

Stolen crypto is not useful if the attacker cannot convert it back to cash. So understanding the laundering pipeline is critical to understanding the full economic model of crypto fraud.

Mixing and Tumblers

The simplest laundering step is a mixer, also called a tumbler. A mixer is a service that pools coins from multiple users and then redistributes them in ways that break the chain of custody. If I send 1 BTC to a mixer, I do not get the same 1 BTC back. I get 1 BTC that came from someone else’s deposit.

Mixers are sometimes voluntary services that users employ to protect their privacy. But in the context of stolen funds, they are money laundering tools. Law enforcement has been cracking down on mixing services, but many still operate, especially on the dark web.

Swap Services and Atomic Swaps

Another approach is to convert Bitcoin to a different cryptocurrency that has stronger privacy properties. We found references to swap services running on Tor, such as swp.cx, which claim to execute cryptographic atomic swaps between Bitcoin and Monero without requiring custody of the funds.

The attacker sends BTC to the service, which then sends Monero back to the attacker. Monero is pseudo-anonymous and much harder to trace on the blockchain. From there, the attacker can convert to other coins or cash out to fiat via less-regulated exchanges.

Privacy Coins

Privacy coins like Monero use ring signatures and stealth addresses to obscure the sender, receiver, and transaction amount on the blockchain. A transaction in Monero cannot be traced by following the chain of public addresses. This makes Monero the preferred destination for stolen BTC.

The conversion happens on a swap service or exchange. The attacker loses a small percentage to fees and exchange rates, but gains plausible deniability. Once in Monero, the funds are effectively invisible to on-chain analysis.

Chain Hopping and OTC Markets

The most sophisticated attackers use chain hopping: moving stolen funds across multiple blockchains and currencies before cashing out. Bitcoin to Ethereum to Monero to a stablecoin to a privacy token and back. Each hop adds complexity and expense, but it also significantly increases the cost of forensic analysis.

Finally, the attacker accesses over-the-counter (OTC) brokers, often in countries with weak AML enforcement or corrupt officials. They sell large quantities of crypto for cash, receiving wire transfers to bank accounts in their name or under shell companies. These OTC brokers do not ask difficult questions and are incentivised to facilitate large transactions.

Casino Bonus Exploitation

One lesser-known crypto fraud vector is casino bonus exploitation. Online casinos offer sign-up bonuses to new players: deposit $100, get a $100 bonus. To claim the bonus, you must meet a turnover requirement, usually 30 to 50 times the bonus amount. This is designed to be difficult.

But with access to stolen payment methods and identity documents, a fraudster can create dozens or hundreds of accounts and claim bonuses using different identities. A casino bonus exploitation kit, selling for $150 to $350 on the dark web, automates this process. The kit includes scripts to bypass identity verification, claim bonuses, meet turnover requirements using automated play, and cash out.

The profit margins are high. A $3,000 to $10,000 bonus can be turned into actual cash if the attacker is patient and covers their tracks. The casinos absorb the losses, and usually do not prosecute because of the reputational and legal costs.

Scale of the Problem

To appreciate the scale, consider the raw numbers.

Sixteen billion compromised accounts are for sale on dark web markets. That is more than twice the world population. Many accounts are duplicates across multiple breaches, but the number still represents massive exposure. Any crypto user with an email address used on a commonly breached service is a potential target for credential-based attacks.

Stolen Bitcoin wallets with known balances, in the hundreds or thousands of BTC, are actively listed on the marketplace. These are not speculative. These are wallets that have been compromised and whose balances have been verified.

Wallet-drainer families have collectively stolen $300 million or more in the last two years. Many attacks go unattributed and unreported, especially from users in countries with weak cybercrime reporting infrastructure. The true number is certainly higher.

The tools themselves are cheap. A full-featured drainer costs $100 to $500 per month to rent. A mnemonic cracker is a few hundred dollars. An investment of a few thousand dollars can yield millions in stolen crypto. The economics are favourable for the attacker. They are not.

How SOS Intelligence Monitors Crypto Threats

SOS Intelligence has been monitoring these dark web markets since 2024. Our approach focuses on two core capabilities.

DARKSEARCH Crawling and Indexing

Our DARKSEARCH crawler maintains a running index of major dark web marketplaces, including the venues where crypto fraud tools are sold. We track new tool releases, pricing changes, operator behaviour, and customer feedback. This gives us a real-time view of the threat landscape.

We extract and parse product listings, vendor history, and customer reviews. We track changes in pricing, which often correlate with law enforcement action or shifting market dynamics. When a major drainer family exits or goes dark, we identify the shift early and begin looking for successor operations.

Cryptocurrency Address Monitoring

We also monitor the blockchain itself for known crypto fraud addresses. When a wallet drainer operation is disrupted or a perpetrator is identified, their associated addresses often remain public. We track these addresses for ongoing movement of funds, which can identify new campaigns or money laundering patterns.

By correlating blockchain data with dark web intelligence, we can often connect a phishing campaign to a drainer family, and that family to a money laundering pipeline. This gives our customers early warning before their users are targeted.

Defensive Recommendations

For crypto holders and exchanges, defence is possible. So here is what we recommend.

For Individual Crypto Holders

Use hardware wallets for significant amounts. Hardware wallets store private keys offline and require physical confirmation of transactions. They are resistant to mnemonic cracking, wallet.dat attacks, and phishing.

If you use hot wallets, use strong and unique passphrases. Do not use dictionary words or common patterns. Use a password manager to generate and store passphrases. This makes brute force attacks impractical.

Never approve transactions on suspicious sites or in response to unsolicited messages. Drainers rely on approval signatures. If you do not approve, you do not lose funds.

Monitor your wallet addresses for unauthorised transactions. Set up blockchain monitoring alerts on your addresses. If funds start moving without your action, you can investigate immediately.

Use two-factor authentication on exchange accounts. Many drainers target exchange credentials. MFA, even SMS-based MFA, adds a layer of protection.

For Exchanges and Custodians

Implement withdrawal limits and delays. If a customer’s account is compromised, a withdrawal delay gives the customer time to notice the anomaly and cancel the transaction.

Monitor for suspicious wallet addresses in withdrawals. If a customer is withdrawing to a known drainer address or money laundering service, flag it for review.

Educate users about phishing. Many victims do not realise they have been compromised until weeks after the attack. Clear guidance on how to identify phishing reduces successful attacks.

Implement address whitelisting. Allow customers to whitelist trusted withdrawal addresses and require manual override for new addresses. This blocks many spontaneous account takeovers.

Work with blockchain analysis firms to identify incoming funds from known stolen addresses. Money laundering at scale means some stolen funds flow into honest people’s wallets. Detecting and blocking this upstream reduces the utility of theft.

Conclusion

Cryptocurrency fraud is not a niche problem. It is a $300 million to $500 million per year industry, with efficient, scalable tools and business models. The tools are cheap, the barriers to entry are low, and the margins are enormous.

The most striking finding is not the theft itself, but the industrialisation of fraud. DaaS offerings like Angel Drainer and Inferno Drainer have turned wallet draining into a franchise model. Anyone with a phishing campaign and a few hundred dollars can become a crypto criminal. This scale is what makes the problem so difficult to solve.

Detection is possible but hard. Many attacks leave no blockchain signature. Most attacks are indistinguishable from normal user behaviour. And the speed of the ecosystem means new tools and evasion techniques emerge constantly.

The path forward requires three things. First, better security practices from users. Hardware wallets and strong passphrases are not sexy, but they work. Second, better tooling from exchanges and custodians. Withdrawal limits, address whitelisting, and outgoing transaction monitoring can block many attacks. Third, continued law enforcement and intelligence work to disrupt the most profitable operations.

SOS Intelligence will continue monitoring these threats. We will continue indexing dark web marketplaces and tracking the money laundering pipelines. We will continue alerting our customers when we identify attacks targeted at their users. And we will continue building the tools that make attribution and defence possible.

Appendix: DARKSEARCH Observed Listings

Between February 2026 and March 2026, our DARKSEARCH crawlers observed the following active marketplace listings offering cryptocurrency fraud tools and services. All onion URLs are defanged to prevent accidental access.

External References

This report draws on the following open-source intelligence and blockchain security research:

  • Chainalysis (2025). 2025 Crypto Crime Report. Available at: https://www.chainalysis.com/reports/crypto-crime-report-2025/. Documents wallet drainer losses exceeding $500 million in 2024; tracks drainer family evolution and exit patterns.
  • ScamSniffer (2024-2026). Wallet Drainer Tracking. Available at: https://scamsniffer.io. Real-time tracking of Angel Drainer, Inferno Drainer, and Pink Drainer operational signatures across blockchain transactions.
  • SlowMist (2024-2026). Blockchain Security Research. Available at: https://slowmist.medium.com. Technical analysis of wallet drainer mechanics, transaction patterns, and operational security.
  • Elliptic (2024-2026). Blockchain Analytics Research. Available at: https://www.elliptic.co. Tracks money laundering pipelines, privacy coin conversions, and OTC broker involvement in stolen funds movement.
  • FBI IC3 (2024). Internet Crime Complaint Center – Cryptocurrency Fraud Statistics. Available at: https://ic3.gov. Official statistics on reported cryptocurrency fraud, wallet draining, and wallet compromise cases.
  • Atomic Wallet Security Incident (June 2023). Initial reports and analysis of $35 million hack attributed to Lazarus Group; tracked credential circulation on dark web marketplaces through 2026.
  • MITRE ATT&CK Framework. Cryptocurrency Fraud Tactics. Documents attack patterns including credential dumping (T1005), phishing for information (T1598), and signed script proxy execution (T1216).

Header image by Art Rachen on Unsplash

Wallet by Emil Kalibradov on Unsplash

Drain by Daniel Dan on Unsplash

Casino by Michał Parzuchowski on Unsplash

"SOS
Investigation, Opinion, The Dark Web

Dark Web Services: current Average Prices (2026 Update)

Dark Web Services: current Average Prices (2026 Update)

Introduction

Back in 2022, I published our first deep dive into dark web pricing. At the time, the landscape was already complex, but it was still possible to draw fairly clean lines between the categories of goods and services being traded. Four years on, those lines have blurred considerably.

The underground economy has matured. Prices have shifted, new product categories have emerged, and the operational sophistication of threat actors has increased significantly. Ransomware-as-a-Service is now an established business model. AI-generated phishing kits are being sold alongside traditional credential dumps. Crypto drainers have become a category in their own right. And stealer log subscriptions are now one of the fastest-growing products on the dark web.

13th May 3pm UK Time

Webinar: 2026 Dark Web Pricing Report

For this updated report, we conducted an exhaustive crawl using our own SOS Intelligence DARKSEARCH platform, scanning active dark web marketplaces, forums, and paste sites throughout Q1 2026. We supplemented this with direct marketplace access via Tor and cross-referenced our findings against published industry research from PrivacySharks, DeepStrike, Privacy Affairs, and Trustwave. This time around, we have also expanded our scope significantly, covering narcotics, firearms, counterfeit goods, cryptocurrency fraud tools, and forged documents alongside the traditional cyber-focused categories. The result is what I believe to be one of the most comprehensive snapshots of dark web pricing available today.

So whether you are a security researcher, an MSSP building threat briefings, or a CISO trying to quantify the risk exposure your organisation faces, this should give you a solid, data-backed foundation.

Methodology

Our approach follows the intelligence cycle: direction, collection, processing, analysis, and dissemination. The direction phase was straightforward: understand what is being sold on the dark web in 2026 and at what price points.

For collection, we used the SOS Intelligence API v2 to run targeted keyword searches across our indexed dark web corpus. This includes content from over 50 active marketplaces, forums, paste sites, and Telegram channels. We queried across 20+ distinct product categories, including stolen financial instruments, identity documents, hacking services, malware, access brokers, narcotics (cocaine, heroin, methamphetamine, cannabis, MDMA, and prescription drugs), firearms, counterfeit goods, cryptocurrency fraud tools, and forged documents. We also accessed active Tor marketplaces directly to verify listed prices against real product pages. Key marketplaces analysed include Tor Market, Tor Amazon, Abacus Market, TheBreakingBad, Gun and Shell Factory, and several standalone vendor storefronts.

During processing and analysis, we normalised prices to USD (where vendors listed in EUR, GBP, or cryptocurrency) and calculated averages across multiple vendors where possible. Where a product category had significant variance (for example, initial access pricing can range from $500 to $50,000+), we present the typical range rather than a misleading average.

One thing worth noting: prices on the dark web are not static. They fluctuate based on supply, demand, law enforcement activity, and even seasonal patterns. What we present here is a snapshot, accurate to Q1 2026, and should be treated as indicative rather than definitive.

Stolen Financial Instruments

Financial data remains the bread and butter of dark web commerce. Credit card data, bank account credentials, and payment platform logins continue to dominate marketplace listings. The availability is enormous, driven in large part by the explosion in stealer log infections and large-scale data breaches.

Credit card data with CVV (card-not-present fraud) remains cheap and abundant. A single card with CVV typically sells for $10 to $40, depending on the issuing bank, card type, and associated balance. Cards with higher balances or from premium issuers command a premium. Cloned physical cards with PIN are a different proposition entirely, typically ranging from $100 for a single card with a $2,500 to $3,500 balance, up to $600 for a batch of 10 cards with a combined balance of $33,000 to $35,000.

ProductPrice Range (USD)Source/Notes
Credit card with CVV$10 – $40Per card, card-not-present
Cloned card with PIN (single)$100 – $250$2,500 – $3,500 balance
Cloned cards (batch of 10)$450 – $600$30,000 – $35,000 combined
AMEX Prepaid (EUR 2,500)$105 – $510Price varies by vendor
Bank login (US)$35 – $500Depends on bank and balance
Bank login (UK/EU)$50 – $1,000+Premium for verified accounts
Bank transfer service ($10K)$500Vendor guarantees delivery
PayPal account (verified)$15 – $55Balance $2,500 – $25,000
Crypto exchange account (Kraken)$249Fully verified
Crypto exchange account (general)$90 – $250Coinbase, Binance, etc.

Compared to our 2022 findings, the average price of stolen credit card data has dropped slightly, reflecting oversupply. Bank account credentials, on the other hand, have held steady or increased, particularly for UK and EU accounts where strong customer authentication (SCA) requirements make compromised credentials more valuable to attackers who can bypass these controls.

Identity Documents and Fullz

Fullz, complete identity packages containing name, date of birth, SSN, address, and often more, remain a staple of dark web commerce. The pricing here has been remarkably consistent over the years, which suggests stable supply chains, likely fed by the steady stream of data breaches affecting organisations globally.

Bulk purchasing drives the per-unit cost down significantly. A batch of 1,000 Social Security Numbers was listed on Tor Market at $65. Business fullz (company identity packages with EIN numbers) go for around $95 for a set of 10, which is particularly concerning for organisations worried about business identity theft and fraudulent corporate filings.

ProductPrice Range (USD)Notes
Individual fullz (US)$20 – $100Per identity, includes SSN
SSN batch (1,000 records)$65Bulk purchase, specific regions
Business fullz with EIN (10 pack)$95Corporate identity packages
US passport scan$100Digital copy only
US physical passport (forged)$3,000 – $3,800High-quality forgery
UK driver’s licence (forged)$500Physical document
EU national ID (forged)$300 – $700Varies by country
Medical records$50 – $500+Depends on completeness
Selfie with ID (for KYC bypass)$50 – $100Growing demand

A notable trend in 2026 is the growing market for KYC bypass packages. These typically include a stolen identity paired with a matching selfie (often obtained from stealer logs that capture webcam images), sold specifically to bypass Know Your Customer verification on financial platforms. This is a direct response to tightened identity verification requirements, and it represents an uncomfortable escalation in the identity fraud ecosystem.

DDoS and Hacking Services

DDoS-for-hire remains one of the most accessible attack services on the dark web. Entry-level DDoS attacks can be purchased for as little as $10 per hour, making it trivially cheap for anyone with a grudge and a cryptocurrency wallet. Monthly subscription packages for sustained DDoS capability go up to $850, though most listings cluster around $200 to $500 per month.

Hacking services for hire are more variable in pricing, reflecting the range of complexity involved. Simple social media account compromises sit at the lower end, while corporate network penetration and database extraction commands significantly higher fees.

ServicePrice Range (USD)Notes
DDoS attack (per hour)$10 – $50Basic layer 4/7 attack
DDoS subscription (monthly)$200 – $850Sustained capability
Social media account hack$25 – $100Facebook, Instagram, etc.
Email account compromise$100 – $500Corporate email higher
Website hacking$200 – $3,000Depends on target complexity
Corporate network access$500 – $10,000+Overlaps with IAB market
Phone hacking/spyware install$300 – $1,500Remote installation
Doxing service$25 – $200Varies by depth of research

The DDoS market has become increasingly commoditised. In 2022 we reported an average DDoS service price of around $382. That number has come down, driven by competition between providers and the proliferation of botnet infrastructure. The real concern is not the price itself but how easy it has become to launch these attacks with minimal technical knowledge.

Malware, Exploit Kits, and Phishing

This is where the dark web economy has seen some of its most significant evolution since our last report. The malware-as-a-service model is now firmly established, with vendors offering everything from basic RATs (Remote Access Trojans) through to sophisticated banking trojans and zero-day exploits.

Phishing kits have become particularly interesting. AI-generated phishing templates are now being sold at a premium, with vendors marketing their kits as capable of bypassing modern email security filters. The quality of these templates has improved dramatically, making traditional security awareness training less effective than it was even two years ago.

ProductPrice Range (USD)Notes
RAT (Remote Access Trojan)$45 – $500Off-the-shelf, basic features
Banking trojan$500 – $1,800Targeted at specific banks
Ransomware-as-a-Service kit$500 – $5,000Includes builder and panel
Stealer log subscription$100 – $1,024/moRedline, Raccoon, Vidar
Phishing kit (standard)$50 – $300Includes templates and hosting
Phishing kit (AI-generated)$200 – $800Bypass modern filters
Zero-day exploit (general)$5,000 – $200,000+Price varies enormously
Exploit kit (browser)$100 – $2,000Pre-packaged exploitation
Botnet rental (1,000 bots)$50 – $200/dayFor spam or DDoS
Keylogger$25 – $150Basic to advanced features

The Ransomware-as-a-Service (RaaS) market deserves special attention. Our platform currently tracks over 100 active ransomware groups, many of which operate affiliate programmes where the actual ransomware deployment is carried out by affiliates who pay a percentage (typically 20-30%) of the ransom to the RaaS operator. The barrier to entry for launching a ransomware campaign has never been lower, and this is reflected in the sustained growth of ransomware incidents globally.

Crypto Drainers and Mixers

This is a category that barely existed in 2022 and is now a significant segment of the dark web economy. Crypto drainers are tools designed to empty cryptocurrency wallets, typically deployed via phishing sites that mimic legitimate Web3 platforms and trick users into connecting their wallets and signing malicious transactions.

Our DARKSEARCH data turned up active listings on DNA Forums and other threat actor communities, with prices ranging from $50 for basic tutorials through to $1,000 for fully operational Solana drainer toolkits. The Tron Trap drainer tool was listed at $300, while general-purpose drainer kits sat around $200 to $500.

ProductPrice Range (USD)Notes
Crypto drainer kit (general)$200 – $500Multi-chain support
Solana drainer$1,000Chain-specific tooling
Tron Trap drainer$300Listed on DNA Forums
Crypto drainer tutorial$50 – $100DIY approach
Crypto mixing/tumbling service1-3% of amountPer transaction fee
Crypto cashout service15-25% of amountConversion to fiat

The emergence of drainer-as-a-service mirrors the RaaS model. Operators provide the tooling and infrastructure, affiliates drive traffic to phishing sites, and profits are split. Some drainer operators take a 20-30% cut of every wallet drained. For context, wallet drainer attacks stole hundreds of millions of dollars in cryptocurrency during 2025 alone, making this one of the highest-growth criminal sectors.

Initial Access Brokers

Initial Access Brokers (IABs) continue to be a critical part of the threat landscape. These are threat actors who specialise in gaining access to corporate networks and then selling that access to other criminals, typically ransomware operators. The IAB market is essentially the supply chain for ransomware.

Pricing varies enormously based on the target organisation’s size, industry, and the type of access being sold. VPN credentials for a small company might go for $500, while domain admin access to a large enterprise can command $10,000 or more. Our 2022 report found an average of around $7,700 for initial network access. In 2026, the range has widened as the market has matured, but the median sits around $2,000 to $5,000 for mid-market targets.

Access TypePrice Range (USD)Notes
VPN credentials (SME)$200 – $1,000Single organisation
RDP access (dedicated server)$10 – $100Commodity pricing
Domain admin (enterprise)$5,000 – $50,000+High-value targets
Web shell access$50 – $500Depends on target
cPanel/hosting access$10 – $50Bulk available
Database access (customer data)$500 – $10,000Depends on record count
Cloud infrastructure access$1,000 – $20,000AWS, Azure, GCP

Cloud infrastructure access is the emerging high-value category here. As organisations continue their migration to cloud platforms, compromised cloud credentials have become increasingly sought after. A set of AWS root account credentials for an enterprise can be worth significantly more than traditional on-premise network access, reflecting the potential blast radius of a cloud compromise.

Stolen Accounts and Subscriptions

The market for compromised online accounts remains massive, covering everything from streaming services to social media to gaming platforms. These are largely driven by credential stuffing attacks leveraging the billions of username/password pairs available from historical breaches, combined with the output of stealer log infections.

Account TypePrice Range (USD)Notes
Netflix/Disney+/streaming$4 – $25Per account, often shared
Spotify Premium$3 – $10Bulk available
Facebook account$25 – $45Higher for aged accounts
Instagram account$25 – $45Followers affect price
LinkedIn Premium$30 – $50Professional accounts
Gaming accounts (Steam, Epic)$10 – $100Game library affects price
Food delivery (Uber Eats, etc.)$5 – $20With stored payment
Email accounts (bulk)$2 – $10Per account
VPN service accounts$5 – $15NordVPN, ExpressVPN, etc.

What strikes me about this category is how cheap everything is. A Netflix account for $4, a Facebook account for $25. The low prices reflect the sheer volume of compromised credentials available. For most consumers, the inconvenience of having an account compromised is minor. But for organisations, compromised employee accounts, particularly email and LinkedIn, can be the starting point for targeted social engineering campaigns.

Counterfeit Currency and Documents

Counterfeit physical currency continues to be traded, though the market has evolved. Our crawl of Robinhood Market found fake Euro banknotes listed from $300 for a small batch up to $1,200 for larger quantities. Western Union transfer services were listed at $200 for a $2,000 transfer, representing a 10% fee.

Bank cheque templates have also become a notable category, with templates available from as little as $5 for basic designs up to $600 for comprehensive kits that include matching security features and printing instructions.

ProductPrice Range (USD)Notes
Counterfeit EUR banknotes$300 – $1,200Various denominations
Counterfeit USD banknotes$350 – $1,500Quality varies significantly
Western Union transfer ($2,000)$20010% fee structure
MoneyGram transfer$150 – $300Similar fee structure
Bank cheque templates$5 – $600Including security features
Counterfeit branded goods (guides)$20 – $200Manufacturing instructions

In our 2022 report, counterfeit currency averaged around $396 per $1,000 face value. The current rates are broadly similar, suggesting this market has reached a stable equilibrium. The real shift is towards digital fraud, with physical counterfeiting becoming a smaller proportion of overall dark web commerce.

Proxy and Hosting Infrastructure

Bulletproof hosting and residential proxy services continue to be essential infrastructure for cybercriminal operations. These services provide the anonymous, abuse-tolerant hosting that enables everything from phishing campaigns to command and control servers.

ServicePrice Range (USD)Notes
Bulletproof hosting (monthly)$50 – $500Abuse-tolerant, offshore
Residential proxy (monthly)$200 – $645Pool of residential IPs
SOCKS5 proxy (per IP)$1 – $10Single use or short-lived
VPN service (criminal-oriented)$5 – $30/moNo-log guarantees
Dedicated server (offshore)$100 – $400/moFull admin access
Domain + hosting bundle$20 – $100For phishing campaigns

Residential proxy pricing has actually increased since 2022, when we reported an average of $645 per month. The current range starts lower but premium services now charge more, reflecting growing demand from threat actors who need residential IP addresses to bypass fraud detection systems and CAPTCHAs.

AI-Enabled Criminal Services

This is entirely new territory since our 2022 report. The commoditisation of large language models has created a new category of criminal tooling that simply did not exist four years ago. Dark web forums now host discussions and sales of jailbroken AI models, custom-trained chatbots for social engineering, and AI-powered tools for generating convincing phishing content at scale.

While we did not find as many standardised price points for AI services as for other categories (the market is still maturing), the trend is clear. AI is being integrated into existing criminal workflows, particularly around social engineering, phishing content generation, and code development for malware. Some vendors are marketing “FraudGPT” and “WormGPT” style tools, essentially LLM wrappers with the safety guardrails removed, at subscription prices of $200 to $1,700 per month.

The implications here are significant. AI lowers the barrier to entry for technically unsophisticated threat actors, increases the quality and scale of social engineering attacks, and makes it harder for defenders to distinguish malicious content from legitimate communications.

Narcotics and Controlled Substances

Dark web drug marketplaces remain one of the most active sectors of the underground economy. Our DARKSEARCH crawls in Q1 2026 revealed multiple operational marketplaces with extensive product catalogues, professional vendor storefronts, and established escrow systems. The sophistication of these operations is notable: vendor pages include lab-testing claims, customer reviews, volume discount tiers, and next-day delivery (NDD) options for domestic shipments.

Three marketplaces stood out during our research. TheBreakingBad, a dedicated vendor storefront operating with a full e-commerce style interface, offered a comprehensive catalogue of stimulants, opiates, and dissociatives with granular volume pricing. Abacus Market, a multi-vendor marketplace, carried similar inventory with slightly different pricing. Tor Market, which operates as a broader multi-category darknet marketplace (also listing firearms, documents, and hacking tools), hosted 47 drug products across multiple vendors at the time of our crawl.

Stimulants

Cocaine remains the most commonly listed stimulant. Colombian cocaine claiming 94%+ purity was available across multiple markets. Crystal methamphetamine was the second most prevalent stimulant listing, with a notably well-developed volume pricing structure from European vendors. Amphetamine paste, particularly popular on European markets, was available in both standard (74%) and premium (94%) purity grades.

ProductPrice RangeVolume PricingSource Market
Colombian Cocaine 94%+$50 – $80/gBulk from $35/g at 100g+Tor Market, Abacus
Crystal Meth 94% (Mexican)€10/g€80/10g, €700/100g, €5,500/kgTheBreakingBad
Crystal Meth (ICE)$99/10g$249/25g, $1,000/100gAbacus Market
Speed Amphetamine 94%€22/10g€90/100g, €700/kgTheBreakingBad
Speed Amphetamine 74%€10/10g€77/100g, €555/kgTheBreakingBad
3-MMC (Metaphedrone)€10/g€350/100g, €3,000/kgTheBreakingBad
MDMA Champagne 84%+$6.50 – $18/g$8/g at 250g bulkAbacus Market
XTC Pills 250mg MDMA€12.50/10 pills€80/100, €750/1,000 pillsTheBreakingBad
XTC Pills (240mg, various)$135 – $200/10 pillsMultiple brands availableTor Market

Opiates and Opioids

Heroin remained available from specialist vendors, with Iranian-sourced uncut product marketed as the premium option. The pricing structure on TheBreakingBad was particularly detailed, offering nine quantity tiers from a single gram to a full kilogram. This level of volume pricing suggests these vendors are servicing both individual users and mid-level distributors.

Prescription opioids also featured prominently. Oxycontin (40mg tablets) and Percocet (5/325mg) were listed on Tor Market, though exact per-unit pricing was often obscured behind “add to cart” interfaces that required account creation to view.

ProductPrice RangeVolume PricingSource Market
Heroin Uncut (Iranian)€22.50/g€175/10g, €1,600/100g, €13,500/kgTheBreakingBad
Heroin #3 (60-70%)$50 – $55/3gMid-grade, EU sourcedTor Market
Oxycontin 40mg (20ct)$120 – $200Prescription tabsTor Market
Percocet 5/325mg (70ct)$150 – $250Price per bottle est.Tor Market
Fentanyl patches/pills$50 – $150Limited listings (high risk)Various

Cannabis

Cannabis products dominated by volume of listings. UK-based vendors advertised next-day delivery (NDD) on multiple strains, essentially running a delivery service comparable to legitimate e-commerce. Listings included premium strains such as OG Cookies, Super Silver Haze, Gorilla Glue, and Amnesia Haze, with clear quantity tiers.

ProductPrice RangeVolume/NotesSource Market
Gorilla Glue (7g)£42 (~$53)UK NDD availableAbacus Market
OG Cookies (various)$50 – $120/quarterMultiple vendorsTor Market
Amnesia Haze (100g)$400 – $600Bulk listingAbacus Market
Super Silver Haze$35 – $80/quarterDutch sourcedTor Market
Cannabis (French market)Varies192 products listedFR marketplace

Psychedelics and Dissociatives

The psychedelics market showed strong activity, with psilocybin products packaged in consumer-friendly formats (chocolate edibles, microdose capsules) and ketamine available from multiple vendors. LSD pricing was harder to pin down through DARKSEARCH alone, but cross-referencing with forum discussions suggests typical street-equivalent pricing in the $5 to $15 per tab range.

ProductPrice RangeNotesSource Market
Psilocybin Chocolate (4g)$40Consumer-packaged edibleTor Market
Psilocybin Capsules 150mg (x100)$80 – $150Microdose formatTor Market
Ketamine S-Isomer€10/g€175/50g, €1,850/kgTheBreakingBad
LSD Tabs$5 – $15/tabForum pricing cross-refMultiple
XTC/MDMA (ecstasy, various)€12.50 – $200/10 pillsBrand-dependent pricingMultiple markets

Prescription Pharmaceuticals

Beyond controlled opioids, a range of prescription medications was available. Benzodiazepines (particularly Xanax and Rivotril) were listed at a fraction of pharmacy prices. Erectile dysfunction medications (Cialis) appeared as bulk listings, likely diverted or counterfeit product.

ProductPrice RangeNotesSource Market
Xanax 2mg (50 pills)€5 – €25Alprazolam, likely pressedAbacus Market
Rivotril 2mg (20 pills)$15 – $40ClonazepamTor Market
Cialis (50 tabs)$120 – $200Bulk pack, likely generic/counterfeitTor Market

The drug marketplace in 2026 functions like a professional retail operation. Escrow, customer reviews, volume discounts, refund policies, and domestic stealth shipping are standard. The operational maturity here mirrors what we have seen in the cyber services space, with vendor reputation systems driving quality competition.

Firearms and Ammunition

Firearms remain one of the most sensitive categories on the dark web. Our DARKSEARCH queries returned listings from multiple sources, including a dedicated storefront called “Gun and Shell Factory” and the firearms category on Tor Market (which carried 10 products at the time of our crawl). A vendor called “GlockZ” was also active with 7 listed products.

It is worth noting that firearms sales on the dark web carry the highest scam risk of any category. Law enforcement honeypot operations are well-documented in this space, and many “vendors” simply take payment and never deliver. That said, the listings themselves are informative for understanding what threat actors believe constitutes a reasonable market price, and the availability of these listings is itself a data point worth tracking.

Handguns

FirearmListed Price (USD)CalibreSource
Glock 17 Gen 4$4999mmTor Market
Glock 19$4509mmGun and Shell Factory
Glock 26$3509mmGun and Shell Factory
SIG Sauer P320$6009mmGun and Shell Factory
SIG Sauer P220$680 (sale from $800).45 ACPTor Market
Desert Eagle$899 (sale from $1,000).44 MagnumTor Market
Beretta M9$2499mmTor Market
Ed Brown Kobra$499.45 ACPGun and Shell Factory
CZ TS 2$8999mmGun and Shell Factory

Long Guns and Submachine Guns

FirearmListed Price (USD)TypeSource
AK-47$800 – $1,200Assault RifleGun and Shell Factory
AR-15$700 – $1,000Semi-Auto RifleGun and Shell Factory
UZI Pro$740Submachine GunGun and Shell Factory

Ammunition was also listed separately, though pricing data was less granular in our crawl results. The presence of both firearms and ammunition on the same marketplaces that sell drugs, stolen data, and hacking tools underscores the breadth of these platforms. Tor Market, for instance, carries categories for Counterfeits, Credit Card/CVV/Dumps, Documents, Drugs (47 products), Firearms and Ammo (10 products), Gadgets, and Hacking (13 products), all under one marketplace roof.

Compared to legitimate retail prices, dark web firearms are generally listed at a discount of 30% to 60% from retail, which reflects the risk premium inverted: buyers on the dark web are willing to pay less because of the high risk of scam, non-delivery, or law enforcement interception. From a threat intelligence perspective, the persistence of these listings indicates ongoing demand from individuals who cannot or will not purchase through legitimate channels.

Expanded Counterfeit and Fraud Services

Beyond the identity documents and financial instruments covered earlier, the dark web hosts a broader ecosystem of counterfeit goods and fraud services. Our expanded DARKSEARCH crawl revealed categories including counterfeit luxury goods, forged academic credentials, cryptocurrency fraud tools, and casino bonus exploitation kits.

Counterfeit Luxury Goods
Tor Market listed counterfeit luxury watches, with a Rolex Submariner Non-Date 41mm (model 124060) featured as a promoted product. Counterfeit luxury goods have historically been a smaller dark web category compared to clearnet operations, but their presence on multi-category darknet marketplaces suggests vendors are expanding their offerings to capture cross-selling opportunities from buyers already on the platform for other products.

Cryptocurrency Fraud Tools

Cryptocurrency fraud tools were among the most expensive single-item listings we encountered. The “Tor Amazon” marketplace (operating since 2019) offered an extensive catalogue including stolen Bitcoin wallets, fake USDT senders, wallet cracking tools, and compromised exchange accounts. The pricing here is particularly instructive.

ProductPrice (USD)DetailsSource
Stolen BTC Wallet (599 BTC)$42,000 – $59,900Priced at ~0.1% of wallet balanceTor Amazon
Atomic Wallet 1BTC+$4,000Pre-loaded compromised walletTor Amazon
Bitcoin Wallet w/ Seeds$1,500 – $6,500Wallet.dat with passphraseTor Amazon
Wallet.dat Passphrase Cracker$400Brute-force toolTor Amazon
Flash/Fake USDT Sender$300 – $500Spoofed transactionsTor Amazon
BTC Mnemonic Brute Tool£550 (~$690)12-phrase wallet crackerStandalone store
BTC Reverse Transaction Tool$400 – $600Transaction reversal exploitStandalone store
Leaked Data (16B accounts)$121,484Apple, Google, Binance etc.Tor Amazon

Financial Fraud and Money Movement

The money movement ecosystem on the dark web continues to grow. Services for laundering funds through compromised payment platforms, cloned cards, and bank transfer services were widely available. The Tor Amazon marketplace offered ATM-cloned cards with guaranteed balances, stolen Visa CC/CVV data, Binance account transfers, PayPal-to-Bitcoin conversion services, and casino bonus exploitation kits.

ProductPrice (USD)DetailsSource
ATM Cloned Card ($15K balance)$900Physical card, PIN includedTor Amazon
VISA CC/CVV ($8K balance)$400Virtual card with full detailsTor Amazon
PayPal $7K Verified Transfer$600 (sale from $700)Within 20 minutes worldwideTor Market
Visa Prepaid Clone ($7.5K)$630 (sale from $750)Physical + online usableTor Market
Binance Account Transfer$300 – $500BTC/ETH/USDT transfersTor Amazon
Paxful Accounts ($5.5K)$250 – $400Guaranteed balanceTor Amazon
Casino Bonus Exploit$150 – $350$3K-$10K bonus exploitationTor Amazon
Bank Flash SQR Tool$800 (sale from $1,500)Bank manipulation softwareTor Amazon
Aviator Predictor Hack AI$400Casino/gambling exploit toolTor Amazon
Gold Bars 100g (Pre-Owned)$8,500Physical delivery, escrowTor Amazon

Forged Documents and Credentials

Forged documents ranged from academic credentials (diplomas, degrees, professional certificates) to government-issued identity documents. Tor Market listed a dedicated Documents category with 4 products, while Tor Amazon carried a broader selection under their Documents department. The “USA Documents” product on Tor Amazon was rated 4.85 out of 5 and priced between $600 and $3,500, covering various forms of US identification.

ProductPrice Range (USD)NotesSource
USA Identity Documents (ID Card)$600 – $3,500Multiple ID types availableTor Amazon
Forged Diploma/Degree$200 – $800Various institutionsMultiple markets
Professional Certificates$150 – $500IT, medical, trade certsMultiple markets
Counterfeit COVID Certificates$50 – $150Declining demandForum listings
Deepfake Service$100 – $500Video/image manipulationTor directories

The breadth of these offerings paints a picture of a mature underground economy that mirrors, and in some ways parodies, legitimate commerce. Marketplaces offer escrow protection, customer reviews, vendor ratings, return policies, and even promotional sales events. Tor Amazon, for example, displays a running shopping cart total (one snapshot showed a cart worth $154,514), tracks “verified sellers” with sales counts, and runs sale pricing on multiple products. This operational maturity makes these platforms resilient and, from a threat intelligence perspective, worth continuous monitoring.

Pricing Comparison: 2022 vs 2026

The table below compares our 2022 findings with the current 2026 data across key categories. Prices are typical midpoint values.

Category2022 Average2026 AverageTrend
Credit card with CVV$243$15 – $40Decreased (oversupply)
Counterfeit currency (per $1K)$396$350 – $450Stable
DDoS service (monthly)$382$200 – $500Decreased (commoditised)
Residential proxy (monthly)$645$200 – $645Wider range, lower entry
Initial network access$7,700$2,000 – $5,000Decreased (median)
Ransomware kitN/A$500 – $5,000New category tracked
Crypto drainer kitN/A$200 – $1,000New category
Stealer log subscriptionN/A$100 – $1,024/moNew category
AI criminal toolsN/A$200 – $1,700/moNew category
Cocaine (per gram)$150 – $300$50 – $80Decreased (dark web discount)
Crystal Meth (per gram)$50 – $100$10 – $15Decreased significantly
Heroin (per gram)$100 – $200$22 – $55Decreased (direct sourcing)
Handgun (Glock 17)$1,500 – $2,500$450 – $500Decreased (high scam risk)
Stolen BTC WalletN/A$4,000 – $59,900New category
Forged ID Documents (US)$250 – $1,000$600 – $3,500Increased (quality premium)

The overarching trend is clear: established product categories have become cheaper as supply has increased, while new, more sophisticated offerings (RaaS, drainers, AI tools) have emerged at premium price points. The dark web economy is following the same pattern as legitimate tech markets, with commodity products racing to the bottom while innovation commands a premium.

Key Takeaways

The barrier to entry keeps falling. DDoS attacks for $10, phishing kits for $50, stolen accounts for a few dollars. The tools for cybercrime are cheaper and more accessible than ever. This has direct implications for the volume of attacks organisations should expect to face.

Stealer logs are the new oil. The stealer log economy has grown enormously. These logs, harvested from malware infections on individual machines, contain browser-saved passwords, session cookies, crypto wallet data, and more. They feed almost every other category: account takeover, initial access brokering, financial fraud, and identity theft.

Ransomware is a mature industry. With over 100 active groups tracked on our platform and well-established affiliate models, ransomware has moved from being an emerging threat to a structural feature of the threat landscape. The supply chain (IABs to RaaS operators to affiliates to money launderers) is well-oiled and efficient.

AI is an accelerant. While AI has not yet created fundamentally new attack types, it is making existing attacks more effective, more scalable, and more convincing. The appearance of AI-enabled tools as a distinct product category on the dark web is a development every security team should be tracking.

Crypto is the preferred battlefield. The emergence of crypto drainers as a major product category, combined with the growth in compromised exchange accounts, tells us that cryptocurrency users and platforms are now firmly in the crosshairs. The pseudonymous nature of crypto transactions makes this an attractive and growing target.

Drug marketplaces operate like professional retailers. The dark web drug economy has reached a level of operational maturity that mirrors legitimate e-commerce. Escrow, customer reviews, next-day delivery, volume discounts, lab-testing claims, and refund policies are now standard. Prices have dropped significantly compared to street equivalents, reflecting the efficiency of direct vendor-to-buyer models that bypass traditional distribution chains.

Firearms listings persist despite high scam risk. While firearms are consistently available on dark web marketplaces, this category carries the highest scam risk and is a known target for law enforcement honeypot operations. The listed prices (30% to 60% below retail) reflect this risk. The intelligence value here is less about the prices themselves and more about the persistent demand signal from individuals seeking to acquire weapons outside regulated channels.

The dark web is a one-stop shop. Multi-category marketplaces like Tor Market (drugs, firearms, counterfeits, hacking tools, documents, and financial fraud under one roof) and Tor Amazon (hacking, financial, electronics, documents, drugs, and guns) demonstrate that the underground economy has consolidated. A single marketplace visit can service everything from identity theft to substance procurement to weapon acquisition. This consolidation has implications for law enforcement, intelligence analysts, and risk modelling.

Don’t miss out!

Webinar: 2026 Dark Web Pricing Report

Conclusion

The dark web economy in 2026 is bigger, more diverse, and more sophisticated than it was in 2022. Prices for commodity products have dropped while new, higher-value categories have emerged. The professionalism of threat actors continues to increase, with customer support, affiliate programmes, and quality guarantees now standard across many marketplaces.

What has changed most since our 2022 report is the breadth. The dark web is no longer just a marketplace for stolen data and hacking tools. It is a fully integrated underground economy spanning narcotics, firearms, counterfeit goods, identity documents, cryptocurrency fraud, and digital services. Multi-category marketplaces have consolidated these offerings under single platforms, complete with escrow systems, vendor ratings, and promotional campaigns that would not look out of place on a legitimate e-commerce site.

For defenders and intelligence professionals, the key takeaway is that the cost of attacking your organisation, or acquiring the tools to do so, is low and getting lower. The investment needed to mount a credible phishing campaign, launch a DDoS attack, purchase a weapon, or obtain fraudulent identity documents is trivial compared to the potential payoff. This asymmetry is the fundamental challenge, and understanding the economics of the dark web is essential to building effective defences and informing policy.

At SOS Intelligence, we monitor these marketplaces continuously so our customers do not have to. Our DARKSEARCH platform indexes content across 50+ active dark web sources, and our analysts track emerging threats, new marketplace activity, and pricing trends in real time. If you want to understand what is being said about your organisation on the dark web, or if you need intelligence on any of the categories covered in this report, our platform gives you that visibility.

Passport photo by Kit (formerly ConvertKit) on Unsplash

Crypto Photo by Pierre Borthiry – Peiobty on Unsplash

Drugs photo by Colin Davis on Unsplash

Money hoto by Dmytro Glazunov on Unsplash

Gun photo by Tom Def on Unsplash

"SOS
Investigation, Opinion

Emoji Smuggling: Hiding Malicious Code in Plain Sight

Emoji smuggling represents an emerging obfuscation technique where attackers exploit Unicode encoding and emoji characters to conceal malicious code, bypass security filters, and evade detection systems. Whilst it may sound whimsical, this attack vector leverages legitimate Unicode functionality to create serious security challenges for organisations. Understanding how attackers weaponise these seemingly innocent characters helps us build better defences and recognise when something suspicious might be happening.

This post explores what emoji smuggling is, how attackers use it, and what organisations can do to protect themselves.

The Foundation: How Text Actually Works

Before we dive into the attack itself, we need to understand something fundamental about how computers handle text. When you type a letter, number, or emoji, your computer doesn’t actually store that visual symbol. Instead, it stores a number that represents that character. This system is called Unicode, and it’s what allows your computer to display everything from English letters to Chinese characters to emoji.

For example, when you use the fire emoji 🔥, your computer stores it as the number U+1F525. Every character you can type has its own unique number in the Unicode system. This is brilliant for international communication, but it also creates opportunities for attackers.

The key insight is this: many security systems were built to look for suspicious patterns in regular letters and numbers, but they often don’t scrutinise emoji and special Unicode characters as carefully. Attackers exploit this gap.

What Is Emoji Smuggling?

Emoji smuggling is the practice of using emoji, special Unicode characters, or look-alike characters to hide malicious content from security systems while keeping it functional for their purposes. Think of it as writing a secret message in invisible ink that only becomes visible when you want it to.

Attackers use several techniques:

Look-Alike Characters: Some characters from different alphabets look identical to English letters but are technically different. For instance, the Cyrillic letter ‘а’ looks exactly like the English ‘a’, but computers see them as completely different characters. An attacker might register a domain like “pаypal.com” (using a Cyrillic ‘а’) that looks legitimate to humans but directs to a phishing site.

Emoji as Code: This technique involves creating a substitution cypher where each emoji represents a command, function, or piece of data. Attackers establish a mapping system, similar to how spies might use a codebook. For example, they might decide that:

  • 🔥 represents “delete”
  • 📁 represents “file”
  • 🌐 represents “download”
  • 💀 represents “execute”

So a string like “🔥📁🌐💀” would decode to “delete file, download, execute”. To anyone glancing at log files or monitoring network traffic, this looks like someone simply sent some emoji in a message. Security systems scanning for dangerous keywords like “delete”, “execute”, or suspicious command patterns won’t flag it because they’re looking for text, not pictures.

The attacker’s malware or script includes a decoder that translates these emoji back into actual commands when executed. What makes this particularly effective is that emojis feel innocuous. We’re used to seeing them in messages and social media, so their presence doesn’t immediately raise suspicion the way a long string of seemingly random characters might.

Consider a real scenario: an attacker gains limited access to a system and needs to communicate instructions to their malware without triggering security alerts. They might send what appears to be a harmless message containing emojis through a chat system or email. The malware on the compromised system receives this message, decodes the emoji, and executes the hidden commands. To security analysts reviewing logs, it simply looks like someone sent some emoji.

Invisible Characters: This is perhaps the most insidious technique because it exploits characters you literally cannot see. Unicode includes several characters that have zero width, meaning they take up no visual space on screen. These include the Zero-Width Space (U+200B), Zero-Width Non-Joiner (U+200C), and Zero-Width Joiner (U+200D).

Here’s how this works in practice. Imagine a security system is configured to block any script that contains the text string “malicious_function”. An attacker can break up this string by inserting zero-width characters between the letters:

What you see: malicious_function()
 What’s actually there: mal​ici​ous_​fun​cti​on() (contains invisible zero-width spaces)

To the human eye, even if you’re carefully reading through code, these look identical. But to a security scanner looking for the exact string “malicious_function”, the second version doesn’t match because those invisible characters break up the pattern. The scanner sees “mal[invisible]ici[invisible]ous[invisible]_fun[invisible]cti[invisible]on” and doesn’t recognise it as a threat.

However, when this code actually runs, many programming languages and interpreters ignore these zero-width characters during execution. The invisible spaces are stripped out, and the function executes normally. So the attacker has successfully hidden their malicious code from security scans whilst maintaining its functionality.

Attackers also use invisible characters to hide data within seemingly innocent text. Imagine you’re trying to smuggle a password out of a secure system. You could write a normal-looking sentence like “Please review the quarterly report”, but encode the password in invisible characters interspersed throughout. To anyone reading it, it’s just a mundane sentence. But someone with the right decoder can extract the hidden information.

This technique is particularly dangerous because it’s virtually impossible to detect through visual inspection alone. You need specialised tools that reveal invisible characters, and even then, you need to know how to look for them.

Direction Trickery: Unicode includes special characters that change the direction text flows (needed for languages like Arabic). Attackers use these to make filenames appear safe when they’re actually dangerous. A file might display as “document.txt” but actually be “tnemucod.exe” with a direction-reversal character hiding the true extension.

Why This Works

You might wonder why this is effective if it seems so simple. The answer lies in how security systems are designed.

Most security tools were built to detect patterns in regular ASCII text (the basic English letters, numbers, and symbols). They look for suspicious keywords, known malicious code patterns, or dangerous file types. But when attackers encode their attacks using Unicode tricks, these patterns become unrecognisable to the security system.

It’s similar to how a metal detector at an airport won’t find a ceramic knife. The detector is designed to find metal, and the knife is dangerous, but because it’s made of the wrong material, it slips through. Similarly, security filters are often designed to catch ASCII-based threats, so Unicode-based threats slip through.

Additionally, completely blocking Unicode would break legitimate functionality. Businesses operate globally, users have names in different languages, and emojis are a standard part of modern communication. Security teams can’t simply ban all non-English characters without severely impacting usability.

Real-World Examples

Understanding the theory is one thing, but seeing how this plays out in practice makes the threat more tangible.

Phishing Attacks: Attackers register domain names using look-alike characters. A company email might tell you to log in at “microṡoft.com” (note the dot over the ‘s’). To most people, this looks perfectly normal, but it’s not the real Microsoft. Users enter their credentials, and the attacker now has access to their account.

Bypassing Content Filters: Many organisations block certain words in emails or messages to prevent data leaks or inappropriate content. An employee trying to circumvent these filters might write “pаssword” using a Cyrillic ‘а’ instead of the English ‘a’. The filter doesn’t catch it because it’s technically a different word, but humans reading it understand the meaning perfectly.

Hidden Data Exfiltration: An attacker who has compromised a system needs to send stolen data out without triggering data loss prevention systems. They might encode credit card numbers using emoji: “4️⃣5️⃣3️⃣2️⃣ 1️⃣2️⃣3️⃣4️⃣ 5️⃣6️⃣7️⃣8️⃣ 9️⃣0️⃣1️⃣0️⃣”. Security systems looking for the pattern of a 16-digit number won’t detect this, but it’s trivial to decode on the other end.

Malware Obfuscation: Malware authors need to hide suspicious commands from antivirus software. They might write “po​we​rs​he​ll” with invisible zero-width spaces between letters. When a security researcher looks at the code, they see gibberish, and antivirus scans don’t recognise the command. But when the malware runs, it successfully executes PowerShell commands.

Code Injection: Web applications that don’t properly handle Unicode input can be vulnerable to injection attacks. An attacker might submit what looks like normal text but includes hidden direction-control characters that manipulate how the input is processed, potentially executing unauthorised database queries or commands.

The Impact on Large Language Models

As artificial intelligence and large language models (LLMs) become increasingly integrated into business operations and security workflows, emoji smuggling presents a unique and evolving challenge. These AI systems, designed to understand and process human language, can be vulnerable to Unicode-based attacks in ways that differ from traditional security systems.

Prompt Injection via Unicode: LLMs process text input and generate responses based on their training. Attackers can use Unicode tricks to bypass safety filters or inject malicious instructions that the model follows. For instance, an attacker might use invisible characters to break up prohibited phrases that the model has been trained to refuse, or use look-alike characters to make harmful instructions appear benign to content filters whilst remaining interpretable by the model.

Consider a scenario where an LLM-powered chatbot has been instructed never to provide information about bypassing security systems. An attacker might craft a prompt using Cyrillic characters that visually spell out the forbidden request but technically use different Unicode characters. The safety filter checking for specific English phrases might not catch it, but the LLM, trained on diverse text including multiple alphabets, might still understand and respond to the request.

Training Data Poisoning: If emoji-encoded malicious content makes it into an LLM’s training data, the model might learn to recognise and even replicate these encoding schemes. This could result in the model inadvertently helping attackers by generating emoji-encoded malicious payloads or failing to recognise them as threats when analysing suspicious content.

Context Window Manipulation: LLMs have limited context windows (the amount of text they can process at once). Attackers can use invisible Unicode characters to pad inputs, pushing important safety instructions or system prompts out of the model’s effective context whilst keeping malicious instructions within it. The model might then follow attacker instructions without the safeguards that should be governing its behaviour.

Output Encoding Attacks: Even if an LLM correctly identifies malicious content, attackers can request that the output be encoded using emoji or Unicode tricks. The model might comply, creating encoded malicious payloads that bypass downstream security filters. For example, asking an LLM to “translate this command into emoji” could result in the creation of an emoji-based encoding scheme that evades detection.

Jailbreaking and Safety Bypass: The LLM security community has documented numerous “jailbreaking” techniques where carefully crafted prompts cause models to ignore their safety training. Unicode tricks add another dimension to this. Attackers can use direction override characters, invisible spaces, or homoglyphs to craft prompts that appear innocent to automated safety systems but contain hidden instructions that the LLM interprets and follows.

Challenges for AI Security Teams: Defending LLMs against emoji smuggling is particularly challenging because these models are designed to be flexible and understand context across languages and writing systems. Blocking all Unicode would severely limit their utility for international users. Instead, organisations deploying LLMs need to:

  • Implement robust input normalisation before text reaches the model
  • Use multiple layers of content filtering that account for Unicode variations
  • Monitor model outputs for unusual Unicode patterns that might indicate encoding attempts
  • Regularly test models with Unicode-based attack vectors
  • Maintain updated safety training that includes awareness of these techniques

The Detection Problem: Traditional security tools can be configured to flag invisible characters or suspicious Unicode patterns. However, LLMs are probabilistic systems that generate novel outputs. This makes it harder to predict when they might be manipulated into producing emoji-encoded content or responding to Unicode-obfuscated instructions. Security teams need to think about both preventing malicious inputs and detecting problematic outputs.

Real-World Implications: As organisations increasingly rely on LLMs for tasks like code generation, content moderation, customer service, and security analysis, the stakes grow higher. An LLM that can be tricked into generating malicious code through Unicode manipulation, or that fails to identify emoji-smuggled threats in content it’s supposed to be moderating, becomes a liability rather than an asset.

The intersection of emoji smuggling and LLM security represents an emerging area of concern. As these AI systems become more capable and more widely deployed, attackers will continue to probe for weaknesses in how they handle Unicode and interpret encoded content. Organisations must stay vigilant and ensure their AI security strategies account for these evolving threats.

The Challenge for Defenders

Defending against emoji smuggling is tricky because it requires balancing security with functionality. Organisations face several challenges:

International Requirements: Businesses serve global customers and employ international staff. Blocking non-English characters would prevent people from using their actual names or communicating in their native languages. This isn’t just inconvenient; in many jurisdictions, it could be discriminatory.

Performance Concerns: Thoroughly inspecting every character of every piece of text for Unicode tricks requires significant computing power. For high-traffic websites or applications, this can slow things down noticeably.

Evolving Techniques: The Unicode standard contains over 140,000 characters and is regularly updated. Attackers constantly find new, creative ways to exploit this complexity. What works to block attacks today might not catch the techniques used tomorrow.

False Positives: Aggressive filtering can block legitimate content. An email from a Greek customer with a name containing Greek letters might be flagged as suspicious. A message containing many emojis (completely normal in casual conversation) might trigger alerts.

Defensive Strategies

Despite these challenges, organisations can implement effective defences against emoji smuggling. The key is taking a layered approach rather than relying on any single solution.

Input Validation and Normalisation: Systems should normalise Unicode input, converting visually similar characters to a standard form. This helps ensure that “pаypal” (with a Cyrillic ‘а’) and “paypal” (with an English ‘a’) are recognised as attempts to use the same string. For structured data like usernames or email addresses, systems can enforce stricter rules about which characters are allowed.

Context-Aware Security: Different fields need different levels of restriction. A username field might only allow basic English letters and numbers, whilst a comment field can permit a wider range of characters, including emojis. Security controls should adapt to the context rather than applying blanket rules.

Visual Similarity Detection: Advanced systems can detect when Unicode characters are being used to mimic legitimate domains or brands. If someone tries to register a domain that looks almost identical to a major company’s website, the system can flag it for review.

Invisible Character Removal: For most applications, there’s no legitimate reason to include invisible Unicode characters in structured data. Systems can strip these out or flag their presence as suspicious, particularly in fields like usernames, file names, or code inputs.

Monitoring and Anomaly Detection: Rather than trying to block everything suspicious at the gate, organisations can monitor for unusual patterns. A sudden spike in emoji usage in log files, the presence of mixed alphabets in a single field, or zero-width characters appearing in database entries can all trigger alerts for security teams to investigate.

User Education: Technical controls only go so far. Training staff to recognise suspicious URLs (by checking the actual address in their browser, not just what’s displayed), to be cautious about unexpected login requests, and to report unusual behaviour helps catch attacks that slip through automated defences.

Security by Design: When building new systems, developers should consider Unicode handling from the start. This includes using libraries that properly handle normalisation, implementing appropriate validation for each input field, and testing with Unicode attack vectors during security assessments.

What This Means for Different Audiences

For Security Professionals: Emoji smuggling should be part of your threat model. Include Unicode-based attacks in penetration testing, ensure your security tools can detect these techniques, and review how your applications handle Unicode input. This isn’t a theoretical concern; it’s being actively exploited.

For Developers: Don’t assume that checking for suspicious ASCII strings is sufficient. Implement proper Unicode normalisation, validate input based on context, and be aware of how your programming language and frameworks handle Unicode. What you see on screen may not be what’s actually stored or processed.

For Business Leaders: Understand that security isn’t just about detecting known malware signatures or blocking obvious threats. Modern attacks exploit subtle aspects of how systems work. Investment in security tools, training, and secure development practices pays dividends by preventing breaches that could damage reputation and finances.

For Everyday Users: Be sceptical of links, even if they look legitimate. When entering sensitive information, double-check that you’re on the correct website by examining the URL carefully. Be particularly cautious with messages that create urgency or ask you to log in via a provided link.

The Bigger Picture

Emoji smuggling is part of a broader category of attacks that exploit the gap between human perception and machine processing. We see what we expect to see, whilst computers process what’s actually there. Attackers exploit this disconnect.

This isn’t unique to Unicode. Similar principles apply to audio deepfakes (where we hear what sounds like a trusted voice), visual manipulations (where images appear legitimate but are fabricated), and social engineering (where contexts appear trustworthy but are manufactured). The common thread is exploiting trust and perception.

As systems become more sophisticated, so do attacks. The growth of international internet usage and the ubiquity of emoji in modern communication create both opportunities and challenges. We need security solutions that protect without stifling legitimate use, that adapt to new threats whilst maintaining usability, and that account for the complexity of human language and communication.

Conclusion

Emoji smuggling demonstrates that security threats don’t always come from sophisticated zero-day exploits or advanced persistent threats. Sometimes they come from clever misuse of legitimate functionality. A simple emoji or an invisible character can bypass expensive security systems if those systems aren’t designed to handle them.

The good news is that awareness and proper design can mitigate these risks. Organisations that understand the threat, implement appropriate controls, and maintain vigilance can protect themselves effectively. It requires thinking beyond traditional security approaches and considering how attackers might abuse features we take for granted.

As you think about your own organisation’s security, consider asking: How do our systems handle Unicode? Could someone use look-alike characters to impersonate our brand? Are we monitoring for unusual patterns in text input? Could malicious code be hiding in emojis or invisible characters?

These questions might reveal gaps in your defences, but identifying those gaps is the first step towards closing them. In security, the threats we understand and prepare for are far less dangerous than the ones we overlook.

Smiling emoji image photo by chaitanya pillala on Unsplash.

Header image photo by Shubham Dhage on Unsplash.

"The
Investigation

The 0apt Phenomenon: When Ransomware Operators Fake It Until They Make It (Or Don’t)

In late January 2026, a new name appeared on the ransomware landscape with unusual fanfare. Within just 11 days, a group calling itself “0apt” or the “0apt Syndicate” claimed to have compromised over 200 organisations worldwide, including some of the most recognisable corporate names in healthcare, manufacturing, and critical infrastructure. For security teams already stretched thin, monitoring established threat actors, this sudden emergence raised an immediate question: Is this a sophisticated new player we need to worry about, or something else entirely?

Our analysis at SOS Intelligence, combined with findings from the broader cybersecurity community, suggests the answer leans heavily toward “something else entirely.” What we’re witnessing isn’t the birth of a formidable ransomware operation, but rather an elaborate bluff, a digital smoke-and-mirrors show designed to exploit fear, trigger hasty responses, and potentially extract payments for data that was never stolen in the first place.

The Rise of 0apt: Too Much, Too Fast

Most ransomware operations build their reputations slowly and deliberately. Groups like LockBit, ALPHV, and Cl0p spent months or years establishing credibility through verified attacks before becoming household names in the cybersecurity world. They understood that trust, even among criminals, requires proof of capability.

0apt took a different approach. Between January 28 and February 8, 2026, the group posted 208 alleged victims to their dark web leak site. That’s an average of nearly 19 victims per day, a pace that would make even the most prolific established ransomware cartels envious. To put this in perspective, most sophisticated ransomware operations might claim 20-30 victims in a good month, not a week and a half.

Our analysis of their victim list reveals a telling pattern. The operation appears to have launched in two distinct phases:

Phase 1: The Test Run (January 28-30) The first 90 victims on the leak site share a suspicious characteristic: they all read like they were generated by an LLM, asked to create “generic company names”: Blue Water Utilities, Summit Financial Group, Quantum Research Labs, Apex Law Firm, Stellar Aviation Parts. When we attempted to verify these organisations, we found minimal online presence, unclear corporate structures, or, in many cases, no evidence they exist at all beyond a basic domain registration.

As RansomLook, a respected ransomware tracking service, noted in their analysis: “This group is newly observed, and first observation suggest this is not a serious group, as most – if not all – of the claims cannot be validated and are for random company names. Analysis of available GitHub repositories and sandbox detonations suggest the actor lists those sandbox runs as victims.”

In other words, 0apt appears to have been testing their infrastructure, possibly using automated malware sandboxes and fabricated company names to populate their site and make it look operational.

Phase 2: Going for the Headlines (February 3-8) Then something changed. Beginning on February 3, the group pivoted sharply, suddenly claiming to have breached 118 legitimate, verifiable organisations and not just any organisations. We’re talking about household names: Saint-Gobain, Bouygues, Honda, Novartis, DHL, Caterpillar, Mayo Clinic. These are multi-billion dollar corporations with mature security programs and global brand recognition.

This shift in targeting is where the operation becomes particularly interesting from a threat intelligence perspective. The group went from claiming victims that couldn’t be verified to claiming victims that are too big to be credible, at least at this volume and velocity.

The Medical Device Obsession

One pattern immediately jumped out during our analysis: an unusual concentration of victims in the medical devices and equipment industry. Of the 118 “legitimate” victims claimed by 0apt, 20 (16.9%) operate in this specific sector. This list includes major players like Edwards Lifesciences, Hologic, Align Technology, Terumo Corporation, and Dentsply Sirona.

For context, medical device manufacturers typically represent less than 2-3% of ransomware victims in a given year. The concentration of nearly 17% of claims in this narrow industry raises questions. Why would a new threat actor have such outsized success penetrating this particular vertical?

Our hypothesis: these targets weren’t chosen because they were vulnerable, but because they’re valuable at least in terms of potential psychological impact. Medical device companies handle patient data, operate in heavily regulated environments, face strict FDA oversight, and carry enormous reputational risk. The mere appearance of their name on a leak site could trigger immediate board-level concerns, even without verification of an actual breach. In the playbook of an extortion scam, that’s valuable real estate.

The Technical Red Flags: Where the Facade Cracks

If the volume and velocity of claims weren’t suspicious enough, the technical evidence tells an even more damning story. Multiple independent analyses have uncovered significant anomalies that strongly suggest 0apt is running a bluff operation rather than a genuine ransomware enterprise.

The Empty File Problem

Perhaps the most glaring indicator comes from analysis of the actual “data” 0apt claims to have exfiltrated. According to reporting from DataBreach.com and corroborated by our own observations, the download links on the 0apt leak site don’t deliver actual stolen data. Instead, they appear to stream infinite loops of random binary data, essentially digital white noise.

As DataBreach.com explained in their investigation: “According to researchers who watched the traffic, the group’s servers are likely piping a stream of /dev/random (a standard computer tool for making random bits) straight into the user’s browser.” This creates a convincing illusion. The data stream looks like it could be a massive encrypted file hundreds of gigabytes, as the group claims. But there are no file headers, no recognisable structure, no actual content. Just an endless torrent of random bytes that, over Tor’s notoriously slow network, could take days to download before an analyst realises they’ve captured nothing but noise.

This aligns with our own analysis of sample files allegedly stolen from victims. Many contain nothing but 0-byte data, empty shells that prove nothing except that someone created a file with a particular name. No intellectual property, no customer records, no financial data. Just empty digital husks masquerading as evidence of compromise.

Identical Download Sizes and Inflated Metrics

Another red flag emerged when examining the claimed file sizes for different victims. In multiple cases, completely different organisations operating in different countries, different industries, with different IT infrastructures, allegedly had stolen data packages of identical sizes. This defies logic. Real data exfiltration from diverse organisations would produce highly variable file sizes based on what was actually accessed and stolen.

Additionally, the file tree download sizes appeared massively overinflated compared to what would be expected from the types of data purportedly stolen. This suggests the group is manipulating display metrics to make their claims appear more substantial than they are.

The “Proof” That Never Comes

Standard ransomware operations typically provide some form of proof when making victim claims, screenshots of file directories, samples of stolen documents, or other evidence that demonstrates they actually penetrated the target network. This serves a dual purpose: it validates their capability to potential “customers” in the RaaS model, and it pressures victims to take negotiations seriously.

0apt claims to provide evidence of breach 24 hours before publishing data. According to our observations and external reporting, this has never happened. Not once. The promised proof never materialises, yet new victims continue to be added to the leak site regardless. This pattern is inconsistent with how legitimate (in the criminal sense) ransomware operations behave.

Infrastructure Quality: Amateur Hour

Perhaps the most telling technical indicator comes from analysis of 0apt’s operational infrastructure. According to SOCRadar’s research, source code analysis of the attacker’s admin panel revealed internal developer comments written in Hindi or Urdu. These comments included mundane instructions like how to handle default JSON values, the kind of notes you’d expect in a basic web development project, not a sophisticated criminal enterprise.

The infrastructure appears to be what SOCRadar describes as “a chaotic mix of AI-generated scripts and amateur web development.” This isn’t the hallmark of a group that successfully penetrated Fortune 500 companies. It’s the signature of operators who prioritised creating the appearance of a threat over developing actual technical capabilities.

This linguistic evidence also provides clues about attribution. The use of Hindi/Urdu developer comments suggests operators or developers from South Asia, which stands in stark contrast to the Russian-speaking core typical of established, top-tier ransomware operations. While geography alone doesn’t determine capability, it does add to the overall picture of a group that doesn’t fit the profile of what they’re claiming to be.

The Psychology of the Scam: Why It Might Work Anyway

Understanding that 0apt is likely a bluff operation raises an important question: if the technical evidence is so clearly flawed, why bother? The answer lies in psychology, timing, and the mechanics of corporate decision-making under pressure.

The Reputational Trigger

When a company’s name appears on a ransomware leak site next to a claim of “200GB of stolen data,” several things happen simultaneously. Stock prices can react before any technical validation occurs. Board members start asking pointed questions. Legal teams begin assessing regulatory notification requirements. PR departments prepare crisis communications. All of this happens in the fog of uncertainty, before anyone has confirmed whether the breach actually occurred.

For high-profile organisations, particularly those in healthcare, finance, or critical infrastructure, the risk calculus isn’t purely technical. A CISO might know the evidence looks suspicious, but when the CEO asks, “Are you 100% certain we weren’t breached?”, absolute certainty is difficult to provide without exhaustive investigation. And investigations take time that leak site countdown timers don’t allow.

0apt appears to be betting that for at least some victims, the calculus tips toward: “The cost of investigating this properly exceeds the cost of paying to make it go away.” Essentially, they’re trying to monetise uncertainty and reputational risk rather than actual data theft.

Gaming the Ecosystem

The 0apt operation also exploited an underappreciated vulnerability in the threat intelligence ecosystem: automation. Numerous dark web monitoring services, data breach aggregators, and threat intelligence platforms automatically scrape leak sites for new victim claims. When 0apt posted 208 victims in rapid succession, many of these automated systems faithfully reported each claim, treating them as verified facts rather than unsubstantiated allegations.

This created an amplification effect. News bots republished the claims. Companies received automated alerts that they’d been listed. Threat feeds updated to include 0apt as an “active threat actor.” The sheer volume of automated reporting lent the operation a veneer of legitimacy it hadn’t earned through actual technical capability.

RansomLook eventually recognised this and took action, noting: “The group appears unreliable. Most, if not all, of its alleged victims cannot be verified and appear to be randomly selected organisations. WE HAVE DECIDED TO REMOVE ENTRIES FOR THIS GROUP.” But by that point, the noise had already been generated.

The Onion Site Goes Dark

As of this writing, the 0apt onion site has been offline for several days. This could indicate several things: the operators may have achieved their goal (whatever that was), they may have been disrupted by law enforcement or security researchers, or they may be regrouping for another attempt. The pattern of claiming hundreds of victims then going silent is unusual for a ransomware operation that supposedly has ongoing extortion negotiations with major corporations.

Victimology Analysis: Patterns in the Claims

Our analysis of the 118 “legitimate” victim claims reveals several interesting patterns beyond the medical device concentration:

Geographic Distribution:

  • United States: 34 victims (28.8%)
  • United Kingdom: 12 victims (10.2%)
  • France: 10 victims (8.5%)
  • Japan: 10 victims (8.5%)
  • Switzerland: 9 victims (7.6%)

The geographic spread targets countries with strong economies, mature security regulations, and companies that face significant reputational risk from data breaches. These aren’t necessarily the easiest targets; they’re the targets most likely to consider paying to protect their reputation.

Sector Focus:

  • Manufacturing: 67 victims (56.8%)
  • Health & Social Care: 20 victims (16.9%)
  • Professional Services: 4 victims (3.4%)
  • Pharmaceutical: 4 victims (3.4%)

The overwhelming focus on manufacturing (particularly industrial machinery, electronics, and medical devices) suggests a deliberate targeting strategy. Manufacturing companies often handle valuable intellectual property, operate complex supply chains, and face significant operational disruption risks, all factors that theoretically increase willingness to pay ransoms.

However, the pattern also reveals something else: these victim selections look like they could have been compiled from business directories or LinkedIn searches rather than through actual network reconnaissance. The diversity is too perfect, the coverage too comprehensive, the success rate too high to be credible as the output of actual penetration testing and exploitation.

Cross-Referencing with Historical Data: The Repeat Victim Question

One theory we investigated was whether 0apt simply repackaged previously stolen data from earlier breaches. Ransomware cartels sometimes sell or trade access and data, and it wouldn’t be unprecedented for a new group to claim “victims” using datasets obtained from others.

Our cross-referencing of the 0apt victim list against historical breach databases revealed minimal overlap. While one or two of the claimed victims had been hit by other ransomware operations in the past 2-3 years, the numbers weren’t sufficient to suggest wholesale data recycling. This actually makes the operation more suspicious, not less. It suggests the group didn’t even have old stolen data to work with, let alone new breaches.

What This Means for Defenders

The 0apt phenomenon, regardless of whether it represents an outright scam or just an extraordinarily inept threat actor, offers several important lessons for security teams:

Verify Before You React

The most critical takeaway is this: a leak site listing is not confirmation of a breach. In an ideal world, every organisation would have robust internal logging and monitoring that could definitively answer the question “were we breached?” within hours of a claim appearing. In practice, many organisations lack this visibility, which is exactly what operations like 0apt exploit.

If your organisation appears on a leak site:

  1. Check internal logs first – Look for evidence of large-scale data exfiltration (unusual outbound traffic patterns, especially to cloud storage providers or Tor exit nodes)
  2. Look for encryption events – Real ransomware leaves traces: encrypted files, ransom notes, unusual process executions
  3. Examine any provided “proof” – Scrutinise file samples for 0-byte files, check if screenshots could have been doctored or taken from public sources, verify that claimed file trees match your actual infrastructure.
  4. Validate download links – Before spending days downloading alleged proof packages, test the file integrity and check if you’re receiving actual data or random noise.

The Evidence Standard

Organisations should establish a clear evidence standard before engaging with alleged attackers. What would constitute sufficient proof that a breach occurred? File samples containing actual internal data? Screenshots showing authentic network architecture? Access to specific systems that only an insider would know about?

Without a clear evidentiary bar, it’s too easy to fall into the trap of “better safe than sorry” and engage in negotiations over a breach that never happened. 0apt is counting on this impulse.

The Communications Challenge

When a major corporation appears on a leak site, word spreads quickly. Partners ask questions. Customers express concern. Regulators may initiate inquiries. This creates pressure to “do something” even when evidence is lacking.

Security teams should prepare communications strategies in advance that allow them to acknowledge awareness of claims while reserving judgment on their validity. Something like: “We are aware of allegations that have appeared on criminal forums. We are conducting a thorough internal investigation and will communicate transparently about any confirmed impacts to data or systems.”

This is better than either dismissing claims outright (which can backfire if they turn out to be true) or treating unverified allegations as confirmed breaches (which gives credibility to scam operations).

Harden the Basics

Here’s an uncomfortable truth: even if 0apt’s data claims are fake, their initial access vector might not be. The group likely used automated scanners to identify internet-facing vulnerabilities, weak credentials, or unpatched systems. Even if they didn’t do anything meaningful with that access, the vulnerability still exists for the next threat actor who comes along.

Use the 0apt scare as a forcing function to address foundational security hygiene:

  • Patch internet-facing VPN concentrators, firewalls, and web applications
  • Enforce multi-factor authentication on all remote access
  • Implement network segmentation to limit lateral movement
  • Deploy robust logging to detect unusual data exfiltration
  • Regularly test backup and recovery procedures

The Vendor Question

One concerning aspect of the 0apt operation is the inclusion of several third-party service providers and technology vendors on their victim list. In today’s interconnected business environment, a breach at a vendor can cascade to affect dozens or hundreds of downstream customers.

Organisations should proactively monitor whether their critical vendors and partners appear on leak sites, even potentially fake ones like 0apt’s. The claim might be false, but it’s still worth verifying with the vendor rather than assuming, especially if they’re a critical component of your supply chain or handle sensitive data on your behalf.

The Bigger Picture: Scam-as-a-Service?

The 0apt operation represents something potentially more insidious than a traditional ransomware campaign: it’s ransomware theatre. All of the trappings of a sophisticated criminal enterprise; the professional-looking leak site, the countdown timers, the long list of high-profile victims, the technical jargon about encryption algorithms, with none of the actual technical capability to execute the attack they’re claiming.

This raises uncomfortable questions about the future of the threat landscape. If 0apt can generate this much noise with fake claims and random data streams, how many other “ransomware groups” are running similar operations? How much of the ransomware ecosystem is built on bluff and psychological manipulation rather than actual technical exploitation?

The answer likely varies. Established groups like LockBit, ALPHV, Cl0p, and others have proven their capabilities through verified attacks, leaked data, and recovered ransomware samples analysed by security researchers. Their technical bona fides are well-established.

But the ransomware ecosystem has also spawned numerous smaller, shorter-lived operations groups that appear suddenly, make a handful of claims, then vanish. Some of these are likely legitimate operations that failed to gain traction. Others might be running variations of the 0apt playbook: enough smoke to trigger a few payments, then move on before victims realise they’ve been conned.

Current Status and Outlook

As of February 10, 2026, the 0apt onion site remains offline. No victims have publicly confirmed breaches attributed to the group. No validated samples of stolen data have surfaced. The group has made no public statements explaining their silence or their sudden disappearance.

Several scenarios seem plausible:

  1. Mission Accomplished: The operators may have successfully extracted payments from one or more victims who paid to have their names removed from the leak site, regardless of whether an actual breach occurred. Having monetised the operation, they shut down before attracting too much scrutiny.
  2. Operation Disrupted: Law enforcement or security researchers may have identified and disrupted the infrastructure. While less likely (since the operation appears to be primarily a scam rather than actual malware distribution), it’s possible that the attention from the security community led to hosting providers or law enforcement action.
  3. Regrouping: The operators may be refining their approach, building new infrastructure, or planning a “second season” of the operation with lessons learned from this initial attempt.
  4. Abandoned: It’s also possible the operators simply gave up when the operation didn’t produce expected results or when the security community rapidly identified it as a likely scam.

Regardless of which scenario proves accurate, the 0apt phenomenon has already served its purpose as a case study in how not all ransomware operations are what they seem.

Recommendations for the Security Community

The 0apt situation highlights several areas where the threat intelligence community can improve collective response to emerging threats:

Verification Before Amplification: Threat intelligence platforms and dark web monitoring services should implement stronger verification processes before automatically reporting leak site claims as confirmed breaches. A multi-tier system (unverified claim / partially verified/confirmed) would provide more accurate intelligence to customers.

Sharing Technical Indicators: When operations like 0apt emerge, rapid sharing of technical analysis (0-byte files, random data streams, infrastructure quality assessments) can help the broader community identify and filter out scam operations before they generate widespread concern.

Education and Awareness: Security awareness training should include scenarios around threat actor claims and the importance of verification. Too many organisations still treat a leak site posting as equivalent to a confirmed breach.

Pressure on Platforms: The hosting providers, domain registrars, and payment processors that enable these operations, even scam operations, should face pressure to verify the legitimacy of ransomware “businesses” using their services. While difficult to enforce, it’s worth pursuing.

Conclusion: Trust, But Verify (Actually, Just Verify)

The 0apt operation serves as a reminder that in the threat intelligence world, we cannot take claims at face value, even from criminal actors who theoretically have a reputational incentive to be honest about their capabilities. The ransomware ecosystem has matured to the point where running a convincing fake operation is apparently easier and potentially more profitable than developing actual technical capabilities.

For security teams, this creates both challenges and opportunities. The challenge is that we now need to verify not just whether our defences worked against an attack, but whether an attack even occurred in the first place. The opportunity is that operations like 0apt are, ultimately, easier to defend against than sophisticated threat actors with genuine capabilities. Their success requires that we panic and pay rather than investigate and verify.

At SOS Intelligence, our analysis suggests treating 0apt claims with extreme scepticism unless and until concrete evidence emerges that contradicts the accumulating technical indicators of a scam operation. The volume of claims, velocity of posting, technical anomalies, infrastructure quality, and operational patterns all point toward an elaborate bluff rather than a capable threat actor.

That doesn’t mean organisations can completely ignore 0apt claims if they appear on the leak site. It means those claims should trigger an investigation, not an immediate crisis response. Verify your logs, examine your systems, and look for actual evidence of compromise. If you find it, respond accordingly. If you don’t, you’ve likely dodged not a ransomware attack, but a psychological operation designed to exploit fear and uncertainty.

In a threat landscape increasingly crowded with noise, the ability to separate signal from fabrication is becoming as important as the ability to defend against actual attacks. The 0apt phenomenon is a test case in that skill, and so far, the security community appears to be passing.

Stay skeptical. Stay vigilant. And remember: in cybersecurity as in life, if something seems too bad to be true, it just might be.

SOS Intelligence continues to monitor 0apt and similar emerging threats. Organisations that believe they may have been legitimately compromised should conduct thorough internal investigations and consult with incident response specialists. For questions or to share additional intelligence on 0apt, please contact Daniel Collyer at SOS Intelligence.

""/
Investigation, Opinion

Key Cyber Threat Intelligence Trends to Watch in 2026

Why 2026 Matters for CTI

As organisations enter 2026, cyber threat intelligence finds itself at a critical inflexion point. The threat landscape continues to expand in volume and complexity, but the pressures shaping it are no longer purely technical. Geopolitical instability, regional conflict, and sustained economic uncertainty are increasingly influencing who is targeted, why, and to what end. For businesses, this means cyber risk is now inseparable from broader strategic and operational risk.

At the same time, the pace of technological change continues to accelerate. Artificial intelligence is now firmly embedded on both sides of the threat equation. Adversaries are using AI to scale social engineering, automate reconnaissance, and rapidly adapt tooling, while defenders are racing to apply the same technologies to detection, analysis, and response. This arms race is generating more data, more alerts, and more intelligence than ever before.

Yet quantity is no longer the problem. Many organisations are experiencing intelligence overload, where feeds, reports, and indicators accumulate faster than they can be meaningfully consumed. Decision makers are not asking for more information, but for clearer insight. They want to understand which threats matter, how they are likely to manifest, and what actions should be prioritised in response.

As a result, 2026 represents a decisive shift for cyber threat intelligence. The focus is moving away from collecting more data and towards understanding it better. Success is increasingly defined by context, relevance, and the ability to translate technical detail into actionable judgment. This is less a year of entirely new threats and more a year defined by how existing threats are used, scaled, and adapted to specific targets and circumstances.

In this article, we explore the key trends shaping cyber threat intelligence in 2026, and what they mean for organisations seeking to make informed, risk-based decisions in an increasingly uncertain environment.

AI-Native Threat Actors Become the Norm

By 2026, the use of artificial intelligence by threat actors can no longer be described as experimental or emerging. For many adversaries, AI-enabled tooling is now embedded into everyday operations, shaping how attacks are planned, executed, and refined. Rather than creating entirely new categories of threats, AI is amplifying existing ones by increasing their speed, scale, and apparent sophistication.

One of the most visible impacts is in phishing, pretexting, and broader social engineering activity. AI-generated content allows attackers to produce convincing messages tailored to specific organisations, roles, or even individuals with minimal effort. Language quality is no longer a reliable signal of legitimacy, and pretexts can be rapidly adapted based on open source information, previous engagement, or real-time feedback. This has significantly reduced the cost and skill barrier traditionally associated with effective social engineering.

Malware development has also been accelerated. AI-assisted coding and analysis tools enable faster iteration, allowing threat actors to modify payloads, obfuscation techniques, and delivery mechanisms in near real time. Polymorphism and frequent recompilation mean that identical samples may exist only briefly, limiting the usefulness of traditional signature-based detection and static file indicators. The result is a faster-moving malware ecosystem that is harder to catalogue and track using conventional methods.

Reconnaissance and target profiling are increasingly automated. Threat actors can now use AI to process large volumes of leaked data, scraped content, and technical metadata to identify high-value targets and likely points of weakness. This automation enables more precise targeting while reducing the need for manual research, allowing even smaller or less experienced groups to operate with a level of efficiency previously associated with more capable actors.

Taken together, these developments are blurring traditional distinctions between high-skill and low-skill adversaries. Tools that once required significant expertise to develop or operate are becoming accessible through automation and commoditised services. As a result, lower capability actors can conduct campaigns that appear more polished, more targeted, and more persistent than their underlying skill level would suggest.

For cyber threat intelligence teams, this shift has important implications. Static indicators such as file hashes, domains, and IP addresses are ageing even faster than before, often becoming obsolete within hours or days. While such indicators still have operational value, they can no longer be the primary lens through which AI-enabled activity is understood.

Instead, there is a growing need to focus on behavioural patterns and campaign-level analysis. Understanding how attacks are structured, how lures evolve over time, and how infrastructure is deployed and rotated provides more durable insight than individual technical artefacts. Equally important is tracking the evolution of tradecraft. The key intelligence question is no longer which tool was used, but how it was applied, adapted, and combined with other techniques to achieve an objective.

In 2026, effective threat intelligence depends less on cataloguing tools and more on recognising patterns of behaviour. As AI continues to level the playing field for adversaries, the ability to identify and contextualise these patterns will be central to maintaining meaningful visibility into the threat landscape.

AI-Enabled Tradecraft in Practice

During 2024 and 2025, security researchers documented the use of generative AI tools such as WormGPT and FraudGPT in live phishing and business email compromise campaigns, enabling fluent, highly targeted lures at scale. Microsoft and Google both reported attackers using AI-assisted reconnaissance to tailor phishing based on user roles, organisations, and cloud environments. In parallel, Mandiant and Microsoft observed identity-focused intrusions where domains, payloads, and malware variants rotated faster than traditional indicators could be operationalised. While static indicators decayed rapidly, behavioural patterns such as role-based targeting, cloud-hosted delivery, MFA abuse, and living-off-the-land activity remained consistent.

Content and Format Abuse Outpaces Traditional Detection

As technical controls continue to improve, threat actors are increasingly shifting their focus away from exploiting software vulnerabilities and towards abusing trust in common content formats. By 2026, malicious activity is frequently concealed within files and data types that organisations are structurally inclined to allow, inspect lightly, or prioritise for usability over security.

Content-type smuggling and polyglot files are becoming more prevalent as attackers exploit discrepancies between how systems interpret file formats. A single file may present itself as benign to one control while being parsed differently by another, allowing embedded scripts or payloads to execute downstream. These techniques are not new, but they are now being applied more systematically and at greater scale, particularly in environments that rely on automated content handling.

Common formats such as PDFs, images, emojis, markdown, and compressed archives are increasingly abused as delivery vehicles. PDFs can carry embedded scripts or external references, images can contain hidden data or exploit parsing behaviour, and text-based formats can be manipulated to trigger unexpected interpretation by browsers, email clients, or automated analysis tools. Even elements designed for expression and accessibility, such as emojis, can be repurposed to carry hidden instructions or evade simple content inspection.

Delivery mechanisms are also evolving. Rather than relying solely on direct email attachments or malicious links, attackers are increasingly using trusted SaaS platforms and collaboration tools to distribute payloads. File sharing services, document collaboration platforms, and messaging tools provide a level of implicit trust and are often deeply integrated into business workflows. This makes it harder for both users and security controls to distinguish malicious activity from legitimate use.

These techniques are particularly effective at evading gateway and sandbox-based detection. Many security controls are optimised to analyse standalone files or clearly defined executables, not content that only becomes malicious when rendered in a specific context or combined with user interaction. Sandboxes may fail to replicate the precise conditions required to trigger malicious behaviour, while gateways may prioritise performance over deep inspection of complex or nested formats.

For cyber threat intelligence teams, this trend reinforces the importance of tracking delivery mechanisms as a primary tactic, technique, and procedure. Understanding how malicious content is introduced into an environment often provides more durable insight than focusing solely on the final payload. The same malware family may be delivered through multiple formats and channels, each tailored to exploit specific organisational habits or control gaps.

This also highlights the intelligence value of analysing how malware arrives, not just what it is. Patterns in file types, hosting platforms, and user interaction requirements can reveal actor preferences and campaign objectives that are not visible through static analysis alone. Such insights are particularly valuable for informing detection engineering and user awareness efforts.

Finally, this trend underscores the need for stronger collaboration between cyber threat intelligence teams and email and web security functions. Intelligence on emerging delivery techniques must be translated into practical guidance for those configuring and tuning controls. In 2026, effective defence against content and format abuse depends not only on identifying malicious artefacts, but on understanding and disrupting the pathways through which they are delivered.

Abuse of Trusted Formats and Platforms

During 2023–2025, multiple security vendors reported widespread abuse of PDFs and archive files to deliver malware while bypassing email and web gateways, including campaigns where malicious content was only revealed after user interaction. Microsoft and Google both documented attackers hosting payloads on legitimate SaaS platforms such as OneDrive, Google Drive, and Dropbox, exploiting implicit trust and integration with enterprise environments. Researchers also observed the use of HTML smuggling and polyglot files to evade content inspection by disguising executable behaviour within allowed formats. In many cases, sandbox detonation failed to trigger malicious activity due to environmental checks or delayed execution. These campaigns demonstrated that the most reliable intelligence signal was not the final payload, but the consistent delivery techniques and abuse of trusted platforms, reinforcing the value of tracking delivery mechanisms as a primary tactic.

The Continued Rise of Identity-Centric Attacks

The Continued Rise of Identity-Centric Attacks

As organisations continue to adopt cloud services and remote working models, identity has become the primary control plane for access to systems and data. In 2026, attackers are increasingly targeting identity directly, recognising that compromising credentials or sessions often provides broader and more durable access than exploiting a single technical vulnerability.

One of the most common techniques remains multi-factor authentication fatigue, often referred to as push bombing. By repeatedly triggering authentication prompts, attackers aim to exploit user frustration or inattention, eventually inducing approval of a fraudulent request. While awareness of this technique has grown, it remains effective in environments where controls are permissive or user training is inconsistent.

Token theft and session hijacking are also becoming more prevalent. Rather than capturing usernames and passwords, attackers increasingly seek to obtain valid session tokens, cookies, or authentication artefacts that allow them to bypass interactive login processes altogether. These techniques are particularly effective against cloud services and single sign-on environments, where a compromised token can provide access to multiple applications without further challenge.

The abuse of OAuth applications and cloud identities represents another significant area of risk. Malicious or compromised OAuth apps can be granted persistent access to user data and resources, often with limited visibility once approved. Attackers may also create or manipulate cloud-native identities, such as service principals or managed identities, to establish long-term access that blends into normal administrative activity.

Once access is obtained, many adversaries favour living-off-the-land techniques within cloud environments. By using legitimate tools, built-in administrative functions, and native APIs, attackers can move laterally, escalate privileges, and exfiltrate data while minimising the use of overtly malicious tooling. This approach reduces the likelihood of triggering traditional malware-focused detection and allows activity to appear operationally routine.

For cyber threat intelligence teams, these developments necessitate a shift in focus. Traditional indicators such as IP addresses and domains remain relevant, but they provide limited insight into identity-centric attacks that leverage legitimate infrastructure and services. Greater value lies in understanding patterns of authentication abuse, anomalous access behaviour, and misuse of identity features.

Tracking actor playbooks against identity and access management controls is becoming increasingly important. Intelligence that maps how specific adversaries exploit MFA configurations, token lifetimes, OAuth consent processes, or role assignment models can directly inform defensive priorities. This enables organisations to move beyond generic hardening guidance and focus on the controls most likely to be targeted.

In 2026, effective threat intelligence plays a critical role in shaping identity defence. By translating observed attack patterns into concrete recommendations, CTI teams can help organisations prioritise identity hardening efforts and reduce exposure at what has become the most frequently attacked layer of the modern enterprise.

Identity as the Primary Attack Surface

Between 2023 and 2025, Microsoft, Mandiant, and Okta documented a sustained rise in identity-centric intrusions involving MFA fatigue attacks, token theft, and session hijacking, particularly against cloud-first organisations. Campaigns attributed to financially motivated groups showed repeated push bombing attempts followed by abuse of valid sessions rather than credential reuse. Researchers also reported widespread misuse of OAuth applications, where attackers gained persistent access by tricking users into granting permissions to malicious or compromised apps. Once inside, adversaries frequently relied on living-off-the-land techniques, using native cloud tooling and APIs to blend into normal administrative activity. These cases highlighted the limited value of traditional IP- or domain-based indicators and reinforced the importance of tracking identity behaviour and attacker playbooks against IAM controls.

Ransomware Becomes a Business Model, Not a Malware Type

Ransomware Becomes a Business Model, Not a Malware Type

By 2026, ransomware will be best understood not as a single category of malware, but as a service-driven business model. The technical payload used to encrypt systems is often interchangeable, while the real differentiation lies in how operations are organised, monetised, and sustained. This shift continues to reshape both the threat landscape and the way organisations should approach ransomware risk.

Ransomware-as-a-service ecosystems continue to evolve and mature. Core developers provide tooling, infrastructure, and branding, while affiliates conduct intrusions and deploy payloads in exchange for a share of the proceeds. This model allows rapid scaling, frequent rebranding, and the replacement of disrupted components with minimal impact to overall activity. It also creates a steady flow of new and short-lived variants that complicate traditional tracking.

At the same time, ransomware operations are increasingly decoupled from encryption itself. Data theft and extortion-only models remain prevalent, particularly where reliable backups or operational resilience reduce the impact of encryption. Many campaigns now combine multiple pressure points, including data leaks, regulatory exposure, and direct contact with customers or partners. These hybrid approaches are designed to maximise leverage while reducing technical complexity.

Rebranding and fragmentation further obscure attribution. Groups regularly change names, infrastructure, and public-facing personas in response to law enforcement action or reputational damage. In some cases, operators deliberately adopt the branding or tactics of other groups to mislead victims and researchers. False-flag activity adds further noise, making it difficult to draw conclusions based solely on malware samples or ransom notes.

Targeting is also shifting. While large enterprises remain attractive, mid-sized organisations are increasingly in focus due to perceived gaps in security maturity and incident response capability. Supply chains continue to present valuable opportunities, allowing attackers to leverage trusted relationships to increase reach and impact. These campaigns often prioritise speed and disruption over long-term persistence.

For cyber threat intelligence teams, these trends present both challenges and opportunities. Actor clustering becomes more difficult as tooling and branding fragment, but it also becomes more valuable. Understanding how campaigns relate to one another through shared behaviours, infrastructure management, and operational patterns provides insight that individual malware labels cannot.

This reinforces the need to focus on who is behind an operation rather than which strain is used. Tracking negotiation behaviour, communication style, leak site activity, and pressure tactics can reveal consistent operator fingerprints even as technical components change. Such intelligence is particularly valuable for incident response planning, negotiation strategy, and executive decision-making.

In 2026, effective ransomware intelligence depends on moving beyond file-based analysis and towards a deeper understanding of adversary operations as businesses in their own right. Those who can identify and anticipate how these businesses operate are better positioned to disrupt them and reduce their impact.

Ransomware as an Operational Business

From 2023 to 2025, ransomware groups such as LockBit, ALPHV, and Cl0p were repeatedly observed operating as service-based ecosystems, with affiliates conducting intrusions while core teams managed tooling, infrastructure, and leak sites. High-profile campaigns, including the MOVEit and GoAnywhere mass exploitation events, demonstrated how data theft and extortion could be conducted at scale without relying solely on encryption. Researchers also documented frequent rebranding and fragmentation following law enforcement pressure, complicating attribution based on malware families alone. Across these campaigns, consistent behaviours such as negotiation style, leak site structure, and pressure tactics persisted even as payloads and infrastructure changed. These patterns underscore the value of actor-centric intelligence focused on who is operating, rather than which ransomware strain is deployed.

Geopolitics Drives Threat Actor Priorities

Geopolitics Drives Threat Actor Priorities

In 2026, the influence of geopolitics on the cyber threat landscape is more pronounced than ever. Nation-state and state-aligned actors are not only increasing in activity but are also shaping the broader ecosystem in which financially motivated and ideologically driven groups operate. Cyber operations are now a routine extension of geopolitical competition, conflict, and signalling.

One key trend is the spillover of geopolitical tensions into cyberspace. Regional conflicts, diplomatic disputes, and economic sanctions frequently coincide with surges in cyber activity, ranging from espionage and influence operations to disruptive attacks. These campaigns may not always be directly attributable to a single state, but they often align closely with national interests or strategic objectives.

Critical infrastructure and logistics networks are increasingly attractive targets. Energy, transport, telecommunications, and supply chain management systems offer opportunities for intelligence collection, disruption, and strategic pressure. Even limited or short-lived interference can have outsized economic and political effects, making these sectors a persistent focus for capable adversaries.

Hacktivism continues to play a prominent role, often blurring the boundary between grassroots activism and state-aligned activity. In some cases, hacktivist groups act as proxies or amplifiers, conducting operations that provide plausible deniability while supporting broader strategic aims. In others, state actors deliberately mimic hacktivist tactics to obscure attribution and complicate response decisions.

These dynamics contribute to increasingly blurred lines between cybercrime, espionage, and disruption. Financially motivated groups may be tolerated or tacitly supported when their activity aligns with national interests, while espionage operations may incorporate criminal techniques or infrastructure. This convergence makes simple categorisation of threats less meaningful and increases the risk of misinterpretation.

For cyber threat intelligence teams, this environment elevates the importance of strategic intelligence alongside tactical reporting. Understanding the geopolitical context in which activity occurs is often essential to interpreting intent, likely targets, and potential escalation. Mapping geopolitical events to observed cyber activity can help organisations anticipate periods of heightened risk and adjust their posture accordingly.

Equally important is the ability to communicate uncertainty and intent to leadership. Strategic intelligence rarely offers definitive answers, but it can provide informed assessments and plausible scenarios. In 2026, effective CTI is measured not only by technical accuracy but by its ability to support informed decision-making in a world where cyber activity is increasingly intertwined with global politics.

Geopolitics Shaping Cyber Operations

Between 2022 and 2025, geopolitical events including the war in Ukraine and heightened tensions in the Middle East coincided with spikes in cyber activity targeting government, energy, logistics, and telecommunications sectors. Security firms and government agencies reported coordinated campaigns involving espionage, disruption, and influence operations aligned with national interests. Hacktivist groups emerged rapidly around these conflicts, often amplifying or obscuring state-aligned activity through defacements, data leaks, and denial-of-service attacks. In several cases, financially motivated and politically aligned operations used overlapping infrastructure and techniques, blurring traditional threat categories. These trends highlighted the growing importance of strategic intelligence that links geopolitical developments to cyber activity and communicates intent and uncertainty to decision-makers.

Intelligence Consumers Demand Clarity, Not Just Alerts

Intelligence Consumers Demand Clarity, Not Just Alerts

As cyber threat intelligence becomes more widely consumed across organisations, expectations around how intelligence is delivered are evolving. In 2026, the challenge is no longer access to threat data, but ensuring that alerts and intelligence are timely, relevant, and actionable for their intended audience.

Security teams and decision makers are exposed to a growing volume of alerts, notifications, and intelligence updates. While this flow of information is essential for maintaining situational awareness, it can become difficult to distinguish between background noise and issues that require immediate attention. This has led to increasing demand for clarity alongside coverage.

Rather than simply asking what has been observed, intelligence consumers are asking more targeted questions. They want to understand why an alert matters, how it relates to their environment, and what actions should be considered next. Alerts that are enriched with context, confidence, and clear analytical judgment are far more likely to drive effective response than raw signals alone.

This has reinforced the importance of tying intelligence to risk and impact. When alerts are mapped to threat actors, campaigns, targeting patterns, or likely objectives, they become easier to prioritise and act upon. Intelligence that highlights relevance, such as sector targeting, geographic focus, or alignment with known tradecraft, enables organisations to make faster and more informed decisions.

Narrative also plays an increasingly important role. Even within alert-driven systems, structured explanations and concise assessments help consumers interpret activity and avoid misreading its significance. The ability to combine timely alerting with clear analytical framing is becoming a key differentiator in intelligence delivery.

For CTI providers, this reflects a broader maturity shift from delivering data alone to delivering understanding at scale. Alerts remain a critical mechanism for awareness and response, but their value is maximised when they are supported by consistent analysis and clear articulation of what the intelligence means. In 2026, the most effective intelligence services are those that help customers move confidently from notification to decision.

CTI Tooling Consolidation, Integration, and Automation

The CTI tooling landscape continues to evolve as organisations seek to simplify workflows and extract greater value from the intelligence they consume. By 2026, many teams are consolidating platforms and prioritising solutions that integrate cleanly into existing security operations rather than operating in isolation.

Overlapping tools and fragmented intelligence sources can make it difficult to maintain a coherent view of the threat landscape. As a result, there is growing emphasis on platforms and services that centralise intelligence, reduce duplication, and present information in a consistent and usable format. Integration with SIEM, SOAR, EDR, and email security tooling is increasingly expected rather than optional.

Automation plays a central role in enabling this consolidation. Automated enrichment, correlation, and triage allow large volumes of intelligence to be processed and surfaced rapidly. This is particularly important for alert-driven intelligence delivery, where speed and scale are critical. Automation ensures that alerts arrive with the context needed to support immediate action.

At the same time, expectations around automation are becoming more realistic. While machines excel at processing data and identifying patterns, analytical judgement remains essential for interpreting intent, assessing confidence, and identifying meaningful shifts in adversary behaviour. The most effective intelligence platforms combine automated processing with human-led analysis.

This balance also shapes discussions around return on investment. Customers increasingly expect intelligence tooling to demonstrate clear operational benefit, such as improved detection, faster response, or better prioritisation. Intelligence that is delivered in a form that integrates naturally into security workflows is more likely to achieve this impact.

For CTI teams and providers alike, a key consideration is deciding what should be automated and what should remain analyst-driven. Repeatable processes and large-scale data handling benefit from automation, while assessments of intent, relevance, and strategic significance continue to rely on human expertise.

In 2026, the enduring value of experienced analysts is not diminished by automation but amplified by it. By pairing scalable delivery mechanisms with consistent analytical oversight, CTI providers can deliver intelligence that is both timely and trusted. This combination is central to meeting rising customer expectations in an increasingly complex threat environment.

What This Means for CTI Teams in 2026

Taken together, these trends point to a clear evolution in how cyber threat intelligence teams must operate in 2026. The challenge is not a lack of data or tooling, but ensuring that intelligence capability is aligned with real organisational needs and outcomes. Teams that adapt their focus and ways of working will be best placed to deliver sustained value.

First, there is a renewed need to invest in analytical skills alongside technology. Tooling and automated alerting provide essential scale and coverage, but they do not replace the ability to assess relevance, weigh confidence, and draw meaningful conclusions. Developing analysts who can interpret complex activity, recognise patterns over time, and communicate insight clearly remains one of the most effective ways to improve intelligence outcomes.

Second, collection should be increasingly guided by clearly defined priority intelligence requirements. Rather than attempting to monitor everything equally, effective CTI teams focus on the threats, actors, and techniques most relevant to their organisation or customers. Well-defined PIRs help shape what data is collected, how it is analysed, and how it is delivered, ensuring that intelligence production remains purposeful rather than reactive.

Strong relationships across the security and business landscape are also essential. CTI does not operate in isolation, and its value is maximised when it is closely connected to security operations, incident response, identity and access management, and senior leadership. Regular engagement with these stakeholders helps ensure that intelligence outputs align with detection needs, response priorities, and strategic concerns.

Finally, success in 2026 is increasingly measured by influence rather than output. The most effective CTI teams are those that can demonstrate how intelligence has informed decisions, shaped defensive priorities, or enabled faster and more confident responses. Reports and alerts remain important delivery mechanisms, but their true value lies in the decisions they support.

For CTI teams navigating an increasingly complex threat environment, these principles provide a practical foundation. By combining strong analytical capability, focused collection, collaborative working, and outcome-driven measurement, intelligence teams can remain relevant and impactful in the year ahead.

Conclusion: The Evolution of CTI

Cyber threat intelligence in 2026 is evolving rapidly. What was once largely a support function is increasingly a strategic enabler, providing insight that shapes decisions across security operations and organisational leadership. Threats are faster, more complex, and noisier than ever, driven by automation, AI, and shifting geopolitical pressures.

In this environment, the differentiators for effective intelligence are context, clarity, and credibility. Understanding not just what is happening, but why it matters and how it affects the organisation, is what turns data into actionable insight. Teams that can provide this perspective, supported by robust analytical capability and integrated tooling, will be best placed to help organisations anticipate, prioritise, and respond to evolving threats.

2026 will not be defined by new types of threats alone, but by the ability of intelligence teams to interpret them, communicate their significance, and drive meaningful action. In this way, cyber threat intelligence will continue to move from reactive observation to proactive influence, ensuring its central role in organisational resilience and security strategy.

1 2 3 4
New: Attack Surface Management · Dark web intelligence. Now with the bigger picture. | Explore SOS Intelligence ASM →
Privacy Settings
We use cookies to enhance your experience while using our website. If you are using our Services via a browser you can restrict, block or remove cookies through your web browser settings. We also use content and scripts from third parties that may use tracking technologies. You can selectively provide your consent below to allow such third party embeds. For complete information about the cookies we use, data we collect and how we process them, please check our Privacy Policy
Youtube
Consent to display content from - Youtube
Vimeo
Consent to display content from - Vimeo
Google Maps
Consent to display content from - Google
Spotify
Consent to display content from - Spotify
Sound Cloud
Consent to display content from - Sound