Articles Tagged with

Introduction
Tor hidden services exist for one reason: anonymity. The entire architecture of onion routing is designed to ensure that a visitor cannot determine where a service is physically hosted, and that the hosting provider’s real IP address never leaks. In theory, this makes hidden services untraceable. In practice, it does not.
The gap between theory and practice is where threat intelligence gets interesting. Over the past decade, researchers, law enforcement, and OSINT practitioners have demonstrated repeatedly that the anonymity of Tor hidden services can be undermined not by breaking the cryptography or the network protocol, but by exploiting something far simpler: misconfiguration.
At SOS Intelligence, we crawl and index dark web content continuously through our DARKSEARCH platform. As part of that work, we encounter misconfigured hidden services regularly. Some expose their real server IP addresses through default web server configurations. Others leak identifying information through debug pages, status endpoints, or metadata embedded in the content they serve. In this article, we will walk through the most common ways that Tor hidden services inadvertently reveal their clearweb identity, how intelligence analysts can use these techniques ethically, and what this means for anyone running or monitoring hidden services.
How Tor Hidden Services Are Supposed to Work
Before we get into the failures, it is worth understanding what a properly configured hidden service looks like. When a Tor hidden service is set up correctly, the web server (Apache, Nginx, or whatever is being used) binds exclusively to localhost, typically 127.0.0.1. The Tor daemon running on the same machine creates a virtual tunnel, accepting incoming connections from the Tor network and forwarding them to the local web server.
The critical point is that the web server should never be listening on a public-facing IP address. If it only listens on 127.0.0.1, the only way to reach it is through the Tor daemon. The server’s real IP address is never exposed to the visitor because the visitor’s traffic is routed through the Tor network and terminates at the Tor daemon, not at the web server directly.
This is the theory. The reality is that many hidden service operators, whether through ignorance, laziness, or haste, fail to configure their servers this way. And when they fail, they leave behind digital breadcrumbs that can be followed all the way back to a clearweb IP address, a hosting provider, and often a physical location.
The Classic: Apache mod_status
The most well-documented and arguably most devastating misconfiguration involves Apache’s mod_status module. This has been a known issue since at least 2001, but it continues to surface on Tor hidden services in 2026.
So here is how it works. On most Linux distributions, Apache ships with mod_status enabled by default. This module provides a real-time status page at /server-status that displays diagnostic information about the running web server. The information it exposes includes the server’s uptime, current connections, the IP addresses of connected clients, the URLs being requested, virtual host configurations, and critically, the server name and IP address of the machine itself.
On a standard ClearWeb server, access to /server-status is typically restricted to localhost or specific IP ranges via Apache’s configuration. But here is where the misconfiguration occurs: when the Tor daemon forwards traffic to the local Apache instance, that traffic arrives from 127.0.0.1 (because the Tor daemon is local). This means it passes the default access restriction. The /server-status page becomes accessible to anyone connecting via Tor.
What Gets Exposed
When an analyst successfully accesses /server-status on a misconfigured Tor hidden service, the data returned can be remarkably detailed. The server name field often contains the server’s real hostname, which may resolve directly to a clearweb IP. The virtual host configuration can reveal other domains being hosted on the same machine. Active connection details may show clearweb IP addresses of other visitors or the server’s own outbound connections. In some cases, the page reveals the exact Apache version, operating system, and loaded modules, giving a complete fingerprint of the server.
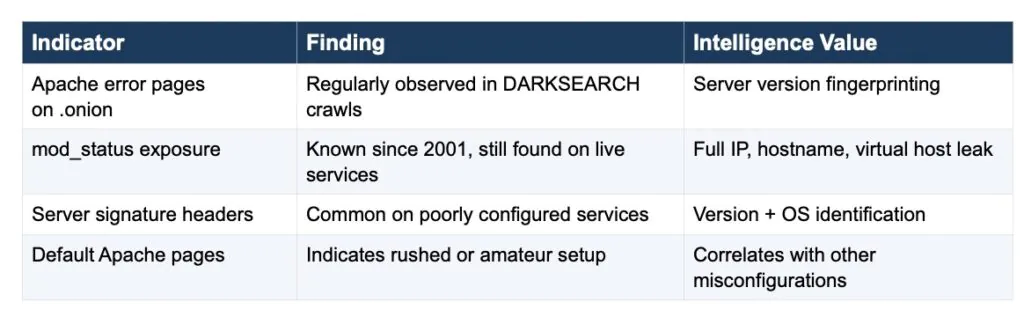
During our DARKSEARCH crawls, we have identified numerous Tor hidden services returning Apache error pages (403 Forbidden, 404 Not Found) that include server signature information in the response headers:
- hxxp://cii64fki62v2mudocjvgarzlmnpqrfp6xb7korapmdd7qmjpnccgduyd[.]onion
- returned a standard 403 Forbidden page during our crawl on 3 March 2026, including the server signature in the response.
- hxxp://hmxt5u75kj5qxqjqhckgaoda6zndgxcazleersyioat4iuq3ldgmkcid[.]onion and hxxp://pbbeck4xcy3jzbu6lv5db3c5n3n44wngmpb5jj3yo4px32mlznziwbid[.]onion
- displayed similar Apache error patterns.
While these are less severe than a fully exposed /server-status page, they still leak server version information that can be cross-referenced with Shodan, Censys, or similar clearweb scanning databases to narrow down the server’s identity.
Real-World Prevalence
PHP Information Disclosure: phpinfo() and Friends
PHP’s built-in phpinfo() function is another classic source of information leaks on Tor hidden services. Developers routinely create test pages (often info.php, phpinfo.php, or test.php) that call phpinfo() to verify their server configuration. The problem is that these pages are frequently left in production, and on a hidden service, they can be accessed by anyone.
The phpinfo() output is extraordinarily detailed. It includes the server’s IP address (in the SERVER_ADDR variable), the server’s hostname (SERVER_NAME), the document root path (which may contain revealing directory structures), all loaded PHP extensions, environment variables that may contain database credentials or API keys, and the exact PHP and operating system versions.
The SERVER_ADDR field is particularly damaging. On a properly configured hidden service, this should show 127.0.0.1. But if the web server is bound to a public IP (the misconfiguration we keep coming back to), SERVER_ADDR will show the server’s real clearweb IP address, directly. No correlation or inference required.
Searching for phpinfo() Pages
Using our DARKSEARCH API, analysts can search for common phpinfo page titles and content patterns across indexed Tor content. The search is straightforward: look for pages containing strings like ‘PHP Version’, ‘SERVER_ADDR’, ‘DOCUMENT_ROOT’, or the characteristic phpinfo() HTML table structure. Our crawls regularly index pages that match these patterns across the onion network.
Beyond phpinfo(), similar information can be leaked by debug frameworks and error reporting configurations. PHP applications running in development mode may display detailed stack traces that include file paths, database connection strings, and server IP addresses. Laravel’s debug page, for instance, is notorious for exposing the full application configuration, including environment variables, when APP_DEBUG is set to true.
SSL/TLS Certificate Leaks
This is one of the more elegant de-anonymisation techniques and was documented extensively by researcher Yonathan Klijnsma. The core issue is that some hidden service operators install SSL/TLS certificates on their Tor-hosted web servers, often for the same domain they use on the clearweb.
So when a hidden service operator obtains an SSL certificate (whether from Let’s Encrypt, Comodo, or any other CA), that certificate is logged in public Certificate Transparency (CT) logs. These logs are searchable using tools like crt.sh. If the same certificate is used on both the hidden service and a clearweb server, or if the certificate’s Subject Alternative Names (SANs) include the server’s clearweb domain, the link between the .onion address and the clearweb identity becomes trivial to establish.
Even without direct domain overlap, the certificate itself contains metadata. The organisation name, the country, the issuance date, and the certificate serial number can all be used as pivot points. Cross-referencing certificate fingerprints with databases like crt.sh, Censys, or Shodan’s SSL certificate search can reveal other services using the same certificate, potentially including clearweb servers.
Why This Keeps Happening
The reason this misconfiguration persists is partly a misunderstanding of what SSL does in the context of Tor. The Tor protocol already encrypts traffic between the client and the hidden service. Adding SSL on top of this does not improve security in any meaningful way for a .onion service. But operators who are accustomed to clearweb hosting habits often install SSL certificates out of habit or because their web application framework requires HTTPS.
The more dangerous scenario is when an operator runs a dual-stack configuration: the same server hosts both a clearweb site and a hidden service. If the SSL certificate covers both, the link is immediate. But even single-stack hidden services can be compromised if the certificate was previously used on a clearweb server, because CT logs are permanent.
Default Pages, Error Messages, and Server Signatures
Not every de-anonymisation technique requires accessing a special endpoint. Sometimes, the information leaks from the most basic server responses.
Default Installation Pages
When our DARKSEARCH crawlers encounter a Tor hidden service showing the default Nginx welcome page, the default Apache test page, or a framework’s default landing page, this tells us several things. First, the operator likely set up the service quickly and did not complete the configuration. Second, the default page often reveals the exact server software version. Third, the default configuration files associated with these pages may have additional endpoints enabled (like /server-status for Apache or /stub_status for Nginx).
We have observed this pattern repeatedly in our crawl data. Onion addresses serving generic 403 Forbidden or 404 Not Found pages with Apache or Nginx signatures in the response body are surprisingly common:
- hxxp://eme7o5bdqwsqvdcj4j6ore6exvxnh6jv3d3nkieopmxfbmdxtrhiljqd[.]onion
- Returned a 404 Not Found message stating ‘Not Found. The requested URL was not found on this server.’ with clear server identification in the response headers, indexed during our March 2026 DARKSEARCH crawl.
Each of these reveals the web server software and often the version number, which becomes a fingerprint.
Verbose Error Pages
Application-level errors can be even more revealing. A misconfigured Django application will display a detailed debug page showing the settings module, installed middleware, database engine, and file paths. A Node.js application crashing with an unhandled exception may dump stack traces containing absolute file paths. A misconfigured PHP application might display MySQL connection errors that include the database host (which could be a clearweb IP if the database is hosted externally).
Each of these error patterns provides pivot points. File paths can reveal operating system details and directory structures. Database connection strings can point to external clearweb services. Stack traces can reveal the application framework and version, which can be correlated with publicly accessible source code repositories.
HTTP Response Headers
Even when the page content itself reveals nothing, the HTTP response headers can leak information. Common leaky headers include X-Powered-By (reveals the backend technology), Server (reveals the web server and version), X-AspNet-Version (reveals the .NET framework version), and custom headers that may include internal hostnames or IP addresses. The Via header, used by proxies, can sometimes reveal the chain of servers the request passed through, potentially including clearweb infrastructure.
Exposed Administration Interfaces
One of the most directly exploitable categories of misconfiguration involves web-based administration panels that were intended to be accessible only from localhost but end up being exposed via the Tor service.
Common Exposed Services
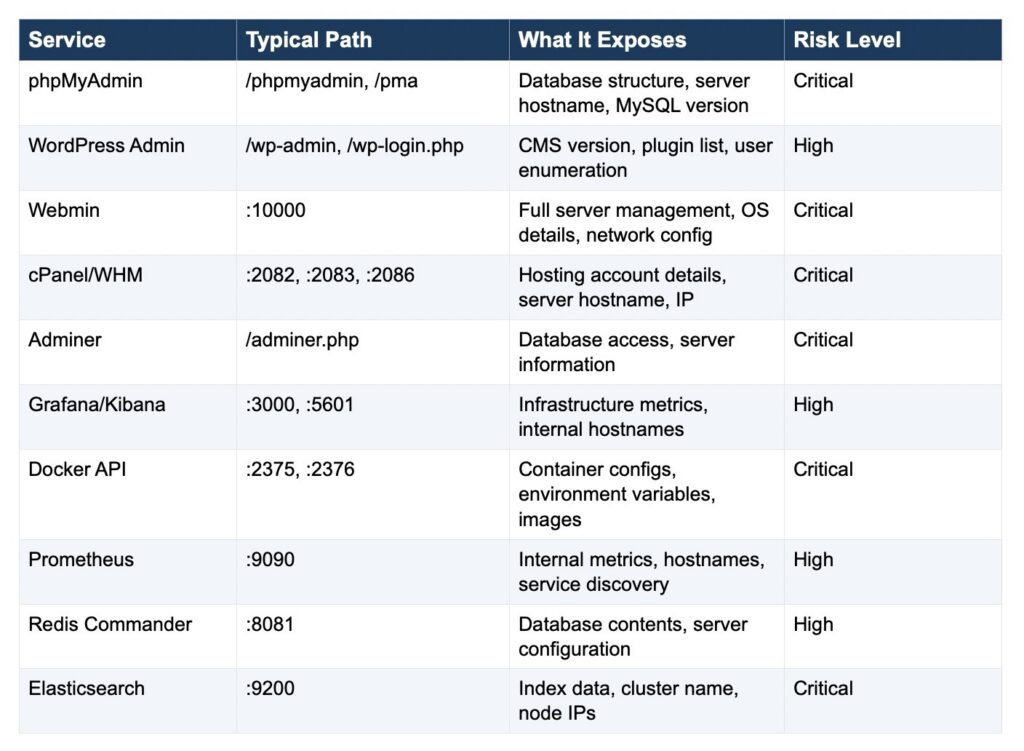
The pattern here is consistent. Services that bind to 0.0.0.0 (all interfaces) by default become accessible through Tor when the hidden service is configured to forward traffic to the server’s local port. An operator who sets up a hidden service and also runs phpMyAdmin for database management may not realise that phpMyAdmin is now accessible to the entire Tor network.
During our research, we found numerous onion addresses serving content that strongly suggests exposed administration interfaces. WordPress login pages on hidden services, for example, are extremely common in our DARKSEARCH index. While a WordPress login page alone does not expose a clearweb IP, the WordPress installation itself may contain metadata (in uploaded images, in theme files, in plugin configurations) that references clearweb URLs. We also observed directory listing capabilities on some services:
- hxxp://ylf6u5gurfisvhgheevy4rxzcw36gyp4r55crqlmiydmzwi2xkvmhcad[.]onion
- (Go Go Onion directory)
- hxxp://wikipenntwqezw7ycy72zmblcxh6fodtqb6yyyfyz55uoh4fx6wqciid[.]onion
- (HiddenWiki)
which index and expose other onion services and their details.
Metadata and Content-Based Leaks
Beyond server configuration issues, the content hosted on a hidden service can itself contain identifying information.
EXIF Data in Images
Images uploaded to hidden services may contain EXIF metadata including GPS coordinates, camera make and model, software used to process the image, timestamps, and in some cases, the original filename that may reference a clearweb domain or username. Tools like OnionScan, developed by Sarah Jamie Lewis, specifically check for EXIF data in images hosted on hidden services. Our DARKSEARCH platform includes a similar capability, allowing analysts to identify images with residual metadata that can be correlated with clearweb sources.
Embedded Clearweb Resources
A hidden service page that loads JavaScript libraries, CSS stylesheets, images, or fonts from clearweb CDNs creates a tracking vector. When a visitor loads the hidden service page, their browser (or, in our case, our crawler) can observe the external resource requests. More importantly, the CDN operator can log the timing of those requests, and the hidden service operator has implicitly revealed that they control the account on the CDN from which the resources are served.
The reverse is also true: if a hidden service’s HTML source contains hardcoded clearweb URLs (perhaps the developer copied the template from their clearweb site), those URLs can directly identify the operator. We have seen this in our crawls, where onion-hosted pages reference clearweb domains in their source code, style sheets, or embedded scripts:
- hxxp://bfdxjkv5e2z3ilrifzbnvxxvhbzsj67akjpj3zc6smzr4vv6oz565gyd[.]onion
- (observed as a XenForo forum)
- hxxp://33333337u3npxstc4rrx2z2o5z5cvmbbdr4maqzlutpgmgcqobnxxuqd[.]onion
- (VicePaste service)
sometimes reveal resource references in their indexable content.
DNS Leaks
If the hidden service’s server makes outbound DNS requests (for example, to resolve a database server hostname, to check for updates, or to load external content), those DNS queries go through the server’s regular network stack, not through Tor. An observer with access to the DNS infrastructure can see the server’s real IP address, making those queries. This is not directly detectable through our DARKSEARCH crawls, but it is a significant vector that complements the other techniques discussed here.
Using the SOS Intelligence API for Tor Service Analysis
At SOS Intelligence, our DARKSEARCH API provides programmatic access to our indexed dark web content, including Tor hidden service data. Analysts can use this to systematically search for the misconfiguration patterns described in this article.
DARKSEARCH Endpoint
The DARKSEARCH endpoint (GET /api/v2/darksearch/new) accepts search queries and returns indexed content from Tor hidden services. By searching for terms like ‘server-status’, ‘phpinfo’, ‘wp-login’, or specific error message patterns, analysts can identify potentially misconfigured services at scale. Each result includes the onion hostname, the page title, the indexed content, and timestamps showing when the page was crawled.
Practical Search Patterns
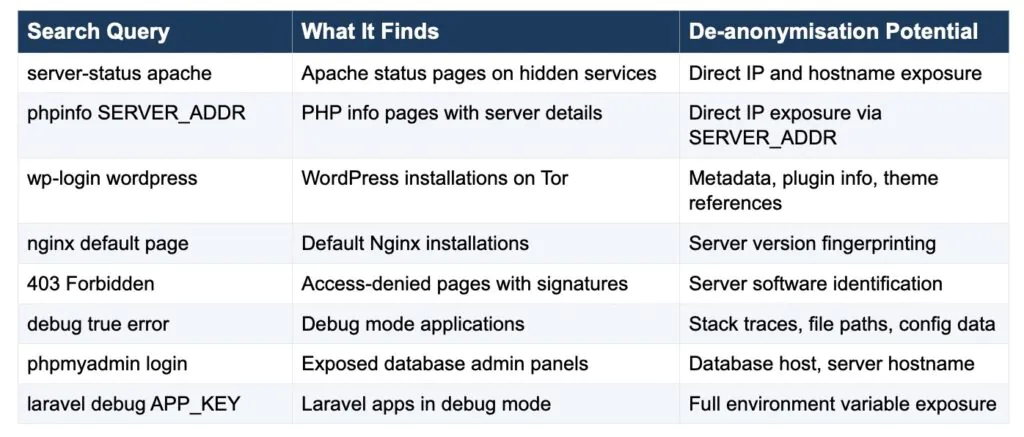
Tor Metadata Endpoints
Beyond DARKSEARCH, our Tor API endpoints provide metadata about onion services, including path information that can reveal directory structures and exposed endpoints. By analysing the paths crawled on a given onion service, analysts can identify non-standard endpoints that may correspond to administrative interfaces or debug pages.
Defensive Guidance: Hardening Hidden Services
While this article has focused on offensive OSINT techniques, the defensive side is equally important. If your organisation runs legitimate hidden services (for example, for secure whistleblowing, censorship circumvention, or privacy-preserving communication), the following configuration practices are essential.
Web Server Configuration
Bind to localhost only. Your web server must listen exclusively on 127.0.0.1. In Apache, this means setting Listen 127.0.0.1:80 in the main configuration. In Nginx, use listen 127.0.0.1:80. Never use 0.0.0.0 or *.
Disable mod_status and mod_info. In Apache, explicitly disable these modules with a2dismod status and a2dismod info. Do not rely on access controls alone.
Remove default pages and test files. Delete index.html default pages, phpinfo.php test files, and any other diagnostic scripts before going live.
Suppress server signatures. In Apache, set ServerTokens Prod and ServerSignature Off. In Nginx, add server_tokens off to the http block.
Strip revealing headers. Remove X-Powered-By and other headers that reveal your technology stack.
Application Configuration
Never run in debug or development mode. Ensure your application is running in production mode with detailed error reporting disabled for end users.
Do not use SSL certificates. Tor already provides end-to-end encryption. Adding SSL to a hidden service only creates a de-anonymisation vector through Certificate Transparency logs.
Avoid loading external resources. Host all JavaScript, CSS, fonts, and images locally. Do not reference clearweb CDNs.
Strip EXIF data from images. Process all uploaded images to remove metadata before serving them.
Infrastructure Security
Isolate the hidden service. Run it in a dedicated container or VM that has no other services exposed. Do not host a clearweb site and a hidden service on the same machine.
Block outbound connections. Configure firewall rules so the hidden service machine can only communicate through Tor. This prevents DNS leaks and outbound connections that could reveal the real IP.
Audit regularly. Use tools like OnionScan to check your own hidden service for information leaks. Treat this as part of your regular security review process.
The Intelligence Value of Misconfigured Services
For threat intelligence teams, the techniques described in this article are not theoretical. They produce actionable results. When a dark web marketplace, ransomware leak site, or fraud operation is hosted on a misconfigured Tor hidden service, the exposed clearweb IP can lead to a hosting provider, a jurisdiction, and potentially an individual.
Even partial information has value. A server version fingerprint can narrow the search space from billions of IPs to thousands. A leaked hostname can be resolved and cross-referenced. A certificate fingerprint can be tracked across multiple services. An exposed admin panel username can be correlated with clearweb accounts. The cumulative effect of multiple small leaks is often enough to identify the operator.
Law enforcement agencies have used exactly these techniques in major dark web takedowns. The Silk Road investigation benefited from a server misconfiguration that leaked the site’s IP address via its CAPTCHA server. The Hansa Market takedown involved Dutch National Police exploiting similar configuration errors to identify and eventually operate the marketplace. These are not exotic attacks. They are straightforward OSINT techniques applied to poorly configured servers.
Appendix: Observed Indicators from DARKSEARCH
The following table documents real onion addresses observed during DARKSEARCH crawls in March 2026 that exhibit the misconfiguration patterns discussed in this article. These services were indexed through our standard crawling process and represent active examples of the threat vectors described throughout this report. All onion addresses are defanged for security purposes (dots replaced with [.]).
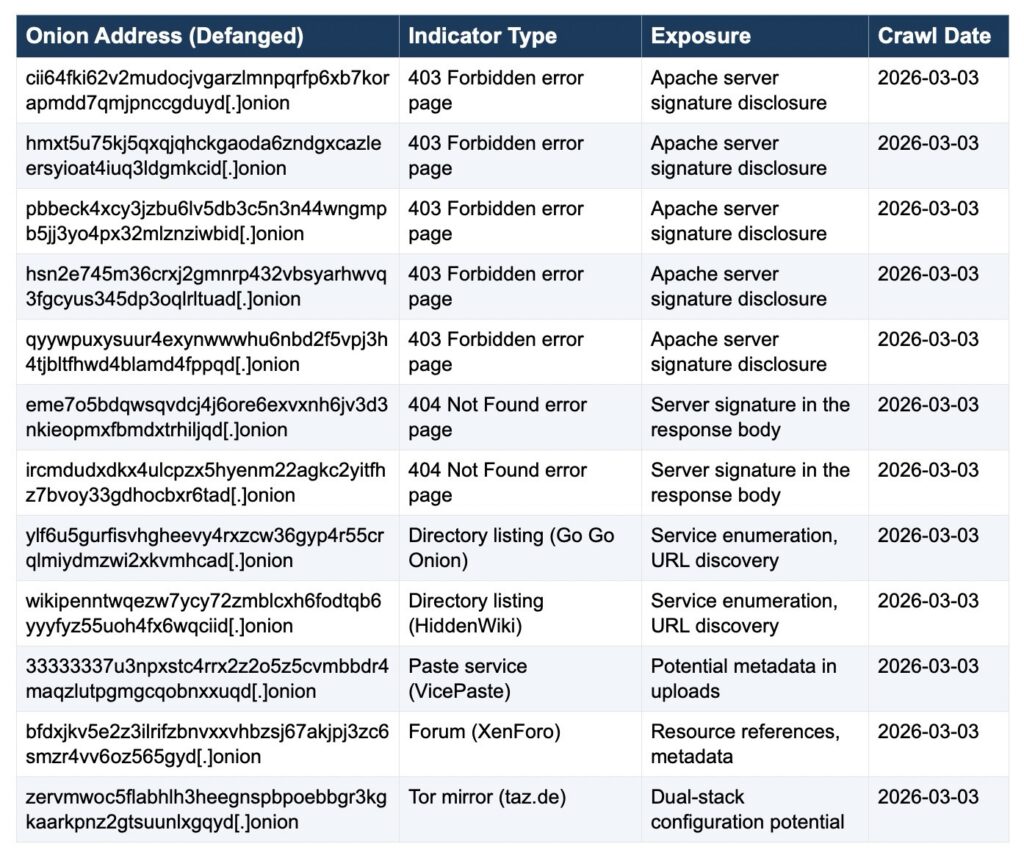
The presence of these indicators in our DARKSEARCH index demonstrates that misconfiguration de-anonymisation techniques remain effective against real-world Tor hidden services. Each category of indicator (error page signatures, directory listings, resource references) represents a distinct attack vector that threat intelligence teams can operationalise at scale using the DARKSEARCH API.
External References and Tools
The following resources provide additional context, methodologies, and tooling for Tor hidden service analysis and de-anonymisation research:
Academic and Research Papers
- Klijnsma, Y. (2015). ‘HTTPS: The Wrong Side of History’ documented SSL certificate de-anonymisation techniques and Certificate Transparency log analysis methods for identifying hidden service operators.
- Lewis, S. J. (2014). ‘OnionScan: Automated OSINT for Tor Hidden Services’ introduced methodologies for systematic scanning and metadata extraction from onion services.
Law Enforcement Case Studies
- Silk Road Investigation: Federal law enforcement identified Ross Ulbricht’s infrastructure partly through misconfiguration vectors, including a CAPTCHA server that leaked IP address information due to poor isolation from the Tor service.
- Hansa Market Takedown: Dutch National Police (Politie) identified and eventually operated the Hansa marketplace by exploiting similar misconfiguration patterns, including exposed administrative interfaces and information disclosure vulnerabilities.
Publicly Available Tools
- OnionScan (by Sarah Jamie Lewis): Automated tool for scanning Tor hidden services and extracting metadata, EXIF data, and server information. Source available on GitHub.
- crt.sh: Certificate Transparency search engine allowing analysts to query public CT logs for SSL certificates. Useful for linking .onion services to clearweb domains.
- Shodan (shodan.io): Internet-wide scanning database that indexes server banners, headers, and metadata. Can be used to cross-reference server fingerprints and configurations.
- Censys: Internet scanning and certificate database providing similar capabilities to Shodan, with particular strength in certificate transparency log analysis.
- DARKSEARCH API (SOS Intelligence): Programmatic access to indexed dark web content, including Tor hidden services. Supports systematic searching for misconfiguration patterns and metadata extraction.
Related Reading
- Greensill, J. & Aldridge, J. (2019). ‘Cryptomarkets and the Future of Illicit Drug Markets’ discusses operational security practices and common failures of dark web services.
- NIST Cybersecurity Framework: Provides defensive guidance for organisation-wide security hardening, including principles applicable to Tor hidden service deployment.
Conclusion
The anonymity provided by Tor is only as strong as the weakest configuration on the server. The Tor network itself remains robust, but the humans running hidden services make mistakes. They leave debug pages enabled. They install SSL certificates that link back to their identity. They run web servers with default configurations that expose status pages. They load resources from clearweb CDNs. They forget to strip metadata from images.
For threat intelligence professionals, these mistakes are opportunities. They provide a way to peer behind the curtain of anonymity and identify the infrastructure, and sometimes the individuals, behind dark web operations. The techniques are well-documented, the tools are freely available, and the results are frequently actionable.
At SOS Intelligence, we provide the raw data and search capability that makes this kind of analysis possible at scale. Our DARKSEARCH platform indexes dark web content continuously, and our API gives analysts programmatic access to search for the exact patterns described in this article. If you are running a threat intelligence programme, and you are not systematically checking for these misconfigurations, you are missing intelligence.
Header photo by Rafael Garcin on Unsplash.
Hidden door photo by Stefan Steinbauer on Unsplash




Recent Comments